Updated Jul 28, 2026
Version 3.0
ScottSawyer Microsoft
MicrosoftMicrosoft
Hi team, I have some questions
1, Are multiple compliance discovery scripts executed each in its own isolated process/subshell, or are they sourced/evaluated within a shared shell context? (We need to know whether exit, readonly, or shared variable names across scripts can interfere with one another.)
2, Where on the device is the discovery script staged and executed from during a compliance check-in? What is the working directory and the exact interpreter/invocation used?
3, Which log contains the actual STDOUT/return value and failure reason for a compliance discovery script (as opposed to a Shell Script deployment)? Is the script's STDOUT/JSON output logged anywhere, or only pass/fail + PolicyID?
4, Do macOS custom compliance discovery scripts run in root/system context or in the signed-in user's context?
Thank you team!
 Microsoft
Since it's launched by the IntuneMdmAgent LaunchDaemon, it has same access with agent, full access to /Library, system config, MDM plists, etc.
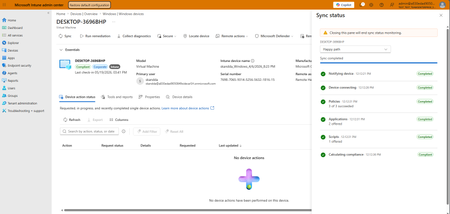
I have a new issue with this. Yesterday, the detection script ran and returned a status of RUNNING; however, today, the Company Portal is showing an error: 65007 (Script returned failure). After syncing, the device is still compliant, and the status in Compliance Settings is now 'Compliant'. In the known issues made by Microsoft, I belive that my script included return value. Could you please help me in checking this? Thank you!
Thank you so much!