MST is essentially Certificate Transparency for code signing, and the post is refreshingly honest about why that matters. The value isn't stopping a stolen key from producing a valid signature. It's that the misuse can't happen quietly anymore. Web PKI made that same trade a decade ago and it held up well.
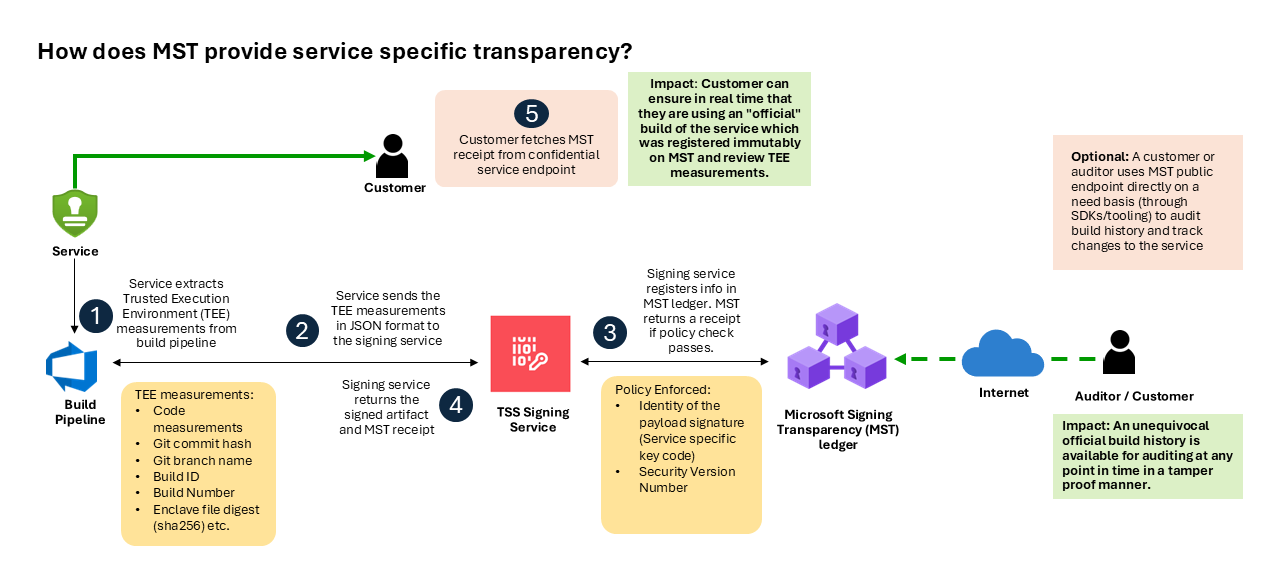
From (my) detection and IR side, the signing event interests me less than the question of who is watching the ledger afterwards. The receipt proves inclusion at signing time, fine. But that only buys you something if someone is checking the log for entries under their own signing identity that nobody authorized. Same discipline as watching CT logs for certs issued against your domains. Skip that and you have great forensics for after an incident and not much of a control during one.
Worth naming what it doesn't cover, too. A SolarWinds-style compromise, where the build is tampered with before a legitimate signer signs it, still produces a valid and logged signature. MST won't flag that on its own. What it does is move the question from "was this signed" to "did we expect this signing event", and answering that is a baselining problem. You need to know what normal signing activity looks like before an unexpected entry means anything.
Two things I'd want answered. Is there consumer-side guidance or tooling for subscribing to ledger entries for a given identity and alerting on the ones you didn't expect? And does GA mean customers can sign their own artifacts through MST, or is this Microsoft attesting its own releases with the ledger open for inspection? The monitoring approach changes a lot depending on which one it is.

 Microsoft

