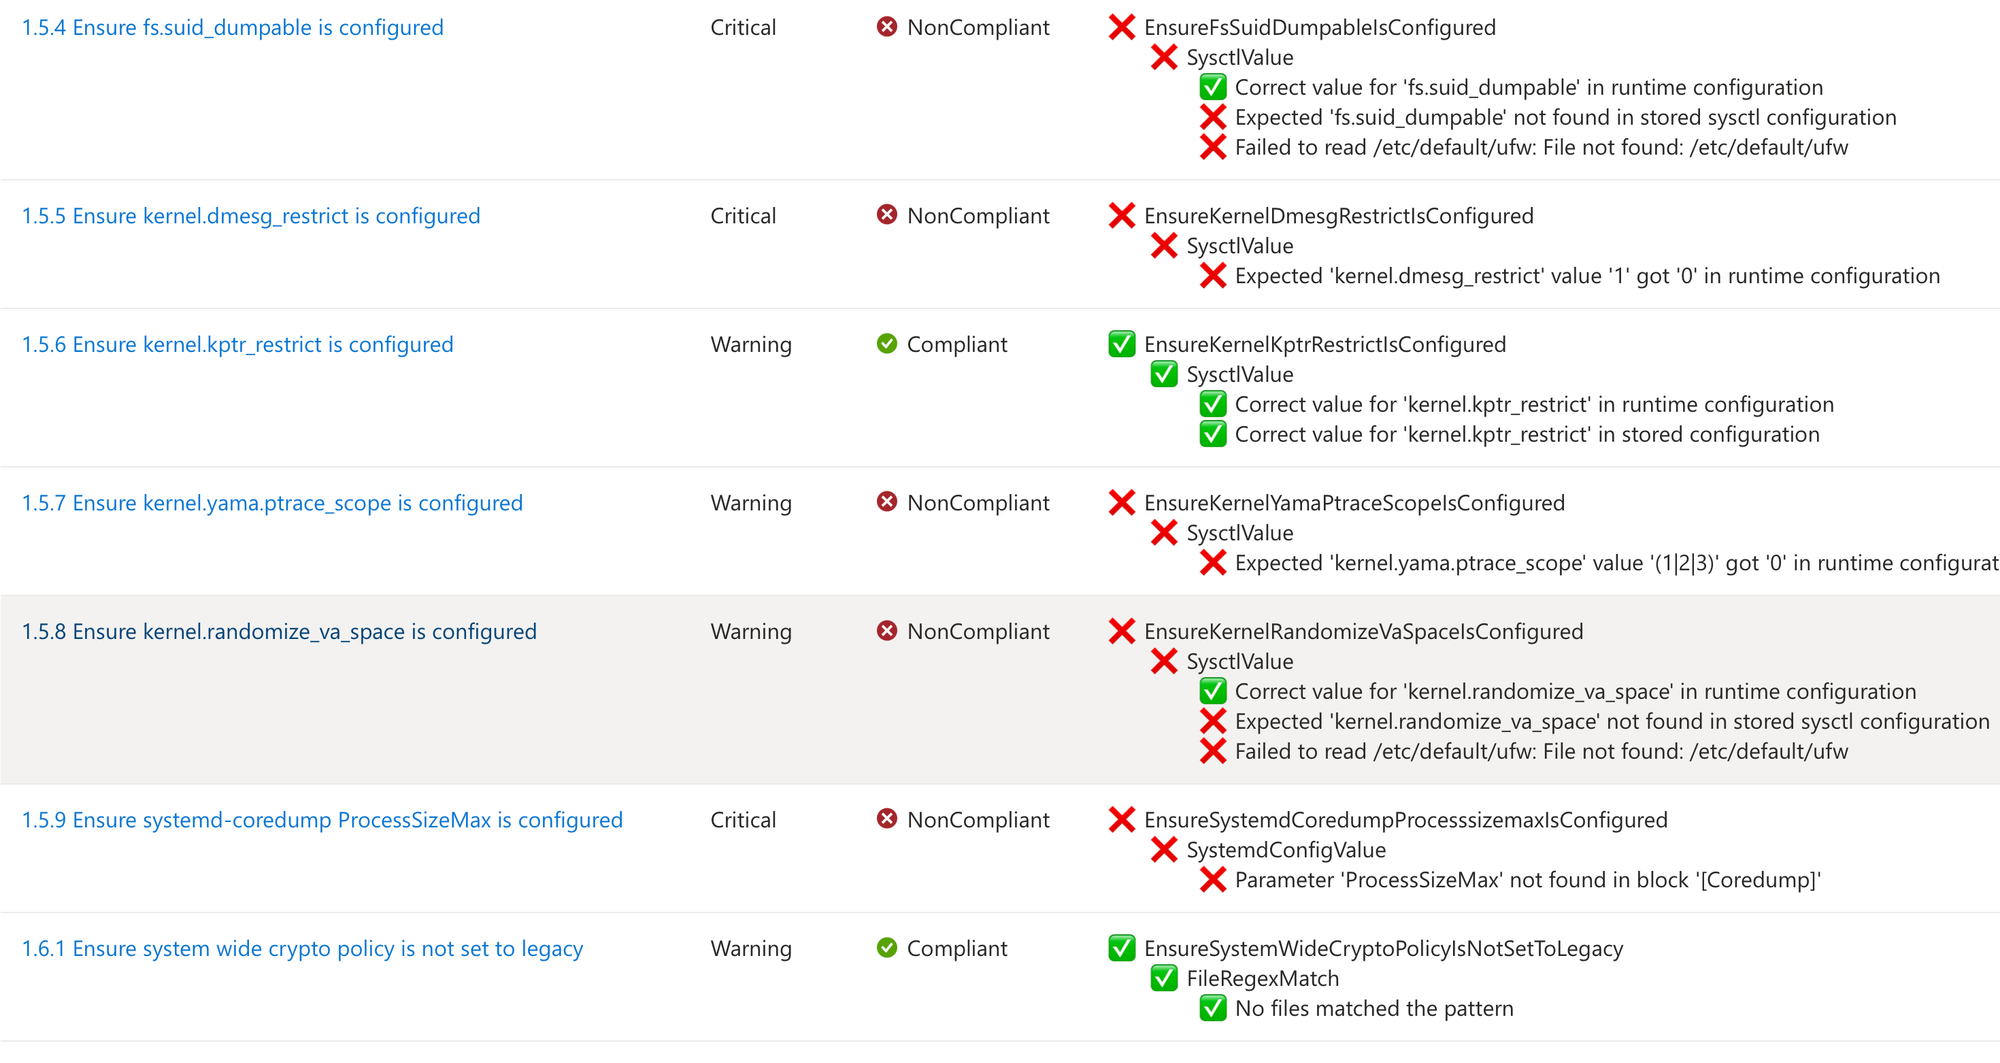
A few months ago, in From Policy to Practice: Built-in CIS Benchmarks on Azure – Flexible, Hybrid-Ready, we introduced a new way to bring Center for Internet Security (CIS) Benchmarks to your Linux estate using Azure Policy with Machine Configuration. It builds on the broader customizable security baseline policies in Machine Configuration capability.
Today we're excited to share the next milestone: the audit capability for CIS Benchmarks on Linux is now Generally Available (GA).
This release is officially powered by kompli - our native Linux compliance and hardening engine for CIS, STIG, and custom baselines. kompli is the evolution of the engine that drove the preview, now established as the dedicated home for this capability going forward.
What "GA" means for you
The audit experience is now ready for production use. You can continuously assess your Linux workloads against official, CIS-certified benchmarks - at scale, across Azure and hybrid environments through Azure Arc - and get clear, CIS-style compliance reporting directly in Azure Policy and Azure Resource Graph.
If you've read the previous post, the how hasn't changed, so we'll keep this one short:
- Automated compliance assessment - continuously monitor Linux systems against official CIS benchmarks.
- Tailored benchmarks - customize evaluations with exceptions and custom parameters, no code changes required.
- Compliance reporting - detailed, CIS-style reports across your fleet.
- Hybrid-ready - the same baselines apply to Azure VMs and Arc-enabled servers on-premises or in other clouds.
All supported benchmarks are CIS Benchmark Assessment Certified and stay in parity with the content published on the CIS website.
Supported distributions and benchmark versions
With this release, audit is GA across the following distributions, covering Level 1 + Level 2 Server profiles:
| Distribution | CIS Benchmark Version(s) | Profiles | Audit |
|---|---|---|---|
| Ubuntu 20.04 / 22.04 / 24.04 LTS + Pro | v3.0.0 / v2.0.0 + v3.0.0 / v1.0.0 | L1 + L2 Server | ✓ |
| Red Hat Enterprise Linux 8 / 9 / 10 | v3.0.0 + v4.0.0 / v2.0.0 / v1.0.1 | L1 + L2 Server | ✓ |
| AlmaLinux 8 / 9 | v3.0.0 + v4.0.0 / v2.0.0 | L1 + L2 Server | ✓ |
| Rocky Linux 8 / 9 | v2.0.0 + v3.0.0 / v2.0.0 | L1 + L2 Server | ✓ |
| Oracle Linux 8 / 9 | v3.0.0 + v4.0.0 / v2.0.0 | L1 + L2 Server | ✓ |
| Debian 11 / 12 | v2.0.0 / v1.1.0 | L1 + L2 Server | ✓ |
| SUSE Linux Enterprise 12 / 15 | v3.2.1 / v2.0.1 | L1 + L2 Server | ✓ |
| AKS Optimized Azure Linux 3 | v1.0.0 | L1 + L2 Server | ✓ |
This GA covers the audit (assessment) capability. Looking ahead, STIG benchmarks are coming next, followed by a granular per-rule auto-remediation capability with dynamic scope assignments.
You can run these benchmarks against your own hardened images, against CIS hardened images, and against custom images built on top of vanilla distros — as long as /etc/os-release retains its original content. We're also working with vendors to minimize deviations.
Getting started
- Open Azure Policy in the Azure portal.
- Under Authoring, select the new Machine Configuration blade.
- Choose Official Center for Internet Security (CIS) Benchmarks for Linux Workloads, then Modify Settings to pick the distributions you want to assess.
Full documentation, including per-distribution rule details, supported parameters, and any known deviations from the official CIS toolset, is available here:
- Overview: CIS Security Benchmarks for Linux Workloads
- Per-distribution references: AlmaLinux, Azure Linux, Debian, Oracle Linux, Red Hat Enterprise Linux, Rocky Linux, SUSE Linux Enterprise, and Ubuntu - all linked from the overview page.
We're building this with you
As part of this GA release, we've also expanded the set of exposed rule parameters compared to the preview - giving you more out-of-the-box customization across rules and distributions. That said, our customer-driven approach still stands: we keep the experience clean by enabling parameters based on real demand, so if there's a rule, benchmark version, or distribution you'd like parameters enabled for - or any feedback on rules, evaluations, or distro coverage - let us know:
Try it out, tell us what you think, and help shape what we build next.

 Microsoft