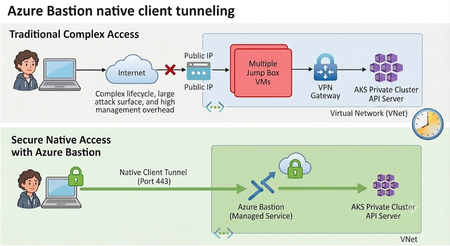
I am not sure why there is a VPN gateway between the jump host and the AKS cluster, as the diagram shows them both in the same VNet.
The jump host could be hosted privately in the same VNet and accessed through Azure Bastion. This would reduce the attack surface while fulfilling the same purpose as the solution described in this article. Of course, the jump host would be an additional resource to manage.
As I see it, native access through Azure Bastion eliminates the need for a jump host, as already mentioned in the article. It also allows administrators to use native kubectl or other third-party tools running on their local machines to perform Kubernetes-related tasks. However, a jump host provides additional capabilities for tasks unrelated to Kubernetes, such as development or testing activities.

 Microsoft
