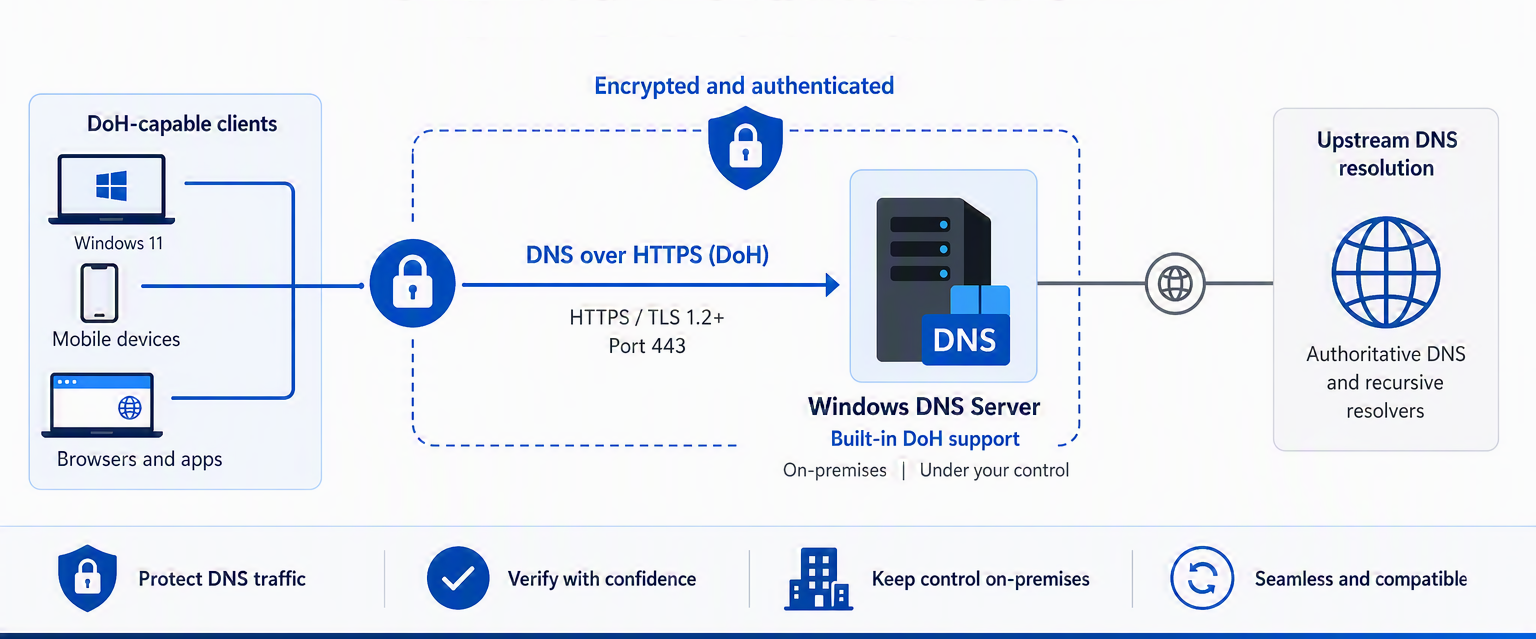
Today, we’re excited to announce that DoH support for Windows DNS Server is generally available on Windows Server 2025 for client-to-server DNS traffic.
When we first introduced DNS over HTTPS (DoH) for Windows DNS Server in public preview, we described it as a Zero Trust upgrade to the foundation of enterprise networking. With general availability, organizations can now deploy encrypted and authenticated client-to-resolver DNS traffic directly within their existing on-premises DNS infrastructure. The goal is to help improve privacy, reduce spoofing risk, and advance Zero Trust DNS without requiring a new resolver architecture.
This release helps organizations secure one of the most critical, and traditionally exposed components of modern networks while preserving compatibility with existing enterprise DNS deployments.
Why DNS security matters more than ever
DNS remains at the heart of every network interaction: every application, every service, every workload depends on it. Yet historically, DNS traffic has been transmitted in the clear. This could expose sensitive query and response data to passive monitoring and traffic analysis, man‑in‑the‑middle attacks, and unauthorized inspection of user and system behavior.
As enterprise environments adopt Zero Trust architectures and face evolving regulatory requirements, securing DNS further is no longer optional; it’s foundational.
What DoH brings to Windows DNS Server
DNS over HTTPS changes how DNS traffic is transported. DNS encapsulates DNS queries and responses inside HTTPS, encrypted by TLS. With general availability, Windows DNS Server enables the following capabilities:
|
Capability |
Value for organizations |
|
Encrypted DNS (between client and server) |
• DNS queries and responses are encrypted in transit using HTTPS. • Helps prevent eavesdropping and unauthorized inspection. • Helps protect DNS data from tampering while in transit. |
|
Authentication |
• TLS certificates help clients verify the identity of the DNS server. • Helps reduce the risk of spoofing and impersonation attacks. |
|
Standards-based interoperability |
• Built on the IETF DNS over HTTPS standard, RFC 8484. • Designed to work with modern RFC 8484-compliant clients, including Windows clients that support encrypted DNS. |
|
Integration with existing infrastructure |
• Runs within the Windows DNS Server role; no separate resolver is required. • Existing DNS resolution behavior remains unchanged. • Traditional unencrypted DNS can continue alongside DoH where required, supporting incremental adoption. • Traditional unencrypted DNS is used for DNS server to DNS server communication. |
From preview to general availability: What’s changed
In our previews, we worked closely with private and public sector organizations to validate real-world deployments and evaluate the experience.
With general availability, this release is designed for production use and delivers several key benefits: enhanced stability and supportability, clearer deployment guidance, greater operational confidence, and improved alignment with enterprise security best practices and Zero Trust architectures.
This milestone reflects your feedback and validation across diverse enterprise environments.
Advancing towards Zero Trust DNS
DoH on Windows DNS Server isn’t just a feature, it’s part of a broader strategy to enable Zero Trust DNS across the Windows ecosystem.
Windows clients already support encrypted DNS. Now, Windows Server provides the on-premises resolver counterpart, enabling encrypted and authenticated DNS across endpoints and infrastructure.
This unified approach helps organizations establish a consistent security posture for name resolution without requiring external DNS services or an architectural redesign.
For many organizations, including U.S. federal agencies, this model also helps support certain requirements for encrypted DNS protocols between clients and resolvers.
For organizations aligning with U.S. federal guidance such as OMB M-22-09 or NIST Secure DNS Deployment Guide, this release supports encrypted DNS communication between clients and Windows DNS Server using standards-based protocols. While this release focuses on encrypting client-to-resolver communication, support for encrypted communication between Windows DNS Server and upstream DNS resolvers is planned for a future update. Together, these capabilities will help enable fully encrypted DNS resolution paths aligned with aspects of U.S. federal Zero Trust objectives.
What to expect operationally
Enabling DoH on Windows DNS Server introduces encrypted communication for supported clients over HTTPS while preserving compatibility with most existing DNS deployments.
Organizations can expect DoH traffic between DoH clients and Windows DNS Server to be encrypted via TLS, DNS queries to be transported as HTTPS requests, existing DNS functionality to continue operating as expected, and mixed environments, encrypted and traditional DNS, to be supported.
This allows organizations to adopt encrypted DNS incrementally, without disrupting existing workloads.
Getting started
DoH is available on Windows Server 2025 running the June 9, 2026 update (or newer)...
Recommended deployment flow:
- Configure a trusted TLS certificate.
- Enable DoH in the DNS Server service.
- Configure supported clients to use the secure endpoint.
Consult our documentation for more details: Enable DNS over HTTPS in DNS Server.
Share your feedback and help shape future improvements
In addition to standard support channels, you can also submit feedback directly from Windows Server using Feedback Hub. It provides a streamlined way to report issues, suggest enhancements, and share deployment experiences with the Windows DNS Server product team.
Work toward a more secure foundation
DNS has long been one of the most critical and exposed protocols in enterprise networks. With DoH now generally available in Windows DNS Server, your organization can help secure that foundation further.
Consider bringing encrypted DNS into existing infrastructure today. You can help strengthen your organization’s security posture, better align with modern Zero Trust principles, and help protect sensitive network signals from exposure.
Your DNS Server software just got an upgrade, and now it’s ready for production.

 Microsoft


