Updated Jun 11, 2026
Version 1.0
JorgeCañas Microsoft
 MicrosoftMicrosoft

Great!
Does this also enforce DoH at the OS/network level, or can browsers (Chrome, Firefox, Edge) still set their own DoH resolver independently and bypass this entirely?
 Microsoft
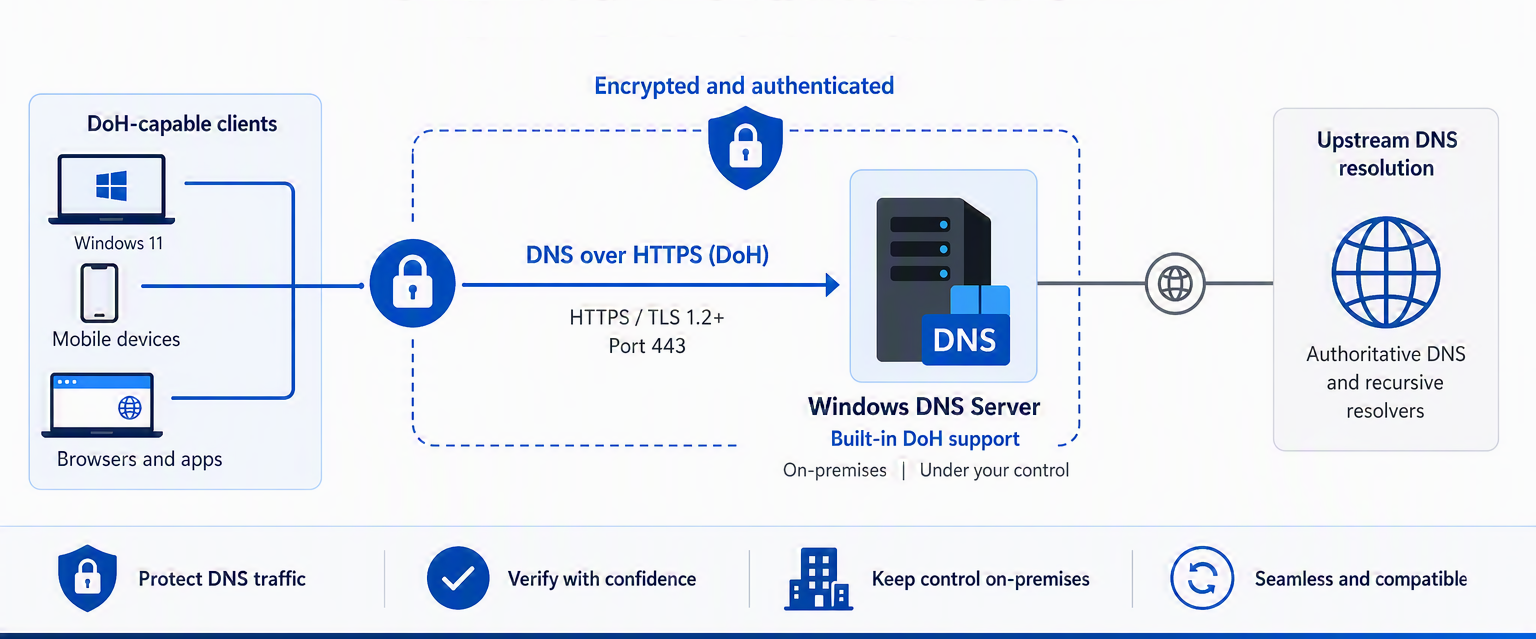
The scope of this feature is on the DNS server side: it enables Windows DNS Server to accept, process and respond to DNS-over-HTTPS requests. Whether a browser, operating system or any other application uses a DNS server is determined by that client-side DNS configuration and policies in place.
We do have a feature in Windows 11 (ie. on the client side) called Zero Trust DNS. That feature will block connections towards any IP address that has not been discovered through the resolver configured on the operating system settings. So, when that feature is active, web browsers running on that machine will still be able to query their own DNS servers to resolve IP addresses, but the browsers will be unable to connect to the resolved IP addresses.