web apps
472 TopicsAzure Catalyst: one connected, agent-led modernization experience across apps, data, and infra
Azure Catalyst brings together Azure and GitHub Copilot in one experience to modernize applications, data, and infrastructure. It connects discovery, planning, and execution to help customers modernize faster, reduce complexity, and accelerate AI transformation.1.5KViews0likes0CommentsIntroducing Geo-redundancy in Azure App Service: Simplify multi-region application resilience
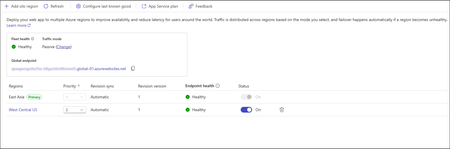
Building resilient applications across Azure regions has traditionally required teams to deploy and maintain separate applications, coordinate application updates and configuration, and manage traffic routing and failover. While these capabilities are essential for business-critical applications, implementing them can introduce significant operational complexity. Today, at Microsoft Ignite 2026, we're excited to announce the public preview of Geo-redundancy in Azure App Service, a new capability that simplifies how customers build and operate regionally resilient web applications. With Geo-redundancy, you can extend an eligible Azure App Service web app across multiple Azure regions, synchronize supported application content and configuration, and configure health-based traffic routing and regional failover, all through a unified App Service experience. The result: less time managing multi-region application infrastructure and more time delivering application value. Multi-region resilience, simplified Geo-redundancy introduces a more integrated approach to building multi-region applications on Azure App Service. Instead of independently provisioning, deploying, and maintaining web applications in multiple regions, you can start with an existing eligible web app and add managed regional replicas in supported Azure regions. Azure App Service provisions and manages the corresponding regional application and App Service plan resources, synchronizes supported application revisions, and maintains the underlying Azure Traffic Manager configuration. This gives you a simpler way to establish and operate a multi-region application topology while retaining control over where your application runs, how traffic is distributed, and how application revisions are synchronized. What's new in the public preview? Geo-redundancy brings together several capabilities designed to simplify regional application resilience: Managed regional replicas: Extend your application into additional Azure regions without independently provisioning and maintaining each regional deployment. Application content and configuration synchronization: Keep supported application revisions aligned across regions, reducing the effort required to coordinate multi-region deployments. Flexible traffic routing: Choose between Active and Passive traffic modes to align regional traffic distribution with your application's resilience strategy. Integrated health-based routing and failover: Use Azure Traffic Manager to direct new connections to eligible, healthy regional endpoints according to your configured routing policy. Application revision control: Inspect synchronization status, validate application revisions, and use supported last-known-good revision capabilities to maintain greater control over regional deployments. Together, these capabilities reduce the operational overhead of managing multi-region web applications while giving teams more control over how applications are deployed and served across regions. Choose how your application serves traffic across regions Different applications have different resilience requirements. Geo-redundancy supports two traffic modes, giving you flexibility in how regional application replicas participate in serving requests. Active mode: Serve traffic across multiple regions With Active mode, multiple healthy regional replicas can serve application traffic simultaneously. You can configure traffic weights to influence how new connections are distributed across eligible regional endpoints. This approach is useful for applications designed to operate across multiple regions, allowing you to distribute application traffic while maintaining regional deployment flexibility. Passive mode: Prioritize a primary region with regional failover With Passive mode, your application primarily serves traffic from a designated region, with additional regional replicas available as failover destinations. You configure regional routing priorities to determine which endpoints should receive traffic when the preferred region becomes unavailable. This approach is particularly useful for applications that normally operate from a primary region but need an alternative regional hosting destination when disruptions occur. Both modes use Azure Traffic Manager's DNS-based routing capabilities. Routing decisions depend on endpoint health and the configured policy, with failover timing influenced by DNS caching and client behavior. Whether your application needs multiple active regions or a primary region with standby capacity, Geo-redundancy provides an integrated way to configure and manage regional traffic routing. Simplify application deployments across regions Maintaining consistent application versions across regions is an important part of operating resilient applications. Geo-redundancy helps simplify this process by enabling supported application content and configuration to be synchronized from your primary web app to regional replicas. Rather than coordinating every regional application deployment independently, you can deploy supported updates to your primary application and manage their synchronization across regional replicas. The preview also introduces revision-management capabilities that help you: Inspect application revision and synchronization status across regions. Control when supported application revisions are synchronized. Validate application revisions in regional replicas. Retain a validated last-known-good revision for a replica where supported. These capabilities give application teams greater visibility and control over regional application versions, helping reduce the complexity of coordinating deployments across multiple Azure regions. Applications should still be validated in each region, including their dependencies and regional configuration. Changes made outside supported deployment workflows may require an explicit snapshot or synchronization action. Build resilience across your application architecture Geo-redundancy simplifies multi-region application hosting on Azure App Service, but resilient applications also depend on the availability of their underlying services. Databases, storage accounts, secrets, networking, external APIs, and other application dependencies must be designed and configured with appropriate regional resilience. For example, an application replica may be healthy and available in another region, but it still needs access to the data and downstream services required to process requests. Geo-redundancy does not automatically replicate databases, Azure Storage, Azure Key Vault, live runtime state, or external dependencies. Customers remain responsible for designing and testing the resilience of these services, including data consistency, regional connectivity, and recovery behavior. Geo-redundancy simplifies the application hosting layer of your resilience architecture, allowing your team to focus on the broader application and data resilience strategy. Get started with Geo-redundancy in public preview The public preview of Geo-redundancy is initially available for eligible Windows web apps running on Premium v3 and Premium v4 App Service plans in supported multitenant Azure regions. Getting started involves five steps: Choose your application and regions. Review preview eligibility, supported configurations, and regional availability. Add a regional replica. Configure Geo-redundancy for an eligible web app and select a supported Azure region. Configure traffic routing. Choose Active or Passive mode and configure the appropriate regional weights or priorities. Synchronize and validate your application. Verify supported application content, configuration, and revision status across regions. Test your resilience strategy. Validate endpoint health, regional failover, recovery behavior, and the availability of application dependencies. Before enabling the preview, review the published support matrix for supported regions, application configurations, custom-domain requirements, and known limitations. Pricing Geo-redundancy introduces a per-enabled-application monthly charge in addition to the App Service compute charges associated with the primary application and regional replicas. For current pricing and billing details, see Azure App Service pricing. Take the next step toward multi-region application resilience Building regionally resilient applications shouldn't mean building and operating your own multi-region application deployment and traffic-management solution. With Geo-redundancy in Azure App Service, we're making it simpler to extend applications across Azure regions, coordinate application revisions, and configure regional traffic routing and failover. The public preview is an opportunity to explore a simpler approach to multi-region application hosting, with more integrated management and greater control over regional application behavior. Ready to explore what's possible? Explore Geo-redundancy in Azure App Service and get started with the public preview.174Views0likes0CommentsModernize more Windows applications with Managed Instance on Azure App Service
For many organizations, the hardest part of modernizing a Windows web application isn't moving the code. It's understanding the dependencies that tie the application to its current server: installed components, registry settings, Windows services, network shares, and other operating system configuration. Since Managed Instance on Azure App Service became generally available in August 2026, we've continued investing in ways to make these migrations easier to discover, assess, and execute. At Microsoft Ignite 2026, we're highlighting three updates: Azure Catalyst support, Premium v3 availability, and Isolated v4 support. Together, they make Managed Instance easier to include in portfolio-scale modernization plans and give customers more flexibility in choosing where to host eligible applications. Start with discovery: Azure Catalyst support for Managed Instance Modernization begins with understanding which applications you have and which Azure destination fits their requirements. Applications with Windows-specific dependencies may have been ruled out for conventional App Service migrations, leaving teams to choose between extensive rewrites and continuing to manage virtual machines. Azure Catalyst support for Managed Instance helps bring this hosting option into migration discovery and assessment workflows. Teams can revisit Windows web applications that were previously considered unsuitable for standard App Service hosting, assess their dependencies, and evaluate whether Managed Instance is an appropriate destination. This supports a more repeatable modernization approach: Discover Windows application workloads across the estate. Assess application and infrastructure dependencies, using Azure Migrate and available assessment tooling. Identify candidates whose requirements align with Managed Instance capabilities. Validate one representative application in a non-production environment. Expand from a proven migration pattern to a wider application portfolio. Azure Catalyst assessment informs the decision; it does not guarantee compatibility or eliminate the need to test installation scripts, networking, configuration, and application behavior. Managed Instance also complements Azure Catalyst in GitHub Copilot modernization for .NET, which can help teams assess, remediate, validate, and deploy suitable applications. More hosting flexibility: Premium v3 availability Managed Instance initially emphasized Premium v4 hosting. We're expanding the options with support for Premium v3 and Premium v3 memory-optimized plans in enabled regions. This gives customers an additional path where Premium v4 regional capacity or availability would otherwise constrain a modernization project. It also allows teams to consider a broader set of App Service compute options when balancing workload needs, capacity, and cost. Premium v3 availability is being enabled across eligible App Service infrastructure over time. Dedicated hosting: Isolated v4 support We're also expanding Managed Instance to Isolated v4 App Service plans in App Service Environment v3. This brings Managed Instance capabilities to a single-tenant App Service hosting environment for organizations whose architecture calls for dedicated hosting and network isolation. It offers another modernization option for eligible Windows web applications with installed components, operating system customization, or other supported dependencies. Isolated v4 expands the choice of hosting environment; it does not mean arbitrary server administration or that every Windows workload is supported. Customers should validate Managed Instance feature boundaries, region support, networking, and application dependencies before migration. Why Managed Instance matters Managed Instance on Azure App Service is designed for Windows web applications that need more operating system customization than conventional App Service hosting offers, while retaining managed platform benefits such as patching, scaling, diagnostics, and identity integration. Capabilities include: - Configuration scripts for supported installers, components, Windows features, and services. - Registry adapters for supported application configuration. - Storage mounts for required file-share and drive-letter scenarios. - Secure RDP through Azure Bastion for diagnostics and familiar Windows tools. - Managed identity and Azure Key Vault integration for securely accessing supported resources and secrets. Managed Instance is intended for eligible Windows web applications. It is not a Linux or container hosting option, nor a replacement for a fully customizable Windows virtual machine. From one application to a modernization portfolio These updates connect the key stages of modernization: - Discover and assess: Use Azure Catalyst and application assessment tools to identify candidates. - Modernize where needed: Use GitHub Copilot modernization for .NET and targeted changes to address compatibility gaps. - Choose the hosting model: Evaluate Managed Instance on Premium v3, Premium v4, or Isolated v4, subject to region and plan support. - Migrate and operate: Validate dependencies and deploy to App Service with managed operational capabilities. A practical first step is to revisit one Windows web application previously excluded from App Service because of its dependencies. Assess it, validate its fit, and use the lessons learned to inform a repeatable approach for similar applications. Get started - Managed Instance quickstart - Managed Instance configuration documentation - Managed Instance samples and configuration scripts - Managed Instance overview on Microsoft Learn Revisit applications that previously seemed too complex for App Service. With Azure Catalyst support and more hosting choices, Managed Instance can help you move more of your Windows application portfolio to a managed platform with fewer changes.74Views0likes0CommentsWhat's new in Azure Container Apps at Ignite'26
Azure Container Apps (ACA) is a fully managed serverless container platform that enables developers to design and deploy microservices and modern apps without requiring container expertise or needing infrastructure management. With built-in autoscaling (including scale to zero), per-second billing, advanced networking, and built-in observability, ACA lets teams focus on their code instead of their clusters. Since Build’26 we have continued to innovate on two fronts: Azure Container Apps Sandboxes, which provide secure, isolated environments where agents can run untrusted code, and the infrastructure behind Microsoft’s agent platforms that customers can use to build their own agent platform, and Azure Container Apps Express, the fastest way to deploy a container image as an internet-reachable app, with no environment to provision. Both are now generally available, and this blog covers everything we are announcing at Ignite’26. The agentic world is changing the workloads coming to ACA Agents don’t just answer questions anymore; they run code, call tools, deploy endpoints on demand, and work for hours on a task. That shifts what platforms need to deliver: instant startup, strong isolation for code nobody has reviewed, scoped identity and network access, and the ability to scale to zero and back when the work is done. ACA was built for exactly this shape of workload, and customers across industries are building on it: Nous Research runs Hermes Agent workloads on ACA Sandboxes, where agent execution happens in isolated microVMs that start in under a second and release compute when idle Discovery Bank runs its agent-assist and Discovery AI applications on Azure Container Apps, hosting lightweight APIs, business logic, and orchestration that connect its contact center, Azure Databricks, and Azure OpenAI to deliver personalized banking experiences with scalable, low-latency responses Crowe uses ACA autoscaling workers to asynchronously process lease documents, extract and verify key terms, and deliver audit reports that flag higher-risk leases for human review Photon Education uses ACA alongside Azure Functions to run specific Classwise microservices, separating content management, real-time interactions, and background processing from the core app so AI-powered classroom features stay responsive and reliable Ghassan Aboud Holding runs the GrandChef AI shopping agent and its APIs on ACA, which scales with demand and powers recipe and preference-based product recommendations and cart building in the Grandiose app BKW uses ACA as part of an Azure-native MCP server that makes AI weather and geospatial insights available to agentic workflows, supporting energy and infrastructure decisions with human oversight WTW uses ACA as a scalable hosting environment for Radar Vision’s application services, supporting its event-driven platform that analyzes insurer performance and delivers near-real-time, AI-generated insights to pricing, underwriting, and claims teams Templafy uses ACA Sandboxes to give an AI agent isolated, disposable workspaces where it can clone repositories, run tools, and explore code to answer engineering and product questions without exposing internal systems Azure Container Apps Sandboxes are now generally available Introduced in preview at Build’26, ACA Sandboxes are now generally available. Sandboxes are a first-class resource type alongside apps, jobs, and dynamic sessions, enabling you to build your own agent platform with your choice of framework, lifecycle services, and governance, designed with zero-trust security provisions. Each sandbox is an isolated microVM that boots from cached images in under a second, can be suspended with its full memory and disk state snapshotted, and resumes in under a second. Stopped sandboxes incur no compute charges, and a single sandbox group can burst to thousands of concurrent sandboxes. The GA release includes lifecycle controls, snapshots, an egress proxy with host allowlists, deny policies and credential injection, virtual network integration, persistent volumes, and telemetry export, along with the Python and TypeScript SDKs, the aca CLI, Bicep, and a preview Terraform provider. Sandboxes are quickly becoming the Azure standard for customers to build agent platforms and multi-tenant SaaS. The same infrastructure already runs cloud sandboxes in GitHub Copilot, Foundry Hosted Agents, Azure SRE Agent, and Azure Container Apps Express. The pattern is simple: govern the agent in Microsoft Foundry, and let its work run in a disposable sandbox with scoped identity and network access. To get started, see the Sandboxes overview. Azure Container Apps Express is now generally available ACA Express, which we introduced in preview in May, is now generally available. You bring a container image, and Express handles the rest: no environment to provision, no networking to configure, and no scaling rules to write. Apps are running in seconds, start from zero in well under a second, scale to and from zero automatically, and are billed per second. Express runs on Azure Container Apps Sandboxes and is available in more than 40 Azure regions. ACA Express is gaining momentum since launch, with customers creating Express apps across thousands of Azure subscriptions, growing at >35% MoM. Alongside this new adoption, we’re automatically moving eligible existing apps to Express, so more customers can benefit without needing to manage the transition themselves. These migrations are designed to improve performance while preserving the features and capabilities those apps already use. Express is getting closer to feature parity with Consumption, and the rest of the features are coming soon. Express is purpose-built for developers who want to ship fast (SaaS apps, APIs, web dashboards, and prototypes) and for agents that deploy on demand (MCP servers, tool-use endpoints, and human-in-the-loop UIs). To learn more, see the Express overview. Introducing built-in interactive integration of Azure SRE Agent in Azure Container Apps ACA has built-in integration with Azure SRE Agent. The Container Apps portal now has a first-class experience for interactive debugging with SRE Agent, launched in preview. Developers can start a session from any container app and get evidence-backed, actionable root cause analysis and expert answers in minutes, with nothing to deploy. Each session is serverless and on demand. It starts in seconds, stays focused on your question, and ends when you’re done. ACA is the first Azure service to bring this experience to customers, and we plan to extend it to more services in the future. Getting started takes a click. Select Debug with Azure SRE Agent on any app and ask your question in your own words, for example “Why did my latest revision fail to start?” or “Why is my app scaling out so often?” The agent already knows which app you are looking at, asks for your approval before it reads anything, and then works through your app’s configuration, revisions, deployment history, Azure Monitor metrics, and Log Analytics logs, much like an experienced SRE would. It runs read-only with your own Azure identity, so it never changes your resources and only proposes fixes, and each session runs in an isolated sandbox that is deleted when the session ends. When an issue needs more help, the agent can draft a support request for you to review and submit to Azure Support, or you can deploy Azure SRE Agent right from the session to bring that intelligence to your entire environment. Azure Container Apps is now a target in Azure Migrate We are announcing that Azure Container Apps is now available as a target in Azure Migrate. Azure Migrate can discover and assess Java web apps running on Apache Tomcat and .NET web apps running on .NET Core, and help you plan the move to ACA with a wave plan. The migration then continues in GitHub Copilot app modernization, which handles code changes, containerization, and deployment. Together they give teams a single path from discovery to a running container app. See Migrate to Azure Container Apps with Azure Migrate to learn more. Additional Enhancements and Ecosystem Updates More regions: Since Build’26 we have continued to expand ACA’s global footprint, adding six new regions: Germany North, New Zealand North, Chile Central, Korea South, Belgium Central, and Jio India Central. Express is available in more than 40 Azure regions. New tooling in VS Code: Azure Container Apps Sandboxes are now integrated directly into Visual Studio Code, making it easier to create and manage secure, isolated environments without leaving your development workflow. Developers can execute commands, create snapshots, and manage sandbox lifecycle directly from the ACA extension. Bring your own orchestrator to ACA Jobs: ACA Jobs are a great fit for batch processing, ETL, machine learning, and other tasks that run to completion, but many teams already have an orchestrator. The new Bring Your Own Orchestrator collection provides 13 community-maintained templates for connecting the workflow engine you already use, such as Airflow, Temporal, Argo Workflows, Dagster, Prefect, Durable Functions, and Logic Apps Standard, to ACA Jobs. You keep your control plane, and ACA Jobs runs the work on serverless, scale-to-zero infrastructure. Join us at Ignite and stay in touch We have a full lineup of sessions at Ignite’26. Come meet the ACA team, see demos of Sandboxes, Express, and Azure SRE Agent, and hear from customers running agents in production. Breakout 448: Run secure agent loops in production with isolated sandboxes at scale Lab 722: Operate secure, multi-tenant agentic apps on Azure Container Apps Theater Session 901: The agentic path from legacy apps to AI-native on Azure Container Apps Lightening Talk 1279: Deploy AI apps effortlessly with Azure Container Apps Express Theater Session 1026: Your existing apps, your next decade of cloud-native Lightening Talk 1293: Design serverless architectures for speed, cost efficiency and AI apps Table Talk 1847: Lessons learned: What it takes to run AI agents in production Breakout 423: Build AI-native with Azure's agentic application platform Can’t make it? We want to hear from you either way. Share feedback, ask questions, and follow our roadmap and monthly product updates on the Azure Container Apps GitHub repository, and open an issue to tell us what you want to see next. Thank you for building with Azure Container Apps.245Views2likes0CommentsIntroducing Azure App Service Builder (Public Preview)
This is a summarized version of the full post which can be found here: Introducing Azure App Service Builder: From code to a running app Builder brings application builds, hosting, and deployment management into one app-focused workflow. Connect an authorized GitHub repository for source-based builds or deploy a ZIP package, track deployment progress, and open your app at its service-provided URL. The initial preview focuses on static sites, web applications, and HTTP APIs. Whether you write code directly or work alongside an AI coding agent, Builder helps reduce the setup and handoffs between development and deployment so you can spend more time building and iterating on your application. A new option alongside the App Service you use today Builder does not replace existing Azure App Service experiences. Those experiences remain available and supported, and there is no requirement to move an existing application. Builder offers a new starting point for applications where a streamlined code-to-app workflow is a priority. The public preview is intended for development and test workloads, has no financially backed SLA, and is not recommended for production workloads. Supported regions, runtimes, workflows, and resource limits apply. Read the full announcement For a walkthrough, more on how Builder fits alongside existing App Service experiences, and what to expect during preview, read Introducing Azure App Service Builder: From code to a running app on the App Service Builder blog. Ready to explore? Visit the Builder portal and the App Service Builder documentation to get started.394Views0likes0CommentsInside the architecture: How connectors work with Azure Functions
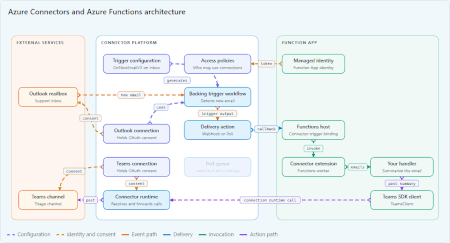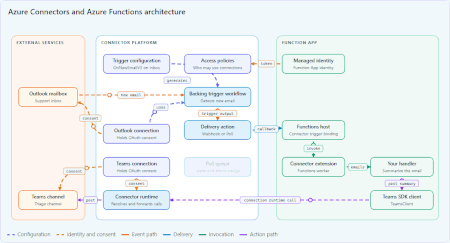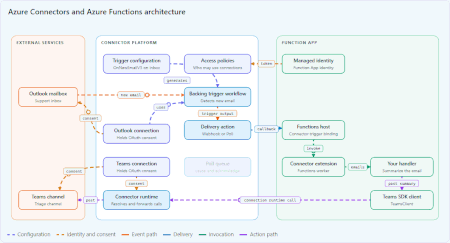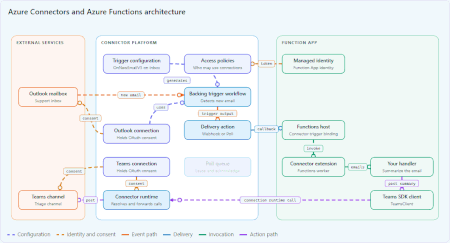
Say you run a shared support inbox. Each time a customer writes in, you want a function to read the email, pick out the important parts, and post a summary in your team's Teams channel. The business logic might be twenty lines. The rest is authorization, change detection, event delivery, and a second set of permissions to post in Teams, and you rebuild most of it for every service you touch. Azure Connectors and the Connector SDKs take that work on. The platform manages connections and authorization. The same app can react to events in one service and call operations in another. Webhook and poll delivery give you push or pull, so you can pick what fits your app. One SDK per language covers the Connector catalog with typed operations and payloads, VS Code tooling handles setup, and SDKs are available for .NET, Python, and Node.js from day one. Underneath those promises are a handful of pieces we built and a few decisions about where each one stops. The support inbox runs through all of them. Follow that one email from Outlook to Teams, and you'll know exactly how to wire up the next hundred integrations yourself. Starting from what Azure already has Azure already runs more than 1,600+ managed Connectors to services like Salesforce, SAP, SQL Server etc. They power Azure Logic Apps and Power Automate, and API Hub hosts their connections, OAuth consent, and runtime. Logic Apps already knows how to run Connector triggers, whether the source sends notifications, accepts a webhook subscription, or has to be polled. So we didn't write a second integration for each service. We built a new front door to the existing Connector runtime, one that application code can use directly, and added the glue Azure Functions needs on top. Most of the new work falls into four areas: A control plane, the Connector Namespace, that exposes connections, access policies, and trigger configurations as Azure resources. A runtime layer that proxies SDK calls into API Hub and turns trigger configurations into system-managed workflows with a delivery step at the end. A Functions Connector extension, with host and worker pieces, that receives events by webhook or by polling and feeds the Functions scale controller. One code generator that emits typed SDKs for .NET, Python, and Node.js from live Connector metadata, plus tooling that sets everything up. The control plane: Connector Namespace A Connector Namespace is an Azure Resource Manager resource of type Microsoft.Web/connectorGateways. Under it sit three child resource types: connections, connection access policies, and trigger configurations. Because they're ARM resources, you can create them with Bicep, the CLI, or the VS Code tooling, and they get the usual Azure role-based access control and lifecycle. A connection is the application-facing name for a backing API Hub connection, the same kind Logic Apps uses. The consent you grant for Outlook lives there. An access policy lists the Microsoft Entra identities, such as a Function App's managed identity, that may use a connection. That split means the identity that calls the connection and the account that consented to the mailbox are separate, and you can change one without touching the other. Authorize the connections: the Function App's managed identity presents a token to the access policies, and the Outlook and Teams connections hold OAuth consent for their accounts A trigger configuration describes an event source. Its properties include the connection, the Connector operation (for the support inbox, OnNewEmail), the operation's parameters, optional trigger conditions and settings, and a delivery mode. For webhook delivery it carries the callback details; for poll delivery the service fills in the polling endpoints. Each namespace also gets a stable host name, and a background job repairs its DNS record if it drifts. The action path: a proxy into API Hub When your handler posts the summary to Teams, the generated SDK client sends an HTTPS request to the connection's runtime URL. On the platform side that URL maps to `api/connectorGateways/{gateway}/connections/{connection}/runtime`, followed by the operation's own path. Behind that route, the runtime processor handles each request in four steps: It resolves the application-facing connection to its backing API Hub connection and environment, in the namespace's scale unit. It builds the API Hub runtime URL and checks that the requested path stays inside that connection, so a caller can't reach a different connection by rewriting the path. It strips identity headers supplied by the caller and attaches a platform service token, plus headers that pass the caller's managed identity through. It forwards the method, path, query, and body to API Hub, which runs the Connector operation against Teams. The caller authenticates with a Microsoft Entra token for the API Hub audience. In the Node.js SDK the default scope is `https://apihub.azure.com/.default`, and the token comes from any Azure Identity TokenCredential, typically the Function App's managed identity. The SDK side is thin on purpose. Generated clients extend a shared base class that holds the runtime URL and credential. A shared HTTP pipeline built on Azure Core adds the token, a user agent, tracing, and retries. Retries apply by default only to safe methods such as `GET` and `HEAD`, because retrying a `POST` that sends a message could send it twice. Paged operations follow `nextLink` values. When a continuation link points at a different host, as some Connector back ends return, the SDK reroutes its path and query through the connection's runtime URL, so paging stays behind the proxy. Failures surface as a ConnectorExceptions that carries the Connector name, the operation, the status code, and the response body. The trigger path: system-managed workflows When you create a trigger configuration, the trigger API validates the request, generates a Logic Apps workflow definition, creates the workflow directly in a platform-owned subscription under a generated name, and stores the workflow details alongside the trigger configuration. Updates rewrite the workflow, and deleting the trigger configuration removes the workflow, its poll queue, and its message history. The workflow generator picks the right trigger shape for the operation's metadata: a notification subscription, a webhook subscription, or a recurring poll. It adds `splitOn` for operations that return batches, so each item becomes its own run unless the configuration opts out, and it applies any trigger conditions you set. The workflow ends with a Connector delivery action. We generate a workflow per trigger configuration because Logic Apps already has years of hardening around subscription renewal, polling state, and trigger history, and every Connector trigger already runs on it. The workflow stays an implementation detail: customers work with the trigger configuration resource and never see or edit the workflow. Two ways to deliver an event How the platform notices a new email and how the event reaches your function are separate problems. The backing workflow handles the first. The delivery action at the end of the workflow handles the second, and it supports two transports. Webhook delivery For webhook delivery, which is the default, the delivery action makes an HTTPS call to the callback in the trigger configuration, using the workflow engine's HTTP retry policy. On the Function App side, the callback is the host's `/runtime/webhooks/connector` route, protected by a system key named `connector_extension`. A `functionName` query parameter selects the function. The host returns `202` when the invocation succeeds, `400` for a missing or invalid name, `404` for an unknown function, and `500` when the invocation fails. Poll delivery For poll delivery, the delivery action writes the event to an Azure Storage queue owned by that trigger configuration and records it in a message history table. Storage queue messages are limited to 64 KB, so when an event is larger the action queues a reference to the workflow run's output instead of the output itself. The poll runtime API sits in front of the queue and has four operations: `receive`, `acknowledge`, `hasMessages`, and `approximateQueueDepth`. `receive` hands out events under a temporary lease with an opaque lock token. `acknowledge` deletes an event only when the message ID and a still-valid lock token match. If the lease expires first, the event becomes visible again. The reported depth is approximate and excludes leased messages. Deliver the event by Poll: the delivery action enqueues the event, and the Functions host receives and acknowledges it from the Poll queue Poll delivery means the Function App never exposes an inbound endpoint, and work can build up safely when the app is busy, scaled to zero, or running on a developer's laptop. Inside Azure Functions: the connector extension The Functions side has two layers. A host extension, written as a WebJobs extension, owns transport and scaling. A worker extension for each language turns payloads into typed objects for your handler. The host extension The host extension registers a connectorTrigger binding. Each function picks webhook or poll delivery, and the binding starts the matching listener. Backoff: an empty queue backs off with jitter, up to a configurable maximum interval; receive failures get their own capped backoff. Auth: the listener authenticates to the polling endpoint with the connection's credential, usually the Function App's managed identity. Concurrency: a function that takes one event at a time can run several invocations in parallel, up to `MaxConcurrentCalls`. A batched function processes one batch at a time per listener. Acknowledgment: an event is acknowledged only after its invocation succeeds; a failed invocation leaves it unacknowledged so it comes back when the lease expires. Large outputs: when an event holds a link to a large output, the listener downloads it, with a 100 MB default cap. Poll delivery also plugs into Azure Functions target-based scaling: The Connector trigger reports how much work is waiting by reading the queue's approximate depth through the same poll runtime API. Azure Functions does the scaling, aiming for `ceil(depth / target)` instances. The target is the function's pending-event threshold, or the per-instance concurrency that the platform supplies when it has one. Batch size and concurrency don't change that calculation. Batching therefore happens in several places. The source trigger can return a collection, `splitOn` can split it into separate runs, and the poll listener can deliver several events to one invocation. The batch settings have the same meaning in every language: Setting .NET isolated Python Node.js Receive several events per invocation IsBatched = true cardinality=func.Cardinality.MANY cardinality: Cardinality.Many Maximum events per invocation MaxBatchSize max_batch_size maxBatchSize Concurrent single-event calls MaxConcurrentCalls max_concurrent_calls maxConcurrentCalls Pending events per instance, for scaling TargetPendingEventThreshold target_pending_event_threshold targetPendingEventThreshold The batch size can be 1 through 32 and defaults to 1. The worker extensions Because the host extension does the transport work, each language worker only has to bind payloads. The .NET isolated worker extension deserializes the payload into the type your function declares, such as a generated Office365OnNewEmailTriggerPayload, or into `ConnectorEvent<T>[]` when you also want each poll message ID. Python functions use the connector_trigger decorator from the azure-functions library. Other workers reach the same host extension through the Functions extension bundle and the connectorTrigger binding type. The Node.js extension shows how thin this layer is. One generic wrapper registers the trigger and flattens every payload shape (a single item, a collection in `body.value`, or an array of poll envelopes) into one list of items, keeping the original in `rawPayload`. Each Connector's helper is then a few lines that add a friendly alias and borrow the item type from the generated SDK. This is the whole OneDrive for Business file: import { BlobMetadata } from "@azure/connectors/generated/OneDriveForBusinessExtensions"; import { OneDriveFileTriggerContext } from "../../types"; import { createConnectorTrigger } from "./createConnectorTrigger"; const registerFileTrigger = createConnectorTrigger<BlobMetadata, OneDriveFileTriggerContext>( (context) => ({ ...context, files: context.items }), ); export const onNewFiles = registerFileTrigger; export const onUpdatedFiles = registerFileTrigger; `BlobMetadata` comes from the same generated module that the OneDrive client uses for actions, so a trigger payload and an action response share one type, defined once from the connector's metadata. Calling out from the handler After reading the email, the handler posts a summary to Teams. That call leaves the Function App through the same Connector platform, going the other way. The handler calls a generated Teams client with typed input. The client holds the Teams connection's runtime URL and an Azure Identity credential, gets a Microsoft Entra token, usually for the Function App's managed identity, and sends the request. The Function App never holds a Teams token or secret. The connection's access policies decide whether that identity may use the Teams connection, and the connection holds the OAuth consent for the account that posts. The Connector runtime resolves the connection, replaces the caller's identity headers with a platform token, and runs the operation against Teams. This path doesn't depend on how the email arrived, so it works the same with webhook or poll delivery and with any Connector in the catalog. Idempotency is the handler's job. The SDK won't retry a failed post, but a redelivered event runs the whole invocation again, so the handler should check before posting the same summary twice. One generator, three SDKs The SDKs are generated. A shared generator, `CodefulSdkGenerator`, reads live Connector Swagger definitions through Azure Resource Manager, cleans them up, and emits clients for C#, Python, and TypeScript. Each SDK repository records what produced it in a generation manifest: the generator commits, the metadata API version, and a hash of every Connector's Swagger input. That makes each regeneration traceable to a specific generator revision and a specific set of Connector definitions. Besides action methods, the generator emits models for request and response bodies, typed trigger payloads and trigger operation constants, catalog constants that list the available Connectors, and support for paging and dynamic schemas. Each language then has a small handwritten runtime (the base client, the HTTP pipeline, errors, and paging) that the generated code builds on. Naming rules are kept consistent across languages, so the same Connector and operation have recognizable names whether you write C#, Python, or TypeScript. For setup, the VS Code connection manager and the connection-setup skill create the namespace and connection through the ARM preview API, open the OAuth consent page and check that the connection reports `Connected`, add access policies for your developer identity or the Function App's managed identity, and write the runtime URLs into local or deployed app settings. Recap When a customer writes in, the backing workflow detects the email through API Hub's existing Connector trigger. The delivery action then either calls the Function App's webhook or writes to a per-trigger storage queue that the host extension polls and scales on. The language worker binds the payload to a type that came from the same generator as the SDK, and the handler uses a generated Teams client whose calls go through the namespace's runtime proxy into API Hub. Each piece reuses what was already there: the Logic Apps workflow engine for triggers, API Hub for connections and Connector runtime, the Functions extension model and scale controller for hosting, and Azure Identity for credentials. The new parts are the namespace resources that tie them together, the delivery step, the Functions extension, and the generator that keeps every language's types in step with the Connectors themselves. References Connectors SDKs Language Repository .NET Azure/Connectors-NET-SDK Python Azure/Connectors-Python-SDK Node.js Azure/Connectors-NodeJS-SDK Azure Functions connector extensions Component Repository Host extension and .NET isolated worker extension Azure/azure-functions-connector-extension Python worker extension azurefunctions-extensions-connectors Node.js worker extension azure-functions-nodejs-extensions-connectors Samples Sample Repository .NET email triage into Teams Azure-Samples/functions-connectors-net-e2e-email-users-teams .NET connector samples Azure/Connectors-NET-samples Python connector samples Azure-Samples/functions-connectors-python TypeScript connector samples Azure-Samples/functions-connectors-typescript Note: The connector platform internals described in the post (the resource model, runtime proxy, trigger workflows, delivery action, and Poll runtime API) aren't in a public repository, so they have no links here.232Views3likes0CommentsRun on your schedule: App Service plan start/stop now in public preview
Start and stop your apps together Managing an environment with multiple apps shouldn't mean stopping and starting each app individually. App Service plan start/stop brings that control to the plan level, letting you manage the apps and deployment slots it hosts together. Today, we're announcing the public preview for this feature for Premium v4 (Pv4) and Premium memory-optimized v4 (Pmv4) plans. Stop the plan to take its workloads offline, then start it again when you're ready, without issuing separate commands for each app. NOTE: Start and stop operations are asynchronous: the apps on your plan don’t all stop or become ready to serve requests immediately. After you stop a plan, app shutdown and cleanup can continue over the next few minutes. When you start it again, allow time for your applications to become ready before sending traffic. This is particularly useful for development, test, and demo environments that share an operating schedule. Because the operation affects the entire plan, make sure every hosted workload can tolerate the interruption. To bring workloads on a stopped plan back online, start the plan rather than an individual app. Get started with Azure CLI You can call the start and stop REST operations using az rest . Sign in to Azure, select the subscription containing your plan, and set its resource group and name: resourceGroup="[RESOURCE-GROUP-NAME]" planName="[APP-SERVICE-PLAN-NAME]" planId=$(az appservice plan show \ --resource-group "$resourceGroup" \ --name "$planName" \ --query id --output tsv) || exit 1 # Stop the plan. All hosted apps and deployment slots will be unavailable. az rest --method post --url "https://management.azure.com${planId}/stopSites?api-version=2026-07-15" When you're ready to run the workloads again, start the plan: az rest --method post --url "https://management.azure.com${planId}/startSites?api-version=2026-07-15" Plan for application startup time before sending traffic back to the environment. A successful API response isn't a substitute for checking that your applications are ready to serve requests. Get started with the Azure portal You can also use the Azure portal to start and stop your plans. On the App Service plan Overview page, select start and stop as you may have done for your individual apps. If you try to start an app when its App Service plan is stopped, you will get an error letting you know to start the App Service plan instead. NOTE: This feature is rolling out in the portal over the next few weeks. If you don't see the option in the portal yet, check back in a couple days and use the Azure CLI in the meantime. Billing considerations Compute billing for an eligible plan pauses when the plan is stopped, even though app shutdown and cleanup can continue over the next few minutes. Compute billing resumes when the plan is started. Charges for other resources and services can continue. Preview limitations and considerations Supported tiers: Premium v4 and Premium memory-optimized v4 only. Other App Service plan tiers aren't supported. Availability: All public regions that support Premium v4 Plan-wide impact: All apps and deployment slots on the plan are affected. Don't stop a plan that also hosts workloads that must remain available. Restart at the plan level: Attempting to start an individual app will not restart the plan. You must restart the plan to restart the apps. Automatic scaling: Plans with App Service automatic scaling enabled aren't supported. This is distinct from Azure Monitor autoscale. Scaling in progress: Wait for an in-progress asynchronous scale operation to finish before starting or stopping the plan. Start/stop throttling: Plan start and stop operations are subject to a five-minute throttle. Account for this when scheduling operations or testing repeated start/stop cycles. Changes while stopped: Start the plan before scaling it or making other plan updates. Try the preview Try start/stop on a development or test plan whose apps share an operating schedule. Review the apps and deployment slots it hosts, then use the plan-level commands to stop and start those workloads together instead of managing each app individually. For the API details, see Stop Web Apps and Start Web Apps.273Views0likes0Comments
Can't access http context user claims in Azure Function
Background: Create an Azure Function (.NET Core & C#) that will be consumed in a SPO App. We created an Entra App Registration for the Azure Function and added App Roles for this App Registration where the App Role is using “Users/Group”, but not “Application”. Issue: In the SPO App (deployed in SPO Page), we can see the user claim and App Registration’s - App Role in the context of the user that’s hitting the SPO Page (thru Authorization header), however, in the Azure Function code the req.HttpContext.User.Claims object is empty. So what is required or missing from a configuration perspective either in the Azure Function or App Registration to make this work?495Views0likes2Comments
How do I sign out of my OIDC Entra ID Application?
We have an application protected with Entra ID using ODIC. To sign into our application or SPA goes through a series of redirects before getting a JWT and refresh token at the end of the Entra ID OIDC authentication flow. All of that works great. When a user is done with our application, we want them to be able to sign out of our application. In our mind, that means invalidating the `refresh_token` they received when signing in. We're not seeing an OAuth endpoint to do that. Given the default lifetime for the refresh_token, I'd rather not simply ignore/discard it as it could be used to generate a new JWT (however unlikely). I am posting this on here after searching the web for several hours. All I am able to find on the web is single sign-out (SLO), which would sign my user out of all of Office 365 when they sign out of our application. That is not what I want. How do I invalidate the user's `refresh_token`? Is there a "revoke" endpoint in Entra ID? If not, then what other options do we have?428Views0likes2Comments