security
19 TopicsEstablish a macOS security baseline with mSCP and Microsoft Intune custom compliance
By: Iris Yuning Ye, Product Manager | Microsoft Intune Organizations that manage Mac devices need a reliable way to evaluate their security posture against a recognized baseline. Microsoft Intune custom compliance provides the device compliance evaluation policy, and the National Institute of Standards and Technology’s (NIST) macOS Security Compliance Project (mSCP) provides macOS security rules and checks mapped to compliance requirements. Earlier this year we released Intune custom compliance for macOS devices. The feature uses a discovery script and JSON file to define compliance settings. With the mSCP command-line tool, you can select and tailor a security baseline, generate a macOS discovery script, and pair the discovered identifiers with an Intune rules JSON file. Intune then evaluates each device against the chosen baseline and uses the result in compliance reporting and Conditional Access decisions. In this blog, we’re introducing a JSON conversion script (mscp_to_intune_json_conversion.sh). The script converts the mSCP’s generated vendor manifest into the JSON format required for Intune custom compliance. Prerequisite Before you begin, set up the mSCP locally by following the NIST guidance: Getting started with the macOS Security Compliance Project. Create a security baseline Next, we’ll establish and configure the security baseline on the device. Select your security baseline: Choose a security baseline your organization intends to evaluate devices against by looking through frameworks supported by mSCP (for the example in this blog we’ll use CIS Level 1) Configure your baseline: When creating the baseline for the first time, you'll follow a guided process to specify the name of the custom baseline, your name and organization, choose what specific rules to include or exclude. Once the customization process is completed, a new baseline file containing all the rules you specified is generated under the custom/baselines/ directory as a YAML file. ./mscp.py baseline –k cis_lvl1 –t Note: The command uses the following flags: -k Specifies the keyword. In this example, we're using cis_lvl1 . -t Enables tailoring, allowing you to select specific rules to include and define organization-specific values. Once the baseline YAML file is generated, run the command below to generate mSCP documents. These files will be saved into a build/[your specified project name] directory. ./mscp.py guidance –s –M [yaml file location] The yaml file location should be the relative location on top of your mSCP folder. Note: The command uses the following flags: -s Generates the compliance script. -M Generates the JSON vendor manifest file. Once the JSON Vendor Manifest and compliance script are successfully generated, we highly recommend running a test check to verify that all rules and values are defined as expected. Note: If you're using the container method, exit the container to proceed to run the check. (Exit container: NIST macOS Security Getting Started) The key is to locate where you build folder is and where the .sh file was saved in: sudo ./[base folder]/cis_lvl1_macos_27.0/cis_lvl1_macos_27.0_compliance.sh --check Create mobileconfig file Create a mobileconfig file by creating a plain text file, then copy and paste the example in GitHub into it. Configure the .mobileconfig profile Update the PayloadType key to match the audit file name. This ensures the compliance script uses the correct managed arguments when running. Example: In our demo, the value is updated to: org.intune_compliance_lv1_macOS_26.0.audit Customize the following keys based on your organization's requirements and preferences: PayloadDescription PayloadOrganization PayloadDisplayName Test the .mobileconfig profile To verify the configuration, install the .mobileconfig profile locally on a test MacOS device. Open System Settings > General > Device Management. Select the + button to add a configuration profile. Navigate to the saved .mobileconfig file, select it, and click Open. Follow the prompts to Continue and Install the profile. Note: Administrator privileges are required to install the device profile. Validating the Results: Once the profile is installed, run the generated compliance script. If the script runs successfully and outputs JSON, the managed arguments are correctly set. Run the generated compliance script with no arguments specified to make sure it uses the managed arguments from the installed mobileconfig file. sudo ./[base folder]/cis_lvl1_macos_27.0/cis_lvl1_macos_27.0_compliance.sh Once testing is complete, remove the test profile for your local Mac. It’s critical to ensure all testing profiles are removed from target devices before deploying from Intune to avoid conflicts. You can deploy the custom mobileconfig profile for the managed arguments using Intune to the desired set of macOS devices. Important: Deploy the .mobileconfig file to target devices before deploying the custom compliance policy. Otherwise, the custom compliance policy may not run correctly. Use JSON conversion script Next, use the mscp_to_intune_json_conversion.sh script from GitHub to convert the mSCP JSON Vendor Manifest file into the specific JSON format required for Intune’s custom compliance policy. The command line is comprised of three parts: Locate where you saved the conversion script. Specify the JSON file from security baseline you intend to convert from. Specify the name of the custom compliance JSON file you intend to convert to. ~/ mscp_to_intune_json_conversion.sh [base folder]/cis_lvl1_macos_27.0/cis_lvl1_macos_27.0_compliance.json > intune_custom_compliance.json You can now upload the compliance script built by the mSCP that can be found in the build directory as your Discovery Script within Intune’s custom compliance policy. You can also upload the converted JSON file as the JSON for custom settings. Devices with the mobileconfig profile installed will run the compliance script using the managed arguments and output the JSON required for the custom discovery script. Keep in mind Start with a small pilot group and a focused baseline of your choice. Validate every identifier, returned data type, and expected value before broad deployment. Deploy mobileconfig file and make sure the file is already successfully deployed on target devices before custom compliance policy. Review the per-setting results in the Intune admin center > Reports > Device compliance -> Noncompliant devices and settings. Make sure the JSON file generated is aligned with other discovery scripts’ output to avoid misalignment errors. The recommended first step is to pilot one baseline on a small Mac device group, document the source version and rule mapping, and expand only after the discovery script output and Intune results have been validated. Conclusion The steps and scripts provided simplifies the flow to connect the mSCP with Intune’s custom compliance feature. By leveraging mSCP, organizations can efficiently translate recognized macOS security guidance into actionable, measurable compliance signals. While Intune provides the mechanism to capture identifiers and current device values, the rules JSON define the precise evaluation criteria. Together, these tools create a transparent, automated path from a high-level security baseline to detailed, device-level compliance reporting. A special thank you to Robert Gendler from NIST for authoring the mscp_to_intune_json_conversion.sh script and collaborating on this project. Disclaimer Collaboration on this post does not imply NIST endorsement of the products or services offered by Microsoft. Any mention of specific tools or software is for informational purposes and does not constitute a recommendation by NIST.796Views0likes1CommentMicrosoft Intune Settings Catalog updated to support Windows 11, version 26H2
10.06.26 Update: The Windows security baseline for Windows 11, version 26H2 is now available for all customers in Microsoft Intune. This baseline reflects current Microsoft security recommendations and is the latest available Windows security baseline in Intune. Windows 11, version 26H2 is now available, and Microsoft Intune provides day zero support for validated Windows policy settings in the settings catalog. We continue to invest in the settings catalog infrastructure to ensure timely support for new Windows policy settings. This enables organizations to adopt new OS versions and features without delay and maintain secure, compliant, and well-managed environments. Settings catalog support for Windows 11, version 26H2 As part of Windows 11, version 26H2 settings catalog support, the settings catalog now includes all newly released settings and updates to existing settings introduced with the latest Windows 11, version 26H2 release. The following table highlights settings that are now available for configuration in the settings catalog and ready to use in device configuration profiles for Windows endpoints. While this update aligns with Windows 11, version 26H2 support, not every setting listed is a new 26H2 feature; some are existing Windows settings that are now available for management through the settings catalog. Category Policy Name Friendly Name Above Lock ConfigureAudioOnLockScreen Configure Audio On Lock Screen Application Management EnableMsixAllowedZones Enable MSIX Allowed Zones Device Lock ClearTextPassword Clear Text Password Device Lock RelaxMinimumPasswordLengthLimits Relax Minimum Password Length Limits Printers ConfigureWindowsReadyPrintDriverRanking Configure Windows Ready Print Driver Ranking Privacy LetAppsAccessForegroundText Let Apps Access Foreground Text Privacy LetAppsAccessForegroundText_ForceAllowTheseApps Let Apps Access Foreground Text – Force Allow These Apps Privacy LetAppsAccessForegroundText_ForceDenyTheseApps Let Apps Access Foreground Text – Force Deny These Apps Privacy LetAppsAccessForegroundText_UserInControlOfTheseApps Let Apps Access Foreground Text – User In Control Of These Apps Windows Update IgnoreWindowsUpdateGroupPolicies Ignore Windows Update Group Policies Windows Update SetMaxPauseDays Set Max Pause Days What this means for administrators Administrators can find the new settings within the settings catalog in the Microsoft Intune admin center under Devices > Manage devices > Configuration > Create > New policy. Select Windows 10 and later for the platform and settings catalog for the profile type. Before deploying Windows 11, version 26H2: Review the new and updated settings that apply to your organization. Test configuration profiles with a representative device group. Confirm that the targeted Windows edition and version support each setting. Monitor profile deployment and device status after assignment. Windows 11, version 26H2 security baseline Windows 11 version 26H2 security baseline will also be made available shortly in Intune. We are validating the final recommendations and plan to make the updated baseline available over the coming days following the Windows 11, version 26H2 release. The current baseline includes: A new recommendation for Configure Windows Ready Print driver ranking. An updated Turn off encryption support recommendation that changes the supported Transport Layer Security versions from TLS 1.1 and 1.2 to TLS 1.2 and 1.3. Configure NetBIOS settings - This setting is pending availability in the settings catalog and will be added to the baseline in a future update. Learn more Create a policy using settings catalog in Microsoft Intune Windows 11 - release information Learn about Intune security baselines for Windows devices We welcome your feedback. If you have questions about these settings or Windows 11, version 26H2 management in Intune, leave a comment on this post or follow us on LinkedIn or @MSIntune and @IntuneSuppTeam on X to continue the conversation. Post updates: 10/06/26: The Windows security baseline for Windows 11, version 26H2 is now available in Microsoft Intune. We’ve also updated this post with the Settings Catalog additions introduced as part of Windows 11, version 26H2 support.5.3KViews1like7CommentsUnpacking Endpoint Management: Episodes Available On Demand
Over the course of the Unpacking Endpoint Management series, we brought together experts from across Microsoft Intune, Security, and Customer Experience teams to share practical strategies, lessons learned, and honest conversations about modern endpoint management. While the series has now concluded, the insights remain as relevant as ever. We invite you to explore past episodes on demand and continue connecting with the Intune community through Tech Community, Microsoft Learn, and future opportunities to engage with Microsoft experts. A quick update on the hosts Danny Guillory, a familiar face to the community and a Product Manager for Intune and Configuration Manager, hosted the series alongside Rachelle Blanchard. Together, they brought a strong mix of technical expertise, community engagement, and customer perspective to each episode. Rachelle helped surface real customer questions and guide conversations toward practical outcomes, ensuring each discussion reflected how endpoint management works in the real world. Thank you to everyone who participated Thank you to everyone who participated in Unpacking Endpoint Management and helped shape the conversations throughout the series. Catch up on demand You may have missed them, but you don't have to miss out on the learnings. Watch and learn when it's convenient for you. Policy: from hybrid to cloud-native Device security with Microsoft Intune Trends in endpoint management (live from Tech Takeoff 2026) Not sure where to start? Watch our most recent episode, App management at scale with Intune, now on demand! Watch on demand All episodes of Unpacking Endpoint Management are now available on demand via: aka.ms/JoinUEM. The series brought together experts from across Microsoft Intune, Security, and Customer Experience teams to share practical guidance, lessons learned, and real-world experiences from endpoint management. Continue the conversation While Unpacking Endpoint Management has concluded, there are many ways to stay connected with the Intune team and broader community. Join the Microsoft Intune Community here on Tech Community, and follow us on LinkedIn or @MSIntune and @IntuneSuppTeam on X to engage with experts, discover new content, and stay informed about the latest Intune guidance, best practices, and innovations. A Note from the Team Thank you for being part of the series. We're incredibly grateful to our customers, IT professionals, community members, guest speakers, and Microsoft experts who helped make Unpacking Endpoint Management such a valuable experience. Your questions, feedback, and real-world insights shaped every conversation and helped create meaningful discussions for the broader endpoint management community. Although the series has come to a close, our commitment to listening, learning, and engaging with our community remains unchanged. We look forward to continuing those conversations through the Microsoft Intune Community, Tech Community blogs, Microsoft Learn, events, and future opportunities to connect with Intune product, engineering, and customer success teams. Join the Community to get early insight into what's coming for Intune, connect with experts, and share real-world feedback that helps shape the product. 👉 aka.ms/JoinIntuneCommunity3.5KViews2likes1Comment
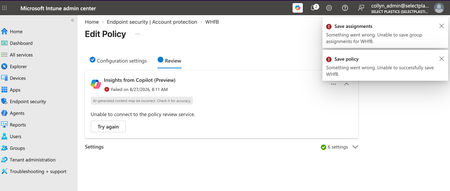
Account Protection Policy Unable to Save
I am trying to configure an Account Protection policy to allow but not enforce Windows Hello for Business in my org's tenant. If I configure any of the device- or user-settings, the policy throws an error when trying to save. Two errors actually, both pretty generic. This has been persisting for the last 24hrs. Does anyone know what may be the culprit here?815Views0likes5CommentsTriage vulnerabilities with the Vulnerability Remediation Agent, now in public preview
As automation and AI accelerate the pace of vulnerability discovery, the window between disclosure and exploitation continues to shrink. For IT and security teams, the challenge is no longer just finding vulnerabilities - it's prioritizing the ones that matter and acting on them before they can be exploited. To help organizations close that gap, we're pleased to announce that the Vulnerability Remediation Agent for Security Copilot in Microsoft Intune is now in public preview and rolling out to all customers. Following a successful limited preview, the agent is now broadly available. This release brings agentic vulnerability remediation out of an early-access cohort and into the hands of every eligible organization - an important step in our continued investment in helping admins reduce exposure faster and with greater confidence. View eligibility prerequisites here. How the agent helps you identify and triage vulnerabilities The Vulnerability Remediation Agent uses data from Microsoft Defender Vulnerability Management to identify Common Vulnerabilities and Exposures (CVEs) across your Intune-managed Windows devices and apps, then prioritizes them for remediation. Rather than leaving admins to sift through lengthy CVE lists with little context, the agent surfaces a prioritized set of recommendations directly in the Intune admin center - accessible from both the Agents and Endpoint security pages. When the agent runs, it evaluates vulnerability data and ranks threats based on factors such as CVSS scores, exposure impact, and affected device count, so the most critical issues rise to the top. Drilling into any suggestion provides: The count of associated CVEs A Copilot-assisted summarized impact analysis Suggested actions and affected systems Exposed devices and potential impact Step-by-step guidance for remediating the threat using Intune After acting on a recommendation, admins can mark it as applied, allowing the agent to retain a record for tracking remediation actions over time. The result is a meaningful reduction in the time it takes to investigate, prioritize, and remediate - strengthening overall security posture. Introducing agentic identity for the Vulnerability Remediation Agent With this release, the agent now operates under Microsoft Entra agentic identity - a meaningful advancement in how autonomous agents are governed and secured. What it is. Agentic identity is a specialized identity in Microsoft Entra ID that allows the agent to operate securely and independently. During setup, the agent provisions a dedicated agentic identity and a corresponding agentic user in your tenant's Microsoft Entra directory. The agent then runs under the permissions delegated to that agentic user rather than under a human user account. Why it matters. Agentic identity decouples the agent from any one person, ensuring its behavior is strictly bound to the permissions and scope you delegate to it. This delivers clearer accountability, a cleaner audit trail, and enterprise-grade governance for autonomous operations. How it helps. Admins remain firmly in control. After setup, delegate the required read permissions to the agentic user in the Microsoft Intune and Microsoft Defender admin centers, then use the built-in Readiness Check to confirm everything is configured correctly before the agent runs. Learn more in Agent identity. Getting started: Connect → Enable → Run → Remediate → Track One of the design goals behind the Vulnerability Remediation Agent is to make agentic security approachable, not complex. Rather than stitching together signals across multiple tools and admin centers, the agent guides admins through a clear, repeatable flow - from connecting your data to tracking measurable improvement over time. Connect — bring Defender and Intune data together. The agent draws on Microsoft Defender Vulnerability Management for CVE intelligence and Microsoft Intune for device and configuration context. With the required Microsoft Defender and Microsoft Intune plugins in place, your vulnerability and management signals work as one. Learn more on what is needed to connect the experience. Enable — turn on the agent. From the Agents node in the Microsoft Intune admin center, set up the agent in a few guided steps. During setup, the agent provisions its Microsoft Entra agentic identity and surfaces the permissions and plugins it needs, so you know exactly what to delegate before the first run. Run — let automated prioritization do the heavy lifting. Once permissions are delegated and the Run Readiness Check passes, you can configure the agent to run on demand or schedule it to run automatically in the background on a cadence you define; scheduling is a unique capability that helps teams stay ahead of emerging risks without requiring constant manual intervention. Each run analyzes your environment and produces a prioritized list of recommendations ranked by CVSS score, exposure impact, and affected device count so the most critical risks rise to the top automatically. Remediate — act with guided, Intune-ready actions. Each recommendation includes a Copilot-assisted impact summary, exposed devices, and step-by-step guidance for remediating the threat using Intune. Admins move directly from insight to action, without leaving the admin center. Track — measure improvement over time. Recommendations can be marked as applied, and the agent retains a record of your remediation actions. The outcome is a streamlined operating model: connect once, enable with confidence, and let the agent drive a continuous cycle of prioritization, remediation, and view progress. For full prerequisites, licensing, plugin, and role requirements, see Vulnerability Remediation Agent overview and set up. The Vulnerability Remediation Agent represents a meaningful step toward a more proactive, AI-assisted security posture, one where admins spend less time sifting through CVE lists and more time acting on what matters most. We invite you to try the public preview today, connect your Defender and Intune data, and experience how agentic remediation can help your team stay ahead of emerging threats. As always, we'd love to hear your feedback as we continue investing in making security in Intune faster, smarter, and more accessible. Share your tips and lessons learned in the comments below or reach out to us on X @IntuneSuppTeam. Join our community! Discuss real-world scenarios, get expert guidance, connect with peers, and influence the future of Microsoft Security products. Learn more at aka.ms/JoinIntuneCommunity.3.5KViews0likes1CommentHow to Configure macOS Privacy Preferences Policy Control (PPPC) Using the Intune Settings Catalog
By: Chris Kunze - Principal Product Manager | Microsoft Intune Privacy Preferences Policy Control (PPPC) settings on macOS are used to pre-approve privacy permissions for apps so users aren't repeatedly prompted by macOS for access requests. Common examples include Full Disk Access, Screen Recording, Camera, Microphone, Accessibility, Files and Folders, and Apple Events permissions. Organizations commonly deploy PPPC profiles to improve the user experience, reduce support calls, and ensure management and security tools have the permissions they require to function correctly. This is especially important for tools such as Microsoft Defender, remote support applications, compliance agents, and inventory tools. PPPC profiles also help standardize privacy settings across managed Macs and support zero-touch onboarding scenarios where users can begin working without manually approving a series of permission prompts. Intune’s settings catalog provides a straightforward way to deploy PPPC settings, but because macOS uses strict matching criteria, a few configuration details are important to get right. If these settings aren’t configured correctly, apps can either break - or worse, fail quietly. This article walks through the key configuration details that help ensure those settings are applied correctly. How macOS evaluates PPPC entries macOS evaluates PPPC entries using a combination of: App identifier (Bundle ID or Path) Code requirement (from the app’s signature) The specific permission being granted or denied. Apple requires each PPPC payload to use either Authorization or Allowed, but not both. If any of these values don’t align correctly, the policy won’t apply. Configure PPPC in Intune settings catalog Create a settings catalog profile. In the Intune admin center, create a macOS configuration profile using Settings Catalog. Search for: Privacy Preferences Policy Control. This is where you'll configure the PPPC permissions required by your application. Use the Authorization field When configuring, select the Authorization setting instead of the legacy Allowed setting whenever supported, but never both. Get the correct code requirement On a Mac where the application is installed, open Terminal and run: codesign -dr - /Applications/YourApp.app Replace /Applications/YourApp.app with the path to the application you're configuring. The output will contain a string similar to: designated => identifier "com.example.app" and ... Copy everything that appears after “designated =>” exactly as displayed. You'll use this value when configuring the PPPC entry in Intune. Note: Some applications return a multi-line code requirement. If that happens, paste the value into Intune as a single continuous string without line breaks. The content for the Identifier field can also be extracted from this command. Configure the PPPC entry After gathering the required information, configure the application entry. Field Value Identifier type Bundle ID or Path Identifier Application Bundle ID Code requirement Full output from the codesign command in Step 3. Authorization Allow Tip: Use Bundle ID for apps whenever possible. Bundle IDs are more reliable than file paths because they typically remain consistent when an app is updated or moved. Why PPPC settings may not apply If these settings fail, they fail silently. Intune may report the policy as successfully applied, but macOS evaluates PPPC entries when the app requests access to the protected resource. Upon app launch, macOS skips any entry where the code requirement doesn’t match the app’s current binary signature without any indication that the setting is skipped. The three most common causes are: Incorrect code requirement The code requirement must match the application's current signing information exactly. Even a small mismatch can prevent the PPPC setting from being applied. Mixing Authorization and Allowed Apple’s documentation states PPPC entries should use either Authorization or Allowed, not both. Wrong identifier type If the PPPC entry is configured with the wrong identifier type, macOS won't match the application correctly. Try it in your environment If you’ve been avoiding the settings catalog for PPPC, try this approach. Pull the identifier and code requirement directly from the app using codesign, use Authorization when available, and validate the configuration with a pilot group before broader deployment. Most PPPC issues come down to matching. Once you understand how macOS evaluates these settings it becomes much more predictable. If you have any questions, leave a comment below or reach out to us on X @IntuneSuppTeam. Join our community! Discuss real-world scenarios, get expert guidance, connect with peers, and influence the future of Microsoft Security products. Learn more at aka.ms/JoinIntuneCommunity.3.3KViews0likes2CommentsSupport tip: Upcoming Microsoft Intune network changes
3/18/2026 Update: The rollout of the Intune network changes described in this blog are in progress across each workload. Additionally, we are beginning to slowly rollout to each scale unit starting with North America 0702. You can find your scale unit location under Tenant administration > Tenant status > Tenant details. To avoid issues or failures with your device management, ensure your network infrastructure allows traffic for Azure Front Door IP addresses. See the details below to verify if your configuration requires an update and use the Azure Front Door Connectivity Diagnostics Tool to validate or troubleshoot. We know many customers don’t always check their service change messages in the Microsoft 365 admin center or the corresponding Message Center content in the Microsoft Intune admin center, so in this blog post we’re highlighting an important upcoming change to Intune network service endpoints. Starting on or shortly after December 2, 2025, Intune will also use Azure Front Door IP addresses to improve security and simplify firewall management. If your organization uses outbound traffic policies based on IP addresses or service tags, you’ll want to review and update your firewall rules to avoid service disruptions. We’ll keep you updated if the timeline shifts. In the meantime, here’s the service change communication that posted to all Intune customers: MC1147982 - Action Required: Update firewall configurations to include new Intune network endpoints As part of Microsoft’s ongoing Secure Future Initiative (SFI), starting on or shortly after December 2, 2025, the network service endpoints for Microsoft Intune will also use Azure Front Door IP addresses. This improvement supports better alignment with modern security practices and over time will make it easier for organizations using multiple Microsoft products to manage and maintain their firewall configurations. As a result, customers may be required to add these network (firewall) configurations in third-party applications to enable proper function of Intune device and app management. This change will affect customers using a firewall allowlist that allows outbound traffic based on IP addresses or Azure service tags. Do not remove any existing network endpoints required for Microsoft Intune. Additional network endpoints are documented as part of the Azure Front Door and service tags information referenced in the files linked below: Public clouds: Download Azure IP Ranges and Service Tags – Public Cloud from Official Microsoft Download Center Government clouds: Download Azure IP Ranges and Service Tags – US Government Cloud from Official Microsoft Download Center The additional ranges are those listed in the JSON files linked above and can be found by searching for “AzureFrontDoor.MicrosoftSecurity”. How this will affect your organization If you have configured an outbound traffic policy for Intune IP address ranges or Azure service tags for your firewalls, routers, proxy servers, client-based firewalls, VPN or network security groups, you will need to update them to include the new Azure Front Door ranges with the “AzureFrontDoor.MicrosoftSecurity” tag. Intune requires internet access for devices under Intune management, whether for mobile device management or mobile application management. If your outbound traffic policy doesn’t include the new Azure Front Door IP address ranges, users may face login issues, devices might lose connectivity with Intune, and access to apps like the Intune Company Portal or those protected by app protection policies could be disrupted. What you need to do to prepare Ensure that your firewall rules are updated and added to your firewall’s allowlist with the additional IP addresses documented under Azure Front Door by December 2, 2025. Alternatively, you may add the service tag “AzureFrontDoor.MicrosoftSecurity” to your firewall rules to allow outbound traffic on port 443 for the addresses in the tag. If you are not the IT admin who can make this change, notify your networking team. If you are responsible for configuring internet traffic, refer to the following documentation for more details: Azure Front Door Azure service tags Intune network endpoints US government network endpoints for Intune If you have a helpdesk, inform them about this upcoming change. If you need additional assistance, contact Microsoft Intune Support and refer to this Message Center post. Note: The above post went to all customers in our public cloud. Customers in Microsoft Intune for US Government GCC High and DoD received the following post (the only difference is the focus on US government network endpoints): MC1147978 - Action Required: Update firewall configurations to include additional Intune network endpoints Note: The previously available PowerShell scripts for retrieving Microsoft Intune endpoint IP addresses and FQDNs no longer returns accurate data from the Office 365 Endpoint service. Instead, use the consolidated list provided in the Intune endpoints documentation. Using the original scripts or endpoint lists from the Office 365 Endpoint service is insufficient and may lead to incorrect configurations. For network best practices, make sure to check out the blog: Support tip: Aligning network policy with Intune and Zero Trust. New: Azure Front Door Connectivity Diagnostics Tool for Intune To help you validate or troubleshoot the recent Intune network changes, we’ve published a lightweight Azure Front Door (AFD) Connectivity Diagnostics Tool. The script tests DNS resolution, outbound TCP connectivity on ports 80 and 443, and HTTPS reachability to the AFD IP ranges used by Intune, directly from an Intune-managed device. This is useful for environments that rely on IP-based firewall, proxy, or VPN rules. Important: This script only tests Azure Front Door endpoints. It does not validate connectivity to non-AFD Intune endpoints, including existing Intune IPs, service FQDNs, or related services such as Windows Notification Service (WNS) or Windows Autopilot. If you have any questions, leave a comment below or reach out to us on X @IntuneSuppTeam or @MSIntune. You can also connect with us on LinkedIn. Post updates: 11/13/25: Added a note to use the consolidated list of Intune endpoints. 12/18/25: We’ve published a new Azure Front Door (AFD) Connectivity Diagnostics Tool to help validate and troubleshoot Intune connectivity after updating firewall rules.812KViews11likes31Commentsdisable Multicast Name Resolution (LLMNR) with Intune
I'm looking for a way to disable Multicast Name Resolution (LLMNR) using Intune. I've checked the MDM Security baseline and all Device configuration policies, but was unable to find the setting. I rather do not want to use Powershell to deploy registry setting, but I do not know another option. Is there anyone who knows how to disable Multicast Name Resolution? Thanks in advanceSolved42KViews0likes10CommentsAs vulnerability discovery moves at AI speed, keeping current is foundational to reduce exposure
Recent advances in automation and AI are accelerating vulnerability discovery and shortening the window between disclosure and exploitation. As Microsoft outlined in our recent Security blog, this shift raises the bar for how quickly organizations need to reduce exposure across their environments. For IT and security teams, this makes staying current on updates more critical than before. While responding to individual Common Vulnerabilities Exposures (CVE) remains essential, keeping current across devices and applications is foundational to reducing exposure as threats evolve. This post focuses on the endpoint execution layer - how Microsoft Intune helps organizations understand their update posture, prioritize action, and reduce the time it takes for protections to land. Introducing the security update status dashboard in Microsoft Intune To act decisively, teams need clear visibility into where systems are current, where gaps exist, and how update deployments are progressing. Without a shared, defensible view of update status, it’s difficult to prioritize remediation or answer a basic question from leadership: “Are we patched?” To address this, Intune is introducing the General Availability of a new security update status dashboard providing centralized visibility into update compliance across Windows Clients, Windows Servers, and Microsoft 365 Apps. The dashboard provides a clear, current view for leadership, backed by current data — without switching between multiple reports or tools. The dashboard surfaces: Visibility into which devices are current on quality and feature updates, which are falling behind, and where remediation gaps exist across your Intune-managed estate The data needed to prioritize action, track progress across deployment rings, and help demonstrate a more accurate compliance posture Insight to where exposure is critical and needs immediate attention Four ways to shrink your vulnerability window The dashboard delivers visibility. The capabilities below help you act on it. 1) Windows Autopatch: deploy updates at scale with control Windows Autopatch manages update orchestration through predefined deployment rings, releasing updates progressively across representative device groups so that quality and security updates reach broad production populations only after passing validation in pilot environments. IT teams shift from manually coordinating deployment schedules each month to focusing on policy and exception management while Windows Autopatch handles sequencing, scheduling, and rollout logic. When critical vulnerabilities emerge, expedited update deployment allows devices to advance more quickly through the rollout process, providing security teams with an additional lever for reducing time-to-secure when AI-driven discovery shortens the window between disclosure and exploitation. 2) Hotpatch updates: Windows updates without the reboot Even when updates deploy rapidly, protection is not realized until a device restarts, and users routinely defer reboots for hours or days. Hotpatch updates for Windows reduces this gap by applying supported security updates to in-memory processes without requiring frequent restarts. Eligible Windows 11 Enterprise devices can reach a protected state immediately after installation, helping reduce the vulnerability window. Operationally, hotpatch updates shifts the restart requirement from monthly update to a smaller number of planned baseline updates per year, enabling organizations to deploy critical fixes without the productivity impact of forced restarts. You can enable hotpatch updates through quality update policies in Intune on supported systems. In addition, with Autopatch update readiness, IT admins can better anticipate when planned quality or feature updates won’t reach a device, understand Autopatch and hotpatch enrollment coverage, and quickly identify blockers to bringing devices into a ready state. 3) Microsoft 365 Apps patching: keep Office and other apps current in lockstep The Microsoft 365 Apps admin center includes Inventory and Cloud Update, giving administrators visibility into update status across connected devices by update channel so they can quickly spot systems missing the latest security updates and track progress. When an accelerated response is required, teams can tighten deadlines and move from staged rollout to immediate enforcement by removing waves, deferrals, or exclusion windows that may delay availability for specific groups, especially where channel divergence or scoped targeting leaves devices outside policy. Because expedited servicing reduces time for testing across diverse configurations, Cloud Update controls such as pausing a deployment or rolling back an update help mitigate risk while closing security gaps quickly. 4) Server updates: Configuration Manager or Azure Arc to accelerate compliance and operational workloads For organizations managing servers, Configuration Manager helps streamline the identification, packaging, and assignment of security updates (for example, with Automatic Deployment Rules) based on classification and severity. Cloud-based sourcing through the Microsoft Update service can prevent deployment failures in distributed environments, while maintenance windows let you pre-stage updates for highly available systems and install them during defined downtime intervals - achieving compliance without unplanned service interruptions. For server estates that are Arc-enabled, you can also use Azure Arc to extend visibility and management across hybrid and multicloud infrastructure. If you need even deeper coverage and insight, consider integrating Microsoft Defender Vulnerability Management (MDVM) to enrich update posture with vulnerability intelligence and prioritize remediation based on real exposure. Using update currency as an enforcement signal Deploying updates is half the job. Verifying they land - and holding the line when they don't - is the other half. Intune compliance policies let you define minimum OS build numbers, required update levels, and grace periods. Devices that fall out of compliance are flagged automatically. Paired with Microsoft Entra ID Conditional Access, update currency can become a condition of access - checking that only current, healthy devices connect to corporate resources. This turns update posture into an enforceable control, not just a reporting metric. Actions you can take today The increasing use of AI in vulnerability discovery, combined with a rapidly evolving threat landscape, underscores the importance of taking proactive security measures. Here are actions you can take today: Assess. Open the new security update status dashboard and know the baseline of your fleet. See how many Windows devices are behind on feature releases, quality updates, and Microsoft 365 Apps patches. Automate. Configure Windows Autopatch for ring-based deployment, enable hotpatch updates on eligible devices, and set Microsoft 365 Apps servicing profiles. Enable expedited updates so you can respond to critical vulnerabilities quickly. Enforce. Pair compliance policies with Conditional Access. Make being current a condition of access to corporate data. Monitor. Review the dashboard weekly. Investigate deployment failures promptly and deploy proactive remediations to clear blockers. Communicate. Share dashboard trends with security leadership and application owners. When stakeholders see the data, update compliance becomes a shared priority, not just an IT burden. Evolve. Revisit your deployment rings, deferral windows, and compliance thresholds quarterly. Use failure patterns from the dashboard to refine your approach and evaluate Windows Autopatch for a fully managed experience that scales with your organization. Every day a device remains out of date is potential exposure to unnecessary vulnerabilities. Intune gives you the tools, and now the visibility, to get current, stay current, and defend your organization at the speed the threat landscape demands. Closing Reducing exposure starts with knowing where you stand. The security update status dashboard in Intune provides a single place to understand update status across Windows devices and Microsoft 365 Apps, helping you identify lagging systems and prioritize action. Make the dashboard part of your regular operational rhythm: review it, act on the gaps it surfaces, and track progress over time. With the right visibility and tooling, staying current becomes repeatable - not reactive. Feature availability varies by license. Learn more about plan details and requirements here. Read the latest Microsoft Security blog to learn how turning AI‑driven discovery into protection at scale can help secure your estate in an AI‑driven threat landscape. Get started with Microsoft Secure Now for guidance in assessing risk and take recommended actions.7.4KViews2likes3CommentsBest practices for securing Microsoft Intune
Microsoft Intune gives IT and security teams a powerful way to manage endpoints at scale - deploying apps, enforcing security baselines, and configuring the settings that keep users productive and your organization protected. That’s why strong admin protections matter, so the right people can make the right changes, in the right scope, with the right safeguards. In this post, we’ll walk through three practical approaches to strengthen Intune protections: Start with least-privilege, designing roles around real admin jobs Embrace phishing-resistant authentication and privileged access hygiene, leveraging Microsoft Entra capabilities to reduce account and token compromise Enable Multi Admin Approval in Intune for sensitive changes Below we outline how to put each approach into practice. 1) Start with least-privilege: design roles around real admin jobs Least-privilege works best when it’s grounded in how your team operates. As a best practice, don’t grant more administrative access than a role truly needs. In Intune, role-based access control (RBAC) lets you tailor permissions and scopes so teams can run day-to-day operations with the minimum set of permissions required, nothing more. Microsoft Entra ID roles that have access to Intune, such as Global Administrator and Intune Administrator, are considered privileged roles with broad permissions in Intune. The use and assignment of privileged roles should be limited and not used for daily administrative tasks within Intune. Least-privilege is about limiting both the actions an admin can take and the users/devices those actions can be applied to. In Intune RBAC, scope tags enable you to constrain an admin’s visibility and actions to a defined set of users and devices - for example, only the devices assigned to a specific region, business unit, or platform team. When implementing RBAC policies, limit both the actions and users/devices an admin has permissions over. Call to action: Treat Intune administration as a set of job-specific roles, not a blanket entitlement. Inventory who has Intune Administrator, Global Administrator, or other high-impact roles, then remove broad assignments that don’t map to a named job function. Leverage Intune built-in role definitions for common personas (Help Desk Operator, Application Manager, Endpoint Security Manager, Read Only Operator) and standardize assignments. Create custom roles for ultimate least-privilege control. Implement scoped administration (scope groups and scope tags) for business units, regions, or platform teams, and validate that admins can only affect resources within their assigned scope. Adopt time-bound privilege elevation such as Microsoft Entra Privileged Identity Management (PIM) for admin roles and require reauthentication on elevation and sensitive operations. 2) Embrace phishing-resistant authentication and privileged access hygiene The security objective is straightforward: privileged access should be hard to obtain and hard to reuse. Microsoft Entra ID capabilities (Conditional Access, phishing-resistant multifactor authentication (MFA), risk signals, and privileged access controls) provide the policy engine that governs who can administer Intune, from where, and under what conditions. Call to action: Every privileged Intune action (Intune RBAC Role Management, device wipe, script deployment) should require strong, policy-verified sign-in, not just a password. Create Conditional Access policies dedicated to privileged roles and admin portals (Intune, Microsoft Entra, and related admin endpoints): require phishing-resistant authentication only, require a compliant device, challenge high-risk users or sign-ins, and restrict access by location or trusted network where feasible. Reduce or eliminate policy exclusions. Eliminate standing access by using Microsoft Entra Privileged Identity Management to assign time-bound roles based on conditions and approval steps, including restricting access to who can administer and assign permissions to apps. Move privileged accounts to phishing-resistant authentication methods and disable weaker methods for those accounts and through policy (see Plan a phishing-resistant passwordless authentication deployment). Establish privilege admin workstations with higher security baselines and use them for Intune high privilege admin accounts. Operationalize your token theft response plan by investigating risky sign-ins and unusual admin activity in Microsoft Defender XDR with signals from Microsoft Entra, Microsoft Defender for Cloud Apps, and Microsoft Defender for Endpoints. Adopt a defense‑in‑depth strategy to reduce the risk and impact of token theft (see Protecting tokens in Microsoft Entra). 3) Multi-admin approval in Intune for sensitive changes Multi Admin Approval introduces a practical governance control: selected Intune changes require a second authorized admin to review and approve before deployment. This is enforced for both Intune admin center actions and actions performed through Intune APIs. Multi Admin Approval reduces the risk that a single action can result in tenant-wide impact. Call to action: Require a second approval for high-impact Intune workflows (such as Intune RBAC role management, device wipe, and script deployment) to add an additional safeguard and help contain potential tenant wide impact. Decide which change types require approval - start with high-impact changes such as Intune RBAC role management and device wipe. Then, add access policies for changes that affect authentication, compliance, security baselines, or broad assignment scopes. Define approver roles and coverage (who can approve, SLAs, and what happens during incidents). Document an emergency/break-glass path with explicit post-change review, so speed doesn’t erase governance. How these measures add up to strong administrative protections When combined, these practices help you shift from relying on “trusted administrators” toward building a more protected administration by design: least-privilege to contain impact, Microsoft Entra-based controls to ensure users are trusted and are who they say they are, and multi-admin approval to govern the changes that matter most. These practices help organizations advance safer speed, clearer separation of duties, stronger audit readiness, and more resilient endpoint operations. If you’re looking for a place to start, here are a few quick steps: start with a quick wins pass - inventory broad, standing Intune role assignments and replace them with least-privilege RBAC roles; enforce Conditional Access and adopt phishing-resistant multifactor authentication for all admin scenarios; and place Intune RBAC role management, device wipe, script deployment behind multi-admin approval.82KViews13likes0Comments