root ca
3 Topics
Central pki
Has anyone implemented a centralised PKI where the Root CA is stored in Azure Key Vault and workloads can automatically obtain the Root CA when they are deployed, as well as receive updated versions when the Root CA needs to be rotated or renewed? I’m looking to implement a centralised PKI for an Azure hub-and-spoke architecture, where workloads across the spokes can automatically obtain and trust the Root CA. The workloads could include VMs, AKS, containers, App Services and Azure Functions. I’m aware that Azure Machine Configuration can be used to deploy certificates to VMs, but this is specific to VMs. What is the recommended approach for distributing the Root CA to the other Azure workload types using a consistent and automated mechanism? Ideally, I’d like the solution to be fully automated, so that new workloads receive the current Root CA during deployment and existing workloads automatically receive updated versions whenever the Root CA is rotated or renewed. I will be deploying the root ca in a key vault via terraform a project for the root ca only to update whenever is needed and then each resources to be able to get the latest root ca. Has anyone implemented something similar, or could you provide guidance on the recommended architecture and distribution mechanism?81Views0likes1Comment
Removal of old CA server stale data
Hi, I'm rebuilding some DC's and figured I'd tidy everything up before doing so as I've come into this with a messy environment. from this, I found an old Trusted Root CA, the certificate authority server was decommissioned in 2021 and all certificates have had an expiry date from 2021. its still being pushed out to domain devices such as servers and desktops. I tried running the 'certutil -dsdelca' command however this comes back with invalid command. I guess the best option is just to remove the class objects from the ADSI edit? as there is a class in AIA, CDP, Certification Authorities, KRA with the certificate nameSolved365Views0likes1Comment
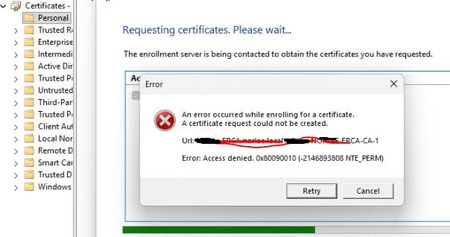
Access denied. 0x80090010 Enroll cert of Windows hello for Business with on-prem PKI CA Server
We have created Certficate Template from on-prem CA Server ( Windows server 2019 ) using this link : https://learn.microsoft.com/en-us/windows/security/identity-protection/hello-for-business/rdp-sign-in?tabs=intune However We can not Enroll Certificate Windows Hello for Business Certificate from User's Desktop ( Windows 11 ) and every time error occurred or Access Denied ( Certificate enrollment for Domain\UserName failed to enroll for a WHfBCertificateAuthentication certificate with request ID N/A from -ERCA.Domain.local\Domain-ERCA-CA-1 (Access denied. 0x80090010 (-2146893808 NTE_PERM)) We have also given Read and Enroll permission to EveryOne and Autheticated Users from CA Certficiate template , but still same erro Please advise if anything more can be done to resolve this issue.1KViews0likes5Comments