reporting experience
8 Topics
Microsoft Account got hacked
Hello my personal Microsoft account got hacked last week and i have been trying to do anything about it since then but it seems like the stupid AI phone support just understands nothing of what i'm talking to it and the official microsoft help pages for login and account problems also just do not help me at all. So my question is now, where and who can help me ? That account has bought games and apps in the store and so on. It cant be that all that is just gone now. I use 2FA and all that but it did not helped at all and i have no explaining for it. If anyone can help me in any way, it would be nice, thanks167Views0likes1Comment
Microsoft confirmed my account was hacked, but says it cannot be recovered
I am looking for guidance from the Microsoft Community or anyone who has experienced a similar account-takeover situation. Microsoft Support investigated my case and confirmed that there was unauthorized access to my Microsoft account. During the takeover, the third party changed the account's security information and enabled 2FA. Microsoft has now told me that because the security information was changed, Customer Support is unable to recover the account. The account has instead been permanently suspended. What I find difficult to understand is that the very security changes made during the confirmed unauthorized takeover now appear to prevent the legitimate account owner from recovering the account. I have already provided evidence supporting my ownership, including: Original Minecraft purchase information/invoice Billing information associated with the purchase My original account details Confirmation that the email address subsequently added to the account does not belong to me Microsoft Support's own investigation confirming unauthorized access I am not asking Microsoft to bypass account-security procedures. I am asking whether there is an escalation or verification process specifically for cases where Microsoft has already determined that an account was compromised. My questions to the community/Microsoft moderators are: Is there a senior Microsoft Account Security, Fraud, or Account Takeover team to which a confirmed-compromise case can be escalated? Can historical account information, previous security information, billing records, purchase history, device/account history, or original game entitlements be used to establish ownership? If the account itself genuinely cannot be restored, is there any process to restore or transfer a legitimately purchased Minecraft entitlement to a new Microsoft account after ownership has been independently verified? Is there any formal review or appeal mechanism available after Support has classified an account as unrecoverable? Has anyone successfully resolved a similar situation where an attacker changed the security information/2FA before the legitimate owner could regain control? I fully appreciate the need for strict account-security controls. However, I would like to exhaust the legitimate escalation and ownership-verification options before accepting that both the account and a legitimately purchased product are permanently lost because of security changes made by an unauthorized third party. Any guidance from Microsoft moderators or community members on the correct escalation channel would be greatly appreciated. Thank you.293Views0likes1Comment
CDOC Contact Information - Responses Failing to Reach CDOC Team
Good afternoon, I'm not sure if this is the correct forum to post this but I thought it might be the best place to start. I have been unsuccessfully trying to recover my child's compromised account for almost a month. Each of the 5 times I have followed the same steps, which eventually lead me to receiving an email with and SIR number, and telling me I need to provide more information to verify ownership of the account. When I reply to the email (from email address removed for privacy reasons and email address removed for privacy reasons ) it's like my response are black-holed somewhere. Eventually I get an email saying the following: This is NAME with Microsoft Customer Support again. I hope your day is going well. I wanted to touch base as I have not heard back from you. We want to be able to assist you with your request, but I still need the information that I requested to be able to consider moving forward with a resolution. I apologize in advance for the length of this email, but I wanted to be sure that I included everything. and then : Hello, This is NAME again with Microsoft Support. I initially e-mailed you on DATE with a request for the information required to confirm what your previous [recovery e-mail] was yours. your previous [recovery e-mail] is required before we can assist with your request. As no response was received, we have closed your case and any further replies will go to an unmonitored mailbox. If you still need assistance, please open a new case with us at Recover your Microsoft account | XBOX Support. You will receive an automated e-mail with confirmation that we have received your ticket. Please respond to that e-mail and reference this ticket number. Or Hello, Thank you for reaching out. This case was previously closed as it was either resolved or closed due to non-response after multiple contact attempts. In both situations, a closure email explaining the reason would have been sent to you. If you require further assistance, please open a new case by visiting hxxps://support.microsoft.com/. No matter what I tell the online chat agent, they tell me to be patient and submit the form. There seems to be no way to escalate the fact that my emails are not reaching the CDOC Team. Is there a workaround to reach them so they can receive the information that I'm providing and recover my child account? J252Views0likes0Comments
« Je suspecte un programme malveillant nommé SecurityHealthHost.exe
« Je suspecte un programme malveillant nommé SecurityHealthHost.exe situé dans AppData\Roaming\Microsoft\Windows\Caches. J'ai également reçu une demande d'installation d'un certificat racine Cisco que je n'ai pas demandé. » et plusieur programe qui sapelle miner sbr me font ramer possible de maider svp178Views0likes0CommentsAutomating Defender Alerts with CISA KEV and n8n – Has anyone tried similar workflows?
Hi everyone, I’ve been experimenting with n8n automation to improve vulnerability management. I created a workflow that cross-references Microsoft Defender for Endpoint vulnerabilities with the CISA Known Exploited Vulnerabilities (KEV) catalog, and then automatically creates Jira tickets for remediation. The flow takes about 16 seconds to run and prioritizes only the CVEs that are both present in the environment and listed in KEV. Has anyone here built similar automation (maybe with Logic Apps, Power Automate, or Sentinel playbooks)? Would love to hear how others handle vulnerability prioritization or ticket creation!723Views0likes0Comments
EDR logs explanation
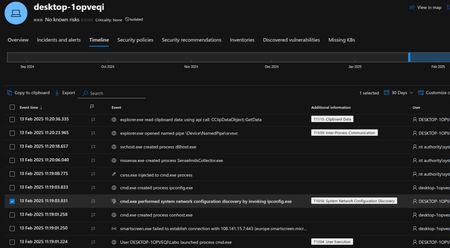
Hello, would it be possible for an expert from this forum to analyze the EDR logs? Could you also explain to me in detail what happened? Furthermore, can you tell me if it is clearly established that the deleted files were deleted by someone physically present on the machine, or if there are other possible explanations? Thanks in advance.309Views0likes0Comments
My laptop has been blocked by BitLocker.
However, there is no BitLocker recovery keys on my Microsoft account. I have tried to call Microsoft support, but I only get bot messages that take me to sites that asks me to go and check my Microsoft account. Is there any way I can chat with a human that can actually help me how to get around this BitLocker? thanks691Views0likes1Comment
Security Experts... Please advise the necessary people
I'm exploring this forum as a last resort, having exhausted all other options. My story involves a serious flaw in Microsoft's security framework, which has devastatingly impacted my once-thriving business. As a small yet vital enterprise of 15 employees, functioning as an MSP and Microsoft Silver Partner, I faced an unforeseen betrayal. During my absence for spinal surgery, a rogue Microsoft CSP Direct Partner, who was only supposed to manage my business temporarily, exploited their Microsoft affiliation. Utilizing social engineering and their insider status, they illegitimately transferred my company's goodwill and assets to themselves. This included the theft of two decades' worth of private data. The gravity of their deception extends beyond my business; they now control my client base, mainly consisting of solicitors and accountants. Despite clear evidence of their phishing and scamming activities, Microsoft has remained passive, allowing the situation to deteriorate. The suppliers, duped by fraudulent documents, are now realizing their mistake but continue to deny my rights to my own business. This inaction, shared by both Microsoft and the suppliers, leaves me entangled in debt and potential litigation. Interestingly, I am still aware of the physical whereabouts of these scammers. Moreover, I possess pages and pages of IOCs that further substantiate their illicit activities. If Microsoft genuinely engaged with this issue and worked collaboratively towards a resolution, perhaps we could transform this into a tale of rectification and justice. But, having pursued every possible channel without success, I am compelled to raise awareness on public forums. With nothing left to lose, I am calling for attention to this matter. Should you be able to assist, or know someone who can, please reach out. My contact details are linked to my forum ID, and Microsoft can easily access my tenant and phone information. Regards, bozzaman1.4KViews0likes2Comments