keyvault
3 Topics
Central pki
Has anyone implemented a centralised PKI where the Root CA is stored in Azure Key Vault and workloads can automatically obtain the Root CA when they are deployed, as well as receive updated versions when the Root CA needs to be rotated or renewed? I’m looking to implement a centralised PKI for an Azure hub-and-spoke architecture, where workloads across the spokes can automatically obtain and trust the Root CA. The workloads could include VMs, AKS, containers, App Services and Azure Functions. I’m aware that Azure Machine Configuration can be used to deploy certificates to VMs, but this is specific to VMs. What is the recommended approach for distributing the Root CA to the other Azure workload types using a consistent and automated mechanism? Ideally, I’d like the solution to be fully automated, so that new workloads receive the current Root CA during deployment and existing workloads automatically receive updated versions whenever the Root CA is rotated or renewed. I will be deploying the root ca in a key vault via terraform a project for the root ca only to update whenever is needed and then each resources to be able to get the latest root ca. Has anyone implemented something similar, or could you provide guidance on the recommended architecture and distribution mechanism?37Views0likes1Comment
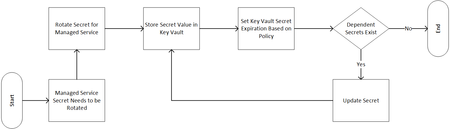
Managing and Rotating Secrets with Azure Key Vault, Managed Services, and some automation – Part 1
Secret rotation is not a new problem. In cloud-based environments many services implement secret-based authentication schemes. For many organizations, these secrets must be rotated on a regular schedule. In addition to the actual problem of rotating the access keys, there exists a problem of how these newly rotated credentials are propagated to all the applications and systems that utilize them. In this multi-part blog series, I will discuss a solution that, through automation, addresses both the scheduled rotation and dependency notification/update requirements.23KViews1like1Comment
WebApps calling KeyVault for secrets
Hi, I have a web app that needs to look up key/values in the key vault. I have assigned identity to the web app and set permissions on KeyVault, but do I still need to enable access on the key vault firewall for the outbound IP of the WebApp? Hard to manged if the WebApp is stopped as the IP will change? Is there a better way?1.1KViews0likes1Comment