external attack surface management
20 TopicsDefender EASM - Performing a Successful Proof of Concept (PoC)
To effectively determine the benefits of adopting Defender EASM, you should perform a Proof of Concept (PoC). Before enabling Defender EASM, you and your team should go through a planning process to determine success criteria, as well as execute a series of tasks that must be accomplished in the PoC.Optimize insights and efficiency with latest Defender EASM features and generative AI integrations
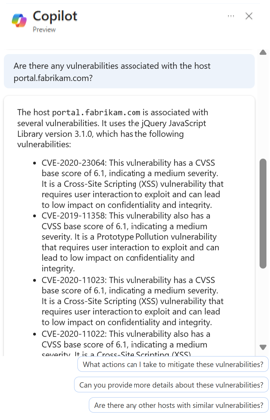
Read the blog to learn about Microsoft Defender External Attack Surface Management (EASM)'s latest updates that increase efficiency and speed to operationalize. Plus, learn about our newest generative AI integrations.One Microsoft: Enriching MDEASM assets with Threat Intelligence Feeds
There is so much data in todays cyber security world that it can become difficult to understand which feeds to prioritize. The Microsoft Defender External Attack Surface can help by showing you what vulnerabilities or exposures are being broadcast to the outside world but getting further context to what is being targeted can only help make informed decisions. This blog will explain the integration with Microsoft Defender Threat Intelligence to give additional insights.Latest Enhancements Boost Usability, Enhance Your Tools and Workflows
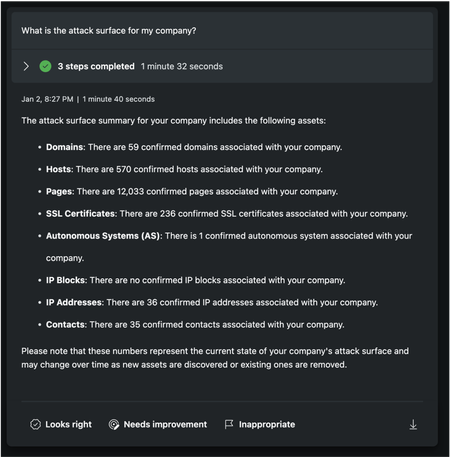
Microsoft Defender External Attack Surface Management (Defender EASM) discovers and classifies assets and workloads across your organization's digital presence to enable teams to understand and prioritize exposed weaknesses in cloud, SaaS, and IaaS resources to strengthen security posture. Features recently added boost usability and enable exciting new ways for customers to leverage their inventory data and critical security insights derived from their organization's assets and workloads. Below, learn about these powerful new enhancements and how you can begin using them today.