detection
177 TopicsMicrosoft Ignite 2026: New Sentinel Connectors Announcement
Microsoft Sentinel helps organizations detect, investigate, and respond to threats across increasingly complex environments. As AI transforms security operations, bringing together the right data and context is more important than ever, giving human defenders and AI agents a more complete view of the environment to reason over and act on. These integrations bring signals from Microsoft and third-party technologies together across the security environment, unlocking richer context for investigations and helping power the new Integrated Security Operations Center (ISOC) in Microsoft Defender, where human defenders and AI agents can reason across the environment with shared context. The connector ecosystem isn’t the only area seeing rapid growth. Microsoft Sentinel continues to add new capabilities, including Nested API support, Azure Blob support, and multi-account support, while AI-powered tools like the connector builder agent are making it easier than ever for developers to build integrations and bring more of their security data into Sentinel. At the same time, Unified Data Management, now in public preview, makes it easier for customers to manage their Microsoft Sentinel data, connectors, tables, and ingestion health in one place. For Microsoft Ignite 2026, we’re excited to showcase recent additions to this growing ecosystem and the partners making them possible. These new and enhanced connectors continue to broaden the security data available to customers, helping human defenders and AI agents gain the context they need across the technology estate. Airlock Digital for Microsoft Sentinel Airlock Digital helps prevent malware, ransomware, and unauthorized software with deny by default application control, allowing only trusted applications, scripts, and processes to run. Its Microsoft Sentinel push integration ingests execution history, browser extension control events, server administrative activity, and policy changes for monitoring and investigation. Included parsers map execution and audit events to Microsoft’s ASIM for analysis alongside other security signals. A customizable workbook supports investigation and monitoring, and teams can create analytics rules using the ingested data. NC Protect Data Connector for Microsoft Sentinel NC Protect Data Connector for Microsoft Sentinel from archTIS brings user activity and protection logs from NC Protect into Sentinel for centralized security analysis. The connector captures user activities and access-related events, while built-in workbooks support investigation and visualization of user behavior. By correlating NC Protect audit data with other security telemetry, the integration helps teams identify suspicious user activity, trigger alerts and response workflows, strengthen auditing, and monitor guest activity across SharePoint and Teams. blacklens.io for Microsoft Sentinel blacklens.io for Microsoft Sentinel brings external and internal attack-surface data, risk-prioritized vulnerabilities, darknet intelligence, and supply-chain risks into Microsoft Sentinel. The connector ingests exposed assets, compromised identities, stolen credentials and session cookies, typosquatting domains, and supplier activity on ransomware leak sites. The solution includes a data connector and analytics rule for creating Sentinel incidents, with configurable notification rules for alert severity and type. Findings are available in Log Analytics for correlation with existing Sentinel signals and can support custom analytics rules, workbooks, automation, and threat investigations. BloodHound Enterprise BloodHound Enterprise (BHE) helps organizations protect critical assets across modern hybrid environments by continuously uncovering identity attack paths and providing actionable remediation guidance. By integrating with Microsoft Sentinel, BHE delivers attack path data and identity security posture insights directly into Sentinel workflows. This helps security teams prioritize remediation efforts based on exposure to critical assets while enriching investigations into identity-based threats, including lateral movement and privilege escalation. Together, BHE and Microsoft Sentinel help security teams connect threat detection to underlying identity risk, speed investigations, and reduce opportunities for attackers. BlueVoyant Anthropic Claude Compliance BlueVoyant Anthropic Claude Compliance brings compliance activity from the Anthropic Claude Compliance API into Microsoft Sentinel using the Codeless Connector Framework (CCF). The connector ingests Claude compliance events into Sentinel, giving security, risk, and audit teams centralized visibility into AI usage and related activity. By correlating these compliance signals with identity, endpoint, and other security telemetry, the integration supports threat hunting, investigation of policy violations and anomalous behavior, compliance monitoring, and repeatable audit workflows. Cato Networks for Microsoft Sentinel Cato Networks for Microsoft Sentinel brings security and network events from the Cato SASE Platform into Microsoft Sentinel using the Codeless Connector Framework (CCF) Push pattern. The connector pushes events into a dedicated Log Analytics table, making Cato activity available alongside other Sentinel data. By centralizing this telemetry in Sentinel, the integration enables security teams to incorporate Cato events into threat hunting, detection, and visualization workflows alongside broader security signals. Check Point EM ThreatCloud Intelligence Feed Connector for Microsoft Sentinel The Check Point EM ThreatCloud Intelligence Feed Connector brings threat intelligence from Check Point Exposure Management into Microsoft Sentinel. The connector ingests indicators of compromise (IoCs), including malicious IP addresses, domains, URLs, and file hashes, enriched with threat context such as confidence, severity, kill-chain stage, and campaign associations. An included playbook further enriches incident IoCs through ThreatCloud, helping security teams correlate intelligence with existing telemetry, accelerate triage and investigation, and reduce the manual effort required to maintain threat intelligence. Check Point Exposure Management Threat Intelligence IoC for Microsoft Sentinel Check Point Exposure Management Threat Intelligence IoC for Microsoft Sentinel brings threat intelligence from Check Point Infinity External Risk Management into Sentinel. The connector ingests malicious IP addresses, domains, URLs, and file hashes, enriched with context such as severity, confidence, and detected activity. By correlating these indicators of compromise (IoCs) with existing logs through analytics rules, hunting queries, and watchlists, the integration helps security teams reduce manual intelligence management, identify matches with external threats, and accelerate threat detection and investigation. Citrix SPA Sentinel App Citrix SPA Sentinel App brings Citrix Secure Private Access and Device Posture service events into Microsoft Sentinel using the Codeless Connector Framework (CCF). The connector imports critical logs, policy outcomes, and user activity data, giving security teams greater visibility into application access and device posture activity. An included workbook supports visualization and analysis of Citrix data, helping SOC teams correlate activity with broader security telemetry, investigate security risks, support compliance monitoring, and strengthen threat hunting across their environment. ContraForce Events for Microsoft Sentinel ContraForce Events for Microsoft Sentinel brings security delivery and administrative activity from ContraForce workspaces into Microsoft Sentinel using the Codeless Connector Framework (CCF). ContraForce is an Agentic Security Delivery Platform for service providers and security teams running triage, investigation, and response across Microsoft Defender XDR and Sentinel. The connector ingests incidents, privileged access changes, service account credential activity, and high-impact workspace actions. Three included analytics rules detect privileged access, credential, and high-impact workspace activity, helping teams monitor and investigate the platform supporting their security operations. Corelight for Microsoft Sentinel By transforming all network traffic into rich, comprehensive evidence, Corelight gives security teams using Microsoft Sentinel the visibility to understand exactly what is happening across their enterprise networks. In addition to native integration with Microsoft Sentinel, Corelight integrates with Microsoft Defender for Endpoint, Defender Vulnerability Management, and Entra ID to streamline investigations, accelerate responses, and remediate incidents quickly and easily. The Corelight App for Microsoft Sentinel includes intuitive dashboards, pre-defined workbooks , sample queries, and analytics rules that help make SOC teams more efficient and effective. CTM360 CTM360 brings external threat visibility into Microsoft Sentinel. The integration connects the CTM360 HackerView and CyberBlindspot platforms to Sentinel through REST APIs, so external attack surface and digital risk events flow straight into security operations workflows. HackerView surfaces externally exposed assets and security issues across your attack surface. CyberBlindspot adds organization-specific threat intelligence from surface, deep, and dark web monitoring. With these signals centralized in Sentinel, security teams can analyze external exposures alongside their broader telemetry and speed up detection, investigation, and response. Cyren CrowdStrike IOC Automation Cyren CrowdStrike IOC Automation connects Cyren IP reputation threat intelligence with Microsoft Sentinel and CrowdStrike Falcon to operationalize malicious IP indicators. An included Logic App playbook automatically retrieves known malicious IP addresses from Cyren and submits them to CrowdStrike Falcon as custom indicators of compromise (IOCs) for blocking and detection. Scheduled execution keeps the intelligence updated and automates the flow of Cyren IP reputation data into CrowdStrike Falcon for blocking and detection. Vaikora AI Agent Signals for Microsoft Sentinel Vaikora AI Agent Signals for Microsoft Sentinel brings behavioral security signals from AI agents into Sentinel for centralized monitoring and response. The connector ingests risk scores, anomaly and threat classifications, policy enforcement decisions, and audit data, including signals for prompt injection attempts and suspicious tool usage. Included analytics rules and a workbook help security teams detect behavioral anomalies, investigate policy violations, and incorporate AI agent risks into existing Sentinel incident workflows. Vaikora AI Agent Signals for SentinelOne Vaikora AI Agent Signals for SentinelOne brings high-risk behavioral security signals from Vaikora into SentinelOne as threat intelligence indicators of compromise (IOCs). The integration filters high-severity and anomalous AI agent activity and maps Vaikora risk scores to SentinelOne severity levels. The resulting IOCs are submitted to SentinelOne and expire after 90 days, enabling Vaikora security signals to be incorporated into SentinelOne endpoint protection workflows. DataBahn Agentic Data Control Plane for Microsoft Sentinel DataBahn’s agentic data control plane integrates with Microsoft Sentinel to provide our shared customers an AI-native data pipeline and orchestration platform that allows them to accelerate enterprise deployments. DataBahn’s pipeline standardizes onboarding and shaping across all data sources while providing operational visibility into data flow and health. Together, the collaboration focuses on reducing onboarding friction, improving normalization consistency, and enabling intentional routing, which helps security teams improve visibility, support threat detection, and streamline investigation and incident response workflows. Delinea Platform for Microsoft Sentinel Delinea Platform Sentinel Solution brings privileged access activity into Sentinel natively through the Content Hub, as a complete SOC package. The connector pulls audit events covering secrets access, authentication, session activity and configuration changes directly into Sentinel. Ready-made workbooks, analytics rules with baseline-driven detection, hunting queries and an automated response playbook let security teams detect bulk secret access, failed sign-in bursts and privilege escalation sooner, investigate without leaving Sentinel and answer auditors with a record of what happened and why it was allowed. Dynatrace Software Intelligence Platform with Microsoft Sentinel Dynatrace integrates bidirectionally with Microsoft Sentinel, bringing application attacks, runtime vulnerabilities, Dynatrace Intelligence problems, and audit logs into Sentinel, where analytics rules, workbooks, and playbooks support detection, triage, and response. Sentinel can also send alerts to Dynatrace and enrich detected attacks with Sentinel and Microsoft Defender XDR insights. Bindplane by Dynatrace complements the integration by collecting and routing logs into Sentinel, including normalization to ASIM tables, giving SOC teams runtime and topology context for investigations. ExtraHop RevealX for Microsoft Sentinel ExtraHop RevealX for Microsoft Sentinel brings network detection and response (NDR) into Sentinel, giving your SOC visibility into threats that endpoint and log tools miss, including lateral movement and credential abuse hiding in encrypted east-west traffic. RevealX decrypts and analyzes network traffic at line rate, out of band with no impact on the network. The connector sends ExtraHop detections into Sentinel for dashboards, custom alerts, and investigation, so network context enriches your existing SOC workflows instead of sitting in a separate console. Fire Compass FireCompass Risks for Microsoft Sentinel brings validated external risk findings from the FireCompass platform into Microsoft Sentinel through the Codeless Connector Framework. The connector ingests risk data including severity, affected assets, assessment context, impact, and remediation guidance. By making validated exposures available in Sentinel, security teams can correlate external risks with endpoint and network telemetry, track remediation progress, and build analytics rules, workbooks, and hunting queries on top of FireCompass findings. Gambit Security Sentinel Solution Gambit brings resilience context into Microsoft Sentinel. It finds the resilience issues in your environment and syncs them to your Sentinel workspace daily, to help analysts see recovery risk before anything goes wrong. Sentinel correlates those issues with its detections. Your team can then prioritize the attacks most likely to disrupt critical operations: the ones hitting resources that aren’t ready to recover. Sentinel tells you what’s happening. Gambit tells you whether you can recover from it. Holm Security for Microsoft Sentinel Holm Security for Microsoft Sentinel brings asset data from the Holm Security platform into Sentinel via the Holm Security REST API. The connector ingests web and network assets into Microsoft Sentinel, including metadata such as IP addresses, hostnames, operating systems, tags, and vulnerability counts per asset. By incorporating this asset inventory alongside other security telemetry, the integration enables security teams to build dashboards, create custom alerts, and correlate asset information with other data in Microsoft Sentinel. Idira Endpoint Privilege Manager for Microsoft Sentinel The Idira® Endpoint Privilege Manager by Palo Alto Networks integration for Microsoft Sentinel pulls application events and policy audit activity into Microsoft Sentinel using the Codeless Connector Framework and the Idira Endpoint Privilege Manager REST API. Events land in a dedicated Log Analytics table, so security teams can analyze privilege activity alongside their other telemetry and build detections. IPinfo: IP geolocation & intelligence database IPinfo: IP geolocation & intelligence database brings contextual IP intelligence into Microsoft Sentinel to enrich security logs and investigations. The solution provides data such as IP geolocation, network ownership and routing, proxy and residential proxy detection, ASN information, and other IP classifications. By adding this context to IP addresses observed in Sentinel, the integration helps security teams better understand indicators of compromise, prioritize security events, strengthen threat detection and investigation, and inform network and access management decisions. Island Solution for Microsoft Sentinel Island Solution for Microsoft Sentinel brings user activity and administrative audit events from the Island Enterprise Browser into Microsoft Sentinel for centralized security monitoring. The solution automatically shares events from the Island Management Console with Sentinel and includes data connectors and workbooks for user activity and admin audit logs. By adding browser activity context to existing security telemetry, the integration helps security teams monitor and analyze user and administrative activity and investigate potential security issues. NetApp Ransomware Resilience for Microsoft Sentinel NetApp Ransomware Resilience detects and contains ransomware attacks on NetApp ONTAP workloads in real time, then enables fast, clean recovery. Its Microsoft Sentinel integration enriches alerts with data-layer context, including attack type, severity, user and IP, and affected cluster, volume, and SVM. The NetApp SOAR playbook can take actions on ONTAP such as trigger immutable snapshots, block suspicious users or IPs, and take compromised volumes offline. Together, these integrations extend the NetApp Platform’s ability to help security teams triage and respond to ransomware attacks, limit data loss, protect recovery points, and coordinate response across storage and security teams. NordStellar for Microsoft Sentinel NordLayer Intelligence by NordStellar for Microsoft Sentinel brings external threat and exposure findings into Sentinel through the Azure Monitor Logs Ingestion API. The integration provides findings including leaked credentials, breach exposures, malware and info-stealer infections, dark web activity, domain impersonation risks, and external attack surface vulnerabilities. By correlating these findings with other security telemetry in Sentinel, the solution helps teams investigate external threats, identify exposures affecting their organization, and automate triage and response through analytics rules and SOAR playbooks. Panorays for Microsoft Sentinel Panorays for Microsoft Sentinel brings third-party security findings from the Panorays platform into Sentinel through the Panorays API. The connector provides security teams with visibility into the security posture of vendors and supply-chain organizations, making third-party risk and vulnerability findings available alongside other security telemetry. By incorporating Panorays findings into Sentinel workflows, the integration helps SOC teams centrally monitor and investigate third-party risks and correlate them with internal security signals. USTA Account Takeover Prevention Sentinel Connector USTA Account Takeover Prevention Sentinel Connector brings compromised credential intelligence from the PRODAFT USTA Threat Intelligence platform into Microsoft Sentinel. The connector ingests alerts for exposed corporate credentials, enabling security teams to investigate potential account takeover risks within existing Sentinel workflows. Included analytics can identify newly compromised credentials and successful Microsoft Entra ID sign-ins involving known-compromised accounts, helping SOC teams operationalize external credential intelligence and prioritize investigation and response. USTA IoC Threat Stream for Sentinel USTA IoC Threat Stream for Sentinel brings curated indicators of compromise (IoCs) from the PRODAFT USTA Threat Stream into Microsoft Sentinel Threat Intelligence. The integration provides indicators including malicious URLs, phishing sites, and malware hashes derived from PRODAFT investigations. By making these indicators available for correlation with existing telemetry, hunting queries, and detection rules, the solution helps security teams identify connections to malicious infrastructure, investigate phishing and malware activity, and incorporate external threat intelligence into existing triage and response workflows. USTA Payment Card Fraud Intelligence Sentinel Connector USTA Payment Card Fraud Intelligence Sentinel Connector brings compromised payment card intelligence from the PRODAFT USTA Threat Intelligence platform into Microsoft Sentinel. The connector retrieves alerts associated with an organization’s payment card BIN ranges and makes them available within Sentinel for investigation. Included analytics identify newly exposed and non-expired compromised cards, helping security teams centralize payment fraud intelligence, prioritize potentially actionable exposures, and incorporate them into existing investigation and response workflows. Pulumi Cloud Audit Logs for Microsoft Sentinel Pulumi Cloud Audit Logs for Microsoft Sentinel brings audit logs from Pulumi, the infrastructure platform for humans and agents, into Microsoft Sentinel through the Codeless Connector Framework (CCF). The connector ingests authentication events, organization membership changes, stack lifecycle operations, policy changes, and access token usage. It also includes three analytics rules that detect failed login attempts, stack deletions, and organization membership changes. Your security team can see what a human or agent did, when, and where across infrastructure as code, secrets, configuration, and policies, which helps speed up security and governance investigations. QCrypton PQC Scanner for Microsoft Sentinel QCrypton PQC Scanner for Microsoft Sentinel brings post-quantum cryptography readiness findings from Azure environments into Sentinel using the Codeless Connector Framework (CCF). The connector provides visibility into cryptographic assets including Key Vault keys, TLS certificates and configurations, and Entra ID app registration certificates, with quantum posture ratings and risk scores. Included are six analytics rules, a workbook, and a notification playbook to help security teams identify vulnerable cryptographic assets and prioritize post-quantum migration planning. SailPoint for Microsoft Sentinel SailPoint for Microsoft Sentinel brings identity security telemetry from SailPoint Identity Security Cloud into Sentinel using the Codeless Connector Framework (CCF). The solution streams audit and search events into Sentinel tables, where analysts can correlate identity activity with other security signals and query SailPoint APIs for additional identity and account context during incident triage. Automated playbooks can also remediate threats by revoking access or disabling compromised accounts, helping teams connect identity insight with investigation and response. SAP LogServ (RISE), S/4HANA Cloud private edition SAP LogServ (RISE), S/4HANA Cloud private edition extends Microsoft Sentinel security monitoring for SAP RISE environments with infrastructure, database, operating system, and network security logs managed by SAP Enterprise Cloud Services. Deployed alongside the Microsoft Sentinel Solution for SAP applications, it complements application-layer monitoring to provide visibility across the SAP stack and enable cross-layer threat detection and correlation. The solution supports near real-time log collection, built-in analytics and workbooks, ASIM-based security content, and correlation with signals from endpoints, Microsoft Entra ID, and other sources in Microsoft Sentinel. MailRisk data connector for Microsoft Sentinel MailRisk data connector for Microsoft Sentinel brings suspicious email data analyzed by users through Secure Practice MailRisk into Sentinel. The connector ingests enriched email metadata and risk assessment updates from the Secure Practice API, providing potential indicators of compromise identified from reported emails. By incorporating MailRisk data alongside other security telemetry, the integration helps security teams correlate suspicious email activity, search and investigate potential threats, and incorporate user-reported email intelligence into alerting and incident response workflows. SecurityScorecard Ratings for Microsoft Sentinel SecurityScorecard Ratings for Microsoft Sentinel provides cybersecurity posture ratings based on continuously monitored risk factors and threat intelligence. SecurityScorecard evaluates organizations using an A-F rating, helping security teams identify and track cybersecurity risks. The solution supports use cases including enterprise cyber risk management, third-party risk monitoring, executive reporting, and cyber due diligence. SIGNL4 - Mobile Alerting & Response for Microsoft Sentinel and Defender for Cloud SIGNL4 bridges the gap between security detection and human response with mobile-first alerting and incident management for Microsoft Sentinel and Defender for Cloud. Its two-way integrations allow security teams to acknowledge, escalate, and resolve incidents directly from their mobile devices, with updates automatically synchronized back to Sentinel. Critical Defender for Cloud findings trigger actionable response workflows, while persistent mobile notifications, automated escalations, and on-call scheduling ensure the right people are reached when it matters most. The result is faster incident response, clear accountability, and a fully auditable process - wherever responders are. SOC Prime Audit CCP SOC Prime Audit CCP brings SOC Prime Platform audit logs into Microsoft Sentinel for centralized security monitoring and analysis. The connector ingests platform activity including user actions, API calls, and administrative events, providing an audit trail across detection engineering processes. By correlating SOC Prime activity with other security signals in Sentinel, the integration helps security teams investigate platform activity, support compliance monitoring, and incorporate audit telemetry into broader threat detection and response workflows. SOCRadar Alerts Azure Sentinel Directional Solution SOCRadar Threat Intelligence for Microsoft Sentinel enriches security operations by bringing prioritized, context-rich alerts directly into Microsoft Sentinel. Covering SOCRadar’s Extended Threat Intelligence capabilities, including Brand Protection, External Attack Surface Management (ASM), Third-Party Findings, and other security modules, the integration helps organizations monitor external threats and manage investigations within their existing SOC workflows. Bidirectional synchronization also helps keep incident status, severity, and comments aligned between Microsoft Sentinel and SOCRadar. SpyCloud Enterprise Protection for Microsoft Sentinel SpyCloud Enterprise Protection for Microsoft Sentinel brings stolen identity data from infostealer malware, phishing attacks, and third-party breaches into Microsoft Sentinel, helping security teams uncover compromised identities, prioritize high-risk exposures, and accelerate remediation to prevent session hijacking and other targeted identity-based attacks. The solution includes a custom API connector, a Logic Apps playbook for ingesting data into Log Analytics, analytic rules that generate Sentinel incidents from breach and malware data, and additional Logic Apps playbooks for incident automation and enrichment. Tenable App for Microsoft Sentinel Tenable App for Microsoft Sentinel brings asset and vulnerability data from Tenable One Vulnerability Management into Sentinel for centralized security analysis. The integration combines Tenable cyber exposure insights with Sentinel’s collection, detection, and investigation capabilities, making vulnerability context available alongside other security telemetry. By incorporating asset and vulnerability findings into Sentinel workflows, the solution helps security teams correlate exposure data with security signals, investigate risks affecting vulnerable assets, and better prioritize remediation efforts. Uniqkey Security Events for Microsoft Sentinel Uniqkey Security Events for Microsoft Sentinel brings authentication, credential access and management, sharing, administrative activity, and platform threat detections into Microsoft Sentinel using the Codeless Connector Framework (CCF). Included analytics rules identify scenarios such as sign-ins from unfamiliar IP addresses, excessive credential access, data exports, and security policy or privilege changes. A workbook visualizes activity and threat detections, helping security teams monitor password-management activity, investigate potential credential risks, and correlate findings with broader security telemetry. Utimaco Enterprise Secure Key Manager Utimaco Enterprise Secure Key Manager (ESKM) integrates with Microsoft Sentinel to provide centralized security monitoring and visibility into cryptographic key management activities through KMIP server logs. The solution enables organizations to monitor key operations, KMIP client activity, and authentication events, helping security teams identify suspicious behavior and investigate potential threats. Built-in analytics rules help detect brute-force authentication attempts, repeated permission-denied events, and key-destruction activity, while hunting queries and a dedicated workbook support deeper investigation of unusual users, source IPs, key retrieval patterns, and after-hours activity. valimail-sentinel-enforce Valimail enables organizations to see who sends email using your domain, protects against domain impersonation, and displays a verified logo in inboxes to increase brand trust. Our Microsoft Sentinel Connector brings Valimail Enforce event data directly into Sentinel, allowing security teams to incorporate our telemetry into unified SIEM workflows, monitor authentication and enforcement trends in real time, and build custom alerts and visualizations based on DMARC events. Once configured, Sentinel continuously ingests Valimail event logs, enriching your broader security intelligence and helping to improve your ability to detect and respond to threats across your environment. Varonis for Sentinel Solutions Varonis for Sentinel Solutions brings enriched, data-centric Varonis alerts into Microsoft Sentinel for triage, investigation, and remediation. Varonis insights are contextualized alongside other security events to provide a unified view of data risk. This allows security teams to view and close Varonis alerts directly within Sentinel, reducing the need to switch interfaces and supporting incident resolution with less manual effort Whisper for Sentinel Whisper for Sentinel enriches Microsoft Sentinel incidents and alerts with threat and infrastructure intelligence for IPs, domains, ASNs, and networks. The solution provides threat scores, supporting evidence, infrastructure relationships, and historical context directly within Sentinel. Included enrichment playbooks, analytics rules, hunting queries, and workbooks support investigation of threats including C2 communications, malicious infrastructure, suspicious domains, and BGP anomalies, while retained enrichment data can be queried and correlated with existing logs. Wiz for Microsoft Sentinel Wiz for Microsoft Sentinel brings Wiz Issues, Vulnerability Findings, and Audit logs into Microsoft Sentinel. Wiz identifies and prioritizes cloud security risks across areas including vulnerabilities, malware, internet exposure, identity, and data security in AWS, Azure, Google Cloud, OCI, Alibaba, and Kubernetes environments. In addition to the solutions from our third-party partners, we are also excited to announce the following connectors published by the Microsoft Sentinel team: Agari Solution Akamai DDOS Protection Alibaba Cloud Networking Atlassian Organization Audit AWS Elastic Kubernetes Service AWS Elastic Load Balancing Cisco Cloud Security Cisco Meraki Events via REST API Crowdstrike Falcon Endpoint Protection Elastic Agent Solution Imperva WAF Cloud Solution Microsoft Copilot Microsoft Dragon Copilot Mulesoft CloudHub Alerts OpenAI Qualys VM Knowledgebase Rapid7 InsightVM CloudAPI SentinelOne TheHive Solution Trellix Enpoint Security Trend Micro Cloud App Security VMware Workspace ONE Zoom Reports Building a more connected foundation for security operations The strength of the connector ecosystem reflects the work of Microsoft and our technology partners to support our shared customers. Together, we are helping organizations connect the technologies they rely on and bring more of their security data into a unified operational experience. For customers If you are a Microsoft Sentinel or ISOC customer, or considering adopting it, we want you to have the security connectors and integrations you need to get value from the platform. If an integration with an independent software vendor (ISV) is not yet available, or you have an issue with an existing solution, we have a dedicated team that may be able to assist by working with ISVs to build new or update existing connectors. If you have such a need, submit a request here. For software companies If you are a software development partner, the Microsoft Sentinel Codeless Connector Framework (CCF) provides a streamlined way to bring your product into the Microsoft Security ecosystem. Partners can also work directly with Microsoft for engineering guidance and support to build or improve a connector. Reach out to us via our intake form. Building a more connected foundation for security operations Our goal is simple: help customers protect their digital environments by giving human defenders and AI agents a more complete picture of risk. We’ll continue investing in connectors, partnerships, and integrated security experiences to help customers defend their organizations with greater visibility, context, and confidence. Learn More Microsoft Sentinel What is Microsoft Sentinel Empower Real-Time Security with Microsoft Sentinel’s CCF Push Feature | Microsoft Community Hub Growing our connector ecosystem with 500+ Microsoft Sentinel connectors What’s new in Microsoft Sentinel: October 2026 Protecting Microsoft's SAP workload with Microsoft Sentinel for SAP: the RISE with SAP chapter Microsoft Defender ISOC in Microsoft Defender Microsoft Sentinel connector hands-on labs Building Microsoft Sentinel Connectors in Minutes with the Sentinel Connector Builder Agent Building a CCF Nested API Pull Connector: A Technical Lab Walkthrough Microsoft Sentinel features in public preview Accelerate connectors development using AI agent in Microsoft Sentinel | Microsoft Community Hub Extending Sentinel Data Integration: Azure Blob Storage Support for CCF Connectors | Microsoft Community Hub Public Preview: Nested API Support Comes to Microsoft Sentinel CCF | Microsoft Community Hub Public Preview: Multi-Account Support for Microsoft Sentinel Codeless Connectors | Microsoft Community Hub Manage all your Microsoft Sentinel data in one place with Unified Data Management (Public Preview) | Microsoft Community Hub1.7KViews0likes1CommentProtecting Microsoft's SAP workload with Microsoft Sentinel for SAP: the RISE with SAP chapter
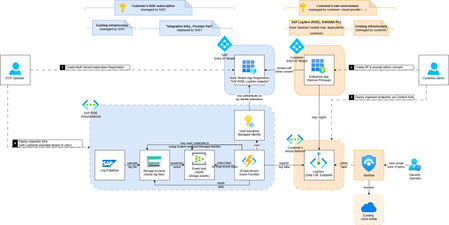
Inside Track | Microsoft Digital When infrastructure operations shift, security visibility must evolve with the operating model Four years ago, we told the story of how Microsoft became Customer Zero for using Microsoft Sentinel as the SIEM for its own SAP estate, pairing a then-new product “Sentinel Solution for SAP” with our existing SOAR platform and proving out cross-correlation between SAP and the rest of the enterprise. The ambition was stated plainly at the time: an internally managed and configured SIEM that could baseline user behaviors and detect anomalies across SAP, spanning the OS and network layer, the database layer, and the application and business logic layers. Then we moved to RISE with SAP on Azure. With that move, responsibility for instrumenting one of those layers transitioned to SAP under the RISE operating model. The visibility challenge shared responsibility creates In RISE with SAP, SAP operates the underlying infrastructure, operating system, and database as part of the managed service. This changes how customers obtain security telemetry from those layers and raises an important shared-responsibility question: how can the customer SOC maintain end-to-end visibility while SAP operates the platform? The layers remain relevant to security monitoring, so visibility must extend across both SAP-managed and customer-managed parts of the landscape. What changed: SAP LogServ meets Sentinel for SAP SAP LogServ is SAP's centralized log service for RISE-managed landscapes, carrying the security-relevant telemetry from the layers SAP now operates. Microsoft Sentinel for SAP ingests it directly, authenticated with managed identity for Azure. There is no stored secret, no rotation calendar and no bespoke connector for a future engineer to inherit and maintain. The integration is a configuration, not a project. “RISE with SAP introduces a shared operating model in which SAP manages the infrastructure while customers remain responsible for maintaining end-to-end security oversight. The integration of SAP LogServ with Microsoft Sentinel for SAP, secured through managed identity for Azure, brings telemetry from SAP-managed layers together with application-layer signals and the wider enterprise context. Our SOC can continue using familiar detections and workflows without a separate integration or credential-management process. At Microsoft, we believe in being Customer Zero, so we are putting this approach to work in our own RISE with SAP on Azure environment.” — Narasa Reddy Pekety, Principal Platform Lead, Microsoft Commerce Financial Platforms (CFP) For our SOC, the practical effect is that almost nothing about the working day changed. Events from SAP-managed layers land in the same tables queried by existing analytics rules based on Microsoft’s Advanced Security Information Model (ASIM), so detections tuned before the move can continue operating after it. Analysts remain in one console rather than managing a separate SAP queue and specialist on-call rotation. Cross-correlation – the ability to examine the points where SAP meets Dynamics 365 and the rest of our IT estate – remains especially important because it preserves the context that could otherwise be lost when telemetry is distributed across operating boundaries. “What I appreciate most is that we did not have to create a parallel operating model for SAP. We can reuse the analytics, investigation workflows, and response processes our SOC already knows, while adding the signals we were missing.” — Satya Veera Phaneendra Bonda, Platform Engineer, Microsoft Digital Who runs what, and where the signal comes from. An opinionated excerpt: Layer Operated by Signal path into our ISOC in Microsoft Defender Application and business logic Microsoft Microsoft Sentinel for SAP, as before the move Database SAP, Global Cloud Operations SAP LogServ Operating system and infrastructure SAP, Global Cloud Operations SAP LogServ Identity, endpoint and the wider cloud estate Microsoft Existing Microsoft Defender connectors, correlated with the above Co-engineering, in the open The part that matters most here is not the connector. It is a standing engineering relationship. The SAP LogServ team and the Microsoft Sentinel for SAP team work as one co-engineering group, shipping new security content on a continuous cadence: detections, analytics rules, watchlists and normalization for log sources as SAP exposes them. “By co-engineering SAP LogServ with Microsoft Sentinel for SAP, we turn SAP-managed telemetry into security insights customers can use immediately – and continue improving together as threats and landscapes evolve.” — Lalit Patil, EVP & CTO Global Cloud Operations, SAP That cadence is the direct continuation of the commitment made in the original solution, that the SAP and Sentinel teams would keep expanding threat-detection capabilities and the risk scenarios the product addresses as it evolves. “We built this as a co-engineering relationship rather than a connector handover, and that is what makes the estate legible to our perception agents. A security AI agent is only as good as the signal and the semantics it is handed. An agent reasoning over an unlabeled log stream is guessing; an agent reasoning over normalized, curated, continuously refreshed detection content is making an informed decision about what to escalate, what to correlate and what to close. Every piece of content the two teams ship raises the floor for every AI agent downstream of it.” — Martin Pankraz, Product Manager, SAP Security, Microsoft That work also attacks a problem we named in the first edition and never stopped working on: separating permissible activity from genuine threats, and improving alert fidelity rather than drowning analysts in false positives. Content that arrives already tuned to the layer it describes is the most direct lever we have on that ratio. Find the latest guidance always on the running engineering blog series on the SAP community. The foundation we need for the Agentic SOC This work also lays the groundwork for what comes next. Project Perception, Microsoft Security’s model for multi-agent defense, relies on blue team agents that detect, triage and respond to incidents, and those agents are only as effective as the signals they can reason over. SAP LogServ and Microsoft Sentinel for SAP provide exactly that: normalized, curated telemetry from the SAP-managed layers and the application layer, correlated with the wider enterprise estate in Sentinel. With that foundation in place, blue team agents can handle incidents involving SAP with the same context as any other part of our environment, rather than treating SAP as a black box. What comes next We intend to do what we did in 2022. We will share the challenges and the remedies as the work proceeds, so that customers can accelerate their own implementations with what we learn rather than rediscovering it. RISE with SAP does not have to mean less security visibility, but it does mean visibility has to be designed in rather than assumed, and designed in early enough that the SOC never works a period without it. We are running it ourselves first, as always. Final words We encourage all fellow RISE with SAP customers to verify their own cloud security posture, integrated SIEM practices, and choose to integrate with SAP LogServ as foundational service. Till next time. Related reading The first edition of this story: “Protecting Microsoft's SAP workload with Microsoft Sentinel,” Inside Track, February 4, 2022 — www.microsoft.com/insidetrack/blog/protecting-microsofts-sap-workload-with-microsoft-sentinel/ Microsoft Sentinel solutions for SAP | Microsoft Learn SAP LogServ integration with Microsoft Sentinel Solution for SAP overview | Microsoft Learn Microsoft Ignite 2026 Sentinel Connector announcments | TechCommunity285Views0likes0CommentsThe leaver who never left: tuning a Sentinel detection from 103 rows to one alert
Most account compromise detections look for something odd: a new country, an impossible journey, or a sign-in at 3 AM. I wanted to catch a case where nothing looks odd at all. Someone leaves the organisation. HR knows, their manager knows, but the request to disable their account sits in a queue or never gets raised. A week later, they sign in from the same laptop, on the same Wi-Fi, into the same apps they used every day. To Entra ID, that is a normal sign-in. Location rules have nothing to catch because nothing has changed. I started from a threat model for a hospital running Microsoft 365. Of the threats I scored, this one stood out because it requires no advanced skill. The person already has a password that works. The only signal is that they are not supposed to be there anymore, and that fact lives with HR, not in the logs. So, the detection has to bring that context into Microsoft Sentinel. Writing it in plain words first Before writing any KQL, I defined exactly what the rule should do: • When an account signs in successfully • AND it is on HR's leavers list • AND the sign-in is after their leave date • THEN raise one High-severity alert per person • EXCEPT when IT is already closing the account, or the person has been rehired The sign-ins are in SigninLogs. For the leavers list, I used a Sentinel watchlist: a CSV with two columns, UserPrincipalName and LeaveDate. To test it, I put my own account on the list with a leave date in the past, so every sign-in after that date should trigger. Version 1 let Leavers = _GetWatchlist('Leavers') | project UPN = tolower(tostring(SearchKey)); SigninLogs | where TimeGenerated > ago(7d) | where ResultType == "0" | where tolower(UserPrincipalName) in (Leavers) | project TimeGenerated, UserPrincipalName, AppDisplayName, IPAddress, Location It worked, and that was the problem. It returned 103 rows for one person: every token refresh, every app. An analyst opening that incident would scroll through a hundred near-identical lines to learn one thing: this person is still getting in. It also ignored the leave date, so it would fire on sign-ins from before someone left as well. Version 2 I made two changes: only count sign-ins after the leave date, and summarise per person instead of listing every event. The result was one row: 103 sign-ins, the first and last time seen, the 4 apps used, and the 2 IP addresses. That is exactly what an analyst needs to decide what to do next. The bug that took the longest Version 2 failed with this error: Failed to resolve scalar expression named 'LeaveDate' The column was clearly there. I could see it in the watchlist. I rewrote the query more than once before I looked at the raw Watchlist table and saw the column was actually called " LeaveDate", with a leading space. The CSV had been saved with a space after each comma. The header looked fine to me, and Sentinel took it literally. The fix was to read the Watchlist table directly, use coalesce() to accept either spelling of the column, and trim() to strip spaces from the values. The bigger lesson: lists from other teams will not always be clean, and a detection should cope with that rather than break. The final query let Leavers = Watchlist | where TimeGenerated > ago(90d) | where WatchlistAlias == "Leavers" | summarize arg_max(TimeGenerated, *) by _DTItemId | where _DTItemStatus != "Delete" | extend RawDate = coalesce(tostring(WatchlistItem["LeaveDate"]), tostring(WatchlistItem[" LeaveDate"])) | project UPN = tolower(trim(@"\s", tostring(SearchKey))), LeaveDate = todatetime(trim(@"\s", RawDate)); SigninLogs | where TimeGenerated > ago(7d) | where ResultType == "0" | extend UPN = tolower(UserPrincipalName) | join kind=inner Leavers on UPN | where TimeGenerated > LeaveDate | summarize SignIns = count(), FirstSeen = min(TimeGenerated), LastSeen = max(TimeGenerated), Apps = make_set(AppDisplayName), IPs = make_set(IPAddress) by UPN, LeaveDate arg_max keeps only the latest version of each watchlist row, and the _DTItemStatus filter drops rows that have been deleted, so someone taken off the list stops alerting. What I would add before using it for real • Feed the list from the HR system instead of uploading a CSV by hand. A list that is two weeks out of date has the same gap as no list. • Build in the exceptions: accounts IT is already closing, and rehires. • Make it a scheduled rule: hourly, 7-day lookback, High severity, with the user mapped as an account entity so the incident links to anything else that account has done. • Check the data is arriving. In the same lab, I found three log sources that had been silent for a month with no error anywhere. A detection is only as good as the data under it. The queries and notes are available on my GitHub: github.com/RabiatuMohammed/sentinel-detections Update: catching the re-enable, not just the sign-in After publishing this, I tested a worse version of the problem. I disabled a test account, watched it get refused at sign-in, then switched it back on. Two minutes later, it was signed in again. 13:11 - Account disabled (AuditLogs: Disable account) 13:15 - Sign-in refused (SigninLogs: 50057, account disabled) 13:29 - Account re-enabled (AuditLogs: Enable account) 13:31 - Signed in again (SigninLogs: 0, success) The rule above only fires at 13:31, after they are back in. The moment that actually matters is 13:29. Disabling the account was the right ending, so switching it back on needs a reason. So, I wrote a second rule that watches for "Enable account" on anyone on the leavers list, and shows who did it: AuditLogs | where OperationName == "Enable account" | extend UPN = tolower(tostring(TargetResources[0].userPrincipalName)), EnabledBy = coalesce(tostring(InitiatedBy.user.userPrincipalName), tostring(InitiatedBy.app.displayName)) | join kind=inner Leavers on UPN | where TimeGenerated > LeaveDate | project TimeGenerated, UPN, LeaveDate, EnabledBy Against the test, it returned one row at 13:29, two minutes before the sign-in. One thing surprised me: the sign-in screen told the user the account was locked, but the log said disabled (50057). Locked would have been 50053. I now go by the error code, not by what the user says they saw. The full query is available on GitHub as DET-LEAVER-02.183Views0likes3CommentsRSAC 2026: New Microsoft Sentinel Connectors Announcement
Microsoft Sentinel helps organizations detect, investigate, and respond to security threats across increasingly complex environments. With the rollout of the Microsoft Sentinel data lake in the fall, and the App Assure-backed Sentinel promise that supports it, customers now have access to long-term, cost-effective storage for security telemetry, creating a solid foundation for emerging Agentic AI experiences. Since our last announcement at Ignite 2025, the Microsoft Sentinel connector ecosystem has expanded rapidly, reflecting continued investment from software development partners building for our shared customers. These connectors bring diverse security signals together, enabling correlation at scale and delivering richer investigation context across the Sentinel platform. Below is a snapshot of Microsoft Sentinel connectors newly available or recently enhanced since our last announcement, highlighting the breadth of partner solutions contributing data into, and extending the value of, the Microsoft Sentinel ecosystem. New and notable integrations Acronis Cyber Protect Cloud Acronis Cyber Protect Cloud integrates with Microsoft Sentinel to bring data protection and security telemetry into a centralized SOC view. The connector streams alerts, events, and activity data - spanning backup, endpoint protection, and workload security - into Microsoft Sentinel for correlation with other signals. This integration helps security teams investigate ransomware and data-centric threats more effectively, leverage built-in hunting queries and detection rules, and improve visibility across managed environments without adding operational complexity. Anvilogic Anvilogic integrates with Microsoft Sentinel to help security teams operationalize detection engineering at scale. The connector streams Anvilogic alerts into Microsoft Sentinel, giving SOC analysts centralized visibility into high-fidelity detections and faster context for investigation and triage. By unifying detection workflows, reducing alert noise, and improving prioritization, this integration supports more efficient threat detection and response while helping teams extend coverage across evolving attack techniques. BigID BigID integrates with Microsoft Sentinel to extend data security posture management (DSPM) insights into security operations workflows. The solution brings visibility into sensitive, regulated, and critical data across cloud, SaaS, and on‑premises environments, helping security teams understand where high‑risk data resides and how it may be exposed. By incorporating data‑centric risk context into Sentinel, this integration supports more informed investigation and prioritization, enabling organizations to reduce data‑related risk and align security operations with data protection and compliance objectives. Commvault Cloud Commvault Cloud integrates with Microsoft Sentinel to bring data protection and cyber‑resilience telemetry into security operations workflows. The connector ingests security‑relevant signals from Commvault Cloud—such as backup anomalies, malware and ransomware indicators, and other threat‑related events—into Sentinel, enabling centralized detection, investigation, and automated response. By correlating backup intelligence with broader Sentinel telemetry, this integration helps security teams reduce blind spots, validate the scope of incidents, and improve coordination between security and recovery operations. CyberArk Audit CyberArk Audit integrates with Microsoft Sentinel to centralize visibility into privileged identity and access activity. By streaming detailed audit logs - covering system events, user actions, and administrative activity - into Microsoft Sentinel, security teams can correlate identity-driven risks with broader security telemetry. This integration supports faster investigations, improved monitoring of privileged access, and more effective incident response through automated workflows and enriched context for SOC analysts. Cyera Cyera integrates with Microsoft Sentinel to extend AI-native data security posture management into security operations. The connector brings Cyera’s data context and actionable intelligence across multi-cloud, on-premises, and SaaS environments into Microsoft Sentinel, helping teams understand where sensitive data resides and how it is accessed, exposed, and used. Built on Sentinel’s modern framework, the integration feeds context-rich data risk signals into the Sentinel data lake, enabling more informed threat hunting, automation, and decision-making around data, user, and AI-related risk. TacitRed CrowdStrike IOC Automation Data443 TacitRed CS IOC Automation integrates with Microsoft Sentinel to streamline the operationalization of compromised credential intelligence. The solution uses Sentinel playbooks to automatically push TacitRed indicators of compromise into CrowdStrike via Sentinel playbooks, helping security teams turn identity-based threat intelligence into action. By automating IOC handling and reducing manual effort, this integration supports faster response to credential exposure and strengthens protection against account-driven attacks across the environment. TacitRed SentinelOne IOC Automation Data443 TacitRed SentinelOne IOC Automation integrates with Microsoft Sentinel to help operationalize identity-focused threat intelligence at the endpoint layer. The solution uses Sentinel playbooks to automatically consume TacitRed indicators and push curated indicators into SentinelOne via Sentinel playbooks and API-based enforcement, enabling faster enforcement of high-risk IOCs without manual handling. By automating the flow of compromised credential intelligence from Sentinel into EDR, this integration supports quicker response to identity-driven attacks and improves coordination between threat intelligence and endpoint protection workflows. TacitRed Threat Intelligence Data443 TacitRed Threat Intelligence integrates with Microsoft Sentinel to provide enhanced visibility into identity-based risks, including compromised credentials and high-risk user exposure. The solution ingests curated TacitRed intelligence directly into Sentinel, enriching incidents with context that helps SOC teams identify credential-driven threats earlier in the attack lifecycle. With built-in analytics, workbooks, and hunting queries, this integration supports proactive identity threat detection, faster triage, and more informed response across the SOC. Cyren Threat Intelligence Cyren Threat Intelligence integrates with Microsoft Sentinel to enhance detection of network-based threats using curated IP reputation and malware URL intelligence. The connector ingests Cyren threat feeds into Sentinel using the Codeless Connector Framework (CCF), transforming raw indicators into actionable insights, dashboards, and enriched investigations. By adding context to suspicious traffic and phishing infrastructure, this integration helps SOC teams improve alert accuracy, accelerate triage, and make more confident response decisions across their environments. TacitRed Defender Threat Intelligence Data443 TacitRed Defender Threat Intelligence integrates with Microsoft Sentinel to surface early indicators of credential exposure and identity-driven risk. The solution automatically ingests compromised credential intelligence from TacitRed into Sentinel and can support synchronization of validated indicators with Microsoft Defender Threat Intelligence through Sentinel workflows, helping SOC teams detect account compromise before abuse occurs. By enriching Sentinel incidents with actionable identity context, this integration supports faster triage, proactive remediation, and stronger protection against credential-based attacks. Datawiza Access Proxy (DAP) Datawiza Access Proxy integrates with Microsoft Sentinel to provide centralized visibility into application access and authentication activity. By streaming access and MFA logs from Datawiza into Sentinel, security teams can correlate identity and session-level events with broader security telemetry. This integration supports detection of anomalous access patterns, faster investigation through session traceability, and more effective response using Sentinel automation, helping organizations strengthen Zero Trust controls and meet auditing and compliance requirements. Endace Endace integrates with Microsoft Sentinel to provide deep network visibility by providing always-on, packet-level evidence. The connector enables one-click pivoting from Sentinel alerts directly to recorded packet data captured by EndaceProbes. This helps SOC and NetOps teams reconstruct events and validate threats with confidence. By combining Sentinel’s AI-driven analytics with Endace’s always-on, full-packet capture across on-premises, hybrid, and cloud environments, this integration supports faster investigations, improved forensic accuracy, and more decisive incident response. Feedly Feedly integrates with Microsoft Sentinel to ingest curated threat intelligence directly into security operations workflows. The connector automatically imports Indicators of Compromise (IoCs) from Feedly Team Boards and folders into Sentinel, enriching detections and investigations with context from the original intelligence articles. By bringing analyst‑curated threat intelligence into Sentinel in a structured, automated way, this integration helps security teams stay current on emerging threats and reduce the manual effort required to operationalize external intelligence. Gigamon Gigamon integrates with Microsoft Sentinel through a new connector that provides access to Gigamon Application Metadata Intelligence (AMI), delivering high-fidelity network-derived telemetry with rich application metadata from inspected traffic directly into Sentinel. This added context helps security teams detect suspicious activity, encrypted threats, and lateral movement faster and with greater precision. By enriching analytics without requiring full packet ingestion, organizations can reduce noise, manage SIEM costs, and extend visibility across hybrid cloud infrastructure. Halcyon Halcyon integrates with Microsoft Sentinel to provide purpose-built ransomware detection and automated containment across the Microsoft security ecosystem. The connector surfaces Halcyon ransomware alerts directly within Sentinel, enabling SOC teams to correlate ransomware behavior with Microsoft Defender and broader Microsoft telemetry. By supporting Sentinel analytics and automation workflows, this integration helps organizations detect ransomware earlier, investigate faster using native Sentinel tools, and isolate affected endpoints to prevent lateral spread and reinfection. Illumio The Illumio platform identifies and contains threats across hybrid multi-cloud environments. By integrating AI-driven insights with Microsoft Sentinel and Microsoft Graph, Illumio Insights enables SOC analysts to visualize attack paths, prioritize high-risk activity, and investigate threats with greater precision. Illumio Segmentation secures critical assets, workloads, and devices and then publishes segmentation policy back into Microsoft Sentinel to ensure compliance monitoring. Joe Sandbox Joe Sandbox integrates with Microsoft Sentinel to enrich incidents with dynamic malware and URL analysis. The connector ingests Joe Sandbox threat intelligence and automatically detonates suspicious files and URLs associated with Sentinel incidents, returning behavioral and contextual analysis results directly into investigation workflows. By adding sandbox-driven insights to indicators, alerts, and incident comments, this integration helps SOC teams validate threats faster, reduce false positives, and improve response decisions using deeper visibility into malicious behavior. Keeper Security The Keeper Security integration with Microsoft Sentinel brings advanced password and secrets management telemetry into your SIEM environment. By streaming audit logs and privileged access events from Keeper into Sentinel, security teams gain centralized visibility into credential usage and potential misuse. The connector supports custom queries and automated playbooks, helping organizations accelerate investigations, enforce Zero Trust principles, and strengthen identity security across hybrid environments. Lookout Mobile Threat Defense (MTD) Lookout Mobile Threat Defense integrates with Microsoft Sentinel to extend SOC visibility to mobile endpoints across Android, iOS, and Chrome OS. The connector streams device, threat, and audit telemetry from Lookout into Sentinel, enabling security teams to correlate mobile risk signals such as phishing, malicious apps, and device compromise, with broader enterprise security data. By incorporating mobile threat intelligence into Sentinel analytics, dashboards, and alerts, this integration helps organizations detect mobile driven attacks earlier and strengthen protection for an increasingly mobile workforce. Miro Miro integrates with Microsoft Sentinel to provide centralized visibility into collaboration activity across Miro workspaces. The connector ingests organization-wide audit logs and content activity logs into Sentinel, enabling security teams to monitor authentication events, administrative actions, and content changes alongside other enterprise signals. By bringing Miro collaboration telemetry into Sentinel analytics and dashboards, this integration helps organizations detect suspicious access patterns, support compliance and eDiscovery needs, and maintain stronger oversight of collaborative environments without disrupting productivity. Obsidian Activity Threat The Obsidian Threat and Activity Feed for Microsoft Sentinel delivers deep visibility into SaaS and AI applications, helping security teams detect account compromise and insider threats. By streaming user behavior and configuration data into Sentinel, organizations can correlate application risks with enterprise telemetry for faster investigations. Prebuilt analytics and dashboards enable proactive monitoring, while automated playbooks simplify response workflows, strengthening security posture across critical cloud apps. OneTrust for Purview DSPM OneTrust integrates with Microsoft Sentinel to bring privacy, compliance, and data governance signals into security operations workflows. The connector enriches Sentinel with privacy relevant events and risk indicators from OneTrust, helping organizations detect sensitive data exposure, oversharing, and compliance risks across cloud and non-Microsoft data sources. By unifying privacy intelligence with Sentinel analytics and automation, this integration enables security and privacy teams to respond more quickly to data risk events and support responsible data use and AI-ready governance. Pathlock Pathlock integrates with Microsoft Sentinel to bring SAP-specific threat detection and response signals into centralized security operations. The connector forwards security-relevant SAP events into Sentinel, enabling SOC teams to correlate SAP activity with broader enterprise telemetry and investigate threats using familiar SIEM workflows. By enriching Sentinel with SAP security context and focused detection logic, this integration helps organizations improve visibility into SAP landscapes, reduce noise, and accelerate detection and response for risks affecting critical business systems. Quokka Q-scout Quokka Q-scout integrates with Microsoft Sentinel to centralize mobile application risk intelligence across Microsoft Intune-managed devices. The connector automatically ingests app inventories from Intune, analyzes them using Quokka’s mobile app vetting engines, and streams security, privacy, and compliance risk findings into Sentinel. By surfacing app-level risks through Sentinel analytics and alerts, this integration helps security teams identify malicious or high-risk mobile apps, prioritize remediation, and strengthen mobile security posture without deploying agents or disrupting users. Semperis Lightning Semperis Lightning integrates with Microsoft Sentinel to deliver deep visibility into identity‑centric risk across Active Directory and Microsoft Entra environments. The connector ingests identity security telemetry such as indicators of exposure, Tier 0 assets, and attack path insights into Sentinel, enabling security teams to correlate identity risks with broader security signals. By bringing rich identity context into Sentinel analytics, hunting, and investigations, this integration helps organizations detect, prioritize, and respond to identity‑driven attacks more effectively across hybrid identity infrastructures. Synqly Synqly integrates with Microsoft Sentinel to simplify and scale security integrations through a unified API approach. The connector enables organizations and security vendors to establish a bi‑directional connection with Sentinel without relying on brittle, point‑to‑point integrations. By abstracting common integration challenges such as authentication handling, retries, and schema changes, Synqly helps teams orchestrate security data flows into and out of Sentinel more reliably, supporting faster onboarding of new data sources and more maintainable integrations at scale. Versasec vSEC:CMS Versasec vSEC:CMS integrates with Microsoft Sentinel to provide centralized visibility into credential lifecycle and system health events. The connector securely streams vSEC:CMS and vSEC:CLOUD alerts and status data into Sentinel using the Codeless Connector Framework (CCF), transforming credential management activity into correlation-ready security signals. By bringing smart card, token, and passkey management telemetry into Sentinel, this integration helps security teams monitor authentication infrastructure health, investigate credential-related incidents, and unify identity security operations within their SIEM workflows. VirtualMetric DataStream VirtualMetric DataStream integrates with Microsoft Sentinel to optimize how security telemetry is collected, normalized, and routed across the Microsoft security ecosystem. Acting as a high-performance telemetry pipeline, DataStream intelligently filters and enriches logs, sending high-value security data to Sentinel while routing less-critical data to Sentinel data lake or Azure Blob Storage for cost-effective retention. By reducing noise upstream and standardizing logs to Sentinel ready schemas, this integration helps organizations control ingestion costs, improve detection quality, and streamline threat hunting and compliance workflows. VMRay VMRay integrates with Microsoft Sentinel to enrich SIEM and SOAR workflows with automated sandbox analysis and high-fidelity, behavior-based threat intelligence. The connector enables suspicious files and phishing URLs to be submitted directly from Sentinel to VMRay for dynamic analysis, while validated, high-confidence indicators of compromise (IOCs) are streamed back into Sentinel’s Threat Intelligence repository for correlation and detection. By adding detailed attack-chain visibility and enriched incident context, this integration helps SOC teams reduce investigation time, improve detection accuracy, and strengthen automated response workflows across Sentinel environments. XBOW XBOW integrates with Microsoft Sentinel to bring autonomous penetration testing insights directly into security operations workflows. The connector ingests automated penetration test findings from the XBOW platform into Sentinel, enabling security teams to analyze validated exploit activity alongside alerts, incidents, and other security telemetry. By correlating offensive testing results with Sentinel detections, this integration helps organizations identify monitoring gaps, validate detection coverage, and strengthen defensive controls using real‑world, continuously generated attack evidence. Zero Networks Segment Audit Zero Networks Segment integrates with Microsoft Sentinel to provide visibility into micro-segmentation and access-control activity across the network. The connector can collect audit logs or activities from Zero Networks Segment, enabling security teams to monitor policy changes, administrative actions, and access events related to MFA-based network segmentation. By bringing segmentation audit telemetry into Sentinel, this integration supports compliance monitoring, investigation of suspicious changes, and faster detection of attempts to bypass lateral-movement controls within enterprise environments. Zscaler Internet Access (ZIA) Zscaler Internet Access integrates with Microsoft Sentinel to centralize cloud security telemetry from web and firewall traffic. The connector enables ZIA logs to be ingested into Sentinel, allowing security teams to correlate Zscaler Internet Access signals with other enterprise data for improved threat detection, investigation, and response. By bringing ZIA web, firewall, and security events into Sentinel analytics and hunting workflows, this integration helps organizations gain broader visibility into internet-based threats and strengthen Zero Trust security operations. In addition to these solutions from our third-party partners, we are also excited to announce the following connector published by the Microsoft Sentinel team: GitHub Enterprise Audit Logs Microsoft’s Sentinel Promise For Customers Every connector in the Microsoft Sentinel ecosystem is built to work out of the box. In the unlikely event a customer encounters any issue with a connector, the App Assure team stands ready to assist. For Software Developers Software partners in need of assistance in creating or updating a Sentinel solution can also leverage Microsoft’s Sentinel Promise to support our shared customers. For developers seeking to build agentic experiences utilizing Sentinel data lake, we are excited to announce the launch of our Sentinel Advisory Service to guide developers across their Sentinel journey. Customers and developers alike can reach out to us via our intake form. Learn More Microsoft Sentinel data lake Microsoft Sentinel data lake: Unify signals, cut costs, and power agentic AI Introducing Microsoft Sentinel data lake What is Microsoft Sentinel data lake Unlocking Developer Innovation with Microsoft Sentinel data lake Microsoft Sentinel Codeless Connector Framework (CCF) Create a codeless connector for Microsoft Sentinel Public Preview Announcement: Microsoft Sentinel CCF Push What’s New in Microsoft Sentinel Monthly Blog Microsoft App Assure App Assure home page App Assure services App Assure blog App Assure Request Assistance Form App Assure Sentinel Advisory Services announcement App Assure’s promise: Migrate to Sentinel with confidence App Assure’s Sentinel promise now extends to Microsoft Sentinel data lake Ignite 2025 new Microsoft Sentinel connectors announcement Microsoft Security Microsoft’s Secure Future Initiative Microsoft Unified SecOps Editor's Note - April 7th, 2026: This blog was updated to include connector descriptions for BigID, Commvault, Semperis, and XBOW.2.6KViews0likes0Comments
Part 4: See, investigate, and measure email and collaboration attacks with Defender reporting
The fourth release in our Defender reporting series helps security teams see the email and Teams attacks that matter, investigate them faster, and measure whether their people are becoming more resilient.742Views0likes0CommentsDeclutter and Defend: Reducing promotional mail noise with Microsoft Defender
Enterprise inboxes are overwhelmed with graymail — legitimate, bulk email like newsletters, vendor promotions, and product updates that isn't malicious but buries the messages that matter. When high volumes of these mails land in the inbox, it crowds out priority communications and can dull security vigilance. Employees conditioned to ignore repetitive emails may miss signs of a real threat. It also creates recurring work for admins and security teams who must continuously tune filters, manage exception requests, and chase noise from user reports for email that isn’t malicious. Because graymail passes every spam filter check, traditional defenses don't separate it — leaving this signal-to-noise gap unaddressed. Today we’re excited to announce that Microsoft Defender now includes built-in graymail filtering. It is delivered natively through a new Promotions experience in Outlook that automatically classifies and separates bulk email, so it no longer competes with business-critical communication in the inbox. Now in Public Preview, this capability learns from how users interact with graymail to become more accurate over time. Coupled with the existing Bulk Senders Insight report, Defender brings data-driven bulk classification and control into the security workflows you already use. What Is Graymail? Graymail is legitimate bulk email that isn't malicious—product newsletters, event announcements, marketing promotions, and software update notifications from reputable, authenticated senders. It is distinct from spam and from phishing - graymail comes from real organizations with proper authentication and traditional spam filters aren't designed to handle it. Graymail handling in Microsoft Defender Microsoft Defender's approach is built on three principles: classify intelligently, deliver natively, and learn continuously. Promotions Folder — Intelligent Inbox Organization A dedicated Promotions folder, natively provisioned in Outlook, now keeps legitimate bulk mail out of the primary inbox. Promotional content is separated from priority emails without being sent to Junk, which means users can still access and browse newsletters and updates at their own pace. The folder appears at the top level of the mailbox for easy discovery and is visible across all Outlook experiences. Non-spam bulk mail below the organization's configured Bulk Complaint Level threshold is automatically routed to the Promotions folder. Messages from senders the user has explicitly allowed continue to land in the Inbox. Messages identified as spam continue to go to Junk. To enable the Promotions folder administrators need to enable the "Bulk Moves Enabled" setting in their anti-spam policy. The Promotions folder is then created for all users and used for routing only when this setting is ON. Existing mail flow is unaffected. Promotional mail tagging and Mailbox Rule Support Messages classified as graymail will automatically be labeled with a "Promotions" system tag in Outlook. The tag provides instant visual context without requiring users to open each message and is visible in Outlook on the Web and the native Outlook desktop apps for Windows and Mac. During Public Preview, the tagging component is opt-in, requiring administrators to enable it by configuring an Exchange Transport Rule. Once generally available, it will be enabled by default. Because this classification is integrated at the client level, the Promotions tag can also be used as a condition in Outlook mailbox rules. This enables custom routing logic for advanced scenarios like moving all promotions-tagged messages from a specific sender to a custom folder, flagging certain promotional emails for follow-up, or auto-forwarding or deleting promotions that meet specific criteria. This transforms the Promotions classification from a one-way filter into a flexible building block for personal and organizational workflows—particularly valuable for power users and teams with compliance or archival requirements. Adaptive Learning Microsoft Defender's graymail filtering gets smarter with every interaction. The system learns directly from how users handle their mail. When a user moves a message out of the Promotions folder and back to the Inbox, future emails from that sender will no longer be placed in the Promotions folder. When a user moves a message from the Inbox into the Promotions folder, future emails from that sender will be routed to the Promotions folder automatically. This creates a personalized, self-improving experience that becomes more accurate over time - no manual rule configuration required, no safe-sender lists to maintain, and no filtering rules for IT teams to manage on behalf of individual employees. Built into existing Security Workflows Administrators also gain visibility through the Bulk Senders Insight report, which provides data-driven guidance on what your organization actually receives and can help tune your bulk mail filtering. Graymail has long been the unsolved middle ground of email security—too legitimate to block, too noisy to ignore. Microsoft Defender now handles it where it should be handled: inside the platform, inside the mailbox, and inside the security workflows your organization already relies on. No new portals, no new vendors, no compromise between security and user experience. Get Started Configure promotions tagging and the promotions folder today - Bulk email detection documentation on Microsoft Learn. Monitor the experience using the Bulk Senders Insight report.14KViews5likes14CommentsYou may be right after all! Disputing Submission Responses in Microsoft Defender for Office 365
Introduction As a Microsoft MVP (Most Valuable Professional) specializing in SIEM, XDR, and Cloud Security, I have witnessed the rapid evolution of cybersecurity technologies, especially those designed to protect organizations from sophisticated threats targeting email and collaboration tools. Microsoft Defender for Office 365 introduced an LLM-based engine to help better classify phishing emails that, these days, are mostly written using AI anyways about a year ago. Today, I'm excited to spotlight a new place AI has been inserted into a workflow to make it better…a feature that elevates the transparency and responsiveness of threat management: the ability to dispute a submission response directly within Microsoft Defender for Office 365. Understanding the Challenge While the automated and human-driven analyses are robust in Defender for Office 365, there are occasions where the response—be it a verdict of "benign" or "malicious"— doesn’t fully align with the security team's context or threat intelligence. If you are a Microsoft 365 organization with Exchange Online mailboxes, you’re probably familiar with how admins can use the Submissions page in the Microsoft Defender portal to submit messages, URLs, and attachments to Microsoft for analysis. As a recent enhancement, now all the admin submissions use LLM based response for better explainability. In the past, disputing such verdicts required separate support channels, using Community support, or manual email processes, often delaying resolution and impacting the speed of cyber operations. Introducing the Dispute Submission Response Feature With the new dispute submission response feature, Microsoft Defender for Office 365 bridges a critical gap in the incident response workflow. Now, when a security analyst or administrator receives a verdict on a submitted item, they have the option to dispute the response directly within the Microsoft 365 Defender portal. This feature streamlines feedback, allowing teams to quickly flag disagreements and provide additional context for review at the speed of operations. How It Works Upon submission of a suspicious item, Microsoft Defender for Office 365 provides a response indicating its assessment—malicious, benign, or other categorizations. If the security team disagrees with the verdict, they can select the "Dispute" option and submit their rationale, including supporting evidence and threat intelligence. The disputed case is escalated directly to Microsoft’s threat research team for further review, and the team is notified of progress and outcomes. This direct feedback loop not only empowers security teams to advocate for their organization's unique context, but also enables Microsoft to continually refine detection algorithms and verdict accuracy based on real-world input, because security is a team sport. Benefits for Security Operations Faster Resolution: Streamlined dispute submission eliminates the need for external support tickets and escalations, reducing turnaround time for critical cases. Greater Transparency: The feature fosters a collaborative relationship between customers and Microsoft, ensuring that verdicts are not final judgments but points in an ongoing dialogue. Continuous Improvement: Feedback from disputes enhances Microsoft’s threat intelligence and improves detection for all Defender for Office 365 users. Empowerment: Security teams gain a stronger voice in the protection of their environment, reinforcing trust in automated defenses. MVP Insights: Real-World Impact Having worked with global enterprises, I’ve seen how nuanced and context-specific threats can be. Sometimes, what appears benign to one organization may be a targeted attack for another, a slight modification to a URL may catch one email, but not others, as slight changes are made as billions of emails are sent. We are only as good as the consortium. The ability to dispute submission responses creates a vital safety net, ensuring that security teams are not forced to accept verdicts that could expose them to risk. It’s a welcome step toward adaptive, user-driven security operations. Conclusion The dispute submission response feature in Microsoft Defender for Office 365 is one of the most exciting features for me, because it focuses on enabling organizations striving for agility and accuracy in threat management. By enabling direct, contextual feedback, Microsoft empowers security teams to play an active role in shaping their defenses. As an MVP, I encourage all users to leverage this feature, provide detailed feedback, and help drive the future of secure collaboration in the cloud. You may be right after all. _________ This blog has been generously and expertly authored by Microsoft Security MVP, Mona Ghadiri with support of the Microsoft Defender for Office 365 product team. Mona Ghadiri Microsoft Security MVP Learn More and Meet the Author 1) December 16th Ask the Experts Webinar: Microsoft Defender for Office 365 | Ask the Experts: Tips and Tricks (REGISTER HERE) DECEMBER 16, 8 AM US Pacific You’ve watched the latest Microsoft Defender for Office 365 best practices videos and read the blog posts by the esteemed Microsoft Most Valuable Professionals (MVPs). Now bring your toughest questions or unique situations straight to the experts. In this interactive panel discussion, Microsoft MVPs will answer your real-world scenarios, clarify best practices, and highlight practical tips surfaced in the recent series. We’ll kick off with a who’s who and recent blog/video series recap, then dedicate most of the time to your questions across migration, SOC optimization, fine-tuning configuration, Teams protection, and even Microsoft community engagement. Come ready with your questions (or pre-submit here) for the expert Security MVPs on camera, or the Microsoft Defender for Office 365 product team in the chat! REGISTER NOW for 12/16. 2) Additional MVP Tips and Tricks Blogs and Videos in this Four-Part Series: 1. Microsoft Defender for Office 365: Migration & Onboarding by Purav Desai 2. Safeguarding Microsoft Teams with Microsoft Defender for Office 365 by Pierre Thoor 3. (This blog post) You may be right after all! Disputing Submission Responses in Microsoft Defender for Office 365 by Mona Ghadiri 4. Microsoft Defender for Office 365: Fine-Tuning | Real-world Defender for Office 365 tuning that closes real attack paths by Joe Stocker Learn and Engage with the Microsoft Security Community Log in and follow this Microsoft Defender for Office 365 blog and follow/post in the Microsoft Defender for Office 365 discussion space. Follow = Click the heart in the upper right when you're logged in 🤍 Learn more about the Microsoft MVP Program. Join the Microsoft Security Community and be notified of upcoming events, product feedback surveys, and more. Get early access to Microsoft Security products and provide feedback to engineers by joining the Microsoft Customer Connection Community. Join the Microsoft Security Community LinkedIn2.2KViews4likes1CommentHunting AI Agent Configuration Drift with Microsoft Sentinel
Four KQL patterns for detecting instruction changes, new MCP servers, ownership changes, and organization-wide sharing I recently authored and contributed four new Microsoft Sentinel hunting queries for detecting security-relevant configuration drift in AI agents. They have been reviewed, approved, and merged into Microsoft's public Azure-Sentinel repository. I built the queries around four changes that can materially affect an agent's behavior, access, or exposure: instructions being modified, MCP servers being connected, owners being added, and sharing being expanded to the entire organization. Each modification may be legitimate, but each deserves enough context for a security team to verify that it was expected and authorized. For a security operations team, the difficult question is often not what does this agent look like now? It is what changed since the last known state? Microsoft Sentinel's AgentsInfo table provides inventory-style snapshots of AI agents and their associated configuration. That makes it useful for more than posture reporting. By comparing a recent snapshot with an earlier baseline, we can hunt for configuration drift that deserves investigation. This post walks through four practical hunting scenarios: Instructions changed on a previously published agent A newly observed MCP server on an existing agent An owner added to an MCP-enabled agent Sharing expanded from a restricted scope to the entire organization The complete hunting queries are available in Microsoft's public https://github.com/Azure/Azure-Sentinel/tree/master/Hunting%20Queries/AI%20Agents. The focus here is the detection design behind them, the KQL patterns they share, and the investigation questions they help answer. What I contributed I wrote the four standalone hunting queries discussed in this article and submitted them to Azure/Azure-Sentinel in https://github.com/Azure/Azure-Sentinel/pull/14702: AI Agents - Instructions changed on previously published agent AI Agents - Newly observed MCP server on existing agent AI Agents - Owner added to MCP-enabled agent AI Agents - Sharing expanded to organization-wide The contribution went through several rounds of technical review. Across six commits, I aligned the queries with the unified AgentsInfo schema, added schema-tolerant IdentityInfo enrichment, improved entity mappings, bounded the identity lookback, expanded all owner values, and kept the ATT&CK mappings limited to scenarios where a precise technique could be defended. Repository collaborator v-atulyadav approved the final revision, and the four queries were merged into master on July 20, 2026. This article explains the detection logic and engineering decisions behind that contribution rather than simply reproducing the final YAML files. Why current-state queries are not enough A current-state query can answer questions such as: Which agents are published? Which agents have MCP servers configured? Which agents are shared with the organization? Who owns a particular agent? Those are important posture questions, but they do not tell us whether the state is new. An agent with an MCP server might have been reviewed and approved months ago. The same MCP server appearing for the first time today is a different security signal. Configuration-drift hunting adds the missing time dimension. Instead of treating a risky-looking property as an event, it compares two states of the same agent and reports only meaningful transitions. The common detection pattern I used the same basic time model across all four hunts: let lookback = 14d; let recent = 2d; The latest snapshot observed during the last two days becomes the current state. The latest snapshot from the preceding portion of the 14-day lookback becomes the baseline. Conceptually, the comparison looks like this: let CurrentState = AgentsInfo | where Timestamp > ago(recent) | summarize arg_max(Timestamp, *) by AgentId | where LifecycleStatus != "Deleted"; let BaselineState = AgentsInfo | where Timestamp between (ago(lookback) .. ago(recent)) | where LifecycleStatus != "Deleted" | summarize arg_max(Timestamp, *) by AgentId; CurrentState | join kind=inner BaselineState on AgentId Several details matter here: arg_max(Timestamp, *) by AgentId selects the latest available state for each agent in the relevant time range. The inner join restricts results to agents that exist in both periods. A newly created agent is therefore not automatically treated as configuration drift on an existing agent. Deleted lifecycle snapshots are excluded so that a deletion record does not become the effective baseline or current configuration. The two-day current window is operationally significant. To retain coverage, these hunts should run within two days of a change. The 14-day and two-day values are practical defaults, not universal constants. Environments with different ingestion cadence or retention requirements can adjust them, but the current and baseline windows must remain non-overlapping. Scenario 1: Instructions changed on a published agent An agent's instructions define its default behavior, persona, and operating boundaries. Changing them can be part of normal development, but it can also weaken restrictions, redirect the agent's behavior, or modify how it uses connected capabilities. The first hunt compares the current and previous instruction values only when the agent was published in both snapshots: CurrentState | join kind=inner BaselineState on AgentId | where CurrentInstructions != PreviousInstructions | extend PreviousInstructionsHash = hash_sha256(PreviousInstructions), CurrentInstructionsHash = hash_sha256(CurrentInstructions), InstructionsLengthDelta = strlen(CurrentInstructions) - strlen(PreviousInstructions) I deliberately chose to expose hashes and a length delta rather than returning both instruction bodies in plaintext. This confirms that a change occurred without unnecessarily spreading potentially sensitive prompts through query results, exports, or screenshots. Useful investigation questions include: Was the change associated with an approved development or release process? Did the agent remain published while the instructions changed? Were guardrails, declared tools, permissions, or sharing settings modified around the same time? Do audit records identify an expected actor and change path? The query maps well to an integrity-focused investigation. Its MITRE ATT&CK mapping is T1565.001 (Stored Data Manipulation), but the result is still a hunting lead rather than proof of malicious manipulation. https://github.com/Azure/Azure-Sentinel/blob/master/Hunting%20Queries/AI%20Agents/AgentsInfoInstructionsChangedOnPublishedAgent.yaml Scenario 2: A newly observed MCP server Model Context Protocol servers can extend an agent with external tools, data sources, or actions. From a defender's perspective, the important transition is not simply that an MCP server exists. It is that a server name appears in the current configuration but was absent from the baseline. The query expands the dynamic McpServers array and builds a set of server names for each agent: let CurrentMcp = CurrentRaw | mv-expand Mcp = McpServers | extend McpName = tostring(Mcp.name) | where isnotempty(McpName) | summarize CurrentMcpServers = make_set(McpName) by AgentI It performs the same normalization for the baseline, then calculates the difference: | extend AddedMcpServers = set_difference(CurrentMcpServers, BaselineMcpServers) | where array_length(AddedMcpServers) > 0 Using set_difference() avoids raising a result merely because the order of array elements changed. The hunt reports only MCP server names present in the current set and absent from the previous set. An analyst should validate more than the displayed name: Is the MCP integration part of the approved inventory? What endpoint, authentication method, and permissions are associated with it? Which tools or data can the server expose to the agent? Was the integration introduced through an expected deployment path? Did ownership, instructions, or sharing change in the same period? I did not assign an ATT&CK technique to this query. Adding an MCP server does not, by itself, prove command execution, persistence, or a specific attacker behavior. Avoiding an overly broad mapping keeps the signal honest. https://github.com/Azure/Azure-Sentinel/blob/master/Hunting%20Queries/AI%20Agents/AgentsInfoNewlyObservedMcpServer.yaml Scenario 3: An owner added to an MCP-enabled agent Ownership is a control-plane relationship. A newly added owner may be able to modify an agent's configuration, instructions, integrations, or publication state. The risk becomes more interesting when the agent already has MCP servers configured. The hunt first limits the current state to MCP-enabled agents: | where array_length(coalesce(McpServers, dynamic([]))) > 0 | project AgentId, Timestamp, Name, Platform, CreatedDateTime, CurrentOwners = coalesce(Owners, dynamic([])), McpServers It then compares the owner arrays as sets: | extend AddedOwners = set_difference(CurrentOwners, PreviousOwners) | where array_length(AddedOwners) > 0 | mv-expand AddedOwnerId = AddedOwners to typeof(string) Expanding AddedOwners produces one row per newly observed owner. This is more useful than returning one opaque dynamic array because every added identity can be enriched, mapped, and investigated independently. I kept the raw object identifier in the result even when identity enrichment fails: | extend AddedOwnerUpn = AccountUpn, UnresolvedAddedOwnerId = iff(isempty(AccountUpn), AddedOwnerId, "") That fallback matters. A missing UPN should not hide the underlying ownership change. Investigation should establish: Is the added owner an expected person, service identity, or administrative group? Does the identity's role and business function justify control of this agent? Was the owner added before other configuration changes? Does the identity appear in related sign-in, audit, or privileged-access activity? Should ownership be removed while the change is reviewed? This query maps to T1098 (Account Manipulation) under Persistence and Privilege Escalation. As with the instruction-change hunt, the mapping frames an investigation hypothesis; it does not label every ownership change as malicious. https://github.com/Azure/Azure-Sentinel/blob/master/Hunting%20Queries/AI%20Agents/AgentsInfoOwnerAddedToMcpAgent.yaml Scenario 4: Sharing expanded to the entire organization An agent can move from a limited audience to organization-wide availability without changing its underlying tools or instructions. That transition can materially increase exposure, especially when the agent has MCP integrations or declared tools. The hunt treats "*" in SharedWith as the organization-wide state. The current snapshot must contain it, while the baseline must not: // Current state | where set_has_element(coalesce(SharedWith, dynamic([])), "*") // Baseline state | where not(set_has_element(coalesce(SharedWith, dynamic([])), "*")) The result also counts MCP servers and declared tools: | extend McpServerCount = array_length(coalesce(McpServers, dynamic([]))), DeclaredToolCount = array_length(coalesce(DeclaredTools, dynamic([]))) | extend HasElevatedCapabilities = McpServerCount > 0 or DeclaredToolCount > 0 | sort by HasElevatedCapabilities desc, Timestamp desc I use HasElevatedCapabilities as a prioritization field, not a verdict. It brings agents with connected capabilities to the top of the result set so analysts can review the potentially larger blast radius first. Questions for triage include: Was organization-wide publication explicitly approved? Is the agent intended for every user, or was a group-based scope expected? What data sources, tools, and MCP servers can organization-wide users reach through it? Do the instructions contain assumptions that were safe only for a restricted audience? Were access reviews or user-acceptance tests completed before the expansion? No ATT&CK mapping is assigned because a broader sharing scope is a security-relevant exposure change, but not a sufficiently precise adversary technique on its own. https://github.com/Azure/Azure-Sentinel/blob/master/Hunting%20Queries/AI%20Agents/AgentsInfoSharingExpandedToOrgWide.yaml Resolving owners without making the hunt schema-fragile The Owners field contains identifiers. Human-readable identity context makes results easier to triage, and entity mappings make those identities more useful in Sentinel investigations. I built a small, materialized IdentityInfo lookup that is shared by the four hunts: let IdentityIdtoUPN = materialize( IdentityInfo | extend ResolvedAccountUpn = tostring( column_ifexists("AccountUpn", column_ifexists("AccountUPN", ""))), IdentityTimestamp = todatetime( column_ifexists("Timestamp", column_ifexists("TimeGenerated", datetime(null)))) | where IdentityTimestamp >= ago(lookback) | where isnotempty(AccountObjectId) and isnotempty(ResolvedAccountUpn) | summarize arg_max(IdentityTimestamp, ResolvedAccountUpn) by AccountObjectId | project AccountObjectId = tostring(AccountObjectId), AccountUpn = ResolvedAccountUpn); There are three design choices worth noting: column_ifexists() accommodates observed IdentityInfo naming variants without maintaining separate query versions. The lookup is bounded by the same lookback period instead of scanning unbounded identity history. arg_max() keeps the latest usable identity record for each object ID. After enrichment, the queries map the account using the UPN components and the Entra object ID: entityMappings: - entityType: Account fieldMappings: - identifier: Name columnName: OwnerAccountName - identifier: UPNSuffix columnName: OwnerAccountUPNSuffix - identifier: AadUserId columnName: OwnerId The strong AadUserId identifier remains valuable even when display information changes. Microsoft Sentinel can use mapped entities in bookmarks and investigation experiences, so mapping the changed owner is more than cosmetic enrichment. Turning a result into an investigation These queries intentionally stop at the configuration transition. AgentsInfo tells us that two snapshots differ; it does not necessarily tell us who performed the change, through which interface, or whether the action was authorized. A practical investigation workflow is: Confirm that the two snapshots represent the expected agent and time period. Review the exact changed property and the agent's current capabilities. Identify the owner or newly added owner through IdentityInfo and Entra ID context. Correlate the transition with the relevant audit source for actor attribution. Check for related changes to permissions, tools, data sources, publication state, and sharing. Validate the change against an approved request, release, or ownership process. Restrict, unpublish, or revert the agent if the exposure cannot be justified. Expected changes can still be useful findings. Repeated legitimate results may reveal that a deployment process lacks a stable change window, that ownership is managed through noisy automation, or that the hunt's timing needs to be aligned with release activity. Tuning the hunts for your environment Before operational use, consider the following adjustments: Run cadence: Execute within the two-day current window. A daily cadence provides overlap without blending current and baseline periods. Lookback: Increase the 14-day lookback only if snapshot history and query cost support it. A longer lookback does not compensate for missing the current window. Known change windows: Add watchlists or environment-specific suppression logic for well-controlled automated deployments, while retaining enough context to audit the change. Agent scope: Filter by platform, business unit, agent naming convention, or owner if different teams require separate triage queues. Risk prioritization: Raise agents with sensitive declared data sources, powerful tools, privileged owners, or broad availability to the top of the result set. Audit correlation: Keep attribution logic separate unless the audit source and join keys are stable in your environment. This makes the configuration-drift hunt reusable while allowing each organization to attach its own control-plane evidence. Test with representative snapshots before treating any hunt as an operational control. In particular, validate array shapes for Owners, McpServers, and SharedWith, confirm the identity fields present in your workspace, and exercise both changed and unchanged states. Using the queries The four YAML definitions have been merged into the Hunting Queries/AI Agents folder of Microsoft's Azure-Sentinel repository. Each file contains the complete KQL, description, entity mappings, and ATT&CK mappings where a precise technique applies. https://github.com/Azure/Azure-Sentinel/blob/master/Hunting%20Queries/AI%20Agents/AgentsInfoInstructionsChangedOnPublishedAgent.yaml https://github.com/Azure/Azure-Sentinel/blob/master/Hunting%20Queries/AI%20Agents/AgentsInfoNewlyObservedMcpServer.yaml https://github.com/Azure/Azure-Sentinel/blob/master/Hunting%20Queries/AI%20Agents/AgentsInfoOwnerAddedToMcpAgent.yaml https://github.com/Azure/Azure-Sentinel/blob/master/Hunting%20Queries/AI%20Agents/AgentsInfoSharingExpandedToOrgWide.yaml The broader pattern is reusable beyond these four scenarios: select a stable current snapshot, select a non-overlapping baseline, normalize dynamic properties into comparable sets, calculate the transition, and enrich only after the drift has been identified. That keeps the core detection explainable and gives the analyst the before-and-after context needed for a defensible investigation. References https://learn.microsoft.com/en-us/azure/azure-monitor/reference/tables/agentsinfo https://learn.microsoft.com/en-us/azure/azure-monitor/reference/queries/agentsinfo https://learn.microsoft.com/en-us/azure/azure-monitor/reference/tables/identityinfo https://learn.microsoft.com/en-us/azure/sentinel/entities-reference https://github.com/Azure/Azure-Sentinel/pull/14702 I authored the four hunting queries discussed in this article and contributed them to Microsoft's Azure-Sentinel repository as https://github.com/Azure/Azure-Sentinel/pull/14702. The complete implementations and review history are publicly available through the links above.1.1KViews1like2CommentsSentinel - Defender XDR KQL Queries Library
Hello all, I’ve been building something over the past few weeks that I think the security community might find useful. https://goxdr.fyi is a searchable KQL query library for Microsoft Sentinel and Defender XDR. The name comes from a nickname my colleagues gave me (GoX) combined with XDR. I also picked up https://goxdr.fyi as a short and easy to remember domain for it. You can check it out here: https://goxdr.fyi The idea came from my own day to day work as someone working in IAM and SOC operations. I constantly find myself writing and refining KQL queries for threat hunting, detection engineering and incident investigation. Over time I realized I had a growing collection of queries that I kept going back to and I thought why not make these available to others? It currently has 117 queries covering identity security, BEC/AiTM detection, NTLM and LDAP attack hunting, OAuth governance, AI/Copilot security, Sentinel alert trending, SOC performance metrics and more. Some of these queries are ones I wrote from scratch based on real scenarios I encountered in production environments. Others are community queries I tested and validated in my own setup. Only the ones I found genuinely useful and that actually worked against real data made it in. Each query comes with a description explaining what it detects and why it matters, along with severity levels, platform tags (Sentinel, XDR or both) and a copy button so you can paste it directly into Advanced Hunting or use it as the basis for an Analytics Rule. The site is open source, hosted on GitHub Pages and licensed under CC BY 4.0. No sign-up, no paywall, no tracking. The source is available. I’ll keep adding queries as new scenarios come up. If there’s enough interest I’m also considering adding Cortex XQL queries for Palo Alto environments. Suggestions, feedback or ideas for new detections are always welcome. Feel free to reach out. Thanks409Views1like0CommentsMicrosoft Sentinel data lake FAQ
Microsoft Sentinel data lake (generally available) is a purpose‑built, cloud‑native security data lake. It centralizes all security data in an open format, serving as the foundation for agentic defense, enhanced security insights, and graph-based enrichment. It offers cost‑effective ingestion, long‑term retention, and advanced analytics. In this blog we offer answers to many of the questions we’ve heard from our customers and partners. General questions What is the Microsoft Sentinel data lake? Microsoft has expanded its industry-leading SIEM solution, Microsoft Sentinel, to include a unified, security data lake, designed to help optimize costs, simplify data management, and accelerate the adoption of AI in security operations. This modern data lake serves as the foundation for the Microsoft Sentinel platform. It has a cloud-native architecture and is purpose-built for security—bringing together all security data for greater visibility, deeper security analysis, contextual awareness and agentic defense. It provides affordable, long-term retention, allowing organizations to maintain robust security while effectively managing budgetary requirements. What are the benefits of Sentinel data lake? Microsoft Sentinel data lake is purpose built for security offering flexible analytics, cost management, and deeper security insights. Sentinel data lake: Centralizes security data delta parquet and open format for easy access. This unified data foundation accelerates threat detection, investigation, and response across hybrid and multi-cloud environments. Enables data federation by allowing customers to access data in external sources like Microsoft Fabric, ADLS and Databricks from the data lake. Federated data appears alongside native Sentinel data, enabling correlated hunting, investigation, and custom graph analysis across a broader digital estate. Offers a disaggregated storage and compute pricing model, allowing customers to store massive volumes of security data at a fraction of the cost compared to traditional SIEM solutions. Allows multiple analytics engines like Kusto, Spark, and ML to run on a single data copy, simplifying management, reducing costs, and supporting deeper security analysis. Integrates with GitHub Copilot and VS Code empowering SOC teams to automate enrichment, anomaly detection, and forensic analysis. Supports AI agents via the MCP server, allowing tools like GitHub Copilot to query and automate security tasks. The MCP Server layer brings intelligence to the data, offering Semantic Search, Query Tools, and Custom Analysis capabilities that make it easier to extract insights and automate workflows. Provides streamlined onboarding, intuitive table management, and scalable multi-tenant support, making it ideal for MSSPs and large enterprises. The Sentinel data lake is designed for security workloads, ensuring that processes from ingestion to analytics meet evolving cybersecurity requirements. Is Microsoft Sentinel SIEM going away? No. Microsoft is expanding Sentinel into an AI powered end-to-end security platform that includes SIEM and new platform capabilities - Security data lake, graph-powered analytics and MCP Server. SIEM remains a core component and will be actively developed and supported. Getting started What are the prerequisites for Sentinel data lake? To get started: Connect your Sentinel workspace to Microsoft Defender prior to onboarding to Sentinel data lake. Once in the Defender experience see data lake onboarding documentation for next steps. Note: Sentinel is moving to the Microsoft Defender portal and the Sentinel Azure portal will be retired by March 31, 2027. I am a Sentinel-only customer, and not a Defender customer. Can I use the Sentinel data lake? Yes. You must connect Sentinel to the Defender experience before onboarding to the Sentinel data lake. Microsoft Sentinel is generally available in the Microsoft Defender portal, with or without Microsoft Defender XDR or an E5 license. If you have created a log analytics workspace, enabled it for Sentinel and have the right Microsoft Entra roles (e.g. Global Administrator + Subscription Owner, Security Administrator + Sentinel Contributor), you can enable Sentinel in the Defender portal. For more details on how to connect Sentinel to Defender review these sources: Microsoft Sentinel in the Microsoft Defender portal In what regions is Sentinel data lake available? For supported regions see: Geographical availability and data residency in Microsoft Sentinel | Azure Docs. Is there an expected release date for Microsoft Sentinel data lake in GCC, GCC-H, and DoD? While the exact date is not yet finalized, we plan to expand Sentinel data lake to the US Government environments. . How will URBAC and Entra RBAC work together to manage the data lake given there is no centralized model? Entra RBAC will provide broad access to the data lake (URBAC maps the right permissions to specific Entra role holders: GA/SA/SO/GR/SR). URBAC will become a centralized pane for configuring non-global delegated access to the data lake. For today, you will use this for the “default data lake” workspace. In the future, this will be enabled for non-default Sentinel workspaces as well – meaning all workspaces in the data lake can be managed here for data lake RBAC requirements. Azure RBAC on the Log Analytics (LA) workspace in the data lake is respected through URBAC as well today. If you already hold a built-in role like log analytics reader, you will be able to run interactive queries over the tables in that workspace. Or, if you hold log analytics contributor, you can read and manage table data. For more details see: Roles and permissions in the Microsoft Sentinel platform | Microsoft Learn Data ingestion and storage How do I ingest data into the Sentinel data lake? To ingest data into the Sentinel data lake, you can use existing Sentinel data connectors or custom connectors to bring data from Microsoft and third-party sources. Data can be ingested into the analytics tier or the data lake tier. Data ingested into the analytics tier is automatically mirrored to the lake (at no additional cost). Alternatively, data that is not needed in the analytics tier can be ingested directly into the data lake. Data retention is configured directly in table management, for both analytics retention and data lake storage. Note: Certain tables do not support data lake-only ingestion via either API or data connector UI. See here for more information: Custom log tables. What is Microsoft’s guidance on when to use analytics tier vs. the data lake tier? Sentinel data lake offers flexible, built-in data tiering (analytics and data lake tiers) to effectively meet diverse business use cases and achieve cost optimization goals. Analytics tier: Is ideal for high-performance, real-time, end-to-end detections, enrichments, investigation and interactive dashboards. Typically, high-fidelity data from EDRs, email gateways, identity, SaaS and cloud logs, threat intelligence (TI) should be ingested into the analytics tier. Data in the analytics tier is best monitored proactively with scheduled alerts and scheduled analytics to enable security detections Data in this tier is retained at no cost for up to 90 days by default, extendable to 2 years. A copy of the data in this tier is automatically available in the data lake tier at no extra cost, ensuring a unified copy of security data for both tiers. Data lake tier: Is designed for cost-effective, long-term storage. High-volume logs like NetFlow logs, TLS/SSL certificate logs, firewall logs and proxy logs are best suited for data lake tier. Customers can use these logs for historical analysis, compliance and auditing, incident response (IR), forensics over historical data, build tenant baselines, TI matching and then promote resulting insights into the analytics tier. Customers can run full Kusto queries, Spark Notebooks and scheduled jobs over a single copy of their data in the data lake. Customers can also search, enrich and promote data from the data lake tier to the analytics tier for full analytics. For more details see documentation. What does it mean that a copy of all new analytics tier data will be available in the data lake? When Sentinel data lake is enabled, a copy of all new data ingested into the analytics tier is automatically duplicated into the data lake tier. This means customers don’t need to manually configure or manage this process, every new log or telemetry added to the analytics tier becomes instantly available in the data lake. This allows security teams to run advanced analytics, historical investigations, and machine learning models on a single, unified copy of data in the lake, while still using the analytics tier for real-time SOC workflows. It’s a seamless way to support both operational and long-term use cases—without duplicating effort or cost. What is the guidance for customers using data federation capability in Sentinel data lake? Starting April 1, 2026, federate data from Microsoft Fabric, ADLS, and Azure Databricks into Sentinel data lake. Use data federation when data is exploratory, infrequently accessed, or must remain at source due to governance, compliance, sovereignty, or contractual requirements. Ingest data directly into Sentinel to unlock full SIEM capabilities, always-on detections, advanced automation, and AI‑driven defense at scale. This approach lets security teams start where their data already lives — preserving governance, then progressively ingest data into Sentinel for full security value. Is there any cost for retention in the analytics tier? Analytics ingestion includes 90 days of interactive retention, at no additional cost. Simply set analytics retention to 90 days or less. Analytics retention beyond 90 days will incur a retention cost. Data can be retained longer within the data lake by using the “total retention” setting. This allows you to extend retention within the data lake for up to 12 years. While data is retained within the analytics tier, there is no charge for the mirrored data within the lake. Retaining data in the lake beyond the analytics retention period incurs additional storage costs. See documentation for more details: Manage data tiers and retention in Microsoft Sentinel | Microsoft Learn What is the guidance for Microsoft Sentinel Basic and Auxiliary Logs customers? If you previously enabled Basic or Auxiliary Logs plan in Sentinel: You can view Basic Logs in the Defender portal but manage it from the Log Analytics workspace. To manage it in the Defender portal, you must change the plan from Basic to Analytics. Once the table is transitioned to the analytics tier, if desired, it can then be transitioned to the data lake. Existing Auxiliary Log tables will be available in the data lake tier for use once the Sentinel data lake is enabled. Billing for these tables will automatically switch to the Sentinel data lake meters. Microsoft Sentinel customers are recommended to start planning their data management strategy with the data lake. While Basic and Auxiliary Logs are still available, they are not being enhanced further. Sentinel data lake offers more capabilities at a lower price point. Please plan on onboarding your security data to the Sentinel data lake. Azure Monitor customers can continue to use Basic and Auxiliary Logs for observability scenarios. What happens to customers that already have Archive logs enabled? If a customer has already configured tables for Archive retention, existing retention settings will not change and will be automatically inherited by the Sentinel data lake. All data, including existing data in archive retention will be billed using the data lake storage meter, benefiting from 6x data compression. However, the data itself will not move. Existing data in archive will continue to be accessible through Sentinel search and restore experiences: o Data will not be backfilled into the data lake. o Data will be billed using the data lake storage meter. New data ingested after enabling the data lake: o Will be automatically mirrored to the data lake and accessible through data lake explorer. o Data will be billed using the data lake storage meter. Example: If a customer has 12 months of total retention enabled on a table, 2 months after enabling ingestion into the Sentinel data lake, the customer will still have access to 10 months of archived data (through Sentinel search and restore experiences), but access to only 2 months of data in the data lake (since the data lake was enabled). Key considerations for customers that currently have Archive logs enabled: The existing archive will remain, with new data ingested into the data lake going forward; previously stored archive data will not be backfilled into the lake. Archive logs will continue to be accessible via the Search and Restore tab under Sentinel. If analytics and data lake mode are enabled on table, which is the default setting for analytics tables when Sentinel data lake is enabled, all new data will be ingested into the Sentinel data lake. There will only be one storage meter (which is data lake storage) going forward. Archive will continue to be accessible via Search and Restore. If Sentinel data lake-only mode is enabled on table, new data will be ingested only into the data lake; any data that’s not already in the Sentinel data lake won’t be migrated/backfilled. Only data that was previously ingested under the archive plan will be accessible via Search and Restore. What is the guidance for customers using Azure Data Explorer (ADX) alongside Microsoft Sentinel? Some customers might have set up ADX cluster for their DIY lake setup. Customers can choose to continue using that setup and gradually migrate to Sentinel data lake for new data that they want to manage. The lake explorer will support federation with ADX to enable the customers to migrate gradually and simplify their deployment. What happens to the Defender XDR data after enabling Sentinel data lake? By default, Defender XDR tables are available for querying in advanced hunting, with 30 days of analytics tier retention included with the XDR license. To retain data beyond this period, an explicit change to the retention setting is required, either by extending the analytics tier retention or the total retention period. You can extend the retention period of supported Defender XDR tables beyond 30 days and ingest the data into the analytics tier. For more information see Manage XDR data in Microsoft Sentinel. You can also ingest XDR data directly into the data lake tier. See here for more information. A list of XDR advanced hunting tables supported by Sentinel are documented here: Connect Microsoft Defender XDR data to Microsoft Sentinel | Microsoft Learn. KQL queries and jobs Is KQL and Notebook supported over the Sentinel data lake? Yes, via the data lake KQL query experience along with a fully managed Notebook experience which enables spark-based big data analytics over a single copy of all your security data. Customers can run queries across any time range of data in their Sentinel data lake. In the future, this will be extended to enable SQL query over lake as well. Note: Triggering a KQL job directly via an API or Logic App is not yet supported but is on the roadmap. Why are there two different places to run KQL queries in Sentinel experience? Advanced hunting queries both XDR and analytics tables, with compute cost included. Data lake explorer only queries data in the lake and incurs a separate compute cost. Consolidating advanced hunting and KQL explorer user interfaces is on the roadmap. This will provide security analysts a unified query experience across both analytics and data lake tiers. Where is the output from KQL jobs stored? KQL jobs are written into existing or new custom tables in the analytics tier. Is it possible to run KQL queries on multiple data lake tables? Yes, you can run KQL interactive queries and jobs using operators like join or union. Can KQL queries (either interactive or via KQL jobs) join data across multiple workspaces? Security teams can run multi-workspace KQL queries for broader threat correlation Pricing and billing How does a customer pay for Sentinel data lake? Billing is automatically enabled at the time of onboarding based on Azure Subscription and Resource Group selections. Customers are then charged based on the volume of data ingested, retained, and analyzed (e.g. KQL Queries and Jobs). See Sentinel pricing page for more details. 2. What are the pricing components for Sentinel data lake? Sentinel data lake offers a flexible pricing model designed to optimize security coverage and costs. At a high level, pricing is based on the volume of data ingested/processed, the volume of data retained, and the volume of data processed. For specific meter definitions, see documentation. 3. How does the business model for Sentinel SIEM change with the introduction of the data lake? There is no change to existing Sentinel analytics tier ingestion business model. Sentinel data lake has separate meters for ingestion, storage and analytics. 4. What happens to the existing Sentinel SIEM and related Azure Monitor billing meters when a customer onboards to Sentinel data lake? When a customer onboards to the Sentinel data lake, nothing changes with analytic ingestion or retention. Customers using data archive and Auxiliary Logs will automatically transition to the new data lake meters. How does data lake storage affect cost efficiency for high volume data retention? Sentinel data lake offers cost-effective, long-term storage with uniform data compression of 6:1 across all data sources, applicable only to data lake storage. Example: For 600GB of data stored, you are only billed for 100GB compressed data. This approach allows organizations to retain greater volumes of security data over extended periods cost-effectively, thereby reducing security risks without compromising their overall security posture. here How “Data Processing” billed? To support the ingestion and standardization of diverse data sources, the Data Processing feature applies a $0.10 per GB (US East) charge for all data ingested into the data lake. This feature enables a broad array of transformations like redaction, splitting, filtering and normalization. The data processing charge is applied per GB of uncompressed data Note: For regional pricing, please refer to the “Data processing” meter within the Microsoft Sentinel Pricing official documentation. Does “Data processing” meter apply to analytics tier data mirrored in the data lake? No. Data processing charge will not be applied to mirrored data. Data mirrored from the analytic tier is not subject to either data ingestion or processing charges. How is retention billed for tables that use data lake-only ingestion & retention? Sentinel data lake decouples ingestion, storage, and analytics meters. Customers have the flexibility to pay based on how data is retained and used. For tables that use data lake‑only ingestion, there is no included free retention—unlike the analytics tier, which includes 90 days of analytics retention. Retention charges begin immediately once data is stored in the data lake. Data lake storage billing is based on compressed data size rather than raw ingested volume, which significantly reduces storage costs and delivers lower overall retention spend for customers. Does data federation incur charges? Data federation does not generate any ingestion or storage fees in Sentinel data lake. Customers are billed only when they run analytics or queries on federated data, with charges based on Sentinel data lake compute and analytics meters. This means customers pay solely for actual data usage, not mere connectivity. How do I understand Sentinel data lake costs? Sentinel data lake costs driven by three primary factors: how much data is ingested, how long that data is retained, and how the data is used. Customers can flexibly choose to ingest data into the analytics tier or data lake tier, and these architectural choices directly impact cost. For example, data can be ingested into the analytics tier—where commitment tiers help optimize costs for high data volumes—or ingested data directly into the Sentinel data lake for lower‑cost ingestion, storage, and on‑demand analysis. Customers are encouraged to work with their Microsoft account team to obtain an accurate cost estimate tailored to their environment. See Sentinel pricing page to understand Sentinel pricing. How do I manage Sentinel data lake costs? Built-in cost management experiences help customers with cost predictability, billing transparency, and operational efficiency. Reports provide customers with insights into usage trends over time, enabling them to identify cost drivers and optimize data retention and processing strategies. Set usage-based alerts on specific meters to monitor and control costs. For example, receive alerts when query or notebook usage passes set limits, helping avoid unexpected expenses and manage budgets. See our Sentinel cost management documentation to learn more. If I’m an Auxiliary Logs customer, how will onboarding to the Sentinel data lake affect my billing? Once a workspace is onboarded to Sentinel data lake, all Auxiliary Logs meters will be replaced by new data lake meters. Do we charge for data lake ingestion and storage for graph experiences? Microsoft Sentinel graph-based experiences are included as part of the existing Defender and Purview licenses. However, Sentinel graph requires Sentinel data lake and specific data sources to build the underlying graph. Enabling these data sources will incur ingestion and data lake storage costs. Note: For Sentinel SIEM customers, most required data sources are free for analytics ingestion. Non-entitled sources such as Microsoft Entra ID logs will incur ingestion and data lake storage costs. How is Entra asset data and ARG data billed? Data lake ingestion charges of $0.05 per GB (US EAST) will apply to Entra asset data and ARG data. Note: This was previously not billed during public preview and is billed since data lake GA. To learn more, see: https://learn.microsoft.com/azure/sentinel/datalake/enable-data-connectors When a customer activates Sentinel data lake, what happens to tables with archive logs enabled? To simplify billing, once the data lake is enabled, all archive data will be billed using the data lake storage meter. This provides consistent long-term retention billing and includes automatic 6x data compression. For most customers, this change results in lower long‑term retention costs. However, customers who previously had discounted archive retention pricing will not automatically receive the same discounts on the new data lake storage meters. In these cases, customers should engage their Microsoft account team to review pricing implications before enabling the Sentinel data lake. Thank you Thank you to our customers and partners for your continued trust and collaboration. Your feedback drives our innovation, and we’re excited to keep evolving Microsoft Sentinel to meet your security needs. If you have any questions, please don’t hesitate to reach out—we’re here to support you every step of the way. Learn more: Get started with Sentinel data lake today: https://aka.ms/Get_started/Sentinel_datalake Microsoft Sentinel AI-ready platform: https://aka.ms/Microsoft_Sentinel Sentinel data lake videos: https://aka.ms/Sentineldatalake_videos Latest innovations and updates on Sentinel: https://aka.ms/msftsentinelblog Sentinel pricing page: https://aka.ms/MicrosoftSentinel_Pricing8.2KViews1like9Comments