cybersecurity
3 Topics
Did AI Bring Microsoft Down?
Question for Microsoft Engineering: Was Agentic AI Involved in the November 12–13, 2026 Microsoft 365 Outage? The recent widespread Microsoft 365 outage appears to have involved server health-check failures, infrastructure configuration issues and cascading service disruptions. I have a question that I believe deserves a clear technical answer from Microsoft's engineering team. Given the increasing deployment of AI-assisted and agentic systems across cloud infrastructure, automated monitoring, configuration management and incident response: Can Microsoft confirm whether any autonomous AI agent initiated, authorised or materially contributed to the configuration changes preceding this incident? Were AI-driven systems involved in the server health-check mechanisms that resulted in multiple servers being taken offline? Did any autonomous AI-driven recovery or remediation processes contribute to the cascading failure or complicate Microsoft's recovery efforts? Does Microsoft maintain sufficiently detailed audit trails to distinguish between human-authorised changes, conventional automation and autonomous AI-initiated actions? I am not suggesting that AI was necessarily responsible. However, given the growing operational autonomy of AI systems, I believe this is a legitimate question that deserves a transparent answer. Can Microsoft Engineering explicitly confirm whether agentic AI was involved at any stage in the incident, including its initiation, escalation or recovery? I would welcome a technically detailed response rather than a general statement that the incident resulted from a configuration error.
Microsoft Purview | Share block at external users
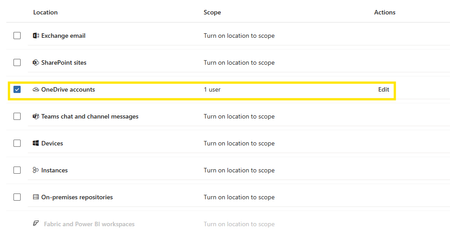
Hello community. I have an issue with Microsoft Purview DLP policies. I am trying to create a policy that prevents documents from being shared through OneDrive with external users, while allowing certain exceptions. However, when I select the option "Block Access to external domains and users" and assign a specific email address to be blocked, it does not work. The configured email address is not being blocked. I was reviewing this with Copilot, and it mentioned that if the external user you are sharing with already exists in Entra ID, the tenant may treat the user differently (not necessarily as an external user). My external user exists in Entra ID as a Guest account. The external user is registered as follows: Displayname: User Name Userprincipalname: user.name_external.domain#EXT#@company.onmicrosoft.com User Type: Guest Has anyone else experienced this issue? I am sharing evidence of the policy configuration.1.3KViews0likes7CommentsAsk Microsoft Anything: Why Cybersecurity Needs a New Security Stack for the AI Era with David Weston
David Weston leads Agentic Security at Microsoft, where he and his team build the AI models, autonomous agents, and evaluation systems redefining how defenders operate. At Microsoft since the Windows 7 era, he has worked across exploit mitigation design, malware analysis, APT research, and led security engineering for Windows, Xbox, Azure OS, and Microsoft's Offensive Security Research & Engineering group. His current work is leading teams training frontier security models, agentic security systems for defenders, and pushing AI-driven vulnerability discovery through Microsoft's Multi-Model Agentic Scanning Harness (MDASH). A longtime member of the research community and former CISA technical advisor, David is a regular presenter at BlueHat, Black Hat, and DEF CON. Key areas Dave and his team can discuss: The vision behind Project Perception How AI is changing the economics of cyber offense and defense Lessons learned from building MDASH and Microsoft's AI security initiatives Security-first AI development and deployment What's next for defenders as agentic systems become mainstream This will be a TEXT-BASED AMA, so ask your questions in the comment section down below and David and team will be answering via comment replies during the live hour!5.4KViews9likes16Comments