azure sql security
199 Topics🔐 Public Preview: Backup Immutability for Azure SQL Database LTR Backups
The Ransomware Threat Landscape Ransomware attacks have become one of the most disruptive cybersecurity threats in recent years. These attacks typically follow a destructive pattern: Attackers gain unauthorized access to systems. They encrypt or delete critical data. They demand ransom in exchange for restoring access. Organizations without secure, tamper-proof backups are often left with no choice but to pay the ransom or suffer significant data loss. This is where immutable backups play a critical role in defense. 🛡️ What Is Backup Immutability? Backup immutability ensures that once a backup is created, it cannot be modified or deleted for a specified period. This guarantees: Protection against accidental or malicious deletion. Assurance that backups remain intact and trustworthy. Compliance with regulatory requirements for data retention and integrity. 🚀 Azure SQL Database LTR Backup Immutability (Public Preview) Microsoft has introduced backup immutability for Long-Term Retention (LTR) backups in Azure SQL Database, now available in public preview. This feature allows organizations to apply Write Once, Read Many (WORM) policies to LTR backups stored in Azure Blob Storage. Key Features: Time-based immutability: Locks backups for a defined duration (e.g., 30 days). Legal hold immutability: Retains backups indefinitely until a legal hold is explicitly removed. Tamper-proof storage: Backups cannot be deleted or altered, even by administrators. This ensures that LTR backups remain secure and recoverable, even in the event of a ransomware attack. 📜 Regulatory Requirements for Backup Immutability Many global regulations mandate immutable storage to ensure data integrity and auditability. Here are some key examples: Region Regulation Requirement USA SEC Rule 17a-4(f) Requires broker-dealers to store records in WORM-compliant systems. FINRA Mandates financial records be preserved in a non-rewriteable, non-erasable format. HIPAA Requires healthcare organizations to ensure the integrity and availability of electronic health records. EU GDPR Emphasizes data integrity and the ability to demonstrate compliance through audit trails. Global ISO 27001, PCI-DSS Require secure, tamper-proof data retention for audit and compliance purposes. Azure’s immutable storage capabilities help organizations meet these requirements by ensuring that backup data remains unchanged and verifiable. 🕒 Time-Based vs. Legal Hold Immutability ⏱️ Time-Based Immutability Locks data for a predefined period (e.g., 30 days). Ideal for routine compliance and operational recovery. Automatically expires after the retention period. 📌 Legal Hold Immutability Retains data indefinitely until the hold is explicitly removed. Used in legal investigations, audits, or regulatory inquiries. Overrides time-based policies to ensure data preservation. Both types can be applied to Azure SQL LTR backups, offering flexibility and compliance across different scenarios. 🧩 How Immutability Protects Against Ransomware Immutable backups are a critical component of a layered defense strategy: Tamper-proof: Even if attackers gain access, they cannot delete or encrypt immutable backups. Reliable recovery: Organizations can restore clean data from immutable backups without paying ransom. Compliance-ready: Meets regulatory requirements for data retention and integrity. By enabling immutability for Azure SQL LTR backups, organizations can significantly reduce the risk of data loss and ensure business continuity. ✅ Final Thoughts The public preview of backup immutability for Azure SQL Database LTR backups is a major step forward in ransomware resilience and regulatory compliance. With support for both time-based and legal hold immutability, Azure empowers organizations to: Protect critical data from tampering or deletion. Meet global compliance standards. Recover quickly and confidently from cyberattacks. Immutability is not just a feature—it’s a foundational pillar of modern data protection. Documentation is available at - Backup Immutability for Long-Term Retention Backups - Azure SQL Database | Microsoft Learn882Views4likes2CommentsStrengthening Ransomware Resilience with Immutable Backups in Azure SQL DB and Azure SQL MI
Ransomware attacks are becoming increasingly sophisticated. Attackers no longer focus only on encrypting or stealing production data. They also target backups, knowing that eliminating an organization's recovery options can turn a security incident into a prolonged business disruption. Imagine discovering that your database has been compromised, only to find that the backups you were counting on have also been deleted. Even with a comprehensive backup strategy, recovery becomes significantly more challenging when attackers can tamper with the very data needed to restore business operations. That's why backup immutability matters. We're continuing to strengthen data protection in Azure SQL Database and Azure SQL Managed Instance with a consistent set of backup immutability capabilities spanning both point-in-time restore (PITR) and long-term retention (LTR) backups. Whether you're protecting recent transactions, maintaining historical backups for years, or preserving data for regulatory requirements, Azure SQL provides multiple layers of protection to help ensure your recovery points remain available when you need them most. What makes immutable backups different? Traditional backup retention policies define how long backups should be kept. But retention alone doesn't necessarily prevent someone with sufficient privileges from deleting backups before they expire. Backup immutability adds another layer of defense. With immutability, protected backups cannot be modified, overwritten, or deleted during their immutability period, even by administrators with elevated privileges. This is particularly valuable when attackers gain access to privileged accounts. While compromised credentials may allow attackers to disrupt production environments, immutable backups help prevent them from destroying protected recovery points. Think of it as adding a safety barrier around your backups, one that helps preserve your ability to recover even when other defenses have been compromised. 1. Built-in protection for your recent backups, automatically One of the simplest ways to improve security is to make protection automatic. Azure SQL Database and Azure SQL Managed Instance now provide immutable protection for up to the most recent seven days of PITR backups by default. The best part? There's nothing you need to do to get started. No additional configuration. No separate storage accounts to manage. No immutability policies to create. No changes to existing backup and restore workflows. No additional charge for the default immutability protection. This capability is integrated directly into the Azure SQL managed backup service. For customers, that means an additional layer of protection is already working behind the scenes, helping safeguard recent recovery points against accidental deletion, malicious activity, and compromised administrative credentials. Whether you're running a business-critical application or a smaller operational database, this built-in protection provides a stronger starting point for your recovery strategy. 2. Need longer protection? Lock immutability to your PITR retention period Seven days of automatic protection is a great starting point, but every organization has different recovery requirements. Some businesses need additional time to detect security incidents, investigate suspicious activity, and determine when their data was last known to be healthy. For these scenarios, Azure SQL offers the option to extend immutable protection across the entire configured PITR backup retention period, up to 35 days where supported. For example, if your database is configured to retain 35 days of PITR backups, you can lock immutability to that retention period, protecting those recovery points against deletion or modification. Once enabled, the lock is permanent. The configured retention period can be increased, but it cannot be shortened. This provides an important safeguard against attempts to weaken backup protection, including those made using compromised administrative credentials. With this capability, organizations can align their backup protection with their recovery requirements, rather than relying solely on the default protection window. The experience is consistent across Azure SQL Database and Azure SQL Managed Instance, making it easier to establish a common data protection strategy across your Azure SQL environment. 3. Protect your long-term backups for years, not just days Recovering from a recent incident is only one part of a comprehensive data protection strategy. Many organizations also need to preserve historical backups for business continuity, regulatory compliance, internal governance, or audit requirements. Azure SQL long-term retention (LTR) supports retaining backups for up to 10 years. With LTR backup immutability, customers can go beyond simply retaining those backups and protect them against unauthorized modification or deletion. Time-based immutability allows organizations to specify how long backups must remain protected. Once immutability is enabled and locked, affected backups cannot be deleted until their retention period expires, even if an administrator later changes or removes the retention policy. Consider a financial services organization that needs to preserve database backups for seven years. By configuring locked time-based immutability, the organization can help ensure those backups remain protected throughout the required retention period. The same approach is valuable for healthcare organizations, enterprises with strict governance requirements, and businesses seeking additional safeguards against ransomware. With a consistent LTR immutability experience across Azure SQL Database and Azure SQL Managed Instance, customers can apply the same protection principles regardless of which service hosts their databases. 4. Preserve critical backups with legal holds Not every data preservation requirement has a predictable end date. An organization may need to retain a specific backup while responding to an audit, conducting an internal investigation, or addressing a legal matter. In these situations, a fixed retention period may not be sufficient. Azure SQL LTR backup immutability also supports legal holds, allowing customers to protect specific existing backups until the hold is explicitly removed. For example, if an organization needs to preserve a database backup associated with an ongoing investigation, it can apply a legal hold to prevent that backup from being deleted while the investigation continues. Legal holds can coexist with time-based immutability, providing flexibility for organizations that need both predictable retention policies and event-driven preservation requirements. This makes immutable backups valuable not only for ransomware resilience, but also for meeting evolving business and governance needs. 5. Consistent protection across Azure SQL Database and Azure SQL Managed Instance For organizations operating both Azure SQL Database and Azure SQL Managed Instance, consistency matters. Security and compliance teams shouldn't have to build entirely different backup protection strategies depending on where a database runs. With a consistent immutability experience across both services, customers can adopt a common approach to protecting recent and historical backups. Here's how the capabilities work together: Capability Customer benefit Default PITR immutability Automatic protection for up to seven days of recent backups Locked PITR immutability Extended protection aligned with configured PITR retention, up to 35 days Time-based LTR immutability Protect historical backups for their configured retention period, up to 10 years LTR legal holds Preserve selected backups until the hold is explicitly removed Together, these capabilities provide flexibility to address different recovery and retention requirements, from recovering a database to a recent point in time to preserving historical backups for years. And because the protection is integrated into Azure SQL's managed backup experience, customers don't need to build or maintain separate immutable backup storage infrastructure. 6. Building a stronger defense against ransomware Let's revisit a common ransomware scenario. An attacker gains access to a privileged account and attempts to disrupt business operations by modifying production data and deleting available backups. Without immutability, the attacker may be able to eliminate critical recovery options. With immutable backups, the story changes. Recent recovery points are protected: Default PITR immutability helps preserve backups from the most recent seven days. Extended recovery history can be safeguarded: Locked PITR immutability can protect a longer recovery window, giving organizations more options when investigating an incident. Historical backups remain protected: Locked LTR immutability helps prevent attackers from deleting backups that organizations need to retain for months or years. Critical records can be preserved: Legal holds provide additional protection for specific backups that must remain available during investigations or audits. While backup immutability doesn't prevent ransomware attacks or guarantee that every restore point is free from compromise, it makes it significantly harder for attackers to eliminate protected backups. That distinction is important. A strong ransomware recovery strategy isn't just about having backups. It's about being able to trust that your backups will still be there when you need them. Immutable backups complement other security and resilience practices, including identity protection, least-privilege access, monitoring, appropriate backup retention, and regular recovery testing. 7. Get started with immutable backups in Azure SQL Getting started is straightforward. If you're using a supported Azure SQL Database or Azure SQL Managed Instance database, you already benefit from default PITR backup immutability for up to seven days. From there, consider your organization's recovery and compliance needs: Review your PITR retention settings. Determine whether the default protection window meets your recovery objectives or whether you need a longer immutable retention period. Consider locked PITR immutability. For databases requiring extended protection, align immutability with your configured PITR retention. Evaluate your long-term backup requirements. Configure LTR immutability for backups that must remain protected for extended periods. Use legal holds when needed. Preserve specific historical backups for audits, investigations, or legal requirements. Test your recovery procedures. Validate that your organization can restore the right data when an incident occurs. Before applying permanent retention locks, carefully evaluate your requirements, because locked protection cannot be removed early. Also remember that backup immutability protects backups, not the database resource itself, so resource deletion protection and recovery planning remain important. Protecting your data. Preserving your ability to recover. As cyber threats continue to evolve, organizations need confidence not only that their data is protected, but also that they can recover when something goes wrong. With backup immutability spanning PITR and LTR backups across Azure SQL Database and Azure SQL Managed Instance, we're making it easier for customers to build stronger, more consistent data protection strategies. From automatic protection for recent backups to long-term immutable retention and legal holds, these capabilities help organizations safeguard critical recovery points, reduce ransomware-related risks, and strengthen their overall resilience. Because when the unexpected happens, the most important backup is the one you can still recover from. Learn more: PITR backup immutability for both Azure SQL DB and Azure SQL MI - Automatic backup immutability for Azure SQL Database and Azure SQL Managed Instance - Azure SQL | Microsoft Learn Azure SQL DB LTR backup immutability - Backup Immutability for Long-Term Retention Backups - Azure SQL Database | Microsoft Learn Azure SQL MI LTR backup immutability - LTR backup immutability - Azure SQL Managed Instance | Microsoft Learn My colleague SudhanshuKhera authored a comprehensive ransomware recovery plan for Azure SQL DB and Azure SQL MI - Overview: Recover Azure SQL Database and Azure SQL Managed Instance from a ransomware attack - Azure SQL Database | Microsoft Learn191Views0likes1CommentDatabase Hub in Microsoft Fabric is generally available: your entire database estate in one place
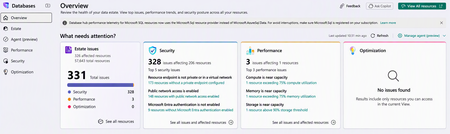
As applications grow, so does the database estate behind them. Many organizations now run hundreds or thousands of databases across cloud, hybrid and multicloud environments. The signals are already there: inventory, health, performance, security, risk and optimization. The hard part is making sense of them, knowing what needs attention and deciding what to do next. Today, we're announcing the general availability of Database Hub in Microsoft Fabric. Database Hub gives you one place to see your whole estate, monitor it at scale and investigate where attention is needed. It covers Azure SQL, Azure Database for PostgreSQL, Azure Cosmos DB, SQL Server and SQL database in Fabric. Everything in this release is built around that idea: one estate, every signal, wherever you work. Get started for free If you're new to Microsoft Fabric, you don't need to set anything up first. Open Database Hub, and you're automatically given a free Fabric license and taken straight to your estate. You only need Fabric capacity to share dashboards, create custom alerts or use Copilot. Generally available today Area What you get Overview A "what needs attention" view across security, performance and optimization, with the top issues and recent signal changes across SQL, PostgreSQL and Cosmos DB Estate inventory A single inventory of supported Azure and Fabric databases, with their issues and suggestions Performance monitoring Near real-time CPU, memory and storage trends, aggregated across the estate and per resource, plus normalized RU and throttled requests for Cosmos DB Security posture Findings such as public network access, missing private endpoints, Microsoft Entra authentication, audit logging and customer-managed keys Investigation The ability to drill from any finding into the affected resource, real-time dashboards and the tools you already use New in general availability: Bulk performance monitoring enablement Monitoring a large estate shouldn't mean configuring it one database at a time. You can now turn on performance monitoring at scale from the Estate view. Select multiple resources and enable performance monitoring data collection for all of them in one step. Start from your inventory. Turn on monitoring in the same place you review your databases, without switching to another portal or tool. Cover more of your estate, faster. Extend monitoring coverage across hundreds of databases without repeating setup for each one. Go from setup to insight. Once data collection is on, monitored resources show up in Performance Monitoring and real-time dashboards. New in general availability: Optimization insights Optimization now sits alongside security and performance in Overview and Estate. It highlights: Resources with a migration assessment ready License model opportunities, such as pay-as-you-go SQL Server instances that aren't reporting usage Now generally available: Real-time dashboards Real-time dashboards for Microsoft SQL, Azure Database for PostgreSQL and Azure Cosmos DB move from preview to general availability. Now generally available: VS Code and SSMS entry points DBAs work in SSMS, and developers work in VS Code. You can now open Database Hub from SSMS and from the Microsoft and MSSQL extensions for VS Code. You land in the same estate view, with the resources you were working on. SSMS VS Code Now generally available: Database Hub CLI skill Ask about estate inventory, health, performance and security posture from GitHub Copilot CLI, VS Code Copilot, Claude Code or Cursor. Get the Database Hub CLI skill from skills-for-fabric, or install it with one command: skills-for-fabric --skill databasehub-cli Then try asking, "How is my database estate doing?" or "Which databases need attention this week?" In preview Public preview: Investigate your estate with Copilot Ask questions about your databases in natural language and get answers grounded in Database Hub data. Explore trends, understand issues and suggestions, and follow up on specific resources. Try prompts such as: "What changed in my databases?" "Which resource should I investigate next?" "Which security findings should I address first?" Public preview: Database Agents Database Agents act as an extra set of eyes on your estate. An agent watches the databases you choose and stays quiet while they're healthy. When something needs your judgment, it raises an issue with supporting evidence and a recommendation. You stay in control: the agent brings the issue to you, and you decide what happens next. Start with the overall finding or select Analyze on a single query to get recommendations for that query. From there, keep investigating with Copilot or go deeper in SSMS. Database Hub is where you see the bigger picture. The database agent alerts you before your users notice. Public preview: Alerts for Azure SQL Database Create alerts from built-in templates or performance charts for one database or many. Alerts can send a Microsoft Teams message or start a Power Automate flow. They're powered by Fabric Activator. Preview: Performance monitoring for SQL Server on Azure VMs Review SQL Server on Azure Virtual Machines in the same Performance Monitoring experience as the rest of your estate. What's next More skills are on the way, including SQL performance monitoring, Cosmos DB performance monitoring and migration skills. Get started today Open Database Hub: https://app.fabric.microsoft.com/workloads/fdh/databaseHub/overview Learn more: https://learn.microsoft.com/en-us/fabric/database/hub Install the Database Hub CLI skill: https://github.com/microsoft/skills-for-fabric/tree/main/skills/databasehub-cli Read more about Database Hub Database Hub in Fabric: Now in Public Preview -Turn Database Signals into Guided Action | Microsoft Community Hub Public Preview: Performance monitoring for Azure SQL in Database Hub | Microsoft Community Hub A Single View of Your PostgreSQL Estate: Database Hub in Public Preview | Microsoft Community Hub Make Estate yours: Focus on the databases and issues you own in Database Hub | Microsoft Community Hub Public Preview: Alerts for Azure SQL Database in Database Hub, powered by Fabric Activator | Microsoft Community Hub Managing security with Database Hub in Fabric: From signals to action | Microsoft Community Hub Database watcher for Azure SQL is retiring: simplify your monitoring with Database Hub | Microsoft Community Hub Ask your database estate a question: Copilot in Database Hub is now in public preview | Microsoft Community Hub435Views3likes2CommentsTake control of transparent data encryption scans: suspend and resume now in preview
Suspend and resume for transparent data encryption (TDE) scans in Azure SQL Database lets you temporarily halt an encryption scan during busy periods and continue it later from the exact point where it stopped, instead of starting over. Why we built it TDE protects your databases, backups, and transaction log files at rest, without any changes to your application. When you turn encryption on or off, the service runs an encryption scan across the database. The scan duration is proportional to the size of the database, and for large databases it can take a long time. While it runs, the scan consumes CPU and I/O, which can affect user workloads during peak hours. Until now, scans were all or nothing: once started, a scan had to complete. What is new Suspend and resume gives database administrators and owners control over the encryption scan: Suspend temporarily halts the encryption scan on the data and log files and releases the resources it was using. Resume restarts the scan from the point of suspension. While a scan is suspended, new or updated data pages continue to be handled according to the direction of the scan. If you were encrypting, new pages are still encrypted. If you were decrypting, new pages are written unencrypted. You can also toggle direction while a scan is suspended. For example, you can start encryption, suspend it, and then turn encryption off. The decryption scan starts from the beginning. The same applies in reverse. This works for TDE with service-managed keys and with customer-managed keys. Manage encryption status in the Azure portal You can see and control the state of the encryption scan directly in the Azure portal. On the transparent data encryption page of your database, the encryption status shows whether the database is encrypted, being encrypted, or suspended, and offers the matching action. Encryption in progress While the scan is running, the status shows that encryption is in progress and a suspend button appears to pause the scan. Suspended When you suspend the scan, the status changes to suspended and a resume button appears so you can continue from where you left off. Encrypted Once the scan completes, the database shows as encrypted. Use T-SQL to suspend and resume The same commands that exist in SQL Server are available in Azure SQL Database. Suspend an encryption scan ALTER DATABASE my_db_name SET ENCRYPTION SUSPEND Resume a suspended encryption scan ALTER DATABASE my_db_name SET ENCRYPTION RESUME Start encryption, suspend it, then decrypt again ALTER DATABASE my_db_name SET ENCRYPTION ON ALTER DATABASE my_db_name SET ENCRYPTION SUSPEND ALTER DATABASE my_db_name SET ENCRYPTION OFF Monitor the scan Track the state of the scan with the sys.dm_database_encryption_keys dynamic management view, which reports the encryption state of the database and its encryption keys. SELECT DB_NAME(database_id), * FROM sys.dm_database_encryption_keys The percent_complete column shows the progress of the encryption state change. Get started and share feedback Suspend and resume is available in public preview for Azure SQL Database. Public preview features are covered by the Supplemental Terms of Use for Microsoft Azure Previews. To learn more about how TDE works, including service-managed and customer-managed keys, see the TDE overview on Microsoft Learn. Try it on your databases and tell us what you think. Your feedback helps us shape the feature before general availability.113Views0likes0CommentsTransparent data encryption in Azure SQL Database now supports AES keys (Generally Available)
TDE with customer-managed keys has traditionally used asymmetric RSA-based key protectors, while broader industry guidance is increasingly focused on preparing for a post-quantum cryptographic (PQC) future and adopting cryptographic approaches that are better aligned with that transition. This update aligns with broader security guidance, including the NSA’s CNSA 2.0 recommendations, which emphasize modern cryptographic planning for a quantum-resistant future. For organizations building crypto agility into their platforms, AES key support is a practical step in that direction. Why it matters Preparing for a post‑quantum world With current technology, breaking asymmetric algorithms such as Elliptic Curve and RSA-2048 using the best-known classical methods would take billions of years. Even with large-scale distributed computing, it is still considered computationally infeasible. Asymmetric algorithms are vulnerable to Shor’s algorithm, which means a sufficiently powerful quantum computer could break RSA-2048 much faster. That said, this would require millions of stable qubits, and current quantum systems are still far from that point. AES, as a symmetric algorithm, is not affected by Shor’s algorithm and remains more resistant to known quantum attacks, including Grover’s algorithm, when used with larger key sizes such as AES-256. The figure below highlights the difference in the estimated effort required to break RSA-2048 and AES-256. For context, the green dashed line represents the age of the universe, about 13.8 billion years. Aligning with modern security guidance Security guidance is moving toward stronger crypto agility and long-term resilience. By supporting AES keys for TDE protectors, Azure SQL Database gives customers a way to align data-at-rest protection with evolving security and compliance expectations. For a broader overview of quantum computing and cryptography, see Microsoft’s post-quantum cryptography overview. How it works (high level) At a high level, nothing changes about the purpose of TDE: it still protects data at rest by encrypting the Database Encryption Key (DEK) with a TDE protector. What changes is the type of key you can use to protect, or wrap, the AES DEK. The AES DEK encrypts database data files and log files. The TDE protector encrypts the DEK. With TDE with customer‑managed keys, the TDE protector is stored in Azure Key Vault or Azure Key Vault Managed HSM. The TDE protector can now be a symmetric AES key instead of an RSA key. For background on customer-managed TDE, see the Customer-managed transparent data encryption (TDE) Get started Make sure the following prerequisites are in place: An Azure SQL Database logical server or database with customer-managed TDE enabled. An Azure Key Vault Premium or Azure Key Vault Managed HSM with support for AES keys. Soft-delete and purge protection enabled on the key store. The required permissions for Azure SQL Database to access the key. You can review the full prerequisites in Microsoft Learn under requirements to configure customer-managed TDE. The setup flow for AES keys is essentially the same as for RSA-based TDE protectors. The main difference is the type of key you create and register. Create an AES key (for example, AES‑256) in Azure Key Vault Premium. Add the key to your Azure SQL logical server. Set the AES key as the TDE protector. Verify that encryption is enabled using system views. For step-by-step configuration guidance, see Microsoft Learn on Create Azure SQL Database Logical Server Configured with User-Assigned Managed Identity and Customer-Managed TDE. Example configuration (PowerShell) The following example shows the basic PowerShell flow: create an AES key, register it with the logical server, and then set it as the TDE protector. # Variables $VaultName = "MyPremiumVault" $keyName = "TDE-AES-Key" $sqlServerName = "my-sql-server" $sqlResourceGroup = "my-sql-rg" # Create an AES-256 HSM-backed key in MHSM Add-AzKeyVaultKey ` -VaultName $VaultName ` -Name $keyName ` -KeyType oct ` -Destination HSM ` -Size 256 # Get key URI $key = Get-AzKeyVaultKey -VaultName $VaultName -Name $keyName # Register the key with the SQL server Add-AzSqlServerKeyVaultKey ` -ResourceGroupName $sqlResourceGroup ` -ServerName $sqlServerName ` -KeyId $key.Id # Set the key as the TDE protector Set-AzSqlServerTransparentDataEncryptionProtector ` -ResourceGroupName $sqlResourceGroup ` -ServerName $sqlServerName ` -Type AzureKeyVault ` -KeyId $key.Id After you enable TDE with AES keys, you can verify the database encryption status by running the following query: SELECT DB_NAME(database_id) AS DatabaseName, encryption_state_desc, encryptor_type FROM sys.dm_database_encryption_keys WHERE database_id <> 2; If the database is encrypted, the view returns an ENCRYPTED state, or ENCRYPTION_IN_PROGRESS while encryption is still underway, with SYMMETRIC_KEY shown as the encryptor type. Learn more Microsoft Learn: customer-managed transparent data encryption for Azure SQL Database Microsoft Learn: configure customer-managed TDE for Azure SQL Database Microsoft Research: post-quantum cryptography overview Conclusion AES key support for customer-managed TDE gives Azure SQL Database customers a practical way to strengthen their encryption strategy while preparing for long-term cryptographic change, including post quantum cryptography. Because the setup experience remains familiar, teams can use this new functionality without rethinking how TDE works operationally.944Views3likes0CommentsAnnouncing Automatic Backup Immutability for Azure SQL Database and Azure SQL Managed Instance
Built-in protection for your most recent backups - enabled automatically Today, we're excited to announce General Availability of automatic backup immutability up to the most recent 7 days of point-in-time restore (PITR) backups in Azure SQL Database and Azure SQL Managed Instance, at no additional cost. With this release, up to most recent 7 days of backups are automatically protected with immutability by default, regardless of your configured PITR retention period. No configuration changes, policy creation, or administrative action are required. This enhancement provides an additional layer of protection for one of your most critical recovery assets - your backups. Why backup immutability matters Cyberattacks continue to evolve, with ransomware increasingly targeting not only production data, but also backup systems. Attackers understand that if backups can be deleted, modified, or corrupted, recovery becomes significantly more difficult and costly. Traditional backup strategies focus on creating recoverable copies of data. Modern cyber-resilience strategies go further by ensuring those backups themselves cannot be altered or removed during a protected period. Immutable backups help ensure that recovery points remain available when you need them most - even in the face of malicious actions, accidental deletion, or compromised administrative credentials. What is changing? Starting with this release: Up to the most recent 7 days of Azure SQL Database and Azure SQL Managed Instance PITR backups are automatically protected by immutability Protection is enabled by default for all databases, with no additional cost No configuration or onboarding is required Protection applies regardless of the database's configured PITR retention setting Because this capability is built directly into the Azure SQL backup service, customers automatically benefit from stronger protection without changing existing backup, restore, or operational workflows. Designed for modern cyber resilience Organizations across industries increasingly require stronger safeguards around backup data as part of broader cyber-resilience programs. Automatic backup immutability helps customers: Improve protection against ransomware attacks Reduce the risk of accidental backup deletion Strengthen recovery readiness Increase confidence that recent recovery points remain available during an incident Simplify adoption of immutable backup practices without additional deployment effort This capability is particularly valuable because the backups most often used during recovery operations are typically the most recent ones. Supporting compliance and governance requirements Many industries must maintain records in a protected, tamper-resistant manner to satisfy regulatory and governance requirements. Azure Storage immutable storage capabilities have been validated for compliance scenarios involving requirements such as: SEC Rule 17a-4(f) CFTC Rule 1.31(d) FINRA record-retention requirements These regulations commonly require records to be retained in a nonerasable, non-rewritable format for a defined period of time. Azure immutable storage uses a Write Once, Read Many (WORM) model that helps organizations meet these requirements. Azure SQL database backups leverage this WORM capability from Azure storage to achieve immutability for the backups. While compliance requirements vary by organization and jurisdiction, automatic backup immutability provides an additional foundational control that can support broader security, governance, and resilience objectives. No additional complexity One of our goals with this release is to deliver stronger security without increasing operational burden. You don't need to: Create immutability policies Configure storage accounts Manage retention locks Extract data The protection is integrated directly into the Azure SQL managed backup service and works automatically for all Azure SQL Database and Azure SQL Managed Instance databases. Pricing and Availability Automatic backup immutability up to the most recent 7 days of point-in-time restore (PITR) backups is available for all Azure SQL Database and Azure SQL Managed Instance databases. There is no additional cost to use this capability. The protection is built into the Azure SQL managed backup service and is automatically applied to the most recent 7 days of backups. No configuration, policy management, or separate licensing is required. By enabling immutable protection by default and at no additional charge, Azure SQL helps customers strengthen their cyber-resilience posture, improve protection against ransomware and accidental deletion, and gain the benefits of immutable backups without added operational complexity. Building on Azure SQL's data protection foundation Automatic backup immutability is the latest enhancement in Azure SQL's ongoing investment in data protection, security, and business continuity. By combining automated backups, point-in-time restore capabilities, geo-redundant backup options, soft delete protection for your Azure SQL logical server and now automatic backup immutability for recent backups, Azure SQL continues to help organizations strengthen their resilience against both operational accidents and modern cyber threats. This is just the beginning. Azure SQL hyperscale backup immutability and a host of other additional capabilities are coming soon. FAQs Q: What is changing? A: Microsoft Azure SQL will start protecting the short-term retention backups for all Azure SQL DB and Azure SQL managed instance databases with immutability to protect against ransomware attacks. Q: Are all my backups protected? A: In this release, up to most recent 7 days of short-term retention backups are immutable, regardless of the configured retention period. For example, if the configured retention period is 7 or less, then all the backups are immutable. If the configured retention period is 35 days, then the most recent 7 days of backups are immutable. Q: Is there any additional cost for this feature? A: No. Immutability for the backups is being provided as a security feature natively. Q: When will this be available? A: The code to enable immutable policy is already in progress in all Azure regions worldwide. In the next few weeks all backups will be on immutable storage. Q: Do I need to do anything to enable/configure immutability? A: No. There is no action needed on your end. The backups will automatically be immutable once the enablement is complete. Q: How can I verify if my backups are immutable? A: In a future release, immutability status will be exposed as a database property. Q: How can I get immutability for my backups beyond 7 days? A: In this release backups up to most recent 7 days are immutable. Immutability for additional retention period will be added in a future release. Limitations Immutability for Azure SQL hyperscale is not included in this release but will be available soon. Learn more To learn more about immutable storage concepts and WORM (Write Once, Read Many) protection in Azure, see: https://learn.microsoft.com/azure/storage/blobs/immutable-storage-overview We are excited to bring this protection to every Azure SQL Database and Azure SQL Managed Instance customer automatically, helping you improve backup security and recovery readiness with no additional effort. Documentation updates More details at https://aka.ms/auto-immutability Looking ahead We are just getting started on this journey of ransomware protection. Additional flexibility and configuration options coming in future releases.1.8KViews3likes3Comments
Managing security with Database Hub in Fabric: From signals to action
As organizations embrace AI, cloud modernization, and increasingly complex application architectures, the database estate continues to grow. What was once a handful of databases can quickly become hundreds or thousands of resources spread across subscriptions, regions, clouds, and database platforms. Security teams and database administrators face a common challenge: understanding the security posture of this growing estate and knowing where to focus attention first. While security controls exist across individual database services, assessing security posture at an estate level often requires navigating multiple portals, manually collecting findings, and piecing together information from different tools. Database Hub in Microsoft Fabric, now in public preview, gives database teams a unified place to discover their database estate and review security posture across supported database platforms. This estate-wide experience helps teams identify potential security gaps, understand where attention may be needed, and determine the right next step to improve overall security posture for databases. Security challenges at database estate scale Most organizations are no longer managing a single database platform. A typical enterprise environment may include: Azure SQL Database, Azure Database for PostgreSQL, Azure Cosmos DB, SQL Server instances running on-premises or through Azure Arc, SQL databases running inside Microsoft Fabric and additional database platforms. As environments expand, common security questions become increasingly difficult to answer: Which databases require attention? Where are security best practices not being followed? Which issues affect the largest portion of the estate? What action should be taken first? Customers need a simpler way to assess security posture across the entire estate rather than investigating databases individually. Database Hub was designed to help answer those questions. Security posture at a glance Database Hub provides a centralized view of database inventory, health, performance, optimization opportunities, and security findings across supported platforms. For security scenarios, the goal is simple: Help customers quickly understand the current posture of their database estate and identify the issues that matter most. Database Hub aggregates security findings across available resources and presents them in an estate-wide view, allowing teams to immediately see areas that require attention. Instead of manually reviewing databases one at a time, administrators can start with a single consolidated view and understand where security gaps exist across their environment. The current public preview introduces an initial set of security checks across supported database platforms. Depending on the database type, these checks cover areas such as authentication, data protection, auditing, and network security. For details about the checks currently available for database resources, refer to the Learn documentation. As we continue to work with customers throughout the preview and beyond, we will use feedback to refine the security experience, expand coverage across database platforms, and introduce additional capabilities. These signals aren't intended to replace the deeper security capabilities available within each database platform. Instead, Database Hub provides an estate-level starting point for identifying potential gaps and deciding where to investigate further. Database Hub complements existing security products and services by providing a unified view of broadly applicable security practices across the database estate. Customers can use these experiences together for a more complete understanding of database security posture. Prioritize what matters most Not all security findings have the same impact. Some controls affect a small number of databases. Others may represent risks across large portions of the estate. Database Hub helps customers focus on their investigation by distinguishing security issues that may require immediate attention from longer-term suggestions, and by showing how many resources are affected. This estate-wide context helps teams understand the potential scope of a finding and decide where to investigate first. Rather than asking: "Which database should I investigate next?" Teams can answer: "Which security issue should I address first?" Move from discovery to action Visibility alone is not enough. Once a finding is identified, the next step is to understand why it matters and what action should be taken. Database Hub provides additional context for findings and helps guide customers toward remediation. Teams can review affected resources, understand the recommendation, and, where supported, refer to relevant documentation and continue to the appropriate management experience to take corrective action. What’s next for security in Database Hub The security signals described above are available as part of the current public preview. Looking ahead, we plan to build on this foundation with additional capabilities that help teams continuously understand, prioritize, and improve security posture across their database estate. We are exploring several areas of investment, including: Broader security coverage: We plan to add security signals across more supported database types and security areas, providing a more complete picture of your database security posture. A dedicated Security page in Database Hub: We plan to create a focused experience that brings security posture, prioritized findings, and affected resources together. The goal is to help security administrators understand overall posture at a glance, see what parts of the estate need attention, and take the right action to improve it. Agentic security analysis: We are exploring agentic capabilities that go beyond configuration-based checks to analyze more complex security scenarios and surface insights, for example, identifying users or applications that may have more privileges than they need and recommend opportunities to move toward least-privilege access. These capabilities represent our forward-looking direction and are not part of the current preview. Customer feedback will help us refine this vision and prioritize the capabilities that provide the greatest value. Try security experiences in Database Hub today Whether you're responsible for a handful of databases or a global database estate spanning multiple platforms, Database Hub provides a simpler way to understand security posture, prioritize action, and move towards a more secure database environment. If you're using Database Hub today, you can already explore the available security experiences and security findings across supported database platforms. As you explore Database Hub, we’d love to hear which security signals, insights, and agentic experiences would be most valuable for managing your database estate. Please share your feedback directly within Database Hub by using the "Feedback" option. Your feedback will help us prioritize the capabilities and experiences we build next and align the Database Hub security roadmap with how you manage security in real-world database estates. We're excited to continue learning from customers and shaping the next generation of database security experiences together. Learn more Explore Database Hub in Microsoft Fabric Review Database Hub documentation on Microsoft Learn366Views1like0CommentsAzure SQL Database is retiring Always Encrypted with Intel SGX enclaves
On October 31, 2027, Azure SQL Database will retire Intel Software Guard Extensions (SGX) enclave functionality for Always Encrypted. Workloads that still depend on Intel SGX enclaves after that date will no longer work as configured. The path forward is Virtualization-Based Security (VBS) enclaves, a hardware-independent option that does not require attestation. To retain secure-enclave capabilities, move databases from DC-series compute to a supported standard-series, non-DC tier and update affected applications for VBS enclave mode. What is changing? Intel SGX enclaves are tied to DC-series compute. After October 31, 2027, databases on these tiers must move to supported compute to retain enclave-enabled capabilities. Applications configured for Intel SGX enclaves may also need driver and connection-string updates. For workloads that do not require isolation from the host operating system, VBS enclaves offer a straightforward migration within Azure SQL Database. If your threat model requires Intel SGX-equivalent host isolation, evaluate SQL Server on Azure Confidential VMs instead. Choose the right migration path Use the migration guide to identify databases and elastic pools on DC-series compute, choose the target architecture that matches your threat model, update application connectivity and attestation settings, and validate the workload before production cutover. Move to VBS enclaves in Azure SQL Database Choose VBS enclaves when you need to protect sensitive data from unauthorized users or malicious insiders but do not require isolation from the host operating system. VBS enclaves run on supported non-DC compute tiers and eliminate attestation requirements. Consider SQL Server on Azure Confidential VMs If your threat model requires stronger isolation from the host operating system, assess SQL Server on Azure Confidential VMs. Compare architecture, operations, compatibility, and cost with the Azure SQL Database option. Start planning early Start now. Discovery, compute-tier changes, application updates, security review, and production validation all take time. Complete the migration before October 31, 2027, to keep enclave-enabled workloads running without interruption. Help and support Have questions? Ask community experts in Microsoft Q&A. If you have an Azure support plan and need technical help, create a support request. Review service retirements that may affect your resources in the Azure Retirement Workbook. For more ways to find impacted resources, see the retirement guidance. Retirement information may take up to two weeks to appear.449Views1like1Comment
Understanding DevOps Auditing API Migration Behavior in Azure SQL Database
Background Historically, DevOps Auditing could be configured through the server-level auditing API using the isDevopsAuditEnabled property under: Microsoft.Sql/servers/auditingSettings As Azure SQL auditing capabilities evolved, a dedicated resource was introduced specifically for DevOps Auditing: Microsoft.Sql/servers/devOpsAuditingSettings This dedicated API is now the supported approach for configuring DevOps Auditing. The Question Customers occasionally observe that setting isDevopsAuditEnabled=true continues to work on some servers but not on others. A recent customer engagement highlighted this scenario where the same deployment was able to enable DevOps Auditing on most servers, while a smaller subset of servers ignored the setting even though the ARM operation completed successfully. At first glance, this appears inconsistent. However, the behavior is expected. How Backward Compatibility Works Today, Azure SQL maintains backward compatibility for customers who still use the legacy auditing API. The behavior is as follows: The recommended and supported approach is to use the dedicated DevOps Auditing resource: Microsoft.Sql/servers/devOpsAuditingSettings 2. The isDevopsAuditEnabled property under: Microsoft.Sql/servers/auditingSettings is no longer recommended for new implementations. 3. To preserve backward compatibility, the legacy property may continue to work for servers that have never been migrated to the new model. 4. Once the dedicated DevOps Auditing API is used on a server for the first time, that server is permanently marked as migrated. 5. After migration, the legacy isDevopsAuditEnabled property is no longer honoured for that server, even if it is supplied in subsequent requests. Why Some Servers Behave Differently Consider an environment with hundreds of Azure SQL servers managed through ARM templates or Azure Policy. The deployment may successfully update: { "type": "Microsoft.Sql/servers/auditingSettings", "properties": { "isDevopsAuditEnabled": true } } For servers that have never used the new DevOps Auditing resource, the setting may still take effect. For servers that were previously configured through: Microsoft.Sql/servers/devOpsAuditingSettings the server is already considered migrated. In these cases, the request can complete successfully, but the legacy property is ignored and DevOps Auditing remains unchanged. Recommended Action Customers should migrate all automation, ARM templates, Bicep templates, Terraform deployments, and Azure Policies to use the dedicated DevOps Auditing resource: Microsoft.Sql/servers/devOpsAuditingSettings and avoid relying on the legacy isDevopsAuditEnabled property going forward. Key Takeaway If isDevopsAuditEnabled appears to work for some servers but not others, it is usually due to the server's migration state: Not yet migrated → legacy flag may still work. Already migrated → legacy flag is ignored. Use Microsoft.SQL/servers/devOpsAuditingSettings for all future configurations. This behavior allows Azure SQL to maintain backward compatibility while providing a clear migration path to the dedicated DevOps Auditing configuration model. For the new API, refer documentation Server DevOps Audit Settings - Create Or Update - REST API (Azure SQL Database) | Microsoft Learn Server DevOps Audit Settings - Get - REST API (Azure SQL Database) | Microsoft Learn Microsoft.Sql/servers/devOpsAuditingSettings - Bicep, ARM template & Terraform AzAPI reference | Microsoft Learn396Views0likes0CommentsHostNameInCertificate changes in Azure SQL Managed Instance affecting client connectivity
Azure SQL Managed Instance is changing how TLS certificates are stored and handled in managed instances. One of those certificates was specifically tailored to support migration scenarios where SQL clients retain the server name, while updating its record in DNS so that it resolves to the managed instance instead. This was supported with an instance certificate that we are now replacing in favor of a more complete solution. When does this change take effect? New managed instances already contain certificates with a reduced list of SANs. Existing managed instances will have their certificates revoked and replaced with reduced certificates during the first week of August 2026. Am I affected? Your SQL clients and applications might be unable to connect if all of the below is true: The client is connecting over the VNet-local endpoint, and The client attempts to establish a Redirect connection, and Client settings contain the HostNameInCertificate connection parameter. The exact error message depends on your application, client, and driver. For example: The target principal name is incorrect. The certificate chain was issued by an authority that is not trusted. The certificate's CN name does not match the passed value. The remote certificate is invalid according to the validation procedure. Failed to validate the server name in a certificate hostname verification failed certificate verify failed: Hostname mismatch My clients are affected. What should I do? If your clients are affected, find an appropriate solution in the table below. If the client is... Solution Connecting to the managed instance's VNet-local endpoint with Redirect using the instance's original VNet-local domain name Remove HostNameInCertificate from client's connection string; or Deploy a private endpoint and ensure your client is connecting to it. Connecting to the managed instance’s VNet-local endpoint with Redirect using a different domain name (for example, via DNS CNAME) Set the instance’s connection type to Proxy; or Deploy a private endpoint and ensure your client is connecting to it. Connecting via private endpoint No action is needed. Connecting via public endpoint No action is needed. Connecting with Proxy connection type No action is needed. What else should I know? Microsoft recommends you adhere to the security best practices for data in flight: Only allow network access to known networks and hosts; see Connecting to a managed instance. Authorize using safe credentials, ideally by using Microsoft Entra where possible. Always use TLS encryption (Encrypt=Strict or Encrypt=Mandatory). Monitor suspicious network activity throughout your network topology. Follow the principle of least privilege. Ensure that your SQL clients and applications have a network path to fetch the latest CRL and/or connect to OCSP for certificate validation.639Views0likes0Comments