azure arc
265 Topics
End of Lifecycle for Windows Server 2012 and 2012 R2
On October 13, 2026, the Extended Security Updates (ESU) program for Windows Server 2012 and Windows Server 2012 R2 ended. This closes the three-year extended coverage period that began when these operating systems reached end of support in October 2023. After today, Microsoft will no longer provide security updates for Windows Server 2012 or Windows Server 2012 R2. How we got here Windows Server 2012 and 2012 R2 reached end of support on October 10, 2023. To give customers time to modernize, Microsoft offered up to three additional years of ESU for eligible servers. Over that time, ESU gave organizations a way to keep receiving critical security updates for workloads that needed more time to upgrade, migrate or modernize. What this means for you Servers still running Windows Server 2012 or 2012 R2 will no longer receive security updates from Microsoft. Unsupported operating systems become harder to secure and maintain over time and running them in production adds security and compliance risk. Unsupported infrastructure shouldn't be a long-term strategy. What to do next If you still have Windows Server 2012 or 2012 R2 workloads in production, start with these steps: Identify affected servers. Inventory your datacenter, edge and cloud environments to find where Windows Server 2012 and 2012 R2 are still running. Understand your dependencies. Many remaining deployments support business-critical applications. Validate what depends on each server before you decide what to do with it. Choose a path for each workload. Options include upgrading to a supported version of Windows Server, migrating workloads to Azure, modernizing applications onto Azure services, or adopting a hybrid approach. Set a timeline and prioritize. Move business-critical and highest-risk workloads first to reduce operational and security exposure. Get help. Engage your Microsoft account team and trusted partners to build a transition plan that fits your environment. Why modernizing is worth it Moving to a supported platform is the best way to stay secure, and it also gives you the following: A stronger security posture, with ongoing security updates and support Better operational efficiency through modern management capabilities The latest performance, reliability and resiliency improvements Less technical debt and lower long-term infrastructure risk Access to new AI, cloud and hybrid capabilities Looking ahead Microsoft is committed to helping you modernize on your terms, whether you're upgrading on-premises infrastructure, migrating to Azure or taking a hybrid approach. To learn more about support lifecycle information and modernization paths, see Overview of Extended Security Updates for Windows Server 2012 and 2012 R2 on Microsoft Learn.300Views0likes0CommentsEpisode 2: Reduce restarts with Hotpatch for Windows Server 2025 | The Azure Arc Check-In
Once a month, the Azure Arc team releases an episode covering a new hybrid and multicloud management scenario. To request a topic or view additional episodes, visit aka.ms/the-azure-arc-check-in. Scenario: Your infrastructure team needs to apply monthly security updates across hybrid Windows servers, but every restart creates another maintenance window and potential workload interruption. Hotpatch can reduce that restart-driven effort while helping you keep eligible servers protected. Try now in Azure aka.ms/aaci-episode2 Why Hotpatch matters Security updates are essential, but coordinating restarts across a distributed server estate takes time and can disrupt workloads. Hotpatch updates Windows security code in memory, allowing eligible security updates to take effect without requiring a restart. For Azure Arc-enabled Windows Server 2025 machines, enabling and using Hotpatch is available at no additional charge. Hotpatch reduces restart frequency, but it does not eliminate every restart. Baseline updates and updates outside the Hotpatch program can still require one. Confirm that your server is eligible Before enabling Hotpatch, confirm that the machine meets the operating system, Azure Arc, and security prerequisites. The server must: Run Windows Server 2025 Standard or Datacenter, build 26100.1742 or later. Run a generally available release. Preview and Windows Server Insider builds are not supported. Meet the Azure Connected Machine agent prerequisites and be connected to Azure Arc. Support virtualization-based security and Virtual Secure Mode. Use Unified Extensible Firmware Interface (UEFI) with Secure Boot enabled. Be a Generation 2 virtual machine when hosted on Hyper-V. Windows Server 2025 Datacenter: Azure Edition follows a different path because Hotpatch is enabled by default and does not require Azure Arc connectivity. For the latest requirements, see Enable Hotpatch for Azure Arc-enabled servers. Verify Virtual Secure Mode Run the following PowerShell command on the server to check its Virtual Secure Mode status: Get-CimInstance -Namespace 'root/Microsoft/Windows/DeviceGuard' -ClassName 'win32_deviceGuard' | Select-Object -ExpandProperty 'VirtualizationBasedSecurityStatus' A result of 2 means Virtual Secure Mode is configured and running. If the result is not 2, resolve the prerequisite before enrolling the machine in Hotpatch. Enabling Virtual Secure Mode requires a server restart, so make that change during a planned maintenance window. Enable Hotpatch through Azure Arc After confirming the prerequisites, enroll the server from the Azure portal: Open Azure Arc, then select Machines. Select the eligible server. Select Hotpatch. Review the confirmation, then select Confirm. Allow about ten minutes for the changes to apply. Verify that enrollment completes and the status is no longer pending. The portal enrollment is intentionally short. Most of the work is making sure the server meets the prerequisites before you begin. Choose how to manage updates Hotpatch enrollment and update installation are separate. After enrollment, continue to manage available updates according to your organization's patch policy and change-control process. Supported options for Arc-connected machines include: Windows Update Azure Update Manager Group Policy SConfig Supported non-Microsoft patch-management solutions Choose the method that fits your existing operations model. Enrolling a server in Hotpatch does not, by itself, install every available update automatically. Plan for the restart cadence Hotpatch changes the monthly update rhythm, but restart planning still matters. Every three months, Microsoft releases a planned baseline with the latest cumulative update. Installing a baseline requires a restart. Hotpatch releases normally follow during the next two months, allowing eligible security updates to be applied without a restart. An unplanned baseline can replace a scheduled Hotpatch release when necessary and will also require a restart. Updates outside the Hotpatch program can require restarts as well, including: Nonsecurity Windows updates .NET updates Drivers Firmware Other non-Windows updates The practical operating model is fewer restart-driven maintenance windows, not a server that never needs to restart. FAQs 1. Does Hotpatch mean I never need to restart the server? No. Planned baselines arrive every three months and require a restart. Unplanned baselines and updates outside the Hotpatch program can also require restarts. Hotpatch reduces restart frequency for eligible security updates; it does not eliminate restart planning. See Hotpatch for Windows Server. 2. Is Hotpatch an extra-cost service for Azure Arc-enabled Windows Server 2025? Enabling and using Hotpatch on eligible Azure Arc-enabled Windows Server 2025 machines is available at no additional charge. Optional Azure management services may have separate pricing. 3. Does enrolling in Hotpatch install every update automatically? No. Enrollment makes the machine eligible to receive Hotpatch updates. Continue using Windows Update or a supported patch-management tool, such as Azure Update Manager, Group Policy, SConfig, or a non-Microsoft solution, to manage available updates according to your patch policy. 4. Can I use Hotpatch with Windows Server Core? Yes. Both Server Core and Server with Desktop Experience are supported when the machine meets all other Hotpatch prerequisites. 5. What does a Virtual Secure Mode status of 2 mean? For the documented Device Guard PowerShell query, a result of 2 means Virtual Secure Mode is configured and running. If you receive another result, resolve the prerequisite before attempting enrollment. Review the current Hotpatch enablement guidance and Hotpatch concepts and update cadence, then visit The Azure Arc Check-in for more episodes.306Views2likes0Comments
Azure Local Storage: Choose the Architecture That Fits Your Business
Organizations modernize infrastructure in different ways. Some prioritize a simple, integrated platform; others need to preserve SAN investments, scale storage independently, or support workloads with different storage requirements. In this post, we'll explore the storage options available in Azure Local, when to use each one, and the business benefits they unlock. One Platform, Multiple Storage Architectures Azure Local brings multiple storage choices into a consistent, cloud-connected platform experience. Hyperconverged Infrastructure (Storage Spaces Direct) Storage Spaces Direct (S2D) provides a hyperconverged architecture where compute and storage are integrated into the same cluster. This model is ideal for customers looking for streamlined deployment experience, with infrastructure managed as a single platform and fewer organizational dependencies. Disaggregated Architecture (SAN Only) Azure Local supports validated external storage arrays connected through Fibre Channel or iSCSI. This architecture enables organizations to leverage existing storage investments and advanced storage services while independently scaling compute to support higher-capacity requirements. This gives customers the flexibility to work with supported storage vendors—including Dell, HPE, Hitachi, Lenovo, NetApp, and Everpure—while using the Fibre Channel or iSCSI connectivity already supported by Azure Local. Hybrid Architecture (Storage Spaces Direct + SAN) Customers can also combine Storage Spaces Direct and external storage to support different workload requirements within the same environment. This approach offers maximum flexibility, allowing organizations to align storage choices with application needs. Which Storage Option Should You Choose? If your goal is... Consider Simple integrated infrastructure Hyperconverged Expand an existing Azure Local cluster storage capacity Hybrid Reuse existing storage investments Hybrid or Disaggregated Independent compute and storage scaling Disaggregated Consolidate storage across workloads Disaggregated Advanced storage efficiency capabilities Disaggregated Flexible workload placement Hybrid Traditional three-tier architecture modernization Disaggregated Minimize infrastructure replacement Disaggregated Higher-scale compute clusters with more than 16 nodes Disaggregated Ready to size your solution? Use ODIN for Azure Local to translate workload, resiliency, growth, compute, and storage requirements into an example solution design. Use ODIN as a planning aid and validate the proposed configuration against official Azure Local documentation and with your preferred hardware and storage partners. Before finalizing your design, review External storage support for Azure Local for supported architectures and protocols, and Supported SAN solutions on Azure Local for validated storage partners and configurations. Use the comparison above to identify the most suitable architecture, then use ODIN, official Azure Local documentation, and partner guidance to validate workload sizing, supported configurations, and operational requirements. Modern Infrastructure Demands More Storage Flexibility Storage architecture decisions increasingly depend on more than capacity and performance. Organizations must also account for operational processes, maintenance planning, existing infrastructure, efficiency services, resiliency, and expected growth. These priorities influence whether an organization chooses an integrated, disaggregated, or hybrid architecture—and which benefits matter most in its environment. The following benefits explain where external storage can add value within that decision. Benefits of External Storage with Azure Local Protect Existing Investments Many organizations already operate enterprise storage platforms that support critical business applications. Azure Local enables customers to modernize compute infrastructure while continuing to leverage existing storage investments, operational expertise, backup strategies, and storage management processes. Get More Value from Every Terabyte Storage efficiency is becoming increasingly important as organizations scale virtualized environments, desktop infrastructure, databases, and application workloads. Many enterprise storage platforms offer advanced services such as compression, deduplication, thin provisioning, and capacity optimization. Organizations can leverage these capabilities while maintaining consistent Azure Local management experience. Spend Less Time Maintaining Infrastructure Operational efficiency is often just as important as infrastructure capabilities. Because compute and storage are separated in SAN-based architectures, organizations can independently manage storage and compute infrastructure. This can help simplify maintenance planning and reduce storage-related operational activities during maintenance events. Customers frequently cite more predictable maintenance windows, simplified update planning, mature storage monitoring practices, and reduced operational complexity. Scale on Your Terms One of the primary reasons organizations adopt external storage is flexibility. In hyperconverged environments, compute and storage typically scale together. With disaggregated storage, organizations can expand storage capacity independently from compute resources. This can be particularly valuable when storage growth outpaces CPU or memory requirements. Designed for Enterprise Resiliency Azure Local pairs cloud-connected infrastructure with the storage maturity Windows Server has refined over many generations. For external storage, that means working with the same well-understood technologies you already rely on—Fibre Channel and iSCSI connectivity, MPIO, dual fabrics, redundant controllers, and Cluster Shared Volumes—applied to the Azure Local platform. Because these are proven, standard building blocks, you have the flexibility to design highly available storage that fits your existing SAN investments and operational practices, rather than adapt to an unfamiliar model. For implementation requirements and configuration steps—including Fibre Channel, iSCSI, MPIO, array-side configuration, and presenting SAN-backed volumes as Cluster Shared Volumes see : Connect an external storage array to Azure Local. Real-World Scenarios Streamlined Infrastructure for Distributed Locations Retail stores, branch offices, and back-office environments can use a hyperconverged architecture to run applications on an integrated compute and storage platform. This approach simplifies deployment and day-to-day operations for locations that need consistent infrastructure without dedicated storage teams. Flexible Workload Placement Manufacturing and healthcare organizations can use a hybrid architecture when some workloads are best served by integrated Storage Spaces Direct and others require external SAN capacity or established storage services. This allows application teams to place workloads on the storage option that best meets their performance, resiliency, and operational requirements. Modernizing while Preserving SAN Investments A manufacturing organization, financial institution, or enterprise datacenter with established SAN platforms and processes can use a disaggregated architecture to modernize compute without redesigning storage operations, retraining teams, or immediately replacing proven infrastructure. Scaling Storage as Data Needs Grow Data-intensive environments—including manufacturing, fintech, and enterprise datacenters—may find that storage capacity grows faster than compute demand. A disaggregated architecture allows them to scale storage and compute independently, helping optimize infrastructure investments over time. Cost and Licensing Considerations Azure Local uses a monthly service fee based on the deployment configuration: Hyperconverged deployments (S2D only): Compute and storage are integrated in the same cluster using Storage Spaces Direct, with no external SAN storage. A monthly service fee of $10 per physical core/month applies. Disaggregated (SAN only), and hybrid storage configurations (S2D with SAN): Disaggregated deployments use external SAN storage instead of Storage Spaces Direct, while hybrid deployments with external storage combine Storage Spaces Direct with external SAN storage. Using external SAN storage has a monthly service fee of $20.1 per physical core/month applies. Prices are subjected to change. For current pricing details and applicable terms, visit Azure Local Pricing | Microsoft Azure. Choosing the Right Fit for Your Business Start with the operating model and workload requirements you need to support, then choose the architecture that best fits them. Azure Local provides a consistent platform experience across hyperconverged, disaggregated, and hybrid deployments. That consistency lets organizations modernize without treating storage architecture as a one-time, irreversible choice. The right storage strategy is the one that fits your workloads, operations, and growth plans. Learn more: Storage Spaces Direct overview; External storage support for Azure Local; Supported SAN solutions on Azure Local; Connect an external storage array to Azure Local; Azure Local pricing; and Azure Hybrid Benefit for Azure Local.588Views2likes3Comments
Workload Orchestration in the Azure portal is now available: Deploy in minutes, scale with ease
Edge deployments rarely stay simple for long. What begins as an application running on a single Kubernetes cluster can quickly expand across stores, factories, branches, or other distributed locations, each having different configuration needs. That is exactly where workload orchestration for Azure Arc comes in. Workload orchestration helps teams manage that complexity by providing a centralized approach to consistently define, configure, and deploy applications across distributed cloud, on-premises, and edge environments, all while catering to custom configuration needs of individual sites and deployment targets. See the experience in action Evaluating a new deployment approach often starts slowly: study the documentation, package an application, complete the setup, and only then decide whether it fits. The Azure portal reverses that order with its jumpstart onboarding experience. Bring your Azure Arc-enabled Kubernetes cluster and deploy a pre-packaged application in minutes. Whether you are validating a proof of concept or introducing the product to your broader team, the new portal onboarding experience turns the end-to-end workflow into something you can quickly try on your own cluster. Scale from first deployment to production Once you have validated the first deployment, you can evolve the same approach for production. Onboard your infrastructure into workload orchestration, organize your deployment sites into hierarchies, and define shared configurations for all deployments – all without leaving the portal. This lets you expand from one cluster to a distributed fleet while retaining centralized governance, repeatability, and site-level flexibility. Ready to try it? Try now by deploying your first application with workload orchestration in the Azure portal. Explore the product documentation for the complete set of capabilities.447Views0likes0CommentsGenerally Available: Transition to WS2012 / R2 ESUs enabled by Azure Arc from Volume Licensing
Customers that have enrolled in WS2012/ R2 ESUs through Volume Licensing for Year 1 can transition to Azure Arc for Year 2 of the program by specifying their Volume Licensing entitlements (Invoice Ids) in provisioning new Azure Arc WS2012/R2 ESU licenses. Extended Security Updates afford customers with critical security patches for end of support Windows Server 2012/R2 machines.6.3KViews3likes4CommentsFive Key Updates on WS2012 ESUs enabled by Azure Arc
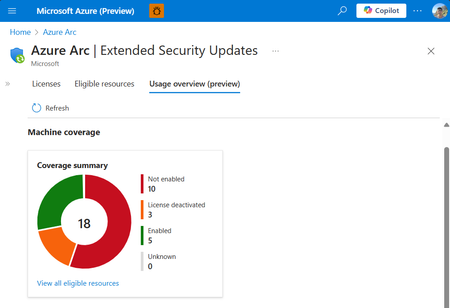
We’re excited to announce the public preview of the Azure Arc ESU Usage View and Transition Scenario from Year 1 Volume Licensing. Additionally, we have made a breadth of improvements to pre-requisites, billing service, and included capabilities.4.2KViews4likes3CommentsWindows Server 2012/R2 Extended Security Updates Licensing and Billing
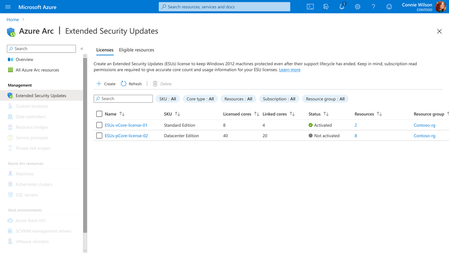
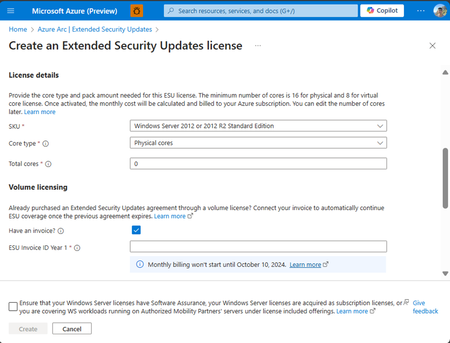
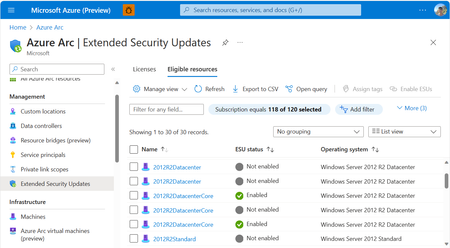
While more and more organizations are moving towards cloud they are all using cloud in their own way depending on size and scale. Some have adopted cloud native model using Microsoft Azure, but some decided to use cloud services while still maintaining their on-premises footprint. The latter approach is known as Hybrid model. Hybrid also means having presence in more than one cloud provider. While the Hybrid model comes with some advantages and flexibility it has certain challenges too. One of the biggest challenges is the added management complexity. In a Hybrid model as the workload grows, organizations might struggle to control the growing complex environments which could be extending across data centers, multiple clouds and even the edge. One common struggle which we will be covering in this blog post today is… the ability to protect your end-of-support Windows Servers which are either in multi-cloud environment or on-premises. What options do Customers have for end-of-support Windows Servers 2012/R2? It’s not always easy for clients to upgrade all older Windows Servers to Win2016 or later. As the on-premises or multi-cloud environment servers reach the end of support, it also means end of security updates which can put business applications running on the server at security risk and can cause compliance issues. The Extended Security Updates (ESU) program is an option that can be used by customers to run Windows servers past the end of support for a maximum period but not indefinitely. The updates provided through ESUs are only Security updates as well as critical and important rated bulletins. Below are options for customers to use ESU: Migrate workload to Azure: Migrate existing affected Windows Server workloads as-is to Azure Virtual Machines which will automatically provide ESU for a defined period without being additionally charged for these updates on top of Azure VM's cost. Migrating workloads to Azure VMware Solution (AVS) also makes them eligible for free ESUs. Get ESU through Azure Stack HCI: On-premises Windows Server 2012/ 2012 R2 virtual machines connected to cloud via Azure Stack HCI can get free ESUs through Azure verification of VMs. Purchase ESU license outside of Azure: By purchasing ESU, they can protect them until they decide to upgrade them to a more recent version or migrate them to cloud. Purchase ESU License Options If workload running outside of Azure and not connected to cloud through Azure Stack HCI, customers have below options for licensing ESU. Azure Arc-enabled Servers: Their on-premises servers or in a hosted environment should be connected through Azure Arc service to have Arc-enabled servers. If they are Arc enabled, they can enroll their Windows Server 2012 and 2012 R2 servers for ESU via the Azure portal. They will be billed monthly on their subscription. Non-Arc enabled physical and virtual machines – For these servers they can enable ESU by acquiring ESU licenses through Microsoft Volume Licensing program. These ESU licenses are valid for annual coverage periods and each license is entitled to a specific server or operating system for the duration it has been purchased. They can acquire license for later years only if they have acquired licenses for prior years. Purchase ESU License Eligibility Criteria To be eligible for ESU licenses, their server/operating system must qualify one of the following: Customers should have Software Assurance to purchase ESUs on-premises or in hosted environment. Windows Server 2012/2012 R2 machines are licensed through Services Provider License Agreement (SPLA) and not using their own licenses. Windows Server 2012/2012 R2 machines are licensed with a Server Subscription where Software Assurance is not required. ESU Licensing with Azure Arc enabled Windows Server 2012/2012 R2 To deliver ESU for Windows Server 2012, customers should provision Windows Server Arc ESU licenses and then apply/link those licenses to Azure Arc enabled servers. These can be done via Azure portal. Before we progress to understand how to provision WS2012 ESU license and to link licenses to Arc enabled servers it is good to be aware about below: Standard vs Datacenter Edition: When standard edition of license selected, it will be limited to 2 virtual instances but with Datacenter Edition, it can be applied to unlimited virtual instances. vCore Vs pCore Licensing: vCore (Virtual Core ) Licensing: When this licensing is chosen, they will pay based on the number of virtual cores (vCores) being used by the OS. It requires a minimum of 8 cores per Virtual machine when selected. It uses the standard edition rate for billing. pCore ( Physical Core) Licensing: If they choose to license based on physical cores (pCores), then they pay based on the number of physical cores (pCores) utilized by the host operating system. It requires a minimum of 16 cores per server when selected. Customers have the flexibility to use this licensing with either edition. NOTE: vCore Licensing cannot be used on physical servers. They can select either licensing options or can also select a mix of pCore and vCore licensing for their virtual machines within the remit of their virtualization entitlements. Create a new ESU WS2012 license: Step 1: Sign in to the Azure portal Step 2: On the Azure Arc service page, select Extended Security Updates in the left pane under Management section. Step 3: Under Licenses tab, select Create. Step 4: Provide the information required in Create an Extended Security Updates license page to configure the license. Resource group: The ESU license will be billed to. License name: You can create multiple licenses. It may be helpful following a naming convention for license name. SKU and Core Type: Select the value based on licensing option chosen. Core Packs: Enter the value based on cores count required. You can modify the number of cores associated with a license later after creation. Step 5: Review the information provided and then select Create. License created from above will appear in the list under Licenses tab. Licenses can be linked to Arc-enabled servers following steps in next section. ESU license can be provisioned in a deactivated state during creation to avoid initiation of billing. Link ESU licenses to Arc-enabled servers: Each license can be linked to one or more Arc-enabled servers. Step 1: Sign in to the Azure portal Step 2: On the Azure Arc service page, select Extended Security Updates in the left pane under Management section. Step 3: Select Eligible Resources tab. This will give you the list of all Arc-enabled servers which are running Windows Server 2012/2012 R2 and eligible for ESU updates. ESU Status column tells us whether the machine is ESU enabled. Step 4: Select the machines from the list (with ESU Status = Not enabled) and then select Enable ESUs. Step 5: Next page Enable Extended Security Updates shows the count of machines selected for enabling ESU and lists the available licenses. Select the license that needs to be linked to these machines and then click on Enable at bottom of page. It will take some time but later the status of machine in ESUs Status column changes to Enabled. NOTE: A Windows Server is eligible to receive ESU updates once linked to an activated ESU license. ESU Licensing limits: Customer can include up to 10,000 cores within each WS2012 ESU license and if needed for more cores then can split the cores across multiple licenses. However, there is a limitation of only 800 licenses per resource group. ESU Billing: Billing for ESU is mainly dependent on three factors: Number of cores provisioned Selection of license edition Any eligible discounts While above three factors sound simple, below are few good to know points before we proceed to understand on how to estimate monthly cost: Is the Customer planning to decommission any servers? Do not include the core counts for servers, which need to be decommissioned and do not require extended security updates applied. Back-billing for sign-ups after the end of support dates: For customers who enroll in ESUs enabled by Azure Arc after the end of support date October 10, 2023, for Windows Server 2012/R2, they will be billed a one-time upfront charge for the months they missed after the end of support date, with billing coming in at the end of the first month when they signed-up. Example: XYZ Corp has decided to enroll for ESU for Windows Server 2012/R2 in February 2024. In that case they will receive a one- time back-bill for October (starting from 11th of the month), November, December 2023, and January 2024 at the end of February month. After February, for the later months, XYZ Corp billing will only be based on the current month. Back-billing applies even if a customer intermittently deactivates ESUs. Example: If XYZ Corp, unenrolls in March 2024 and then decides to re-enrolls in June 2024, the re-enrollment will trigger back-billing for April and May 2024. When ESU enabled by Azure Arc, Customers can link their already paid extended security updates to their eligible Disaster Recovery Benefit servers. Billing is monthly. Decrementing, deactivating, or deleting a license will result in charges for up to five more calendar days from the time of decrement, deactivation, or deletion. Reduction in billing isn't immediate. There is no cost for non-production workloads that need ESU updates. Examples of Cost-Effective ESU Licensing: It is recommended to refer to the Azure Pricing calculator for calculating estimated monthly cost. Let us take some examples (based on public pricing) to understand cost effective ESU licensing. Example 1 *: XYZ Corp. has currently got a VMware cluster containing 28 hosts with 736 physical cores on-premises. There are 90 VMs on the cluster and they are running Windows Server 2012 R2 consuming all 736 cores. Based on above information, public pricing for Arc Enabled ESU for both the licensing option would be: pCore (Physical Core) Licensing: 46 x Windows Server 2012 DC – 16 Core (£341) = ~ £15K / month vCore (Virtual Core) Licensing: 92 x Windows Server Standard – 8 Core (£30) = ~ £3K / month They can either license the entire cluster with 736 Windows Server 2012 Datacenter ESU physical cores or license each VM individually with a total of 736 standard edition virtual cores. In the above case, it's cheaper to purchase an Arc ESU Windows Server 2012 Standard edition license associated with 736 virtual cores if all other factors align with the option. NOTE: In the above example it was assumed that ESU vCore/pCore licensing requirements for the machines were achieved. Example 2 *: ABC Corp has currently got 64 cores of Datacenter Edition and 128 cores of standard edition physical hosts running Windows 2012 and eligible for ESU. When buying licenses, they can buy in 2 or 16 core packs with not much difference in cost. 8 packs of 2 cores costs almost the same as 1 pack of 16 core. When buying 16 core packs then pricing calculation will be: 64 cores of Datacenter Edition = 4x Windows Server 2012 DC – 16 core (£341) = ~ £1.3 K /month 128 cores of Standard Edition = 8 x Windows Server Standard – 16 core (£60) = £480/month When calculating with 2 core packs, calculation will look like: 64 cores of Datacenter Edition = 32 x Windows Server 2012 DC – 2 core (£43) = ~ £1.3 K /month 128 cores of Standard Edition = 64 x Windows Server Standard – 2 core (£7.4) = £473.6 /month As seen in the above calculations, buying multiple packs of lesser core, or buying a smaller count of packs with larger core size does not bring much cost difference. However, for situations where they need granular control on activation of licenses, it might help with the flexibility in buying multiple packs of required cores. * This example is only for illustration purposes. Scenario and factors to consider for cost effective ESU licensing option may vary based on Customer requirements. Summary Extended Security Updates for Windows Server includes security updates, critical and important bulletins for a period after end of extended support. ESUs do not include new features, customer-requested non-security updates, or design change requests. After the period of ESU ends, Microsoft will stop providing updates. It is recommended to upgrade your version of Windows Server to the current version or more recent version as soon as possible for the most advanced security, performance and innovation. Where updates are not immediately possible, migrating your on-premises Windows servers Infrastructure (that has past the end of extended support or almost reaching to it) to Azure or connecting them to cloud using Azure Stack HCI is also an option (for a defined period) as they're eligible for free ESUs. ESU Availability and End dates information for Windows Server 2012/2012 R2 are: End of Extended Support/ESU Start Date: October 10, 2023 ESU End Date Year 1: October 8, 2024 ESU End Date Year 2: October 14, 2025 ESU End Date Year 3: October 13, 2026 Type of Security Update: Critical, Important Learn More Search Product and Services Lifecycle Information - Microsoft Lifecycle | Microsoft Learn Overview of Extended Security Updates for Windows Server 2008, 2008 R2, 2012, and 2012 R2 | Microsoft Learn Product Lifecycle FAQ - Extended Security Updates | Microsoft Learn Extended Security Updates (ESU) on Azure Stack HCI - Azure Stack HCI | Microsoft Learn Manage Azure Arc-enabled Servers using Windows Admin Center in Azure preview | Microsoft Learn Overview of Windows Server upgrades | Microsoft Learn Perform an in-place upgrade of Windows Server | Microsoft Learn16KViews7likes12CommentsGenerally Available: Windows Server 2012 and 2012 R2 Extended Security Updates enabled by Azure Arc
Secure your End-of-Life Windows Server infrastructure on your own terms with Azure Arc. Benefit from the flexibility of a monthly Azure billed service and free access to Azure management services by leveraging Extended Security Updates enabled by Azure Arc for your Windows Server 2012 and 2012 R2 machines.45KViews3likes4Comments