Where your Oracle data on Azure stays under your control
Regulated industries like banking, healthcare, and government face non-negotiable requirements for data localization, privacy, operational control, and compliance. Building on the controls already in Oracle AI Database@Azure, the Oracle Azure Resource Provider now supports the EU Data Boundary, so customers can deploy in the European Union (EU) and the European Free Trade Association (EFTA) with less friction, and Azure Policy support makes sure every deployment follows the rules from day one.
Oracle AI Database@Azure runs Oracle database services in Azure datacenters, with an Oracle-operated control plane in Oracle Cloud Infrastructure (OCI). So sovereignty spans both clouds: the Azure region you deploy in, the connected OCI tenancy, and how you set up the services around your database.
Use the Azure controls you already trust
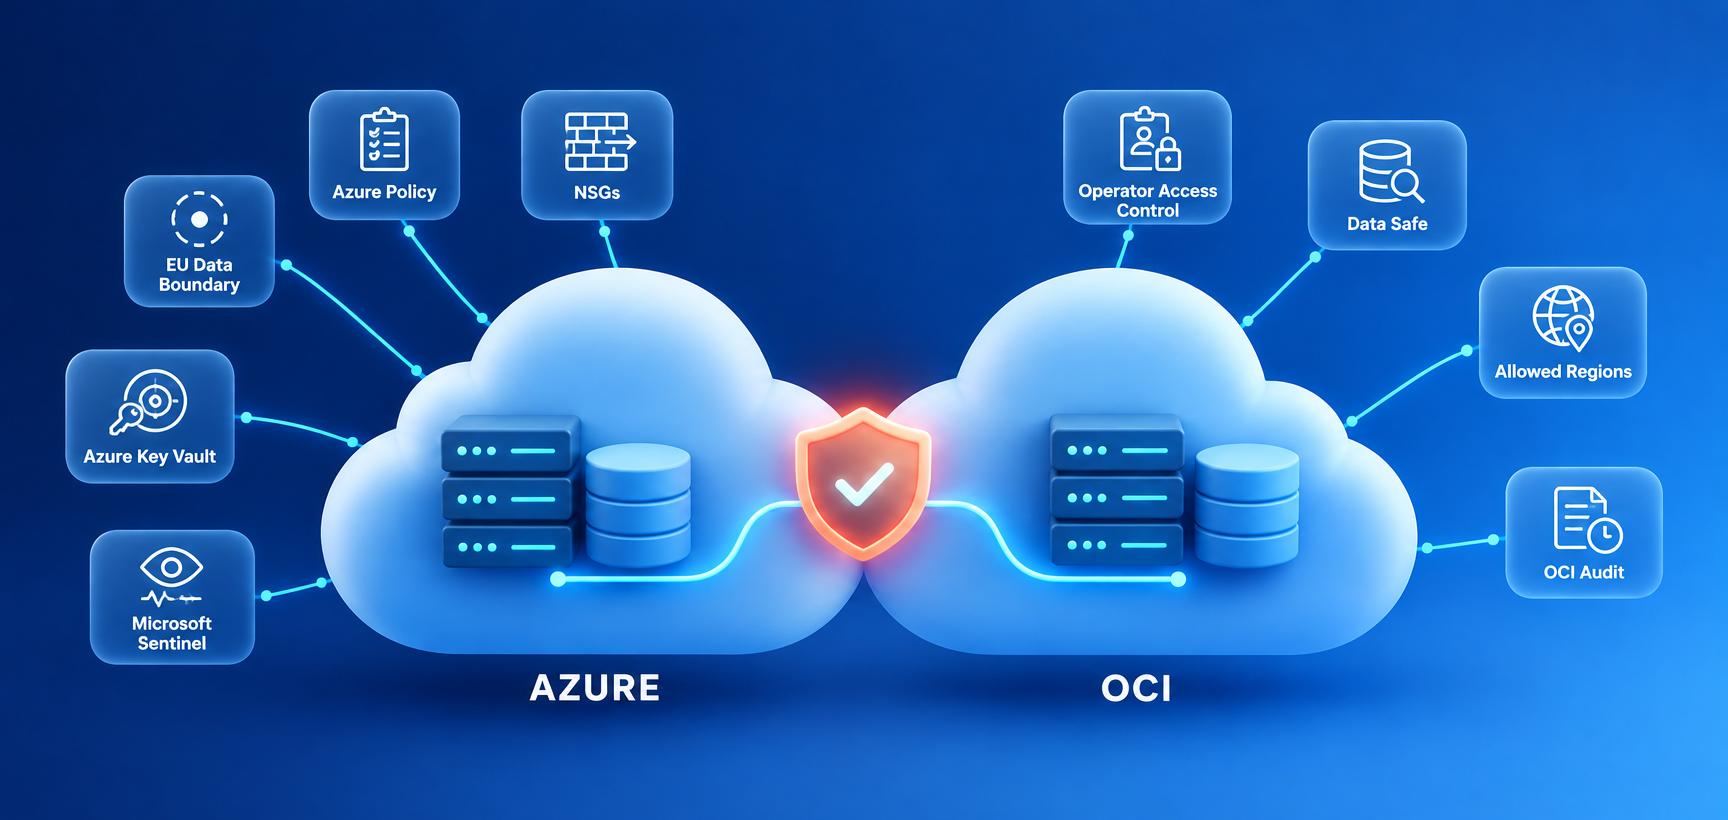
Keep data where it belongs. Oracle databases deploy in the Azure region you choose. The EU Data Boundary covers all EU member states plus the four EFTA countries: Iceland, Liechtenstein, Norway, and Switzerland. Backups stay in Azure when you pick it as the Oracle Database Autonomous Recovery Service location, and Oracle Data Guard between two Azure regions in the same geography keeps standby and replication traffic inside it too.
Own your encryption. Encryption at rest is enforced automatically on Exadata, and connections use Transport Layer Security (TLS). Customer-managed keys work with Azure Key Vault Standard, Premium, and Managed HSM (hardware security module), so you control the key lifecycle. Revoke the key and the database can't use it to start, recover, or restore a backup.
Stay private by default. Oracle AI Database@Azure runs inside your Azure Virtual Network on private IP addresses. With advanced networking on new deployments, your Network Security Groups, user-defined routes, Azure Firewall, and VNet flow logs apply to the database subnet.
Enforce the rules automatically. Azure Policy and Sovereign Landing Zone guidance let you codify requirements such as approved regions or mandatory customer-managed keys, so every Oracle AI Database@Azure deployment stays compliant from day one.
Be ready for an audit at any time. Azure Monitor captures database and infrastructure telemetry, and OCI Audit keeps up to 365 days of administrative activity. Send both to Microsoft Sentinel or the security information and event management (SIEM) tool you already use, and give security teams read-only roles.
Stay in control of the Oracle-managed side
Decide who gets operator access, and see everything they do. Oracle Operator Access Control lets you approve, time-limit, and revoke Oracle operator access to your infrastructure, with keystroke and activity logs and audit reports for every request.
Decide when maintenance happens. For Exadata Database Service on Dedicated Infrastructure, you set and can reschedule the quarterly maintenance window, and Oracle posts monthly security maintenance at least a week ahead.
Control where your tenancy can expand. OCI permissions and an Allowed regions rule in OCI Organizations limit which new regions a tenancy can subscribe to. They don't remove regions you're already subscribed to, so check the home region and existing subscriptions. OCI's Default identity domain also replicates to every subscribed region, so the tenancy's footprint matters even when the database sits inside the EU Data Boundary.
Keep databases running if the control plane is unreachable. If the OCI control plane is unreachable, existing databases keep serving reads and writes. Provisioning, scaling, configuration changes, and maintenance wait until it's back.
Govern your data with Oracle Data Safe. Sovereignty also means knowing what sensitive data you hold and who touches it. Oracle Data Safe, included with Exadata Database Service, finds and classifies sensitive data, masks it for development and test copies, flags risky configurations and users, and audits database activity. It reaches your databases through a secured private endpoint.
Know what the boundary cover. The EU Data Boundary applies within its documented service scope and exceptions. On its own, it doesn't mean every data flow tied to the connected OCI tenancy stays in the EU and EFTA. Where backups, diagnostic and support data, operational data, and your own exports end up, depends on your configuration and the applicable terms.
Oracle subscription, multicloud link, and resource anchor resources are global, so keep personal or confidential information out of their names and labels. Oracle's contract and privacy terms govern Oracle processing and support.
Controls you can't check directly, like back-end operations and physical security, are covered by Oracle and Microsoft assurance reports and certifications, including SOC 1, 2, and 3, ISO 27001, PCI DSS, CSA STAR, and C5. There's no single sovereign certification, so map these to your own requirements.
Plan your deployment
Confirm the supported database service and Azure region, review your OCI tenancy's home region, subscriptions, and identity setup, check where backups and exports land, and register your databases with Data Safe.
Oracle AI Database@Azure gives customers cloud-scale innovation along with the sovereignty assurances their regulators and customers expect.
Learn more
- Read What’s new for Oracle AI Database@Azure at Oracle AI World 2026 | Microsoft Community Hub
- Microsoft EU Data Boundary overview: https://learn.microsoft.com/en-us/privacy/eudb/eu-data-boundary-learn
- Microsoft EU Data Boundary continuing transfers: https://learn.microsoft.com/en-us/privacy/eudb/eu-data-boundary-transfers-for-all-services
- Oracle Database@Azure security and compliance guidance: https://docs.oracle.com/en-us/iaas/Content/database-at-azure/azusr-security-compliance.html
- Oracle Data Safe: https://docs.oracle.com/en/cloud/paas/data-safe/
- OCI organization governance (Allowed regions): https://docs.oracle.com/en-us/iaas/Content/General/organization/add-governance.htm
- Oracle AI Database@Azure compliance programs: https://docs.oracle.com/en-us/iaas/Content/database-at-azure/compliance.htm

 Microsoft