Updated Sep 22, 2026
Version 1.0
TomerBrand Microsoft
 MicrosoftMicrosoft

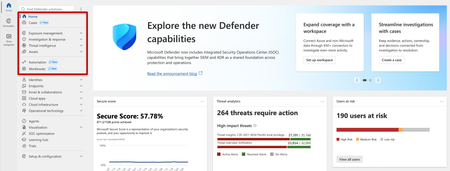
Great direction for Microsoft Defender. The most significant shift here is not simply bringing SIEM and XDR together—it’s creating the foundation for an agentic SOC where security data, context, AI reasoning, and response can operate as a continuous system.
As autonomy increases, governance will become equally important. Agent identity, least privilege, approval boundaries, auditability, and human oversight should be fundamental architectural components.
The future SOC will be less about managing alerts and more about orchestrating trusted decisions and actions at machine speed.
I recently explored this evolution from an architecture perspective as well, focusing on how telemetry, unified security context, specialized AI agents, governed response, and human oversight can come together to build the Agentic SOC. -
https://architectiq.net/articles/the-agentic-soc/