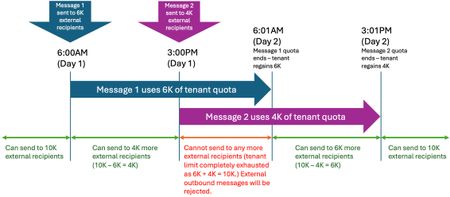
Update Aug 13, 2026: To further strengthen protection against abuse and ensure fair use of Exchange Online resources, we are updating how the Tenant External Recipient Rate Limit (TERRL) quota is cal...
We are a Checkpoint Email Security customer that wants to leverage Checkpoint's inline outbound email scanning. The way it works is it utilizes a transport rule to route outbound email through a connector that sends it to Checkpoint for processing. Checkpoint then re-injects it back into E365 with specific headers set so the transport rule no longer matches and the mail flows out of the normal connector to the recipient's MX record. Microsoft are counting these emails as TWO recipients even though there's only one actual recipient. I did EXTENSIVE analysis of email data that I exported from both Checkpoint and MS Defender Explorer. The Checkpoint data was consistently about half of what MS's TERRL graph shows us. The Explorer data matched the TERRL graph. After digging with Excel and Claude I learned of duplicate entries except for the network message ID. The Internet Message ID was identical. This led me to the understanding that MS is counting these emails twice. This caused significant business impact when outbound emails suddenly stopped working (I've since created a monitoring check to watch for this). Here's another vendor that confirmed the same behavior: https://success.skyhighsecurity.com/docs/mitigate-terrl-impact-while-using-skyhigh-email-dlp
I have cases open with both Checkpoint (their initial response was to disable outbound scanning but that is not acceptable to me) and Microsoft. It's an uphill battle with both because their answers are "buy more licenses" (which we don't need) or "put in another email gateway to offload bulk senders" (which would barely put a dent in our overall traffic.
I don't understand why Checkpoint and other tools that work the same way aren't covered under this from your blog above:
If I send a message to an external recipient but it routes out to a signature service or on-premises for processing, then comes back into Exchange Online to be sent out to the external recipient, will that get counted twice? We were counting these messages more than once earlier. But now we fixed this issue and email is counted only once.
lmt73 I just dealt with this with a client today as well, also using Checkpoint. They're allotted Sent emails allowed is around 18K, yet the highest their running 24 hour amount was around 225. How does this even make sense? Did you get any clarification or work around on this? They were down maybe 2-3 hours today because I was chasing the issue without knowing what the heck was going on. MS support assured me there was an issue with the send limit, but we were around 2% of their limit at any given time.
Those numbers do not make sense, you're right. You can use Explorer in Checkpoint to show outbound emails in the last 24 hours, then export them. If there's a lot, you may need to break it down into smaller time periods. Sounds like you don't deal in high volume though. You can't go directly off of the number shown in the UI because it doesn't factor in emails to multiple recipients. You'll need to export to CSV then ask an AI tool to provide a count of external recipients (you may need to call out that multiple recipients are listed in one cell so it counts them all).
If you have outbound scanning enabled, you can shut it off to see if it helps. But I wouldn't consider that a permanent solution.
Under Policy->Office 365 Mail Threat Detection, at the bottom uncheck Protect (Inline) Outgoing Traffic if it is checked. It will take some time for this to kick in because it manages it via Entra group membership which takes some time to propagate.