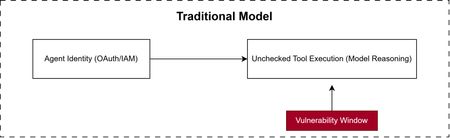
Deploying autonomous AI agents into production without deterministic guardrails introduces severe security risks. When an agent is granted service principal access to execute database operations or financial transactions, system prompts alone cannot serve as a reliable security perimeter. Probabilistic language models remain vulnerable to indirect prompt injection, hallucinated arguments, and unexpected tool calls. Microsoft’s open-source Agent Governance Toolkit (AGT) addresses this gap by providing an inline, sub-millisecond control plane. Sitting directly between model reasoning and tool execution, AGT enforces declarative policies, cryptographically verifies agent identity, and maintains tamper-evident audit logs ensuring that unauthorized agent actions are rendered structurally impossible before code ever executes.
Published Aug 25, 2026
Version 1.0
