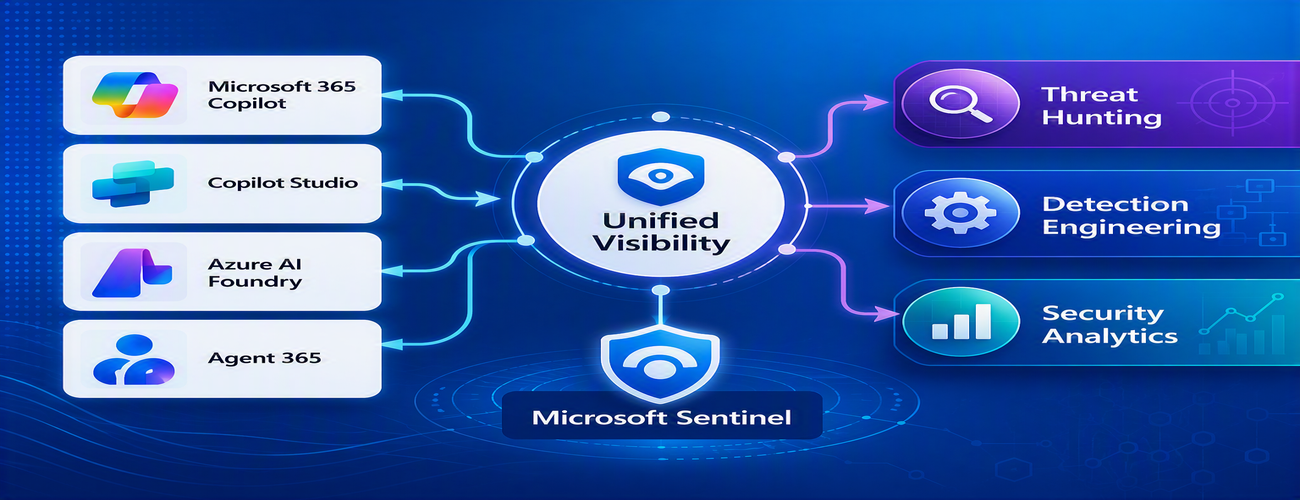
Unified Visibility, Threat Hunting and Detection for Microsoft 365 Copilot, Copilot Studio, Azure AI Foundry and Agent 365
1. Introduction
Enterprise adoption of Generative AI is accelerating rapidly through Microsoft 365 Copilot, Copilot Studio, Azure AI Foundry Agents, Security Copilot, and custom AI agents integrated with business applications.
Unlike traditional SaaS applications, AI agents can:
- Access enterprise data
- Query internal knowledge repositories
- Invoke APIs and MCP tools
- Execute workflows
- Interact with business applications
- Make decisions on behalf of users
While these capabilities improve productivity, they introduce a new attack surface that security teams must monitor and secure.
Common AI threats include:
- Prompt Injection
- Cross Prompt Injection Attacks (XPIA)
- Jailbreak Attempts
- Unauthorized Tool Invocation
- Data Exfiltration through AI Agents
- Agent Identity Abuse
- Excessive Data Access
- Malicious MCP Tool Execution
Traditional SOC monitoring platforms were designed for users, devices, applications and infrastructure—not autonomous AI systems.
To address this challenge, Microsoft provides a comprehensive AI security monitoring framework built around:
- Agent 365 Observability
- Microsoft Agent Identities
- Microsoft Copilot Logs
- Defender XDR
- Defender for AI
- Microsoft Sentinel
Together these components provide end-to-end observability of:
- User prompts
- Agent execution paths
- Tool invocations
- Safety signal detections
- Agent identities
- Security alerts
2. Reference Architecture
AI Security Monitoring Architecture
3. Integration Architecture
Microsoft provides multiple telemetry sources that complement one another.
3.1 Agent Runtime Telemetry
Sentinel Data Connector
Agent 365 Data Connector
Table
UnifiedAgentObservability
Captures runtime behavior of AI agents including:
- User prompts
- Session IDs
- Conversation IDs
- Agent identities
- MCP tool invocations
- Connector invocations
- Tool arguments
- Tool responses
- Request payloads
- Response payloads
- Execution errors
This dataset provides the forensic trail of everything an AI agent performed.
3.2 Agent Governance and Asset Inventory
Sentinel Data Connector
Microsoft Agent Identities
Provides visibility into:
- Agent inventory
- Agent blueprint inventory
- Ownership
- Relationships
- Governance metadata
- Risk context
This allows SOC teams to answer:
- Who owns this agent?
- What permissions does it have?
- Which business unit deployed it?
- Which related agents exist?
3.3 Copilot Audit and Usage Monitoring
Sentinel Data Connector
Microsoft Copilot Logs Connector
Table
CopilotActivity
Provides:
- Copilot usage auditing
- Operational visibility
- User interaction tracking
Useful for governance, compliance and adoption reporting.
3.4 AI Safety Telemetry
Sentinel Data Connector
Microsoft Defender XDR Connector
Table
CloudAppEvents
CloudAppEvents provides AI safety signals such as:
- Prompt Shield detections
- Prompt Injection attempts
- Cross Prompt Injection Attacks (XPIA)
- Jailbreak-related verdicts
- Unsafe prompt classifications
Think of CloudAppEvents as answering:
"Was the prompt malicious?"
3.5 AI Security Alerts
Sentinel Data Connectors
- Microsoft Defender XDR
- Microsoft Defender for Cloud
Tables
- SecurityAlert
- SecurityIncident
Used for:
- AI attack detections
- Security incidents
- Correlated investigation workflows
4. Understanding the Two Most Important AI Tables
CloudAppEvents
Focuses on AI Safety
Questions answered:
- Was Prompt Shield triggered?
- Was this a jailbreak attempt?
- Was XPIA detected?
- Was the prompt suspicious?
UnifiedAgentObservability
Focuses on Agent Runtime Behavior
Questions answered:
- What tool was invoked?
- Which connector executed?
- What arguments were passed?
- What data was returned?
- What actions did the agent perform?
5. Advanced Threat Hunting Scenarios
The Agent365 Observability hunting guide contains several investigation scenarios that can be used directly in Microsoft Sentinel.
Reference: Agent 365 Observability — AI Agent Telemetry Hunting
https://github.com/SCStelz/security-investigator/blob/main/queries/cloud/agent365_observability.md
5.1 Prompt Injection Detection
Detect prompts containing indicators such as:
- Ignore previous instructions
- Reveal system prompt
- Developer mode
- Disregard safety controls
Investigation workflow:
Review Tool Activity
This allows analysts to determine whether a suspicious prompt resulted in downstream actions.
5.2 Session Reconstruction
One of the most powerful capabilities of UnifiedAgentObservability is session reconstruction.
Analysts can correlate:
This creates complete forensic timelines.
5.3 MCP Tool Auditing
Monitor all MCP activity including:
- query_lake
- Graph API tools
- ServiceNow connectors
- SharePoint connectors
- Custom enterprise tools
Questions answered:
- Which tool was used?
- Who triggered it?
- What parameters were supplied?
- What data was returned?
5.4 Sensitive Data Access Monitoring
Monitor AI agent interaction with:
- Employee records
- Customer data
- Financial information
- SharePoint repositories
- HR databases
Useful for identifying:
- Data exfiltration attempts
- Excessive access patterns
- Sensitive data exposure
5.5 Query Lake Monitoring
The GitHub hunting guide introduces monitoring of:
- query_lake
- RunAdvancedHuntingQuery
Analysts can inspect:
- Actual KQL submitted
- Target workspaces
- Data sources queried
- Scope of access
This provides visibility into AI-driven security investigations.
5.6 New Tool Detection
Identify newly observed tool usage.
Examples:
- Unauthorized MCP servers
- Newly registered connectors
- Unapproved tools
- Unexpected integrations
This use case is particularly useful for governance programs.
5.7 Tool Failure Monitoring
Monitor:
- Permission failures
- Connector failures
- Application errors
- Access-denied responses
A sudden increase in failures may indicate:
- Reconnaissance activity
- Misconfiguration
- Privilege abuse attempts
6. Detection Engineering Opportunities
Organizations can create Sentinel Analytics Rules for:
6.1 Prompt Injection Detection
- Developer Mode prompts
- Prompt Override attempts
- System Prompt disclosure requests
6.2 Jailbreak Attempt Detection
- Safety bypass attempts
- Role manipulation prompts
- Instruction override patterns
6.3 Unauthorized Tool Usage
- New MCP tools
- High-risk connectors
- Rare tool executions
6.4 Sensitive Data Access
- HR data queries
- Identity information retrieval
- Large-volume exports
6.5 Agent Identity Abuse
- Ownership changes
- Unexpected agent activity
- Agent-to-agent anomalies
7. Data Lake Exploration and Long-Term Analytics
Because agent telemetry resides within Sentinel Data Lake, organizations can perform:
- Long-term AI investigations
- Historical AI attack analysis
- Agent baselining
- Governance reporting
- Trend analysis
- Tool inventory reporting
Example dashboards include:
- Top Prompt Injection Attempts
- Most Active Agents
- High-Risk MCP Tools
- Agent Ownership Analysis
- AI Security Incidents
- Sensitive Data Access Trends
8. Summary
AI agents represent the next major computing platform, but they also introduce a completely new attack surface.
To effectively secure enterprise AI solutions, organizations require visibility across:
- User interactions
- Agent execution paths
- MCP tool usage
- Prompt safety signals
- Agent identities
- Security detections
Microsoft Sentinel provides this unified view by integrating:
- Agent 365 Observability
- UnifiedAgentObservability
- Microsoft Agent Identities
- Microsoft Copilot Logs
- CloudAppEvents
- Defender XDR
- Defender for AI
By combining AI runtime telemetry with AI safety signals and Defender detections, security teams can move beyond traditional monitoring and build a modern SOC capability for threat hunting, incident response, governance and forensic investigations across Microsoft 365 Copilot, Copilot Studio, Azure AI Foundry and future AI agent ecosystems.
Reference: https://github.com/SCStelz/security-investigator/blob/main/queries/cloud/agent365_observability.md

 Microsoft