Authored by Caroline Perez-Vargas, Michael McReynolds
Introduction
Today at Build, Microsoft showcased Live Migration for Azure confidential computing, a new capability that helps move Intel® TDX Confidential VMs to updated infrastructure with limited interruption while helping protect VM memory and execution context during migration.
Live migration is foundational to reliability: it can improve host availability and help enable routine updates without disruptive maintenance windows. Bringing it to Confidential VMs can reduce planned downtime for platform servicing while preserving the isolation and encryption properties of the underlying confidential computing architecture.
Why this matters: eliminating the maintenance downtime tradeoff
Confidential computing uses hardware-based trusted execution environments (TEEs) to help protect VM memory and execution state from privileged software access, but it has historically made some operational workflows - especially host servicing, OS and BIOS updates - more disruptive. Until now:
-
Most VMs handle host maintenance with a short pause (often seconds), avoiding scheduled windows.
-
Some Confidential VM updates require a planned reboot to apply the latest security patches; these occur multiple times per year and cause minutes of availability loss.
Live migration helps address that tradeoff by improving operational flexibility and availability while supporting the confidentiality and integrity objectives of confidential computing through protected, attested transfers.
Design Goals
Live migration is designed to move a Confidential VM to another host while maintaining protections against privileged software access.
-
Attestation and policy enforcement - the migration flow is designed such that the destination is attested and VM migrates only when the destination satisfies the applicable authorization policy.
-
Confidentiality - migration state is protected during transfer, and the design is intended to reduce the risk of exposure of migration keys to unauthenticated or unauthorized components.
-
Integrity - the design is intended to help ensure the destination receives the correct and current state and that control transfers in a way that supports a one-way switchover.
How it works
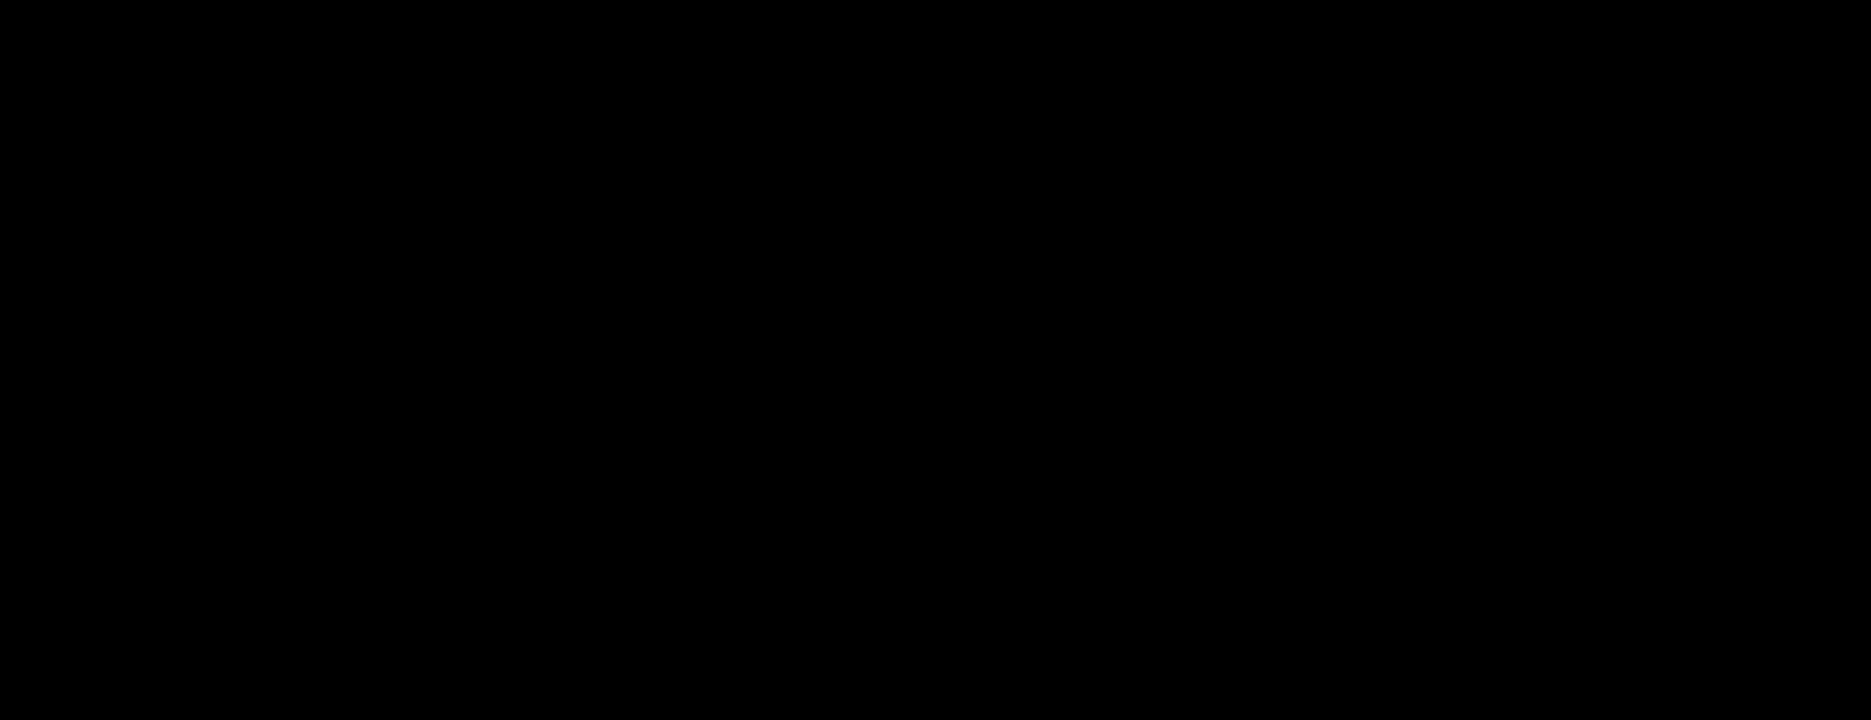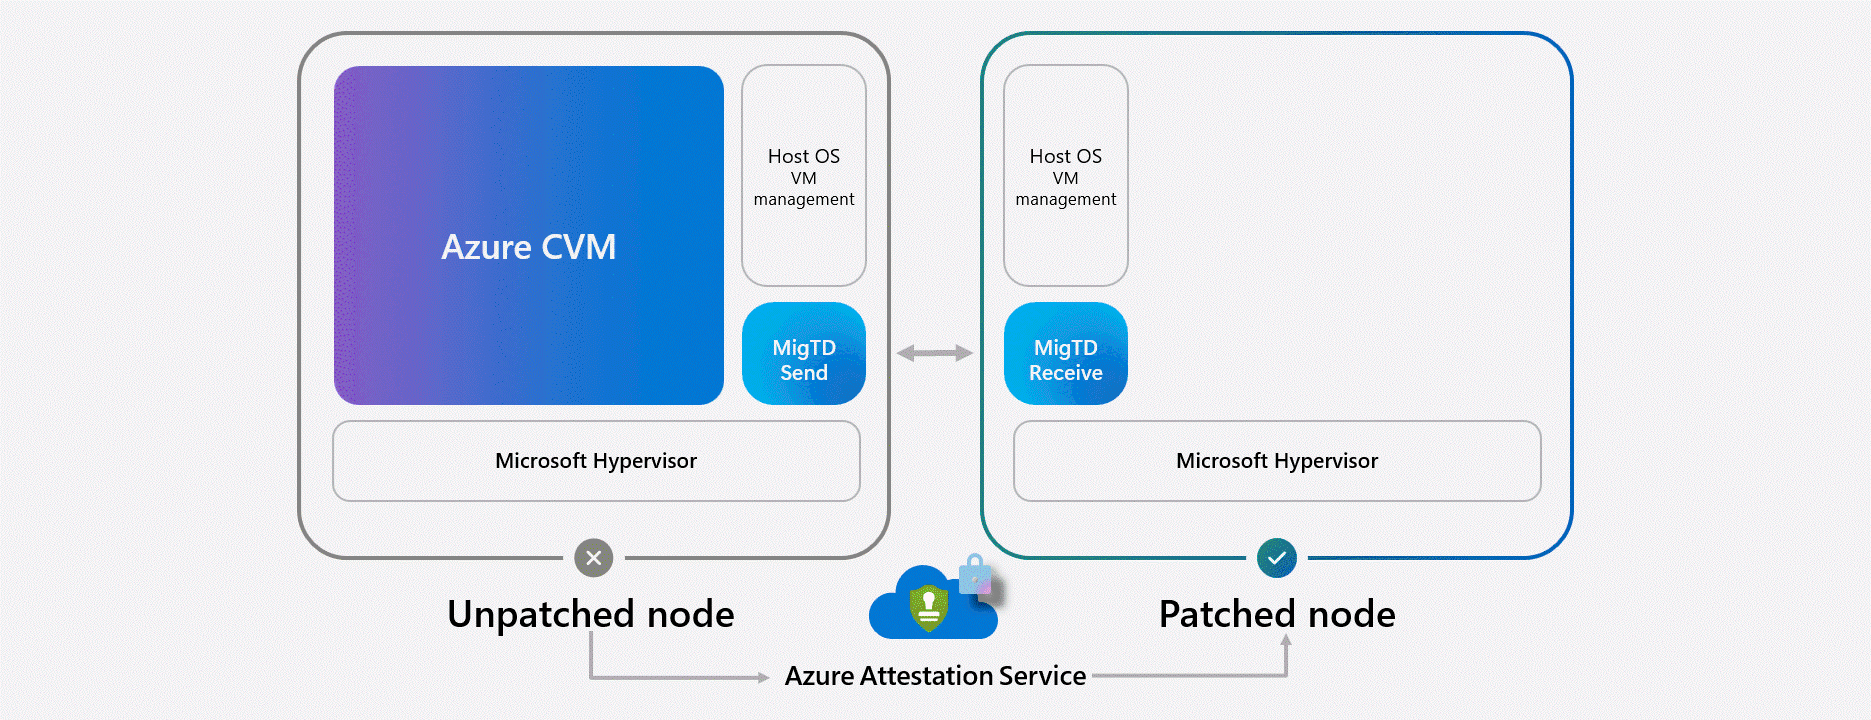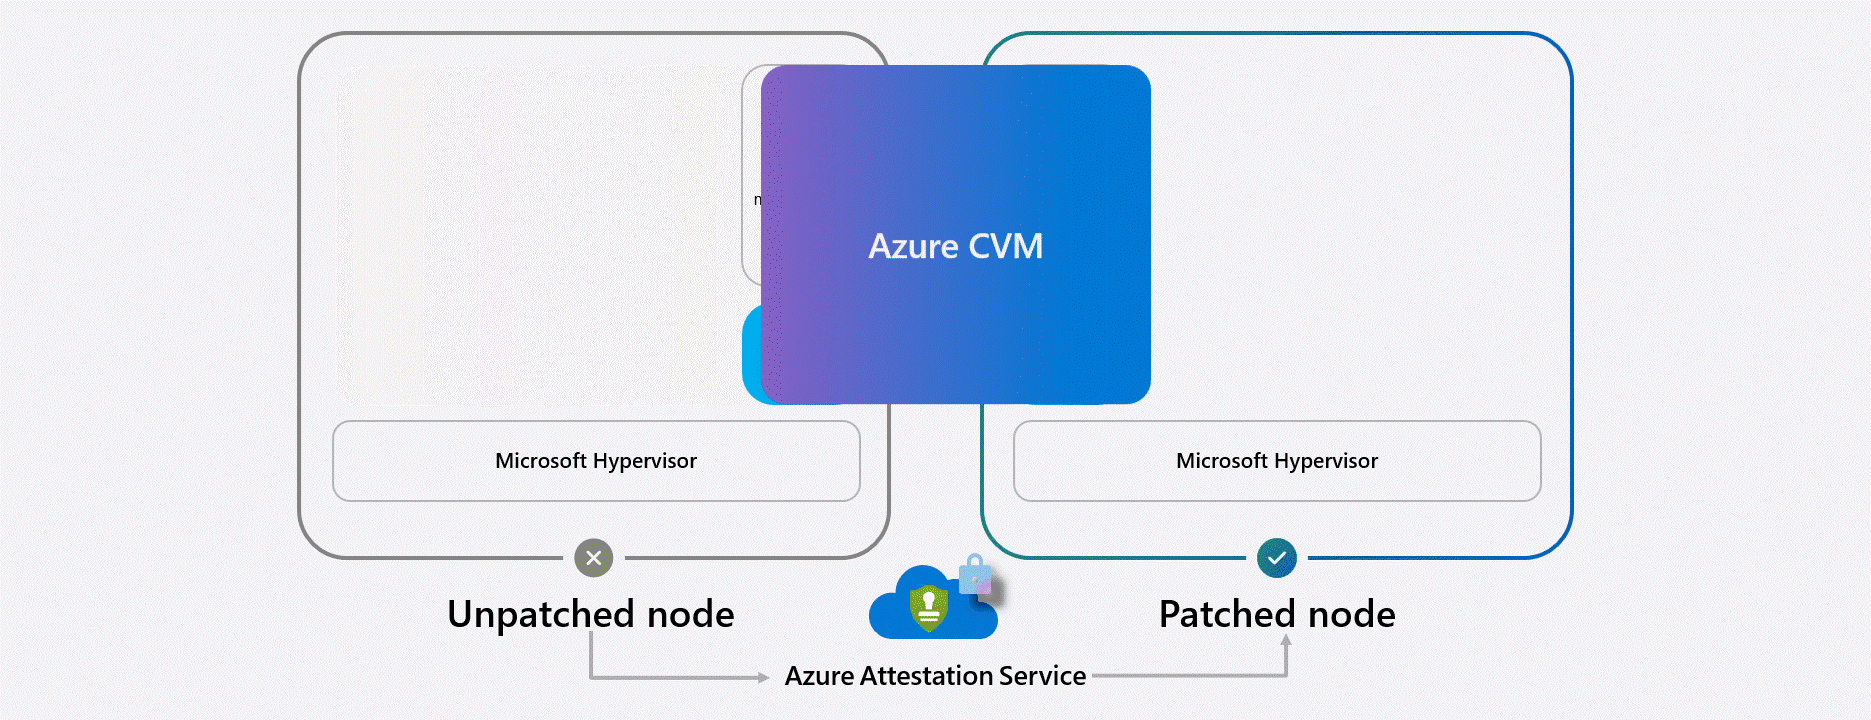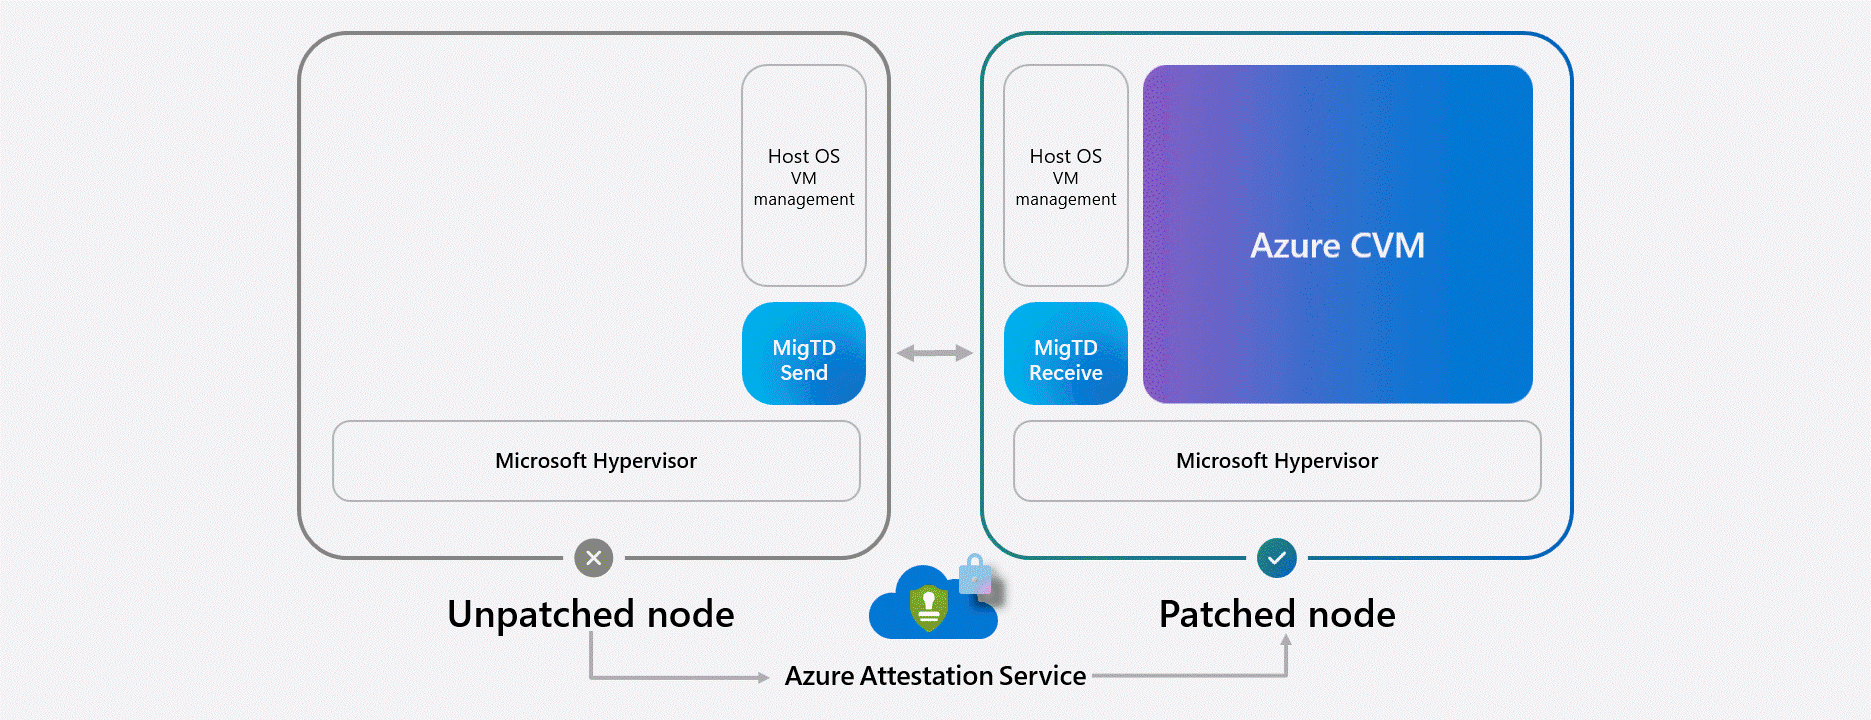
Live migration begins by attesting the destination host and ensuring it is compliant. After verification, the platform transfers memory and execution context over an encrypted channel using iterative copying: most pages are sent while the VM continues running, followed by a brief switchover pause to send the remaining deltas and resume the VM on the new host.
The Steps Involved: seamless migration, with attestable proof
-
Confirm the VM is eligible to migrate - validate the source environment and migration request.
-
Attest and authorize the destination - verify that the target host satisfies required measurements and policy before migration state is transferred.
-
Establish a protected session - perform an authenticated key exchange and derive ephemeral keys associated with the attested destination.
-
Transfer VM state - stream memory and execution state while securely tracking changes made during migration.
-
Complete the final handoff - briefly pause the VM, send the remaining deltas, enforce the one-way switchover, and resume on the destination.
Azure’s control plane coordinates the workflow, while MigTD and the TDX module help enforce attestation, key exchange, and the one-way handoff within the confidential computing architecture.
MigTD and protecting memory during transfer
Under the hood, Intel's TDX live migration architecture introduces the MigTD, a small, open-sourced, attested module which makes migration policy decisions for the confidential VM. MigTD helps by verifying the destination against the migration policy. Since MigTD is in Confidential Trust Boundary (CTB), its measurements are included as part of the Confidential VM attestation evidence which can be remotely verified.
During transfer, the confidential computing architecture is designed to help protect a Confidential VM’s private memory and execution state. Migration must move both the memory contents and page visibility state (private vs. shared), both of which can change while the VM is running. For memory contents, CPU and device accesses can modify memory during migration, so the architecture tracks changes using secure page-table dirty-bit mechanisms in the CPU and IOMMU/SMMUs. For page state, because memory pages can transition between private and shared during migration, the architecture captures and serializes that metadata with the transfer so the destination can reconstruct the intended state.
Demo
Industry Collaboration + Next Steps
Live Migration for Azure confidential computing builds on a long-standing collaboration between Microsoft and Intel to advance Confidential VMs in Azure. In 2024, the teams completed a multi-month security review of the initial architecture and published a joint security report detailing findings and mitigations. Building on that work, Microsoft and Intel collaborated to extend the Intel TDX architecture for Azure’s higher-performance confidential VM scenarios, including support for accelerated devices such as Azure Boost.
This capability will roll out gradually for DC/ECesv6 and DC/ECedsv6-series; further details will be shared ahead of GA. Questions or feedback? Email azconfidentialpm@microsoft.com.

 Microsoft