windows 10
19 Topics
Windows AutoPilot - Hardware Hash
Hi all, I'm running a PowerShell script to generate hardware hashes in order to enroll devices into Intune Autopilot. I followed the instructions from the official MS site, https://docs.microsoft.com/en-us/windows/deployment/windows-autopilot/add-devices The below command runs successfully but the only problem is that when trying to upload to Intune I get an error that the format is incorrect. I then have to manually update the CSV to separate each comma and upload. We have hundreds of devices and, needless to say, it's incredibly tedious to do this for every single one. I can't find a forum that describes a way to edit the script to do this for me. Does anyone have an idea of how to do this, if even possible? md c:\\HWID Set-Location c:\\HWID Set-ExecutionPolicy -Scope Process -ExecutionPolicy Unrestricted Install-Script -Name Get-WindowsAutoPilotInfo Get-WindowsAutoPilotInfo.ps1 -OutputFile AutoPilotHWID.csv Any help would be appreciated. Kind regards,64KViews0likes5Comments
Disable Windows Hello for Business
I am an admin, and attempting to disable "Windows Hello for Business" also referred to as 2-step authentication. From what I gather, this option is set as "disabled" by default. I confirmed this. However Whenever I join a device to Azure AD, it is always prompted with "Windows Hello" and to create a pin. Where can I find the option that allows me to disable this?45KViews0likes7Comments
How to logon with Azure AD credentials on a Windows 10 device with MFA enabled
Hi together, maybe one of you have got the same requirements and run into the same problem. situation: Windows 10 enterprise or windows 10 s Microsoft Intune Cloud (EMS) Microsoft Multi-Factor Authentication (MFA) on-premises handled by ADFS (internal no mfa, external (wap) force mfa) Company Wifi protected with certificates Credentials from Azure AD Problem 1: As far as I have found, Intune is only able to deploy user certificates (SCEP profile) for wifi on windows devices. This causes us that you initially can only logon with your azure ad credentials to a windows machine if you have plugged in the company network or you have a public wifi connection with no authentication, so that you can connect to a wifi on the logon screen. Does anyone managed to deploy client certificates with Intune? Problem 2: As mentioned above we use MFA on-premises and it’s handled by adfs. If a user authenticates from external (over wap) we force mfa on adfs side. This is fine for web applications and other apps but it seems that windows logon cannot handle mfa request and therefore it fails. Does anyone know if this can be achieved somehow that this scenario works? Could this be handled by conditional access? The goal should be that we can use a windows 10 enterprise or windows 10 s device with azure ad credentials which is authenticated to our company wifi network at logon screen already and that we can use multi-factor authentication somehow. Thanks in advance for any input!14KViews0likes3CommentsAutopilot OOBE stuck at "Sign in With Microsoft" page after authenticating on company specific page
I'm trying to set up intune for windows autopilot, but having trouble. I have the policies configured for our Hybrid AADJ environment, and when starting OOBE on a computer I do get prompted to log in at a screen showing our company specific info, but once I authenticate there (using either password or phone sign in) it comes up to an unbranded "sign in with microsoft" screen, asking me to sign in to my work or school account. On this screen, I can enter a username, but the Next button doesn't do anything. I'm just stuck on that screen. What could be causing this behavior? The computer is running W10 v1909 pro, if that matters. One of the intune policies assigned to it should upgrade it to Enterprise, but I'm not even getting that far.12KViews0likes7Comments
Intune enterprise wi-fi profile for windows - clients stuck on pending
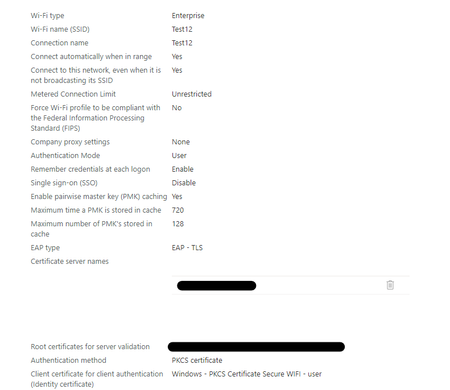
Hi everyone, I opened a ticket with Microsoft but maybe someone already encountered this and can help. We deployed a .1x wireless network and until last Thursday it worked perfectly. here is the setup we use: On Thursday I renamed all the profiles associated with the wireless network to reflect for which clients this profile is for and what it does. Apparently this resulted in deleting the wireless profile from the clients... I decided to recreate the policies of the trusted root certificate profile, PKCS certificate profile and the wireless profile but it still didn't work. The picture above is another wireless network I deployed to test whether the problem is with the wireless name but the new profile also didn't deploy. I also deployed a basic network which deployed successfully. Worth noting but maybe unrelated, We blocked the public store and I checked the policy to make sure it was deployed successfully. any ideas? Rahamim.Solved9.1KViews0likes6Comments
Windows 10 22H2 are not being offered by Intune
Hi everyone, All my devices are the same make/model(Dell Latitude 3520), Windows 10, same device group and Intune MEM/AAD joined. I have set Update Ring to delivery Quality/Feature updates automatically on Intune. Some devices are not being offered the Feature update 22H2 but are receiving the Quality updates normally. If I check updates it says Device updated. This is affecting more than 40 devices. Is anyone have any idea what can be done?7.9KViews1like4CommentsCustom Policy CSP for NCSC Guidance for Windows 10
The NCSC Guidance for Deploying Intune managed Windows 10 clients (https://www.ncsc.gov.uk/guidance/eud-guidance-windows-10-1803-mobile-device-management) lists two custom OMA-URI settings that block unwanted devices from being installed. ./Device/Vendor/MSFT/Policy/Config/DeviceInstallation/PreventInstallationOfMatchingDeviceIDs ./Device/Vendor/MSFT/Policy/Config/DeviceInstallation/PreventInstallationOfMatchingDeviceSetupClasses Unfortunately the policy JSON that the NCSC supply is missing these settings. I tried to create the SyncML for both IDs using guidance from the Internet but I get a catastrophic failure error message in the logs and the policies do not apply. The settings that I have used are ./Device/Vendor/MSFT/Policy/Config/DeviceInstallation/PreventInstallationOfMatchingDeviceIDs <enabled/> <data id="DeviceInstall_IDs_Deny_List" value="PCI\CC_0C0A"/> <data id="DeviceInstall_IDs_Deny_Retroactive" value="1"/> ./Device/Vendor/MSFT/Policy/Config/DeviceInstallation/PreventInstallationOfMatchingDeviceSetupClasses <enabled/> <data id="DeviceInstall_Classes_Deny_Retroactive" value="1"/> <data id="DeviceInstall_Classes_Deny_List" value="{d48179be-ec20-11d1-b6b8-00c04fa372a7}{7ebefbc0-3200-11d2-b4c2-00a0C9697d07}{c06ff265-ae09-48f0-812c-16753d7cba83}{6bdd1fc1-810f-11d0-bec7-08002be2092f}"/> Has anyone successfully applied these settings using a custom device configuration policy? If so where am I going wrong? Any assistance will be gratefully receivedSolved7KViews0likes8CommentsDeploy reset Windows 10 OD via AutoPilot
When Windows 10 machines are delivered from the manufacturer, they have a lot of "bloatware" installed. What is the best method using Windows AutoPilot to remove all these superfluous apps and deploy a basic "vanilla" build of Windows 10 to users?5KViews1like1CommentWindows Hello for Business implementation
Hi, For a couple of days now we've introduced Windows Hello for Business (WHfB) to a subset of test devices from within Intune. Everything works as expected except for one thing I guess: When someone tries to logon with a non-enterprise account (eg. @live.nl) in Teams, and/or Onedrive, the machine is prompting to authenticate with WHfB. Am I missing something? Why is this happening and how can we prevent this? Any thoughts are welcome.4.4KViews0likes8Comments
Windows 365 Administrator built-in role getting 401 unauthorized when enrolling devices
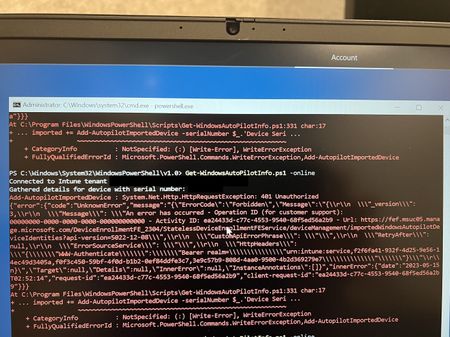
I'm trying to enroll new devices using the get-windowsautopilotinfo script. For this task, I'm trying to use a user assigned with the built-in role "Windows 365 Administrator", which is a new role. https://learn.microsoft.com/en-us/azure/active-directory/roles/permissions-reference#windows-365-administrator Based on the above article, the role has the "microsoft.directory/devices/create" action, with description "Create devices (enroll in Azure AD)". It even says the role can "Enroll and manage devices in Azure AD, including assigning users and policies". But when I execute get-windowsautopilotinfo -online in Windows 10 OOBE Powershell, and login with the Windows 365 Admin. user, I encounter the following error: add-autopilotimportedevice: system.net.http.httprequestexception: 401 unauthorized Anyone else encounter the same problem? Should I just wait a few months for Microsoft to fix the role? 🙂 I've tried waiting 24 hours after assigning the role, same error. It might be unlikely a delay-related issue, a few seconds after assigning the Intune Admin. role, the script executes flawlessly. I've also tried 2 users, 2 separate devices, same error.3.2KViews0likes1Comment