security
664 TopicsStrengthening Security in SharePoint Document Libraries: 5 Essential Best Practices
SharePoint Online has become a critical platform for storing, managing, and collaborating on documents across Microsoft 365 environments. Its flexibility and ease of access make it invaluable to modern organisations. However, if document libraries are not properly managed, businesses can face risks such as unauthorised access, accidental sharing of sensitive data, and compliance challenges. Effective SharePoint security is not about restricting productivity. It is about creating a secure framework that allows teams to collaborate confidently while ensuring business information remains protected. This article was written by https://www.bridgeall.com/a leading https://www.bridgeall.com/microsoft-365-consultancy/sharepoint/offering https://www.bridgeall.com/microsoft-365-consultancy/sharepoint/sharepoint-document-management-systems-implementation/ Five Ways to Improve SharePoint Document Library Security Limit Access Using Role-Based Permissions One of the most effective ways to secure SharePoint is by restricting access to only those who genuinely need it. Many organisations grant broad permissions across sites, creating unnecessary exposure. Following a least-access approach ensures users receive only the permissions required for their responsibilities. Rather than assigning permissions to individual files and folders, consider using Microsoft 365 Groups or SharePoint Security Groups to manage access centrally. This not only improves governance but also makes ongoing administration significantly easier. Review and Restrict External Sharing External collaboration is often necessary, but it can also become a source of data leakage if not controlled appropriately. Review sharing settings at both the tenant and site level to ensure they align with your organisation's security requirements. Good practices include: Preventing anonymous sharing links for libraries containing confidential information. Allowing access only to verified external users where appropriate. Applying expiry dates to shared links so access is automatically revoked after a defined period. Regularly auditing active external sharing relationships. By tightening these controls, organisations can reduce the likelihood of sensitive information being exposed outside the business. Protect Content with Sensitivity Labels Protecting the library itself is important, but protecting the documents within it adds another layer of security. Microsoft Purview Sensitivity Labels enable organisations to categorise content according to its sensitivity and automatically apply protection measures. Depending on the classification, labels can: Encrypt files. Restrict downloading, printing, or copying. Display visual markings such as headers, footers, or watermarks. Maintain protection even when a document is shared or moved outside SharePoint. This approach helps ensure security travels with the information rather than relying solely on where it is stored. Strengthen User Authentication Document-level security should always be backed by strong identity protection measures. Multi-Factor Authentication (MFA) remains one of the most effective ways to prevent unauthorised access resulting from compromised credentials. Combining MFA with Microsoft Entra Conditional Access policies provides even stronger protection. For example, organisations can: Block access from unmanaged devices. Restrict downloads on non-compliant endpoints. Trigger additional verification requirements for sign-ins from unfamiliar locations. Apply risk-based access controls based on user behaviour. These safeguards help ensure only trusted users and devices can access critical information. Continuously Monitor and Review Access Security is not a one-off project. Permissions and risks evolve over time, making ongoing monitoring essential. Microsoft Purview auditing capabilities provide visibility into activities such as file sharing, downloads, edits, deletions, and permission changes. Regular access reviews help identify: Outdated permissions. Dormant guest accounts. Excessive access rights. Unnecessary group memberships. Routine governance reviews help maintain a secure SharePoint environment and reduce the risk of privilege creep. Building a Secure and Collaborative SharePoint Environment A well-secured SharePoint platform should balance protection with usability. Organisations that invest in strong governance, identity controls, information protection, and ongoing monitoring are better positioned to support collaboration without compromising sensitive business data. By implementing these best practices, businesses can significantly reduce security risks while ensuring employees continue to work efficiently within Microsoft 365. At Bridgeall we offer a range of https://www.bridgeall.com/microsoft-365-consultancy/sharepoint/sharepoint-document-management-systems-implementation/ that help you build and maintain a secure platform of SharePoint document librarires.152Views0likes0Comments
SharePoint security broken between Microsoft 365 group and SharePoint group
Hi, Users are giving Member privilege through Teams, which gave them Member privilege in the Member SharePoint group. All good for 99% of the company. PROBLEM : I have 4 users without access to the SharePoint by this method. Security is not broken between Microsoft 365 Group and SharePoint group and is working fine for everybody else. Strangely, I saw that these 4 users are members of more than 1500+ Microsoft 365 Group, since they have been in the business for a long time and touch many projects here). I heard the limit is 7000 but they still have problem. Using the "Check permission", I got "None" for these people, but "Edit - Given through the XYZ Member group" for every other people in the Microsoft 365 Group. Any advice ? Thanks ! Patriccote303Views1like4CommentsExternal Users Unable to Access Microsoft List Form
We have created a Microsoft List and are using the default Microsoft Lists Form for data entry / intake form. Internal users can access the form URL and submit items successfully. However, external users are unable to access the form link, even though they have been granted Contribute permissions to the SharePoint list. External users can: Access the list Create new items using the + New button Edit items based on their permissions However, they cannot access the dedicated Microsoft Lists Form URL and getting following error. This link is only available to internal users. This link is not available to you. Our requirement is to allow external users to: Open the Microsoft Lists Form URL View the form Submit new items without providing additional access beyond what is required for form submission, and without using Microsoft Forms. Is guest/external user access to the Microsoft Lists Form experience supported? If so, what configuration or permissions are required to enable external users to access and submit items through the form URL?Solved498Views0likes3Comments
Recycle Bin and Site Content Hidden for Site Members and Site Visitors
I posted this before but made a mistake with my write up, so I am reposting. I have a requirement that the Recycle bin and Site Contents should be be hidden from the Site Members and Site Visitors. Please how can I achieve this because the Server Infrastructure activation is not working for me. Any workarounds? Please help244Views0likes1CommentRecycle Bin and Site Content Hidden for Site Members and Site Visitors
I have a requirement that the Recycle bin and Site Contents should not be be hidden from the Site Members and Site Visitors. Please how can I achieve this because the Server Infrastructure activation is not working for me. Any workarounds? Please help362Views0likes2CommentsDynamic Mandatory Fields
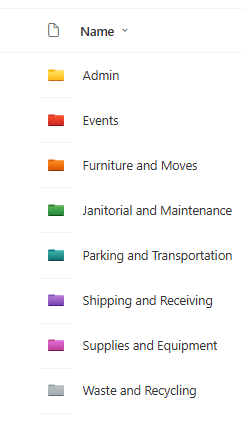
In a SharePoint library, I have folders which are = a. Admin b. Events c. Furniture and Moves d. Janitorial and Maintenance e. Parking and Transportation f. Shipping and Receiving g. Supplies and Equipment h. Waste and Recycling I have Meta data across the library whose data type are all choices and are: a. Document Type = Contract, Financial, planning b. Building = Gym, Garage, Heating c. Asset Category = Office, Playground d. Fiscal Year = FY23, FY24, FY25, FY26, FY27 e. Vendor = Maple Leaf, Canadian Tire, Home Depot f. Status = Active, Pending, Not Active g. Retention Label = 3 years, 5 years h. Service Type = Admin, Events, Furniture and Moves, Janitorial and Maintenance, Parking and Transportation, Shipping and Receiving, Supplies and Equipment, Waste and Recycling Service Type and Retention Label are mandatory fields, with the Rule below for all the files in the various folders: IF Folder Name = Admin, then Service Type = Admin and Retention Label = 5 years; the mandatory fields should be Document Type, Status and Fiscal Year IF Folder Name = Events, then Service Type = Events and Retention Label = 3 years; the mandatory fields should be Document Type, Status and Fiscal Year, Building and Vendor IF Folder Name = Furniture and Moves, then Service Type = Furniture and Moves and Retention Label = 3 years; the mandatory fields should be Document Type, Status and Building IF Folder Name = Janitorial and Maintenance, then Service Type = Janitorial and Maintenance and Retention Label = 3 years; the mandatory fields should be Document Type, Status and Fiscal Year IF Folder Name = Parking and Transportation, then Service Type = Parking and Transportation and Retention Label = 3 years; the mandatory fields should be Document Type, Status and Fiscal Year IF Folder Name = Shipping and Receiving, then Service Type = Shipping and Receiving and Retention Label = 3 years; the mandatory fields should be Document Type, Status IF Folder Name = Supplies and Equipment, then Service Type = Supplies and Equipment and Retention Label = 3 years; the mandatory fields should be Document Type, Status and Fiscal Year IF Folder Name = Waste and Recycling, then Service Type = Waste and Recycling and Retention Label = 3 years; the mandatory fields should be Document Type, Status and Vendor I have used Column Default Value Settings for SharePoint to display Auto-Display the Service Type and Retention Label, but I cannot seem to perform the conditional mandatory fields using Validations setting for the other requirements. Please help362Views0likes1CommentSharePoint Library Help Needed
I have a SharePoint Library where I would like to implement these requirements below and would appreciate your advise: Folders were created at the library level, which looks like the image below. I do not want people to be able to create any folders or upload documents or folders at the library level, but rather only when they open the folders. I have disabled folder creation and created a PowerApps form, so that users can only upload document, edit documents, view details of the documents when they open any of the folders., but I cannot seem to find the Power Apps form when I open any of the folders and try to upload a document or view a document or edit the document details. 2. I have a choice column called Fiscal Year which has options as = FY22, FY 23, FY24, FY25, FY26. By March 2026, I would like to create an automate flow which will auto create FY27 and remove FY22 from the choice, so that the choice column is always limited to only 5 years.236Views0likes3Comments
SharePoint permission change notifications not working
Problem: Trying to get Microsoft Graph change notifications when permissions change on SharePoint/OneDrive drive items (sharing, inheritance breaks, access grants/revocations). Using Prefer: includesecuritywebhooks on subscription creation as documented subscription creates successfully, but the header appears to be silently ignored (notificationQueryOptions is always null in response, Preference-Applied header is always empty). What works: Regular content change notifications fire fine. What doesn't: Zero security notifications on any permission change. Subscription request: POST https://graph.microsoft.com/v1.0/subscriptions Prefer: includesecuritywebhooks { "changeType": "updated", "notificationUrl": "https://...", "resource": "drives/{driveId}/root", "expirationDateTime": "2026-06-12T00:00:00Z" } Permissions (all with admin consent): Files.Read.All, Files.ReadWrite.All, Sites.Read.All, Sites.FullControl.All, Directory.Read.All Already tried: Both v1.0 and /beta endpoints same result Every relevant permission combination But the official document says it should work: Link to documentation: https://learn.microsoft.com/en-us/onedrive/developer/rest-api/concepts/scan-guidance?view=odsp-graph-online#receiving-webhook-notifications-for-security-events Any working example or confirmation of current status would be extremely helpful. Happy to share more details or test specific configurations.67Views0likes0Comments
OneDrive site locked NoAccess for 1 month - Ticket #2605040040008376 - No resolution
I have an open Microsoft support ticket for over 1 month with no resolution. Hoping the community or a Microsoft engineer can help. SITUATION: A departed user (deleted over a year ago) had a OneDrive site that was accessible to other users until recently. Since then the site is completely inaccessible to everyone including admins. Current Status: Active LockState: NoAccess WHAT WE TRIED: - Set-SPOSite -LockState Unlock → command succeeds but site stays blocked - Set-SPOUser -IsSiteCollectionAdmin $true → fails with "Access to this Web site has been blocked" - User does not exist in Entra ID, Deleted Users, or Deleted Sites ROOT CAUSE IDENTIFIED: Site was under a 5-year retention policy in Microsoft Purview. Policy showed error "SiteInReadonlyOrNotAccessible" for this OneDrive. We removed the OneDrive from the policy exceptions but the site remains locked. This appears to be a deadlock: - Site is locked so retention policy cannot detach - Retention policy prevents site from being unlocked No eDiscovery holds found on the site. Microsoft support has been unable to resolve this for 1 month. Does anyone know how to break this deadlock?Solved159Views0likes3Comments