private
9 Topics
Azure Key Vault Replication: Why Paired Regions Alone Don’t Guarantee Business Continuity
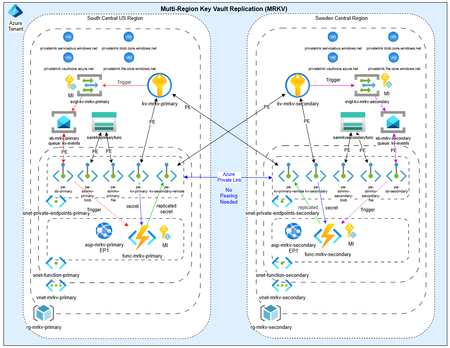
As customers modernize toward multi‑region architectures in Azure, one question comes up repeatedly: “If my region goes down, will Azure Key Vault continue to work without disruption?” The short answer: it depends on what you mean by “work.” Azure Key Vault provides strong durability and availability guarantees, but those guarantees are often misunderstood—especially when customers assume paired‑region replication equals full disaster recovery. In reality, Azure Key Vault replication is designed for survivability, not uninterrupted write access or customer‑controlled failover. This post explains: How Azure Key Vault replication actually works (per Microsoft Learn) Why paired‑region failover does not equal business continuity Two reference architectures that implement true multi‑region Key Vault availability, with Terraform How Azure Key Vault Replication Works (Per Microsoft Learn) Azure Key Vault includes multiple layers of Microsoft‑managed redundancy. In‑Region and Zone Resiliency Vault contents are replicated within the region. In regions that support availability zones, Key Vault is zone‑resilient by default. This protects against localized hardware or zone failures. Paired‑Region Replication If a Key Vault is deployed in a region with an Azure‑defined paired region, its contents are asynchronously replicated to that paired region. This replication is automatic and cannot be configured, observed, or tested by customers. Microsoft‑Managed Regional Failover If Microsoft declares a full regional outage, requests are automatically routed to the paired region. After failover, the vault operates in read‑only mode: ✅ Read secrets, keys, and certificates ✅ Perform cryptographic operations ❌ Create, update, rotate, or delete secrets, keys, or certificates This is a critical distinction. Paired‑region replication preserves access — not operational continuity. Why Paired‑Region Replication Is Not Business Continuity From a reliability and DR perspective, several limitations matter: Failover is Microsoft‑initiated, not customer‑controlled No write operations during regional failover No secret rotation or certificate renewal No way to test DR Accidental deletions replicate No point‑in‑time recovery without backups Microsoft Learn explicitly states that critical workloads may require custom multi‑region strategies beyond built‑in replication. For many customers, this means Azure Key Vault becomes a single‑region dependency in an otherwise multi‑region application design. The Multi‑Region Key Vault Pattern The two GitHub repositories below implement a common architectural shift: Multiple independent Key Vaults deployed in separate regions, with customer‑controlled replication and failover. Instead of relying on invisible platform replication, the vaults become first‑class, region‑scoped resources, aligned with application failover. Solution 1: Private, Locked‑Down Multi‑Region Key Vault Replication Repository: 👉 https://github.com/jclem2000/KeyVault-MultiRegion-Replication-Private Architecture Highlights Independent Key Vault per region Private Endpoints only No public network exposure Terraform‑based deployment Controlled replication using Event Based synchronization What This Enables ✅ Full read/write access during regional outages ✅ Continued secret rotation and certificate renewal ✅ Customer‑defined failover and RTO ✅ DR testing and validation ✅ Strong alignment with zero‑trust and regulated environments Trade‑offs Higher operational complexity Requires automation and application awareness of multiple vaults Solution 2: Low‑Cost Public Multi‑Region Key Vault Replication Repository: 👉 https://github.com/jclem2000/KeyVault-MultiRegion-Replication-Public Architecture Highlights Independent Key Vault per region Public endpoints Minimal networking dependencies Terraform‑based Controlled replication using Event Based synchronization Optimized for simplicity and cost What This Enables ✅ Full read/write availability in any region ✅ Clear and testable DR posture ✅ Lower cost than private endpoint designs ✅ Suitable for many non‑regulated workloads Trade‑offs Public exposure (mitigated via firewall rules, RBAC, and conditional access) Not appropriate for all compliance requirements Requires automation and application awareness of multiple vaults Azure Native Replication vs Customer‑Managed Multi‑Region Vaults Capability Azure Paired Region Multi‑Region Vaults Read access during outage ✅ ✅ Write access during outage ❌ ✅ Secret rotation during outage ❌ ✅ Customer‑controlled failover ❌ ✅ DR testing ❌ ✅ Isolation from accidental deletion ❌ ✅ Predictable RTO ❌ ✅ Azure Key Vault’s native replication optimizes for platform durability. The multi‑region pattern optimizes for application continuity. When to Use Each Approach Paired‑Region Replication Is Often Enough When: Secrets are mostly static Read‑only access during outages is acceptable RTO is flexible You prefer Microsoft‑managed recovery Multi‑Region Vaults Are Recommended When: Secrets or certificates rotate frequently Applications must remain writable during outages Deterministic failover is required DR testing is mandatory Regulatory or operational isolation is needed Closing Thoughts Azure Key Vault behaves exactly as documented on Microsoft Learn—but it’s important to be clear about what those guarantees mean. Paired‑region replication protects your data, not your ability to operate. If your application is designed to survive a regional outage, Key Vault must follow the same multi‑region design principles as the application itself. The reference architectures above show how to extend Azure’s native durability model into true operational resilience, without waiting for a platform‑level failover decision.908Views0likes1CommentPrivate Channel Message ID
For Power Automate approval function, I'd like to post a message or adaptive card to Private Channel as reply, so I need to check message ID in private channel. But option of "copy message link" in private channel as per policy, so I need alternative way to get message ID such as PowerShell etc. If anyone has an idea how to get message ID of private channel, could you please kindly advise a way, thx.1.5KViews0likes0CommentsShow users his posts only in a channel ?
Hello, Is it possible to create a channel that users can only see their posts ? the idea is we want to make a channel that users can report safety concerns but we dont want everyone in channel to see these. Is that something can be done ?2.9KViews1like2Comments
OneNote in MS teams, having both personal notes and public notes
Hi, could anyone give some suggestions about How can use OneNote in MS teams (or any other application in Teams) can have personal notes (only the owner can write and read ) and Public notes, which all people in the team can view and edit? and for public part, open also can have 2 types, 1. owner can write others can only read, 2. every one in the team can edit. especially, if the team/channel having a Virtue meeting. How can we also have private notes and public notes? Thank you!Solved4.7KViews1like3Comments
Private Channel available/enabled globally in TAC - Nothing in client. Wait for Ignite?
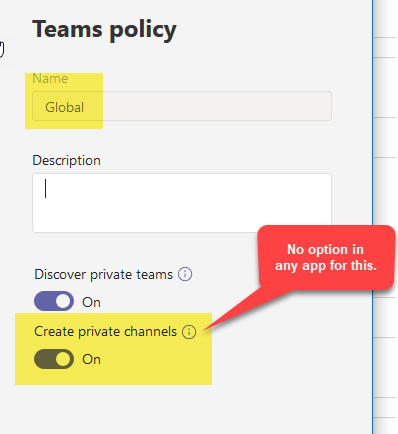
The question to which everyone is seeking the answer, I know. Didn't see anything upon searching so here goes... Recently in the TAC I found under 'Teams || Teams Policies || Global' there is an option to enable private channels. (See SS Below). It's part of the so-called 'global' policy so you'd logically think everyone would get it. However, there's nothing that I see in any of my clients to indicate that functionality. What is also strange is that when you look at the Policy assignments it says '400' default, but we have >2000 licensed users. Huh? Not to mention that it's enabled by default and no one has said anything to me (yet...). My thought is ''Just wait until the trumpets about it are sounded from Orlando next month...' but it's 'partially' there and was wondering if I could find it in PS, create a custom policy, with it enabled and then assign it to myself. I have seen them in action at MS On-Site meetings so they're not a myth, BTW. Anyone?Solved3.4KViews0likes5Comments