mip
15 TopicsMicrosoft Purview Referential Architecture Diagrams
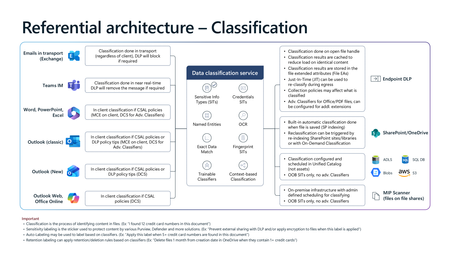
Microsoft Purview architecture diagrams provide a reference view of how classification, sensitivity labelling, Data Loss Prevention (DLP), Insider Risk Management, and Microsoft 365 Copilot protections work together across Microsoft 365 workloads. They illustrate how organisations can consistently identify, label, and protect sensitive data across endpoints, email, collaboration services, browsers, and AI‑assisted workflows—without prescribing a single deployment model. Classification generates sensitivity signals, labels express organizational protection intent, and DLP enforces that intent in real time across devices, apps, and services. Together, these patterns show how Copilot inherits existing security controls so AI‑generated content remains governed within the same compliance boundaries as organizational data.22KViews24likes9CommentsSecure external attachments with Purview encryption
If you are using Microsoft Purview to secure email attachments, it’s important to understand how Conditional Access (CA) policies and Guest account settings influence the experience for external recipients. Scenario 1: Guest Accounts Enabled ✅ Smooth Experience Each recipient is provisioned with a guest account, allowing them to access the file seamlessly. 📝 Note This can result in a significant increase in guest users, potentially in hundreds or thousands, which may create additional administrative workload and management challenges. Scenario 2: No Guest Accounts 🚫 Limited Access External users can only view attachments via the web interface. Attempts to download then open the files in Office apps typically fail due to repeated credential prompts. 🔍 Why? Conditional Access policies may block access to Microsoft Rights Management Services because it is included under All resources. This typically occurs when access controls such as Multi-Factor Authentication (MFA) or device compliance are enforced, as these require users or guests to authenticate. To have a better experience without enabling guest accounts, consider adjusting your CA policy with one of the below approaches: Recommended Approach Exclude Microsoft Rights Management Services from CA policies targeting All resources. Alternative Approach Exclude Guest or External Users → Other external users from CA policies targeting All users. Things to consider These access blocks won’t appear in sign-in logs— as this type of external users leave no trace. Manual CA policy review is essential. Using What if feature with the following conditions can help to identify which policies need to be modified. These approaches only apply to email attachments. For SharePoint Online hosted files, guest accounts remain the only viable option. Always consult your Identity/Security team before making changes to ensure no unintended impact on other workloads. References For detailed guidance on how guest accounts interact with encrypted documents, refer to Microsoft’s official documentation: 🔗 Microsoft Entra configuration for content encrypted by Microsoft Purview Information Protection | Microsoft Learn3.7KViews5likes3CommentsImpact of Deleting old Label in Compliance Portal
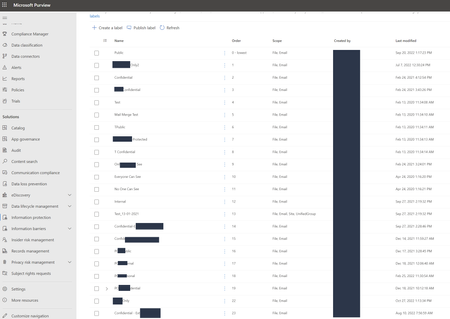
Hi All, I wanted a help to understanding the impact of deleting old label/labels which are not using as of now. However, those labels might be used in previously and because of that I need to understand is there any impact of Data loss. as of now we have too many labels in our environment and purpose is reducing the number of labels. appreciate the help. Thanks, DilanSolved3.1KViews0likes2CommentsFrom Oversharing to Enforcement: A Practical Guide to AI Data Security with Microsoft Purview
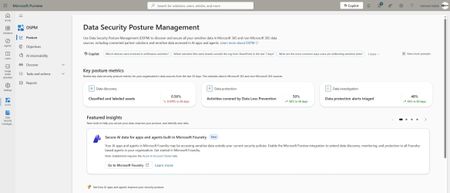
Why AI Changed the Data Security Problem AI does not create entirely new categories of risk—it supercharges existing ones. Traditional data leakage stems from ordinary behavior: sharing a document too broadly, sending an email to the wrong person, copying regulated data to an uncontrolled device. Generative AI amplifies all of these because of the power and speed with which it can proactively surface content that may be obsolete, over-permissioned, or ungoverned. DSPM exists to help with exactly this challenge: it continuously scans your environment to identify sensitive data, assess risk, and recommend actions to reduce exposure. Oversharing at Scale Before AI, an overshared SharePoint file might sit unnoticed. Now, Copilot can summarize it in response to a casual prompt, distributing its contents far beyond the original audience. Prompt Leakage Users can inadvertently expose sensitive information—financial account numbers, health records, project code names—simply by typing them into a Copilot prompt. Because AI interactions feel conversational, users tend to drop their guard. Shadow AI Beyond sanctioned tools, employees experiment with unapproved AI services. Autonomous Agents Autonomous agents expand the data security threat surface by acting independently on sensitive information across systems and boundaries. Their ability to access and share data without direct user interaction increases the risk of oversharing, exfiltration, and unauthorized access, while also introducing complex behavior patterns that are harder to monitor, govern, and control using traditional security models. What Microsoft Purview Now Brings Together Data Security Posture Management (DSPM) DSPM consolidates insights from Data Loss Prevention (DLP), Insider Risk Management, Information Protection, and Data Security Investigations into a single view for monitoring data risks, policy coverage, and posture trends. Now also in Public Preview, DSPM extends coverage to third-party SaaS and IaaS platforms such as Google Cloud Platform, Snowflake, and Databricks, and integrates with partner solutions including Cyera, BigID, and OneTrust for comprehensive risk insights. A central innovation in this version is data security objectives—prominent, selectable cards that each represent a specific security goal. Selecting an objective guides administrators through an end-to-end workflow that groups together the most relevant Purview solutions—information protection, DLP, Insider Risk Management, and eDiscovery—so teams can focus on achieving a specific data security outcome rather than navigating separate solutions. Each Outcome card displays key metrics such as the percentage of data covered by policies, the number of risky sharing incidents, and improvements over time. Within each outcome, DSPM surfaces suggested prioritized actions—applying sensitivity labels, configuring DLP policies, or investigating alerts—all tailored to the organization's data. Administrators can take action directly from the workflow, including remediating oversharing, configuring one-click policies, or launching investigations into suspicious activity. DLP Integration for AI Interactions DLP is one of the core solutions integrated into DSPM's unified approach. The Activity Explorer's AI activities tab captures events where DLP rules were matched during AI interactions—including prompts, responses, and browsing to generative AI sites. DSPM can automate remediation steps such as removing public sharing links or applying data loss prevention policies to help prevent incidents before they happen. AI Observability and Agent Governance Dedicated dashboards and metrics monitor risks associated with AI apps and agents. AI observability enables tracking of agent-specific activities—oversharing, exfiltration, and unusual access patterns—across both Microsoft and third-party environments. Enhanced reporting provides advanced filtering and customizable views, supporting granular analysis of sensitive data usage, DLP activity, and posture trends. Audit logs and activity explorer features help track interactions with AI apps and agents, supporting compliance investigations and incident response. AI-Powered Security Operations DSPM not only secures and governs AI apps and agents but also uses Microsoft Security Copilot and AI agents to help secure and govern data. AI analyzes access patterns, sharing behaviors, and policy gaps to surface actionable risks and can detect unusual activity such as excessive sharing or suspicious downloads. Under administrator guidance, AI agents can take direct action on detected risks—removing public sharing links, applying DLP policies, or revoking permissions. These actions are always audited. To streamline investigations, AI-driven triage agents review alerts from DLP and Insider Risk Management solutions, filtering out noise and highlighting the most critical threats. Three Practical Starting Points For many organizations adopting generative AI, the biggest hurdle isn't recognizing new risks—it's figuring out where to begin. A "boil the ocean" approach can stall progress, while tackling a few targeted areas delivers quicker wins. The best early moves are those that reduce exposure quickly, improve visibility, and build a foundation for stronger governance over time. Starting Point 1: Enable prompt-level protection for Microsoft 365 Copilot An effective first step is to put guardrails on the prompts users enter into AI. Microsoft Purview DLP allows administrators to restrict Microsoft 365 Copilot and Copilot Chat from processing prompts that contain sensitive information. In practice, users are often more comfortable pasting data into a chat prompt than attaching it to an email, which means a well-meaning employee could inadvertently feed a confidential file or personal data into Copilot. Enabling prompt-level DLP creates an immediate safety net: if a user's prompt includes, say, a credit card number or a customer's national ID, Copilot will detect it and refuse to process or share that content. DSPM provides suggested prioritized actions—including configuring DLP policies—that can be activated directly from the workflow, and recommended policies can start in simulation mode. Simulation mode lets you see what would have been blocked or flagged, without actually interrupting users, so you can fine-tune the policy and prepare your helpdesk for any questions. Once you're comfortable with the results, switching to enforcement mode will actively block disallowed prompts and log those events for review. By activating this one control, you've significantly reduced the most immediate oversharing risk—the "oops, I pasted the wrong data" scenario—within hours of starting your AI governance program. Tradeoff: Simulation mode provides safety but delays enforcement. For organizations with imminent regulatory exposure, consider shortening the simulation window and monitoring alert volumes closely. Starting Point 2: Gain visibility into shadow AI usage before broad enforcement The second step is to illuminate what's happening in the shadows. Before rushing into blocking every unsanctioned AI tool, it's crucial to understand how and where AI is being used across the organization. In most enterprises, there's an official layer of AI usage and an often larger, unofficial layer—employees experimenting with free online AI chatbots, writing assistants, or code generators. DSPM provides this visibility. The Discover > Apps and agents dashboard shows AI apps used across the organization, including the top 20 most recently used agents, with details about sensitive data they accessed and how they are protected by Purview policies. The AI observability page provides a broader inventory of all AI apps and agents with activity in the last 30 days, including how many are high risk and the total with sensitive interactions. The Activity Explorer's AI activities tab shows when users browsed to generative AI sites, the prompts and responses involved, whether sensitive information was present, and whether DLP rules were matched. Armed with this insight, you can make informed decisions. If you discover that the majority of "AI consumption" comes from just two external apps, you might focus your immediate controls on those two. Conversely, if the data shows most unsanctioned usage is low-risk, you might decide to monitor rather than block it. The key is visibility first, enforcement second—letting real data guide where to tighten controls versus where to offer secure alternatives. Tradeoff: Visibility without timely follow-through can create a false sense of security. Set a defined window (e.g., 30 days) after which findings must translate into at least one concrete policy action. Starting Point 3: Operationalize DSPM objectives for Copilot A stronger third starting point is to use DSPM as your operational guide, not just a dashboard of charts. DPSM introduces data security objectives—each one a focused end-to-end workflow for a specific outcome. Rather than configuring individual features in isolation, you select an objective and let Purview navigate you through achieving that outcome with the relevant tools. For generative AI, the key objective to leverage early is "Prevent data exposure in Microsoft 365 Copilot and Microsoft Copilot interactions". By selecting this objective in the Purview portal, you're effectively telling Purview, "help me implement whatever is needed to make Copilot safe with our data." The DSPM interface then groups together the critical pieces: it may prompt you to enable a DLP policy, suggest applying or refining sensitivity labels on content, or surface an Insider Risk Management policy template for detecting AI-related risky behavior. It also surfaces metrics so you can track progress—for example, the percentage of data covered by policies, or the number of risky sharing incidents that have been remediated. Using DSPM objectives keeps your team aligned on a clear goal from day one. It shifts the conversation from "what knobs do we turn on?" to "how do we achieve this outcome?" You follow a guided plan curated by the platform's intelligence rather than navigating five different admin pages and hoping it adds up to protection. Tradeoff: Objectives streamline the path but can obscure the underlying complexity. Teams should periodically step outside the guided workflow to review the full policy landscape and ensure no coverage gaps exist between objectives. From Visibility to Remediation: Turning Insights into Action Automated Remediation at Scale DSPM can automate remediation steps such as removing public sharing links or applying data loss prevention policies to prevent incidents before they happen. Under administrator guidance, AI agents within DSPM can take direct action on detected risks—removing sharing links, applying DLP policies, or revoking permissions—and these actions are always audited. This moves the operating model from manual, one-at-a-time fixes to systematic, policy-driven remediation. Closing the Loop: From Risk to Standing Policy DSPM's data security objectives surface suggested prioritized actions such as applying sensitivity labels, configuring DLP policies, or investigating alerts, all tailored to the organization's data. Reporting and analytics are organized by outcome, making it easier to identify and report improvements, compliance, and risk reduction. This turns recurring findings into standing preventive controls. Instead of re-running assessments and manually fixing the same patterns, administrators create durable policies that enforce the desired state going forward. Alert-Driven Investigation and Tuning Audit logs and activity explorer features help track interactions with AI apps and agents, supporting compliance investigations and incident response. Integrated investigation and forensics tools support rapid incident response and root cause analysis for data security events. Impact prediction visuals and progress tracking for remediation steps are surfaced throughout DSPM, enabling administrators to quantify the effect of their actions and adjust course. The closed-loop process is: Discover (DSPM scans and risk assessments) → Remediate (automated actions and bulk fixes) → Prevent (create or tighten DLP and auto-labeling policies) → Monitor (alert review, investigation, and policy tuning). What "Good" Looks Like in a Regulated or Risk-Aware Organization A mature AI governance posture is defined by measurable outcomes and sustainable operating rhythms—not feature count: Clear, communicated AI usage policies. Users know what is and is not acceptable in AI interactions because the tools reinforce the rules. DLP policy tips delivered at the moment of a violation are a primary training mechanism—they remind users in context why their prompt was blocked and what to do instead. Measured enablement over blanket bans. Leading organizations allow Copilot with appropriate controls and restrict only truly unacceptable scenarios. Policies deployed initially in simulation mode provide data to calibrate enforcement thresholds before blocking. This avoids productivity backlash while preserving security posture. High data hygiene and classification rates. Purview's AI protections depend heavily on sensitivity labels. If everything is unlabeled or "General," label-based controls have nothing to act on. Mature organizations invest in auto-labeling and mandatory labeling to close this gap before deploying AI at scale. DSPM's data security objectives include suggested actions such as applying sensitivity labels, directly tying classification to governance outcomes. Quantifiable risk reduction. Security leadership can produce metrics from Purview that show trend lines: DSPM Outcome cards display the percentage of data covered by policies, the number of risky sharing incidents, and improvements over time. These figures feed directly into compliance reporting and audit evidence. Key metrics are tracked over time, supporting continuous improvement of the organization's data security posture. Cross-functional governance. AI governance is not a solo IT Security effort. Stakeholders from security, compliance, legal, and business units review AI usage patterns, discuss policy tuning, and evaluate new Purview capabilities as they release. Role-based access controls within DSPM provide granular access to features and AI content for delegated administration and compliance, enabling this cross-functional model without overexposing sensitive data to every participant. Tradeoff: Strict enforcement can frustrate power users and slow AI adoption. Organizations should explicitly define escalation paths—if a legitimate use case is blocked by DLP, there must be a fast process to review and adjust, rather than a permanent "no." A Phased Adoption Model Phase Focus Key Activities Phase 1 — Quick Wins (weeks) Visibility and baseline safeguards Enable prompt-level DLP for Copilot in simulation mode. Run first DSPM data risk assessment for oversharing. Enable shadow AI discovery via DSPM's Apps and agents dashboard and AI observability page. Start from the DSPM objective "Prevent data exposure in Microsoft 365 Copilot and Microsoft Copilot interactions." Phase 2 — Broad Enforcement (months) Acting on findings Switch DLP policies from simulation to enforcement. Use automated remediation actions (removing sharing links, applying DLP policies, revoking permissions). Expand sensitive information type definitions and add custom types. Rollout user communications explaining new controls and escalation paths. Phase 3 — Mature Governance (ongoing) Continuous improvement and AI-powered operations Leverage AI-driven triage agents to filter alert noise and highlight critical threats. Conduct periodic DSPM posture reviews using Outcome card metrics. Tune policies based on impact prediction visuals and progress tracking. Extend protections to new AI apps and agents as they are adopted—DSPM's AI observability tracks agent-specific activities across Microsoft and third-party environments. Formalize cross-functional AI governance cadence. *Phase 1 should take weeks, not months—the objective is to establish a baseline before risk accumulates. *Phase 2 is where enforcement generates measurable risk reduction. *Phase 3 is ongoing: as Microsoft continues extending Purview to additional AI apps and agent types, the governance framework must evolve in tandem. The DSPM preview's integration with third-party SaaS and IaaS platforms (Google Cloud Platform, Snowflake, Databricks) and partner solutions (Cyera, BigID, OneTrust) means the governance perimeter can expand alongside the organization's AI footprint. Conclusion AI adoption and data protection are not opposing forces. Microsoft Purview now provides the visibility, policy controls, and remediation workflows to move from discovering AI risk to actively governing Copilot, third-party AI apps, and agents at scale. DSPM surfaces oversharing and AI usage patterns through unified dashboards, data risk assessments, and AI observability. DLP blocks sensitive data in prompts and restricts AI access to labeled content. Insider Risk Management detects adversarial AI behavior. AI-driven triage and remediation agents close the gap between identifying a problem and fixing it—with every automated action audited. The path forward starts with practical actions: enable prompt-level DLP, illuminate shadow AI usage, and operationalize DSPM's "Prevent data exposure in Microsoft 365 Copilot and Microsoft Copilot interactions" objective. From there, enforce what you find, measure the results using DSPM's outcome-based metrics, and progressively mature your governance posture. Organizations that operationalize this loop will be in a strong position: able to say, "We use AI to work smarter—and we have the safeguards in place to do it safely."2.9KViews5likes2CommentsPurview Webinars
REGISTER FOR ALL WEBINARS HERE Upcoming Microsoft Purview Webinars JULY 15 (8:00 AM) Microsoft Purview | How to Improve Copilot Responses Using Microsoft Purview Data Lifecycle Management Join our non-technical webinar and hear the unique, real life case study of how a large global energy company successfully implemented Microsoft automated retention and deletion across the entire M365 landscape. You will learn how the company used Microsoft Purview Data Lifecyle Management to achieve a step up in information governance and retention management across a complex matrix organization. Paving the way for the safe introduction of Gen AI tools such as Microsoft Copilot. 2025 Past Recordings JUNE 10 Unlock the Power of Data Security Investigations with Microsoft Purview MAY 8 Data Security - Insider Threats: Are They Real? MAY 7 Data Security - What's New in DLP? MAY 6 What's New in MIP? APR 22 eDiscovery New User Experience and Retirement of Classic MAR 19 Unlocking the Power of Microsoft Purview for ChatGPT Enterprise MAR 18 Inheriting Sensitivity Labels from Shared Files to Teams Meetings MAR 12 Microsoft Purview AMA - Data Security, Compliance, and Governance JAN 8 Microsoft Purview AMA | Blog Post 📺 Subscribe to our Microsoft Security Community YouTube channel for ALL Microsoft Security webinar recordings, and more!2.4KViews2likes0CommentsScaling classification and labeling: an interactive reference architecture update
In April, I published a set of referential architecture diagrams for Microsoft Purview — Microsoft Purview Referential Architecture Diagrams. They have been useful in workshops and training sessions for a simple reason: one picture is worth a thousand words - attempting to explain the complex in a single image. Today I'm publishing an update focused on classification and labeling — and on the wave of public previews that make auto-labeling something you can scale across the entire estate with ease. ➡️ Download the interactive architecture on GitHub here. It's a self-contained HTML file - and it's a lot more than this picture! Why now: auto-labeling scales to the whole estate The most consequential change is surprisingly small. An auto-labeling policy can now be kept on while you edit it, without re-triggering simulation. Anyone who has run auto-labeling at scale knows why that matters. Until now, tuning a policy meant turning enforcement off, re-simulating, waiting, and turning it back on — delays every time you refined a rule. That friction made it challenging for organizations from broadening scope as fast as they wanted to. Removing it changes the operating model: you can simulate once with your conditions and expand scope (sites) when you're ready, without hitting the simulation limit. It arrives alongside a set of previews that lift every ceiling that used to cap the motion: Capacity is up 5x. Auto-labeling for SharePoint and OneDrive moves from 100,000 to up to 500,000 files per tenant per day (Roadmap ID 567890). Simulation goes from 4M to 20M items, so you can model against a real estate rather than a sample. Policy scope gets much bigger. Select up to 1,000 individual SharePoint sites per policy, adaptive scopes support up to 50,000 sites, and you can filter sites by the SiteTemplate property when configuring a policy (Roadmap ID 570445, MC1469958). Reporting finally tells you what happened. Audit and reporting now summarize the sensitive information types detected when labels are applied, and a new 30-day chart shows files processed per day so you can watch policy throughput. A per-policy coverage report correlates files processed during enforcement to the latest simulation run — including the files that enforcement processed but simulation never saw (Roadmap ID 568935). SharePoint library default labels now reach data at rest, applying the library's default label to existing files instead of only new or edited ones (Roadmap ID 559105, MC1477181). Read together, these are one story: classify and label the whole estate — unblocking your Microsoft 365 Copilot deployment by securing the data that matters to you most. The scalability improvements are on by default, and existing policies continue to function unmodified with no end-user impact. What the architecture shows The diagram follows content through five stages, each framed as the question it answers: User input — where information originates: files, email, Teams messages, files on devices, files in transit, and prompts. Information is classified — what is it? SITs, Exact Data Match, named entities, document fingerprinting, trainable classifiers, and AI classifiers, with automatic (in-transit) and on-demand (at-rest) classification as the two entry paths. Labeling files — what is the default security posture, and what did the user intend? Five labeling methods — default label from policy, client-side, library default, service-side auto-labeling, and manual — all converging on one node: the label is applied. Protection — what do we do about it? DLP (including DLP for Copilot), encryption and usage rights, permissions, label inheritance on Copilot responses, Adaptive Protection, and retention. Insights — what did we learn? DSPM, Activity and Content Explorer, the unified audit log, DLP alerts, and Insider Risk alerts. How to use it - it's interactive! It's a single self-contained HTML file — no dependencies or API call — it works offline. Click any node to light up its full upstream and downstream path; everything unrelated dims. The detail panel then shows what it feeds from, what it feeds into, what it sees, what it can do, and — the section I'd argue matters most — what it can't do. Explain runs three guided walkthroughs: Classification vs labels, When is it classified?, and How is it protected? These are my go-to openers for a workshop. Isolate layer cuts the diagram by control plane — sensitivity label, SITs, classifiers, DLP, encryption, permissions, retention, audit. Licensing lens filters to Included in E3, E5 only — the delta over E3, or Pay-as-you-go. Use it to answer entitlement questions honestly: where Microsoft publishes no SKU, the node says so instead of guessing. Always confirm entitlements on a quote, not from a diagram. Overview only strips to titles for a clean read; Fit to width scales the whole thing to the window; light/dark follows your OS or the toggle; it prints cleanly to PDF. Keyboard: Tab between nodes, Enter to select, Esc to reset. Auto-labeling at scale If you're standing up auto-labeling at scale, confirm the prerequisites node first — sensitivity labels enabled for Office files in SharePoint and OneDrive, PDF support enabled separately via EnableSensitivityLabelForPDF, auditing on (simulation requires it), labels published to at least one user, and label scope covering Files and/or Emails. Simulate on your priority sites, review, enforce, then expand scope to more sites or all sites and keep going. Combine that with capabilities already GA — labeling files contextually by site + file types, and overriding manually applied labels — and you can finally clear the backlog of unlabeled files. note: more to come soon for a full deployment guide. Feedback welcome — if a node is wrong, missing a limitation, or missing a link, tell me in the comments and I'll fix it in the next revision.1.7KViews4likes1CommentSharing: PDF readers that support Purview labels
As I was researching on Adobe Acrobat reader and Sensitivity labels, I decided to check if the common alternative PDF readers out there are able to support Purview MIP Sensitivity labels. There is already a published documentation on this for SharePoint-Compatible PDF readers that supports Microsoft IRM: https://learn.microsoft.com/en-us/purview/sp-compatible-pdf-readers-for-irm (last updated Nov-2023) but I wanted to see if these same PDF readers supports the ability for end-users to use/ select labels similar to that of Adobe Acrobat As of 11-June-2025; atleast one of them clearly do: Nitro PDF: Yes. Documentation shows that users can see and use the sensitivity labels. PDF -X.change Editor: Yes. Documentation show that users can see and use the sensitivity labels. (check the official website, I can't hyperlink it because the site is blocked. FOX PDF editor: No. Documentation only states RMS and not clear if it show Purview labels. This is for F.O.X.I.T editor (spelled without the ".") but for some reason there is a community ban on that word and it won't allow me to post the full name PDFescape: No. Sumatra PDF: No Okular: No If there are other PDF readers that I've missed, I encourage you list it down in the comment below. Would love to grow this list.1.7KViews5likes4CommentsMeet the New Microsoft Purview Classifiers Experience: Your Admin Playbook for Public Preview
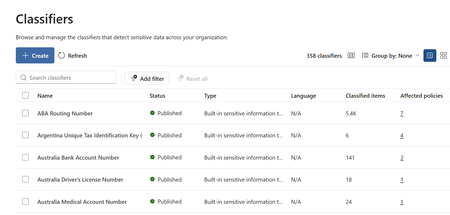
Microsoft Purview Unified Classification Management Experience Feature overview and administrator playbook Overview The new Classifiers experience brings supported Microsoft Purview classification types into one place where administrators can discover, create, inspect, and manage classifiers. It adds practical visibility into classified-item counts and policy dependencies so administrators can make more informed, lower-risk changes. Why this experience is important Classification underpins data protection, data loss prevention, and data security. As classifier inventories grow, administrators need a consistent way to understand what exists, where it is used, and what could be affected by a change. Centralized visibility Search and filter supported classifiers from a unified inventory instead of navigating separate management locations. Safer change decisions Review classified-item counts and affected policies before editing or deleting a classifier. Stronger governance Establish clear ownership, testing, approval, validation, and review expectations. Better coverage analysis Use matched-item information and Data Explorer to understand where classifications occur and where gaps may exist. What administrators can do Discover supported classifier types and understand what the organization already uses. Create classifiers from a single entry point with type-specific preparation guidance. Review classified-item counts and inspect policies that depend on a classifier. Validate matched items across supported data sources and investigate unexpected coverage. Access Classifiers through Information Protection, Data Loss Prevention, or Data Security Posture Management, depending on tenant availability. Supported classification capabilities include sensitive information types, named entities, Exact Data Match, trainable classifiers, credentials, document fingerprinting, optical character recognition, and on-demand classification. How the experience can help Reduce context switching: Use one inventory to find and inspect supported classifiers. Understand impact earlier: Identify policy dependencies before a change reaches enforcement. Improve accountability: Connect classifiers to business owners, policy owners, and reviewers. Standardize operations: Apply the same lifecycle to routine maintenance, quality improvements, and retirement decisions. How the admin playbook helps The companion playbook turns the preview into a practical operating guide. It is designed to be the first place an administrator goes to understand the value of the experience and apply it safely. Explains the administrator value of unified classifier management. Provides a continuous Inventory Offers a decision guide for selecting an appropriate classification method. Shows how to review policy impact and validate matched items. Includes customer scenarios and answers to common licensing, permissions, and coexistence questions. INVENTORY → ASSESS → TEST → APPROVE → CHANGE → VALIDATE → REVIEW Resources Public documentation Current availability, permissions, supported classification capabilities, and product guidance. Administrator playbook A self-contained, interactive guide with workflows, screenshots, scenarios, and FAQs.1.5KViews2likes0CommentsError Information Rights Management not configured
Hi Team. I deploy Microsoft Information Protection with sensitivity labels. After create labels, in both, Office clients and Web, show error: Information Rights Management not configured. For configure IRM, sign in Office, create message or document protected by IRM existing (Attach message in spanish). Trobleshooting: Migrate service Azure Information Protection to Microsoft Information Protection. Delete all labels migrated from AIP to MIP. Create new labels in MIP. Test in Word, Outlook client. Test in Word, Outlook web. Ideas for troubleshooting? Thanks,1.5KViews0likes0CommentsData Security Posture Reports (Custom Workspace and Charts)
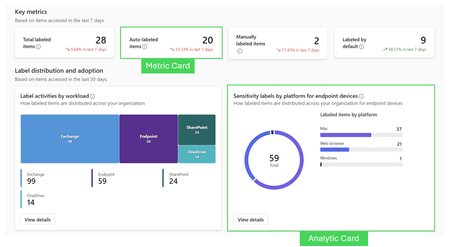
For more insights on OOB Reports, check out this article. Overview: NOW IN PUBLIC PREVIEW Microsoft Purview Posture Reports provide a clear, outcome‑based view of how effectively data protection controls, such as Sensitivity Labels and Data Loss Prevention (DLP) policies, are working across Microsoft 365. Rather than focusing on individual alerts or isolated events, Posture Reports help organizations answer a higher‑level, executive‑ready question: Are our data protection controls consistently applied and actually reducing risk at scale? Posture Reports transform complex telemetry from Audit logs, Activity Explorer, and policy enforcement into measurable, defensible insights that security, compliance, and business leaders can act on with confidence. Building on the out‑of‑the‑box experience, Custom Posture Reports enable teams to create scenario‑specific views tailored to their organization’s risk priorities. Key capabilities include: Custom dashboards with drag‑and‑drop sections and cards Built‑in and custom metric or chart cards powered by Activity Explorer data Flexible filtering to support focused investigations and reporting Tips: Start with clear questions, then choose cards that answer them Avoid overcrowding reports; fewer, well‑chosen cards are more effective Use metric cards for status, analytics cards for understanding Treat custom reports as living assets, iterate as needs evolve This allows security teams to move beyond one‑size‑fits‑all reporting and build views aligned to their unique data protection strategy. Preview note: As this feature is in Preview, capabilities, terminology, and UX may change, and not all scenarios are fully documented yet. Key Concepts Where can I access these reports? Three Locations: Purview.microsoft.com -> Information Protection -> Reports Purview.microsoft.com -> Data Loss Prevention -> Posture Reports Purview.microsoft.com -> DSPM -> Reports (CUSTOM COMING) What is a Custom Report? A Custom Report is a user‑created report container where you assemble one or more cards to visualize Information Protection–related data (for example, labeling, classification, or protection activity). Unlike the built‑in reports, custom reports are designed to be adaptable to different audiences and questions. Typical use cases include: Tracking adoption of sensitivity labels over time Monitoring where sensitive data is most concentrated Creating executive‑friendly, KPI‑style summaries Building analyst views for deeper investigation Core Actions in the Custom Reports Experience Add Report creates a new, empty report canvas. This is the starting point where you define: The report name and purpose Create custom reports with your preferred cards and analytics. Add section is used to create a logical grouping within a custom report. A section acts as a container that helps organize cards on the report canvas into meaningful groupings based on purpose, audience, or storyline. What a section does How sections are used Provides structure to a report by grouping related cards together Improves readability and navigation, especially in reports with multiple cards Helps separate different analytical themes within the same report A report can contain one or more sections Each section can include multiple cards (metric cards, chart cards, analytics cards, or custom cards) Sections are added before cards, serving as the layout framework for the report Add Card lets you place a visualization or metric onto the report canvas. Each card answers a specific question, such as “How much data is labeled Confidential?” or “Where is sensitive content growing fastest?” Cards are the building blocks of custom reports and can be mixed and matched within the same report. Permissions: in order to create these reports, you must have permissions to create labels and DLP policies. Built‑in (OOB – Out of the Box) cards: Custom reports include two built‑in card types that can be added to sections: Metric cards – predefined cards used to display key metrics and trends Analytics cards – predefined cards that provide deeper analytical insights Note: In addition to built‑in cards, you can add custom cards (such as metric‑based or chart‑based custom cards) to tailor the report to your scenario. What is a Metric Card? What is an Analytic Card? Metric cards are designed to highlight a single, high‑level value or KPI and are also the foundation for building custom cards that combine metrics with trend context. Analytics cards provide richer visualizations that help users explore patterns and trends in the data. What they do: A Metric card is used to create a card that pairs a primary metric with its historical trend This allows users to answer not just “What is the value?” but also “Is it improving or declining?” Metric cards are commonly used for adoption, growth, and compliance health indicators These cards focus on showing trends over time What they do: Show distributions, breakdowns, or trends over time Enable comparison across locations, labels, or workloads Support investigation and analysis rather than just reporting These are useful when you need a visual representation rather than a single metric. Display data using charts such as bars, lines, or other visual formats Custom cards allow you to define tailored views aligned to your organization’s unique questions. What they do: Focus on specific scenarios not covered by default cards Combine dimensions or filters relevant to your business context Adapt reporting to regulatory, regional, or operational needs When to use them: Organization‑specific KPIs Regulatory or audit‑driven reporting Advanced scenarios that go beyond standard dashboards Custom cards are especially useful for mature programs where built‑in reports are no longer sufficient on their own. Custom Card Configuration The following example illustrates how a metric‑based custom card can be configured to track adoption trends. Scenario: Track adoption of the Confidential sensitivity label over the last 30 days. Card type: Custom card (built from a Metric card) Metric configuration Filters applied What this card shows Metric: Number of items labeled Confidential Time range: Last 30 days (custom) Display format: Compound (shows total count with trend direction) Sensitivity label: Confidential Workload: SharePoint The current total number of items labeled Confidential Whether labeling activity is increasing or decreasing over the last 30 days A focused view of adoption for a specific label and workload This type of custom card is well‑suited for adoption tracking, executive summaries, and ongoing compliance health monitoring. Metric card configuration: Metric cards currently surface up to 7 days of data, providing recent context for the selected metric. Custom surfaces up to the last 30 days of data. You can choose different display formats, such as: Number – a raw count or value Percentage – a proportional view of the metric Compound – a combination of value and trend for quick interpretation You can apply filters to limit the data set to specific criteria (for example, a particular label, location, or workload), allowing the metric to reflect a targeted scenario rather than all data Chart cards are used to visualize data as a graphical chart and can be created as custom cards when you need a visual representation rather than a single metric. Click on Chart Card and under Chart card configuration, select the primary activities: Sensitivity Label Then define the Chart Type Based on the configuration options shown in the UI, the following chart types are available: Vertical bar – compares values across categories using vertical bars; commonly used for side‑by‑side comparisons Horizontal bar – compares values across categories using horizontal bars; useful when category labels are long Pie – shows proportional distribution of values across categories Donut – similar to a pie chart, with a central area that improves readability Line chart – visualizes trends or changes over time Selecting the appropriate chart type helps ensure the custom card clearly communicates the intended insight and improves overall report readability. These cards are commonly used for trend analysis, distribution views, and comparative reporting. Both make patterns easier to understand. Real World Example The business goal this report is addressing is to prove security value and risk reduction, especially to leadership and stakeholders, by tying data protection investments to measurable outcomes. Primary Business Goal: demonstrate that the organization’s data protection controls are effective in reducing financial data risk. The report shows that sensitive financial data is not only being found, but consistently labeled and enforced through DLP, validating that controls are working as intended. Supporting Business Objectives Executive assurance & trust Provide leadership with evidence that compliance and security controls are actively protecting financial data, not just configured. Risk reduction validation Show that financial SITs are being systematically identified and governed, reducing exposure and improper data handling. Value justification for security investments Correlate auto labeling and DLP outcomes to demonstrate ROI on Purview, labeling, and policy investments. Operational confidence Confirm that auto‑labeling policies are accurately detecting sensitive data at scale and triggering appropriate DLP enforcement. Audit and compliance readiness Establish defensible proof that sensitive financial data is discovered, classified, and protected consistently across the environment. Step 1: Create a report, add a name, and description Step 2: Add a section called Key Outcomes (title and description) and add metric cards to show the data at a glance. Step 3: Add another section. Include the following two out of the box charts available. Step 4: Add another section with the out of the box charts Step 5: Add the last section that ties everything together. One out of the box chart and another custom chart. Step 6: for the custom chart above, Do a vertical bar, pivot (the groupings at the bottom of the chart) to Activity. Then, add filters (Sensitive info type: the SITs and Activity: DLPRuleMatch. The report highlights key outcomes, label adoption, application areas, and auto labeling policies. It identifies the main SITs used in labeling and connects them to DLP, demonstrating that the admin's data security measures are effective, particularly with financial information. Using AI to simplify insights This AI integration builds on Microsoft Purview’s existing reporting stack (Posture Reports, Activity Explorer and Audit) and introduces AI-assisted interpretation, summarization, and report composition to reduce manual analysis and accelerate decision-making. To access the report AI Summary: Click on the report and open “View Details” AI will prepare and summarize the report. AI Report Components Executive Summary Delivers a high level, leadership friendly narrative of the most important insights. Highlights overall posture, major risks, and notable improvements or regressions. Summarizes overall activity (for example, total labeled items and dominant platforms) Calls out major observations and limitations (such as lack of trend comparison due to retention) Provides a concise interpretation of what the data means at a point in time This section answers: “What happened, and what should I know without reading the full report?” Key metrics This section provides the essential quantitative data that forms the foundation of the report. Establishes a baseline that can be tracked over time Quantitative measures such as: Number of policy triggers or Label adoption rates Lists the primary counts, categories, and time range used for analysis Clarifies what measurements are available and which are not (such as trends) This section answers: “What are the exact numbers this report is based on?” Distribution Breakdown This section shows how activity is distributed across categories or dimensions. Breaks total activity into meaningful segments (for example, Mac vs. Web Browser) Displays proportional impact using counts and percentages Helps identify concentration areas or imbalances across platforms This section answers: “Where is activity happening the most?” Trend Analysis Evaluates changes over time when historical data is available. Compares current activity to prior periods Highlights increases, decreases, or stability in behavior Clearly calls out when trend analysis is not possible due to data limitations This section answers: “is behavior improving, worsening, or staying the same over time?” Key Findings Synthesizes insights derived from metrics, distributions, and trends. Interprets the data rather than restating it Identifies notable patterns, gaps, or risks (for example, platform skew or low adoption) Connects observations to possible operational or policy implications. This section answers: “What stands out as important or concerning?” Assessment Provides an overall evaluation of the security or compliance posture Combines findings into a holistic judgment Assesses scope, coverage, and effectiveness of current practices Describes whether the posture is sufficient or limited This section answers: “How healthy is our current posture?” Status Summarizes the assessment into a simple outcome indicator. Recommendations Guides next steps based on observed gaps and risks. Suggests practical actions to improve coverage or effectiveness. Aligns recommendations to best practices and product capabilities. Prioritizes changes that reduce risk and improve consistency. This section answers: “What should we do nex References Provides traceability and supporting documentation. Links to authoritative Microsoft documentation used to inform recommendations Allows readers to validate guidance or explore implementation details This section answers: “Where can I verify or learn more?” Full AI Report Summary Summary Posture Reports represent a shift from security configuration to security outcomes. They empower organizations to confidently answer critical questions about risk, readiness, and return on security investment, especially in an AI‑driven world. As reporting continues to evolve, Posture Reports will play a foundational role in how customers prove, improve, and communicate their data security posture.1.3KViews1like1Comment