microsoft sentinel
100 TopicsNinja Cat Giveaway: Episode 3 | Sentinel integration
For this episode, your opportunity to win a plush ninja cat is the following - Reply to this thread with: what was your favorite feature Javier presented? Oh and what does UEBA stand for? This offer is non-transferable and cannot be combined with any other offer. This offer ends on April 14 th , 2023, or until supplies are exhausted and is not redeemable for cash. Taxes, if there are any, are the sole responsibility of the recipient. Any gift returned as non-deliverable will not be re-sent. Please allow 6-8 weeks for shipment of your gift. Microsoft reserves the right to cancel, change, or suspend this offer at any time without notice. Offer void in Cuba, Iran, North Korea, Sudan, Syria, Region of Crimea, Russia, and where prohibited.55KViews6likes38CommentsMITRE ATT&CK Coverage
Morning from the UK! I am trying to better understand how Defender \ Sentinel protect against the MITRE ATT&CK framework. I am particularly interested in mapping to the tactics \ techniques that tools such as Bloodhound and PingCastle highlight for Active Directory \ Azure Active Directory, but am struggling to see what is available in the product and what is still on the roadmap: https://www.pingcastle.com/PingCastleFiles/ad_hc_rules_list.html In terms of what coverage exists within a Tenant, I know there is improvements planned in the roadmap to the current MITRE coverage in Microsoft Sentinel, but is there any way that I could use a Graph query to get what is currently covered?54KViews0likes7Comments
Unable to apply ASR rules for Windows servers (2012R2,2016, 2019 and 2022) via SCCM
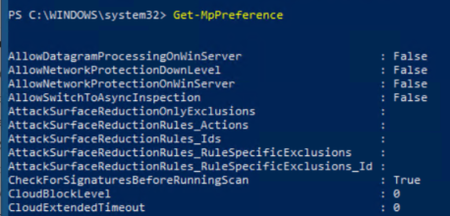
Hi, I have onboarded servers 2012 R2, 2016, 2019 and 2022 into the Microsoft Defender for Endpoint via a unified solution (I am not using MMA or AMA), All statuses are Active and onboarded in the www.security.microsoft.com console. These servers are managing through the SCCM and I could deploy the Antimalware policy for all servers. Still, I am unable to deploy ASR rules for the onboarded servers, I have tried manually configure rules into the servers. Still, when I run Get-MpPreference powershell command there are blank fields for ASR components. Any solution for this? Note: These servers are not joined AAD.50KViews0likes3CommentsBlog Series: Limitless Advanced Hunting with Azure Data Explorer (ADX)
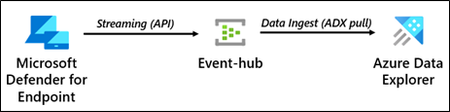
Leverage the power of Azure Data Explorer (ADX) to extend your Microsoft 365 Defender (XDR) / Microsoft Defender For Endpoint advanced hunting data for as long as you want (10 years!). If you enjoy rewriting queries just to look through old data and spending time and money rehydrating it, this post isn't for you!24KViews5likes4Comments
Monitoring copied files on External drive - USB
Hello Guys, i struggle to find a way in Defender for EPP or other solutions to monitor when a user copied files on an external peripheral such as hard drive and USB. Some one have the procedure or documentation ? NOTE : Defender timeline could see when a user is plugging a USB stick. but that's... Thanks !Solved14KViews0likes2CommentsIgnite 2025: What's new in Microsoft Defender?
This Ignite we are focused on giving security teams the edge they need to meet adversaries head on in the era of AI. The modern Security Operations Center (SOC) is undergoing a fundamental transformation, placing AI at the forefront of innovation - not just as an added feature, but as a driving force at every layer of the stack. While much attention is rightly focused on the development of security agents, we fundamentally believe that AI must also evolve the very foundation of our security solutions. This means building solutions that more effectively uncover novel threats, act dynamically to defend the organization during attacks, and reduce the workload for the security team. As organizations adopt AI at an unprecedented speed, we also want to make sure they can do so securely. To meet these security needs of the AI era, we are excited to announce a series of innovations that will help organizations shift to an autonomous defense and an agentic SOC. New agents to help scale and accelerate security operations Evolving Microsoft Defender’s autonomous defense capabilities for better protection Secure your low-code and pro-code AI agents with Microsoft Defender Today, we are taking the first step in shifting security operations from static controls to autonomous defense and from manual toil to agentic operations. But we have an ambitious vision to augment and evolve these AI capabilities and agents across the entire SOC lifecycle and are excited to share some of that vision, as shown in the below graphic, with you at Microsoft Ignite. The Agentic SOC: Scaling expertise and accelerating defense We are excited to introduce four new Security Copilot agents in Microsoft Defender that bring autonomous intelligence across different stages of the SOC lifecycle. These agents combine context, reasoning, and complex workflows to help defenders anticipate attacks sooner, detect smarter, and investigate faster than ever before. Security Alert Triage Agent: In March 2025, we introduced the Security Alert Triage Agent, built to autonomously handle user-submitted phishing reports at scale. The agent reviews and classifies incoming alerts, resolves false positives and escalates only the malicious cases that require human expertise. Early data shows that analysts working with the agent caught up to 6.5x more malicious emails compared to professional graders. Today, we’re excited to announce that the agent’s triage capabilities will soon extend beyond phishing to cover identity and cloud alerts. Secondly, we are also improving our phish admin reporting process with a new agentic email grading system. It replaces a manual review process with advanced large language models and agentic workflows to deliver rapid, transparent verdicts and clear explanations to customers for every reported email. Learn more about the agentic email grading system. Threat Hunting Agent – this agent reimagines the investigation process. Instead of requiring analysts to master complex query languages or sift through mountains of data, the Threat Hunting Agent enables natural language investigations with contextual insight. Analysts can vibe with the agent by asking questions in plain English, receive direct answers, and be guided through comprehensive hunting sessions. This levels up the current NL2KQL experience by enabling analysts to explore patterns, pivot intuitively and uncover hidden signals in real time for a fluid, context-aware experience. This not only accelerates investigations but makes advanced threat hunting accessible to every member of the SOC, regardless of experience level. Dynamic Threat Detection Agent – One of the hardest challenges in detection engineering is finding and fixing false negatives. The Dynamic Threat Detection Agent proactively hunts for false negatives and blind spots that traditional alerting might miss. When a critical incident happens, Copilot will kick off an automated hunt to uncover undetected threats—like unusual residual activity around a sensitive identity. This agent turns ‘probably fine’ into proven secure—hunting the quiet persistence that slips past alerts and closing the gap before it becomes tomorrow’s breach. Threat Intelligence (TI) Briefing Agent – Now native in the Defender portal. Generate tailored, AI‑authored threat briefings in minutes—synthesizing global intel with your environment’s context—without leaving the incident pane. Figure 1. The Threat Hunting Agent showing insights on an incident that contained a high risk binary To make the agents easily accessible and help security teams get started more quickly, we are excited to announce that Security Copilot will be available to all Microsoft 365 E5 customers. Rollout starts today for existing Security Copilot customers with Microsoft 365 E5 and will continue in the upcoming months for all Microsoft 365 E5 customers. Customers will receive 30-day advanced notification before activation. Learn more. Autonomous Defense at Platform Scale Threat actors are automating everything. Ransomware campaigns can encrypt an entire environment in under an hour. Adversaries evade detection and pivot across identities, endpoints, and cloud resources faster than human teams can triage alerts. Traditional SOC models—built on manual workflows and fragmented tools—simply can’t keep pace. Every second of delay gives attackers an advantage. Microsoft Defender now counters that speed by delivering autonomous defense at scale. Defender shifts security from reactive firefighting to proactive protection, embedding AI into the foundation of our protection solutions for instant detection, disruption, and containment—before threats escalate. In 2023, we introduced automatic attack disruption, which autonomously stops attacks in progress—like ransomware or business email compromise—with policy-bound actions that isolate endpoints, disable compromised accounts, and block malicious IPs at machine speed. Today, we’re taking the next step. New capabilities show how AI and agentic technology are transforming security to better protect customers: Unleash automatic attack disruption across your SIEM data: We are expanding the disruption capabilities of Microsoft Defender to some of the most critical data sources customer connect via Microsoft Sentinel including AWS, Proofpoint and Okta. This enables real-time detection and automatic containment of threats like phishing and identity compromise on top of your log data, fundamentally turning your SIEM into a threat protection solution. While these capabilities leverage the power of our platform, Defender is not a requirement for customers to realize this value in Microsoft Sentinel. Figure 2. Attack disruption initiated on an AWS attack Predictive shielding – This brand-new automatic attack disruption capability activates immediately after an attack is first contained. Our first of its kind capability combines graph insights, AI, and threat intelligence to predict potential attack paths for where the adversary might go next. It then applies just-in-time hardening techniques that proactively block the attacker from pivoting. Some of the hardening tactics that will automatically be applied by Microsoft Defender include disabling SafeBoot and enforcing Group Policy Objects, putting a hard stop to the attacker’s movements and ability to execute common techniques for compromise. Learn more about predictive shielding and other endpoint security news. Protect your low-code and pro-code AI agents Generative AI and agents are rapidly transforming how we work, but these powerful new tools also introduce new risks. And with the democratization of agent creation across pro-code, low-code, and no-code building platforms, building agents is now accessible to everyone, many without extensive developer or security knowledge. To help security teams better manage these risks we are excited to announce that we are extending the capabilities and experiences in Microsoft Defender to the protection of agents. From agent security posture management, to attack path analysis, and threat protection for Copilot Studio, Azure Foundry, and agents built and connected via the Microsoft Agent 365 SDK. Learn more about how Microsoft Defender can help protect your agents against threats like prompt injections and more. There is so much more innovation we are introducing in Microsoft Defender today, including expanded endpoint security coverage for legacy systems, improvements to how you can investigate identity-centric threats, and we are bringing cloud security posture management into the Defender portal. Check out the other Defender news blogs for more details. Join us in San Francisco, November 17–21, or online, November 18–20, for deep dives and practical labs to help you maximize your Microsoft Defender investments and to get more from the Microsoft capabilities you already use. Featured sessions: Microsoft Defender: Building the agentic SOC with guest Allie Mellen Blueprint for building the SOC of the future Empowering the SOC: Security Copilot and the rise of agentic defense Identity Under Siege: Modern ITDR from Microsoft AI vs AI: Protect email and collaboration tools with Microsoft Defender AI-powered defense for cloud workloads Endpoint security in the AI era: What's new in Defender13KViews2likes0Comments
KQL to get user reported emails?
Hi all, I'm looking for a KQL query to pull back email report submissions / user reported emails - is this possible? MS pull this data in a 365 security report: https://learn.microsoft.com/en-us/microsoft-365/security/office-365-security/reports-email-security?view=o365-worldwide#user-reported-messages-report I'm looking to retrieve the same data. Thanks7.3KViews0likes3CommentsMonthly news - December 2025
Microsoft Defender Monthly news - December 2025 Edition This is our monthly "What's new" blog post, summarizing product updates and various new assets we released over the past month across our Defender products. In this edition, we are looking at all the goodness from November 2025. Defender for Cloud has its own Monthly News post, have a look at their blog space. 😎 Microsoft Ignite 2025 - now on-demand! 🚀 New Virtual Ninja Show episode: Advancements in Attack Disruption Vulnerability Remediation Agent in Microsoft Intune Microsoft Defender Ignite 2025: What's new in Microsoft Defender? This blog summarizes our big announcements we made at Ignite. (Public Preview) Defender XDR now includes the predictive shielding capability, which uses predictive analytics and real-time insights to dynamically infer risk, anticipate attacker progression, and harden your environment before threats materialize. Learn more about predictive shielding. Security Copilot for SOC: bringing agentic AI to every defender. This blog post gives a great overview of the various agents supporting SOC teams. Account correlation links related accounts and corresponding insights to provide identity-level visibility and insights to the SOC. Coordinated response allows Defenders to take action comprehensively across connected accounts, accelerating response and minimizing the potential for lateral movement. Enhancing visibility into your identity fabric with Microsoft Defender. This blog describes new enhancements to the identity security experience within Defender that will help enrich your security team’s visibility and understanding into your unique identity fabric. (Public Preview) The IdentityAccountInfo table in advanced hunting is now available for preview. This table contains information about account information from various sources, including Microsoft Entra ID. It also includes information and link to the identity that owns the account. Microsoft Sentinel customers using the Defender portal, or the Azure portal with the Microsoft Sentinel Defender XDR data connector, now also benefit from Microsoft Threat Intelligence alerts that highlight activity from nation-state actors, major ransomware campaigns, and fraudulent operations. For more information, see Incidents and alerts in the Microsoft Defender portal. (Public Preview) New Entity Behavior Analytics (UEBA) experiences in the Defender portal! Microsoft Sentinel introduces new UEBA experiences in the Defender portal, bringing behavioral insights directly into key analyst workflows. These enhancements help analysts prioritize investigations and apply UEBA context more effectively. Learn more on our docs. (Public Preview) A new Restrict pod access response action is now available when investigating container threats in the Defender portal. This response action blocks sensitive interfaces that allow lateral movement and privilege escalation. (Public Preview) Threat analytics now has an Indicators tab that provides a list of all indicators of compromise (IOCs) associated with a threat. Microsoft researchers update these IOCs in real time as they find new evidence related to the threat. This information helps your security operations center (SOC) and threat intelligence analysts with remediation and proactive hunting. Learn more. In addition the overview section of threat analytics now includes additional details about a threat, such as alias, origin, and related intelligence, providing you with more insights on what the threat is and how it might impact your organization. Microsoft Defender for Identity (Public Preview) In addition to the GA release of scoping by Active Directory domains a few months ago, you can now scope by Organizational Units (OUs) as part of XDR User Role-Based Access Control. This enhancement provides even more granular control over which entities and resources are included in security analysis. For more information, see Configure scoped access for Microsoft Defender for Identity. (Public Preview). New security posture assessment: Change password for on-prem account with potentially leaked credentials. The new security posture assessment lists users whose valid credentials have been leaked. For more information, see: Change password for on-prem account with potentially leaked credentials. Defender for Identity is slowly rolling out automatic Windows event auditing for sensors v3.x, streamlining deployment by applying required auditing settings to new sensors and fixing misconfigurations on existing ones. As it becomes available, you will be able to enable automatic Windows event-auditing in the Advanced settings section in the Defender portal, or using the Graph API. Identity Inventory enhancements: Accounts tab, manual account linking and unlinking, and expanded remediation actions are now available. Learn more in our docs. Microsoft Defender for Cloud Apps (Public Preview) Defender for Cloud Apps automatically discovers AI agents created in Microsoft Copilot Studio and Azure AI Foundry, collects audit logs, continuously monitors for suspicious activity, and integrates detections and alerts into the XDR Incidents and Alerts experience with a dedicated Agent entity. For more information, see Protect your AI agents. Microsoft Defender for Endpoint Ignite 2025: Microsoft Defender now prevents threats on endpoints during an attack. This year at Microsoft Ignite, Microsoft Defender is announcing exciting innovations for endpoint protection that help security teams deploy faster, gain more visibility, and proactively block attackers during active attacks. (Public Preview) Defender for Endpoint now includes the GPO hardening and Safeboot hardening response actions. These actions are part of the predictive shielding feature, which anticipates and mitigates potential threats before they materialize. (Public Preview) Custom data collection enables organizations to expand and customize telemetry collection beyond default configurations to support specialized threat hunting and security monitoring needs. (Public Preview) Native root detection support for Microsoft Defender on Android. This enables proactive detection of rooted devices without requiring Intune policies, ensuring stronger security and validating that Defender is running on an uncompromised device, ensuring more reliable telemetry that is not vulnerable to attacker manipulation. (Public Preview) The new Defender deployment tool is a lightweight, self-updating application that streamlines onboarding devices to the Defender endpoint security solution. The tool takes care of prerequisites, automates migrations from older solutions, and removes the need for complex onboarding scripts, separate downloads, and manual installations. It currently supports Windows and Linux devices. Defender deployment tool: for Windows devices for Linux devices (Public Preview) Defender endpoint security solution for Windows 7 SP1 and Windows Server 2008 R2 SP1. A Defender for endpoint security solution is now available for legacy Windows 7 SP1 and Windows Server 2008 R2 SP1 devices. The solution provides advanced protection capabilities and improved functionality for these devices compared to other solutions. The new solution is available using the new Defender deployment tool. Microsoft Defender Vulnerability Management (Public Preview) The Vulnerability Management section in the Microsoft Defender portal is now located under Exposure management. This change is part of the vulnerability management integration to Microsoft Security Exposure Management, which significantly expands the scope and capabilities of the platform. Learn more. (General Availability) Microsoft Secure Score now includes new recommendations to help organizations proactively prevent common endpoint attack techniques. Require LDAP client signing and Require LDAP server signing - help ensure integrity of directory requests so attackers can't tamper with or manipulate group memberships or permissions in transit. Encrypt LDAP client traffic - prevents exposure of credentials and sensitive user information by enforcing encrypted communication instead of clear-text LDAP. Enforce LDAP channel binding - prevents man-in-the-middle relay attacks by ensuring the authentication is cryptographically tied to the TLS session. If the TLS channel changes, the bind fails, stopping credential replay. (General Availability) These Microsoft Secure Score recommendations are now generally available: Block web shell creation on servers Block use of copied or impersonated system tools Block rebooting a machine in Safe Mode Microsoft Defender for Office 365 Microsoft Ignite 2025: Transforming Phishing Response with Agentic Innovation. This blog post summarizes the following announcements: General Availability of the Security Copilot Phishing Triage Agent Agentic Email Grading System in Microsoft Defender Cisco and VIPRE Security Group join the Microsoft Defender ICES ecosystem. A separate blog explains these best practices in more detail and outline three other routing techniques commonly used across ICES vendors. Blog series: Best practices from the Microsoft Community Microsoft Defender for Office 365: Fine-Tuning: This blog covers our top recommendations for fine-tuning Microsoft Defender for Office 365 configuration from hundreds of deployments and recovery engagements, by Microsoft MVP Joe Stocker. You may be right after all! Disputing Submission Responses in Microsoft Defender for Office 365: Microsoft MVP Mona Ghadiri spotlights a new place AI has been inserted into a workflow to make it better… a feature that elevates the transparency and responsiveness of threat management: the ability to dispute a submission response directly within Microsoft Defender for Office 365. Blog post: Strengthening calendar security through enhanced remediation.6KViews0likes0CommentsMicrosoft Azure and Microsoft 365 Security - my defense in depth strategy!
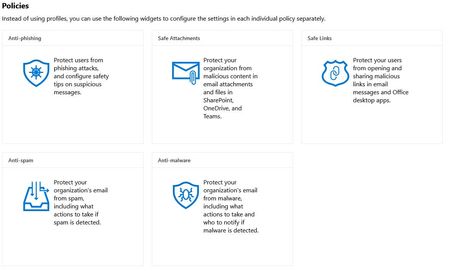
Dear Microsoft Azure and Microsoft 365 security friends, Who is interested in my (small) company? We don't have anything to protect and we don't have any money. Besides, we have a firewall. Furthermore, Mr. Wechsler, you are a bit paranoid with your security thinking. These are the first sentences I always hear when it comes to IT (Cloud) security. But the attacker is also interested in a small company and that is to use their system as a bot. It's not always about money and data. What about the reputation a company has to lose? It takes years to build a good reputation but only one event to damage the reputation. What about the employees, the trust in the company? Do you want to put this at risk as a company, I don't think so! Yes! Extended protection mechanisms always cost extra, I am absolutely aware of that. But I also pay monthly for car insurance and accident and health insurance. I'm grateful every day when I don't need the insurance. That's exactly how it should feel when it comes to IT (cloud) security. Let's start with my IT/Cloud security strategy. I am absolutely aware that this list is not exhaustive. There are so many components to consider, plus every infrastructure/company is always different. I'll try to give you a little help here. We start with Microsoft 365, as a first additional measure, use all policies that start with "Anti-". You can find all the information in the Microsoft 365 Security Center. https://security.microsoft.com/threatpolicy The next step is to use the policies that start with "Safe". You can also find this information in the Microsoft 365 Security Center. Multi factor authentication is a key element to further protect your identities/users. You can set this up per user or with a Conditional Access Policy (my preferred way). Azure Active Directory helps you integrate this protection. https://portal.azure.com If you are subject to a regulatory agency, the Microsoft 365 Compliance Center can help. Here you can set up data loss prevention policies, audits, eDiscovery and much more. https://compliance.microsoft.com/homepage In this day and age of bring your own device and work from home, it's a good idea to include the Endpoint Manager. With it you have the possibility to manage endpoints (Mobile Device Management - MDM) and applications (Mobile Application Management - MAM). https://endpoint.microsoft.com/ Get visibility into your cloud apps using sophisticated analytics to identify and protect against cyberthreats, detect Shadow IT, and control how your data travels. https://portal.cloudappsecurity.com/ The Cloudapp Security Portal provides you with the best possible support. Here you can allow or sanction cloud app, configure anti-ransomware policies, data loss prevention policies and much more. Do you want to know how your Windows Active Directory is doing? Then Microsoft Defender for Identity will help you. With this tool you can transfer the local information to the cloud. With an interface to the CloudApp Security Portal. https://yourtenant.atp.azure.com/timeline No person should always work with elevated rights. Only work with elevated rights when it is really necessary. This is where Azure Privileged Identity Management (PIM) comes in. With this tool you can configure the access as you need it for your needs. https://portal.azure.com With Azure Identity Protection do you have a tool that allows organizations to accomplish three key tasks: 1. Automate the detection and remediation of identity-based risks. 2. Investigate risks using data in the portal. 3. Export risk detection data to third-party utilities for further analysis. https://portal.azure.com Just in time access for administrators, this is also possible for virtual machines with Just in time VM Access. In Microsoft Defender for Cloud you can configure this feature (and much more). Microsoft Sentinel helps you keep track of the health of your organization. A SIEM (Security Information and Event Management) and SOAR (Security Orchestration Automation and Response) tool that should not be missing from your portfolio. The tool offers many connectors (98 at the moment) so that you can connect the most diverse portals to Sentinel. There is still so much to show, I wasn't talking about Role Based Access Control (RBAC) now or Network Security Group (NSG), etc. I know some of you are thinking, hey there is a lot more. I am aware of that. My goal is to give you some positive signals on how you can integrate additional security into your organization. Thank you for taking the time to read this article. Kind regards, Tom Wechsler5.5KViews3likes2CommentsMonthly news - November 2025
Microsoft Defender Monthly news - November 2025 Edition This is our monthly "What's new" blog post, summarizing product updates and various new assets we released over the past month across our Defender products. In this edition, we are looking at all the goodness from October 2025. Defender for Cloud has its own Monthly News post, have a look at their blog space. ⏰ Microsoft Ignite 2025 November 18-20, register now! 🚀 New Virtual Ninja Show episode: What’s new for Microsoft Teams protection in Defender for Office 365 Microsoft Defender Custom detections are now the unified experience for creating detections in Microsoft Defender! Read this blog for all the details. How Microsoft Defender helps security teams detect prompt injection attacks in Microsoft 365 Copilot. We’re excited to share that Microsoft Defender now provides visibility into prompt injection attempts within Microsoft 365 Copilot and helps security teams detect and respond to prompt injection attacks more efficiently and at a broader context, with insights that go beyond individual interaction. Microsoft Defender Experts for Hunting reports now include an Emerging threats section that details the proactive, hypothesis-based hunts we conducted in your environment. Each report also now includes investigation summaries for nearly every hunt that Defender Experts conduct in your environment, regardless of whether they identified a confirmed threat. Microsoft Defender Experts for XDR reports now include a Trends tab provides you with the monthly volume of investigated and resolved incidents for the last six months, visualized according to the incidents' severity, MITRE tactic, and threat type. This section gives you insight into how Defender Experts are tangibly improving your security operations by showing important operational metrics on a month-over-month basis. Threat Intelligence Export is now available in Microsoft Sentinel. Traditionally, Microsoft Sentinel has supported importing threat intel from external sources (partners, governments, ISACs, or internal tenants) via Structured Threat Information eXpression (STIX) via Trusted Automated eXchange of Intelligence Information (TAXII). With this new export feature, you can now share curated threat intel back to trusted destinations. This empowers security teams to contribute threat intel to other organizations in support of collective defense, or to their own central platform to add or enrich threat intelligence. Microsoft Defender for Identity We’re excited to announce that the Defender for Identity Unified Sensor (v3.x) is now generally available (GA). The unified sensor provides enhanced coverage, improved performance across your environment and offering easier deployment and management for domain controllers. Learn more on how to active it in our docs.. Microsoft Defender for Office 365 📘 Email Authentication SecOps Guide (New learn doc) - visit & bookmark our short link: https://aka.ms/authguide The following docs article has been updated with with Compauth Codes: Message Headers Reference New blog series: Best practices from the Microsoft Community Defender for Office 365: Migration & Onboarding Onboarding to Microsoft Defender for Office 365 is often treated as a quick setup task, but it should be seen as a critical opportunity to establish strong security foundations. In my roles supporting incident response and security operations in Microsoft 365, I have observed that onboarding is often underestimated. - Purav Desai, Dual Microsoft Security MVP (Most Valuable Professional) This blog covers four key areas that are frequently missed, but they are essential for a secure and auditable deployment of Defender for Office 365. Before diving into the technical details, it is important to clarify a common misconception about Defender for Office 365 protections. Safeguarding Microsoft Teams with Microsoft Defender for Office 365 As organizations rely more on Microsoft Teams for daily collaboration, securing this platform has become a top priority. Threat actors are increasingly targeting Teams chats and channels with phishing links and malicious files, making it critical for IT admins and security professionals to extend protection beyond email. Enter Microsoft Defender for Office 365, now armed with dedicated Teams protection capabilities. Microsoft Defender for Office 365 enables users to report suspicious messages, brings time-of-click scanning of URLs and files into Teams conversations, and provides rich alerts and hunting insights for SecOps teams. As a collaborative piece between Pierre Thoor, a Microsoft Security MVP, and the Defender for Office 365 Product Engineering Team, this guides with accompanying videos emphasize a proactive, user-driven approach to threat detection and response, turning everyday Teams interactions into actionable security signals for SecOps. Microsoft Defender for Endpoint End of Windows 10 Support: What Defender Customers Need to Know As of October 14, 2025, Microsoft officially ended support for Windows 10. This means that Windows 10 devices will no longer receive security or feature updates, nor technical support from Microsoft. While these devices will continue to operate, the lack of regular security updates increases vulnerability to cyber threats, including malware and viruses. Applications running on Windows 10 may also lose support as the platform stops receiving updates. Endpoint Security Policies can now be distributed via MTO's (Multi Tenant Organization) Content Distribution capability. This capability moved from Public Preview to General Availability (GA). With this capability, you can create content distribution profiles in the multi-tenant portal that allow you to seamlessly replicate existing content - such as custom detection rules and now, endpoint security policies - from a source tenant to designated target tenants. Once distributed, the content runs on the target tenant, enabling centralized control with localized execution. You can read the announcement blog for public preview, as the content shares valuable insights. (Public Preview) Streamlined connectivity support for US government environments (GCC, GCC High, DoD). Learn more in our docs. (General Availability) Isolation exclusions. The Isolation exclusions feature is now generally available. Isolation exclusions allow designated processes or endpoints to bypass the restrictions of network isolation, ensuring essential functions continue while limiting broader network exposure. Learn more in our docs. Microsoft Defender Vulnerability Management (Public Preview) Microsoft Secure Score now includes three new Attack Surface Reduction (ASR) based proactive recommendations that help organizations prevent common endpoint attack techniques including web-shell persistence, misuse of system tools, and Safe Mode based evasion. (Public Preview) You can now use CVE exceptions to exclude specific Common Vulnerabilities and Exposures (CVEs) from analysis in your environment. CVE exceptions allow you to control what type of data is relevant to your organization and to selectively exclude certain data from your remediation efforts. For more information, see Exceptions in Microsoft Defender Vulnerability Management and Create, view, and manage exceptions. For more information, see Exceptions in Microsoft Defender Vulnerability Management and Create, view, and manage exceptions. Microsoft Security Blogs The new Microsoft Security Store unites partners and innovation On September 30, 2025, Microsoft announced a bold new vision for security: a unified, AI-powered platform designed to help organizations defend against today’s most sophisticated cyberthreats. But an equally important story—one that’s just beginning to unfold—is how the Microsoft Security Store is bringing this vision to life through a vibrant ecosystem of partners, developers, and innovators—all contributing together to deliver more value and security to our customers. Security Store is the gateway for customers to easily discover, buy, and deploy trusted security solutions and AI agents from leading partners—all verified by Microsoft Security product teams to work seamlessly with Microsoft Security products. Inside the attack chain: Threat activity targeting Azure Blob Storage Azure Blob Storage is a high-value target for threat actors due to its critical role in storing and managing massive amounts of unstructured data at scale across diverse workloads and is increasingly targeted through sophisticated attack chains that exploit misconfigurations, exposed credentials, and evolving cloud tactics. Investigating targeted “payroll pirate” attacks affecting US universities Microsoft Threat Intelligence has identified a financially motivated threat actor that we track as Storm-2657 compromising employee accounts to gain unauthorized access to employee profiles and divert salary payments to attacker-controlled accounts, attacks that have been dubbed “payroll pirate”. Disrupting threats targeting Microsoft Teams Threat actors seek to abuse Microsoft Teams features and capabilities across the attack chain, underscoring the importance for defenders to proactively monitor, detect, and respond effectively. Harden your identity defense with improved protection, deeper correlation, and richer context Expanded ITDR features—including the new Microsoft Defender for Identity sensor, now generally available—bring improved protection, correlation, and context to help customers modernize their identity defense.5.1KViews1like1Comment