microsoft defender threat intelligence
15 TopicsMicrosoft Defender Threat Intelligence and Sentinel integration deep dive
See how quick detection and response are vital to navigating today's fast-moving cyberattacks. We'll break down a cyberattack and show how Microsoft Defender Threat Intelligence, combined with Microsoft's SIEM and XDR solutions, constructs a multi-stage incident giving visibility into the attack timeline and all related events. We'll then investigate the attacker and automate mitigations to contain the damage. This session is part of the Microsoft Secure Tech Accelerator. RSVP for event reminders, add it to your calendar, and post your questions and comments below! This session will also be recorded and available on demand shortly after conclusion of the live event.5.7KViews5likes26CommentsNew Blog Post | The New Microsoft Security Customer Connection Program (CCP)
Read the full blog post: The New Microsoft Security Customer Connection Program (CCP) - Microsoft Community Hub The security community is constantly growing, changing, and learning from each other in order to better position the world against cyber security threats. For years, Microsoft has driven a customer-obsessed development process by hosting two private communities for end-users of Microsoft security products: the Microsoft Cloud Security Private Community and the Microsoft 365 Defender Customer Connection Program. Under a strict confidentiality framework, our engineering teams get direct community feedback and insights for our roadmap plans, new user experience designs, private preview features, and more. Today, we are happy to announce that these two communities have now come together under one team – The Microsoft Security Customer Connection Program.
CIS Benchmark 1.4 "Ensure that activity log alert exists for the Delete Network Security Group Rule"
Hi, We are trying to remediate this policy receommnedation as per CIS Benchmark 1.4.0, but cannot see an option to configure this rule. Can anyone please advise where to look for this option to remediate this recommendation? Many thanks
Blocking someone from trying to log in
I was involved in a romance scam. I have my computer set up that you need to approve login through my cell phone. Now, I have reason to believe that he is unsuccessfully trying to login to my computer from different isps all over the world. He tries several times a day almost every day. I have enabled all the security ways that I can. Is there any way I can block him without the hassle of changing my email everywhere?
Unable to Disable User Quarantine Mails after enabling security presets
Hi, We have recently enabled security preset policies with Standard protection in our tenant. Since then, our users are receiving quarantine mails from Microsoft. We use AdminOnlyAccessPolicy for quarantine in Anti-spam and Anti-phishing threat policies and in a couple of transport rules and yet users are receiving these quarantine mails. We did try creating a custom quarantine policy and assigning it to Anti-spam and Anti-phishing threat policies, hoping it would override the preset policies, but it didn't work. I know we can either turn off preset policies or block these using transport rules, but these are last resorts. Is there any way or policy to stop these mails keeping the security preset policies on? Thanks in Advance!!Solved
New Blog | 10 essential insights from the Microsoft Digital Defense Report 2023
By Quy Nguyen Published Jan 08 2024 09:19 AM In an era marked by escalating cyber threats, Microsoft sheds light on the global security landscape through the Microsoft Digital Defense Report 2023. Harnessing extensive security research and a unique vantage point, Microsoft not only comprehends the current state of cybersecurity but also utilizes a diverse range of security data to predict and identify indicators of cyber threats. Read the full blog post here: Microsoft Digital Defense Report 2023New Blog Post | Microsoft Defender Weekly Wrap – Issue #50
Microsoft Defender Weekly Wrap – Issue #50 - Azure Cloud & AI Domain Blog (azurecloudai.blog) Happy Friday all! This newsletter is 50! I just want to make it a quick point to thank you all for tuning in and continuing to tune in. This newsletter - and this community - continues to grow by leaps and bounds. Who knew 50 weeks ago that a simple idea like this could swell into something so far reaching and valuable to many of you. I receive commentary frequently from folks that count on this newsletter weekly and participate heavily in the associated LinkedIn group. Your community patronage is amazing and always appreciated. Remember, if you see something you like in the newsletter content don’t keep it to yourself. Share it with someone that needs it. That’s how we continue to grow. … GitLab Survey - Defender for DevOps GitLab Integration The Defender for DevOps team is looking to broaden the Microsoft Defender for Cloud ecosystem by offering customers the ability to onboard their GitLab resources into Defender for DevOps. If your DevOps team uses GitLab in any capacity, we request your feedback to better understand how you interact with the GitLab platform. Survey link: https://rodtrent.com/o9o … The Must Learn KQL Christmas edition has been relaunched for the holidays! Know someone (or yourself) that lives KQL? Could be better than a Christmas Hallmark movie. https://must-learn-kql.creator-spring.com/listing/get-kql-for-christmas All proceeds go to St. Jude. … Even with the purposeful effort to consolidate security portals I think you’ll agree with me that Microsoft still has portal glut. I found the Microsoft Cloud command line this past week and thought I’d share with all of you. If you’ve not seen this already, you’ll thank me for the link: https://cmd.ms/ … That’s it from me for this week. Have a wonderful weekend and week ahead! Talk soon. -RodCheck out our new Microsoft Defender Threat Intelligence Blog on Tech Community
Hey all! I just wanted to make sure everyone had seen that we recently added a new Product Blog under the SCI umbrella on Tech Community- The Microsoft Defender Threat Intelligence Blog. The DTI Tech Community is dedicated to keeping up with today's cyber attackers by sharing Best practices, Threat hunting tips, New features/product updates, and Access to training, workshops, and certifications. I'd love to hear if you are planning on incorporating DTI into your daily workflows by using Microsoft's advanced dynamic threat intelligence to uncover and understand threat infrastructure and detect threats to defend your organizations. Let me know in the comments if you've been able to check out the new blog!New blog post | Entra Identity Governance with Entra Verified ID
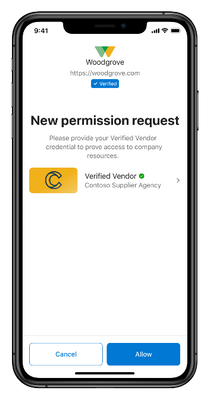
I’m excited to announce the integration of Entra Identity Governance Entitlement Management with a very cool technology we recently introduced, Microsoft Entra Verified ID! If you think about what you need to onboard new users including employees, contractors, partners, or other business guests, it often includes verifying identity information and credentials. This process can be tedious and time-consuming, requiring users to fill out redundant online forms or paperwork, ultimately delaying hiring timelines and ramp-up periods. Entra Identity Governance with Entra Verified ID – Higher Fidelity Access Rights + Faster Onboarding - Microsoft Community Hub