microsoft defender for endpoint
43 Topics
Defender for servers (P1)
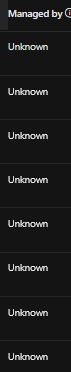
Hey guys, I enabled my Defender for cloud trial licens (P1) for my Windows servers. They are onboarded and i can see them visually in the (security.microsoft.com) EDR Portal. My enforcement scope is set to Intune - so all my AV policies etc are created there. I want to create a AV Policy for my Windows servers but i can't see the objects in Entra. What is best practice. To register them in Entra manually or should it automaticlly create a object in Entra during the onboarding process? Can't create & assign a AV policy etc until i create a group and put all my servers into that group. Any ideas? Also might be worth mentioning i see that they are managed by "unknown" and not Microsoft Sense? Should i point back the scope to the Defender portal? Whilst my endpoints are managed by Intune.281Views0likes1CommentUpdating SDK for Java used by Defender for Server/CSPM in AWS
Hi, I have a customer who is Defender for Cloud/CSPM in AWS. Last week, Cloud AWS Health Dashboard lit up with a recommendation around the use of AWS SDK for Java 1.x in their organization. This version will reach end of support on December 31, 2025. The recommendation is to migrate to AWS SDK for Java 2.x. The issue is present in all of AWS workload accounts. They found that a large amount of these alerts is caused by the Defender CSPM service, running remotely, and using AWS SDK for Java 1.x. Customer attaching a couple of sample events that were gathered from the CloudTrail logs. Please note that in both cases: assumed-role: DefenderForCloud-Ciem sourceIP: 20.237.136.191 (MS Azure range) userAgent: aws-sdk-java/1.12.742 Linux/6.6.112.1-2.azl3 OpenJDK_64-Bit_Server_VM/21.0.9+10-LTS java/21.0.9 kotlin/1.6.20 vendor/Microsoft cfg/retry-mode/legacy cfg/auth-source#unknown Can someone provide guidance about this? How to find out if DfC is going to leverage AWS SDK for Java 2.x after Dec 31, 2025? Thanks, Terru197Views0likes0CommentsFile Integrity Monitoring - Agentless Issues in Detecting Changes to Files
Hello! Looks like there have been some recent updates made to File Integrity Monitoring. After reviewing the MS documentation https://learn.microsoft.com/en-us/azure/defender-for-cloud/file-integrity-monitoring-overview#recommended-items-to-monitor it looks like you can now create custom Rules for Files and for custom Registry keys. From what I can gather from the documentation, agentless scans are used for custom rules that you create and an agentless scan occurs once every 24 hours. I have created several custom rules to detect if a file has been Deleted, Added, Modified or Renamed and Defender for Cloud is still not detecting any changes. I have made changes to these files 3 days ago, and no changes have been reported back. Any ideas why this might not be working. I have already confirmed that the appropriate RBAC Roles have been assigned to my Key Vaults where CMK Disks are being used. I also wanted to know if the Agentless FIM can monitor Folders / Directories as well. I haven't seen anything about this in the documentation. Is this even supported?556Views0likes1CommentOnboarding MDE with Defender for Cloud (Problem)
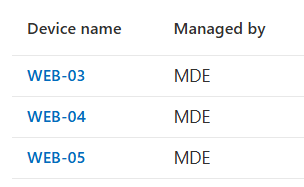
Hello Community, In our Customer i have a strange problem. We onboarded with Azure Arc server and activate a Defender for Cloud servises only for Endpoint protection. Some of this device onboarded into Microsoft Defender portale, but not appears as a device, infact i don't have opportunity to put them into a group to apply policy. I have check sensor of Azure Arc and all works fine (device are in Azure Arc, are in the defender portal and see them on Intune (managed by MDE)). From Intune portal From Defender portal But in difference from other device into entra ID exists only the enterprise application and not device I show the example of device that works correctly (the same onboarding method) Is there anyone who has or has had this problem? Thanks and Regards, Guido630Views0likes3Comments
Unable to resolve - A vulnerability assessment solution should be enabled on your virtual machines
We currently have a mix of approximately 45 Windows / Linux Servers and AVD machines which are not successfully being marked as compliant with the Defender recommendation "A vulnerability assessment solution should be enabled on your virtual machines". On the subscription level we have Defender for Servers Plan 2 enabled and Agentless Scanning CSPM enabled. Within a subscription some of the of these VMs are compliant and others are not. Their compliance state doesn't appear to have any relevance to if the Qualys or MDE extensions are installed. We have servers that are healthy that have Qualys, MDE, or none installed and are healthy. Our VMs are not using the full feature set of Defender Plan 2 as we use CrowdStrike so the Defender for Endpoint functionality of the Defender for Servers Plan 2 has been disabled, but to my knowledge this shouldn't impact Vulnerability assessments. In Security Portal it does seem that generally all the VMs that healthy for this recommendation are visible in the devices section. Whereas these 45 that are not, are either not searchable or have sensor health state "inactive". We have an Azure Policy generated to onboard devices to Vulnerability assessment using MDE.Tvm and it seems to be generally working but not for these 45 devices. The Microsoft Documentation is really unclear, what do we need to make these systems compliant?629Views0likes6CommentsGuidance for handling CVE-2025-31324 using Microsoft Security capabilities
Short Description Recently, a CVSS 10 vulnerability, CVE-2025-31324, affecting the "Visual Composer" component of the SAP NetWeaver application server, has been published, putting organizations at risk. In this blog post, we will show you how to effectively manage this CVE if your organization is affected by it. Exploiting this vulnerability involves sending a malicious POST request to the "/developmentserver/metadatauploader" endpoint of the SAP NetWeaver application server, which allows allow arbitrary file upload and execution. Impact: This vulnerability allows attackers to deploy a webshell and execute arbitrary commands on the SAP server with the same permissions as the SAP service. This specific SAP product is typically used in large organizations, on Linux and Windows servers across on-prem and cloud environments - making the impact of this vulnerability significant. Microsoft have already observed active exploits of this vulnerability in the wild, highlighting the urgency of addressing this issue. Mapping CVE-2025-31324 in Your Organization The first step in managing an incident is to map affected software within your organization’s assets. Using the Vulnerability Page Information on this CVE, including exposed devices and software in your organization, is available from the vulnerability page for CVE-2025-31324. Using Advanced Hunting This query searches software vulnerable to the this CVE and summarizes them by device name, OS version and device ID: DeviceTvmSoftwareVulnerabilities | where CveId == "CVE-2025-31324" | summarize by DeviceName, DeviceId, strcat(OSPlatform, " ", OSVersion), SoftwareName, SoftwareVersion To map the presence of additional, potentially vulnerable SAP NetWeaver servers in your environment, you can use the following Advanced Hunting query: *Results may be incomplete due to reliance on activity data, which means inactive instances of the application - those installed but not currently running, might not be included in the report. DeviceProcessEvents | where (FileName == "disp+work.exe" and ProcessVersionInfoProductName == "SAP NetWeaver") or FileName == "disp+work" | distinct DeviceId, DeviceName, FileName, ProcessVersionInfoProductName, ProcessVersionInfoProductVersion Where available, the ProcessVersionInfoProductVersion field contains the version of the SAP NetWeaver software. Optional: Utilizing software inventory to map devices is advisable even when a CVE hasn’t been officially published or when there’s a specific requirement to upgrade a particular package and version. This query searches for devices that have a vulnerable versions installed (you can use this link to open the query in your environment): DeviceTvmSoftwareInventory | where SoftwareName == "netweaver_application_server_visual_composer" | parse SoftwareVersion with Major:int "." Minor:int "." BuildDate:datetime "." rest:string | extend IsVulnerable = Minor < 5020 or BuildDate < datetime(2025-04-18) | project DeviceId, DeviceName, SoftwareVendor, SoftwareName, SoftwareVersion, IsVulnerable Using a dedicated scanner You can leverage Microsoft’s lightweight scanner to validate if your SAP NetWeaver application is vulnerable. This scanner probes the vulnerable endpoint without actively exploiting it. Recommendations for Mitigation and Best Practices Mitigating risks associated with vulnerabilities requires a combination of proactive measures and real-time defenses. Here are some recommendations: Update NetWeaver to a Non-Vulnerable Version: All NetWeaver 7.x versions are vulnerable. For versions 7.50 and above, support packages SP027 - SP033 have been released and should be installed. Versions 7.40 and below do not receive new support packages and should implement alternative mitigations. JIT (Just-In-Time) Access: Cloud customers using Defender for Servers P2 can utilize our "JIT" feature to protect their environment from unnecessary ports and risks. This feature helps secure your environment by limiting exposure to only the necessary ports. The Microsoft research team has identified common ports that are potential to be used by these components, so you can check or use JIT for these. It is important to mention that JIT can be used for any port, but these are the most common ones. Learn more about the JIT capability Ports commonly used by the vulnerable application as observed by Microsoft: 80, 443, 50000, 50001, 1090, 5000, 8000, 8080, 44300, 44380 Active Exploitations To better support our customers in the event of a breach, we are expanding our detection framework to identify and alert you about the exploitation of this vulnerability across all operating systems (for MDE customers). These detectors, as all Microsoft detections, are also connected to Automatic Attack Disruption, our autonomous protection vehicle. In cases where these alerts, alongside other signals, will allow for high confidence of an ongoing attack, automatic actions will be taken to contain the attack and prevent further progressions of the attack. Coverage and Detections Currently, our solutions support coverage of CVE-2025-31324 for Windows and Linux devices that are onboarded to MDE (in both MDE and MDC subscriptions). To further expand our support, Microsoft Defender Vulnerability management is currently deploying additional detection mechanisms. This blog will be updated with any changes and progress. Conclusion By following these guidelines and utilizing end-to-end integrated Microsoft Security products, organizations can better prepare for, prevent and respond to attacks, ensuring a more secure and resilient environment. While the above process provides a comprehensive approach to protecting your organization, continual monitoring, updating, and adapting to new threats are essential for maintaining robust security.6.6KViews0likes0CommentsCost Calculator for Defender for Cloud (Public Preview)
Did you know Microsoft Defender for Cloud has a built-in cost calculator to easily calculate the costs of protected resources in your cloud environment? No? Well, I didn’t either until I stumbled upon the button in the MDC portal myself. Apparently, Microsoft announced the preview for the MDC cost calculator last month, on February 19, 2025. With this post, I’m sharing my experience with this new cost calculator for Microsoft Defender for Cloud, providing guidance and comparing available options to calculate the costs. https://myronhelgering.com/cost-calculator-for-defender-for-cloud/675Views0likes0Comments
No automatic MDE.Windows installation anymore
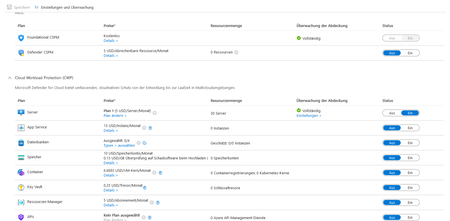
We have an Azure subscription to which our on-premises servers are connected via Azure Arc. Actually, only Microsoft Defender for Servers Plan 1 should be used. However, ‘Plan 2’ is billed in the cost analyses, which leads to significantly higher costs than planned. I´ve fixed it but it lead to the Problem of not installing MDE.Windows anymore. The servers are connected to Azure by executing a script, after which some plugins are installed(MDE.Windows, MicrosoftMonitoringAgent, and on some servers "WindowsPatchExtension"). In the environment management of Defender for Cloud we have explicitly selected plan 1, despite this plan 2 is activated for each server. There is no Log-Workspace. Here are the Policies, i think they go automaticly created by Azure. I´ve deleted "ASC provisioning LA agent Windows Arc" and the linux one because this is deploying the two Extensions "MicrosoftMonitoringAgent" and "WindowsPatchExtension", which activate Plan 2. After deleting those to Extensions i should not get billed as Plan 2 anymore. My Problem is now that i don´t have the policy to install the MDE Plugin anymore. How do i get this working again, i need to install only the MDE Plugin on the computers to ensure we only use Plan 1. No other extensions, no Log-Workspace... Appreciate the help.456Views0likes0CommentsMicrosoft Defender for Cloud Customer Newsletter
What's new in Defender for Cloud? Defender for Cloud’s CSPM sensitive scanning capabilities now include Azure files. This feature is in GA. Learn more about it here. File integrity monitoring (FIM) update Staring June 2025, FIM requires a minimum Defender for Endpoint (MDE) client version. For Windows devices, please make sure you have Windows 10.8760 or later and for Linux, 30.124082. For more details, please refer to our documentation. Blogs of the month In December, our team published the following blog posts we would like to share: AKS Security Dashboard Strategy to Execution: Operationalizing Microsoft Defender CSPM MDC Named a Leader in Frost Radar TM for CNAPP for the 2nd Year in a Row! GitHub Community Learn more about MDC and XDR integration by following this lab – module 25. Visit our GitHub page. Defender for Cloud in the field MDC Ignite updates 2024 Cloud detection response (CDR) for Defender for Containers Improvements in Container's posture management Visit our YouTube page! Customer journey Discover how other organizations successfully use Microsoft Defender for Cloud to protect their cloud workloads. This month we are featuring Properstar, a leading real estate platform, partnered with Microsoft to simplify unstructured real estate data and leverage dynamic AI-powered solutions like Azure Open AI to provide relevant search results. Then, they were able to scale up, using Defender for Cloud to implement data protection and regulatory compliance. Security community webinars Join our experts in the upcoming webinars to learn what we are doing to secure your workloads running in Azure and other clouds. Check out our upcoming webinars this month in the link below! I would like to register Watch past webinars We offer several customer connection programs within our private communities. By signing up, you can help us shape our products through activities such as reviewing product roadmaps, participating in co-design, previewing features, and staying up-to-date with announcements. Sign up at aka.ms/JoinCCP. We greatly value your input on the types of content that enhance your understanding of our security products. Your insights are crucial in guiding the development of our future public content. We aim to deliver material that not only educates but also resonates with your daily security challenges. Whether it’s through in-depth live webinars, real-world case studies, comprehensive best practice guides through blogs, or the latest product updates, we want to ensure our content meets your needs. Please submit your feedback on which of these formats do you find most beneficial and are there any specific topics you’re interested in https://aka.ms/PublicContentFeedback. Note: If you want to stay current with Defender for Cloud and receive updates in your inbox, please consider subscribing to our monthly newsletter: https://aka.ms/MDCNewsSubscribe743Views0likes0Comments
"Duplicate" alerts in Defender for Cloud from MDE
Hello, I discovered that security alerts generated from Defender for Endpoint are causing "duplicate" security alerts in Defender for Cloud. We have several Azure Arc-enabled servers active with Defender for Server P1 which includes Defender for Endpoint integration. Hence Arc servers are automatically onboarded to Defender for Endpoint. We had a false positive caused by the addition of AV exclusions which generated an alert / incident in Defender XDR which was then synced to Sentinel. Closing the alerts in Defender XDR or Sentinel resulted in synced status between the two. However it seems the same alerts were also created in Defender for Cloud, and their status remained "open" even after being resolved in Defender XDR. The link in the open Defender for Cloud Alert effectively opens up the resolved alert in Defender XDR. So it seems to be the same alert but its status is not being synced. Is this a known issue?353Views0likes1Comment