microsoft defender for cloud apps
85 Topics
New Blog Post | Prioritize Risk remediation with Microsoft Defender for Cloud Attack Path Analysis
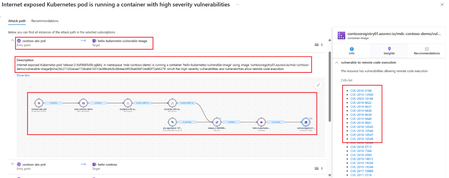
Prioritize Risk remediation with Microsoft Defender for Cloud Attack Path Analysis - Microsoft Community Hub Our previous blogs “A Proactive Approach to Cloud Security Posture Management with Microsoft Defender for Cloud,” and "Proacting Hunting with Cloud Security Explorer in Defender for Cloud - Microsoft Community Hub" emphasized the importance of proactive security posture management and outlined a successful organizational structure for security teams. As a follow up article here we walk you through the scenarios how to identify and mitigate the biggest security risk issues while distinguishing them from less risky issues. Cloud environments are dynamically changing and to support rapidly changing threat and business environments in near real time, security teams need to act rapidly and effectively to mitigate risks and protect sensitive data and critical systems. Though cloud security solutions detect vulnerabilities and misconfigurations, growing number of assets can mean hundreds or thousands of security recommendations, overwhelming the security professionals to remediate the risks. By using Microsoft Defender for Cloud Attack Path Analysis, organizations can gain a better understanding of the potential attack paths that an attacker may take to compromise their cloud environment. This enables security professionals to prioritize risk remediation efforts and focus their resources on the most critical vulnerabilities and risks, to improve their overall security posture. To understand the prerequisites to Identify and remediate attack paths, visit: Identify and remediate attack paths - Defender for Cloud | Microsoft Learn Security administrators can use attack path analysis for risk remediation by following these steps: Identify the Attack Paths: The first step is to identify the attack paths that an attacker might take to exploit vulnerabilities in the system. This includes mapping out the various components of the system, identifying the entry points, and analyzing the potential paths that an attacker might take. Analyze the Risks: After identifying the attack paths, the next step is to analyze the risks associated with each path. This includes evaluating the likelihood and impact of a successful attack and identifying the potential consequences for the organization. Prioritize Remediation Efforts: Based on the analysis of the risks, security administrators should prioritize their remediation efforts. This includes focusing on the most critical vulnerabilities and attack paths that present the greatest risk to the organization. Develop and Implement Mitigation Strategies: After prioritizing remediation efforts, security administrators should develop and implement mitigation strategies to address the identified vulnerabilities and attack paths. Test and Monitor: After implementing mitigation strategies, it is important to monitor the system to ensure that the vulnerabilities have been addressed and the attack paths have been closed. Security administrators need to proactively use the Attack Paths to ensure all critical paths are remediated Original Post: New Blog Post | Prioritize Risk remediation with Microsoft Defender for Cloud Attack Path Analysis - Microsoft Community HubMy learning path to become a Microsoft Certified: Security Operations Analyst Associate (SC-200)!
Dear Microsoft 365 / Azure Security Friends, To be completely honest, I really had the absolute greatest respect for this test. Why, quite simply Kusto Query Language (KQL) was not necessarily my strength until now. But since this is exactly a big part of this exam, there was already some "discomfort" with it. But exactly this "discomfort" was the motivation to take on KQL to acquire the knowledge. In this exam you will be quizzed on topics in Azure Sentinel, Azure Security Center, Microsoft 365 Defender. This spectrum is huge, please take enough time to "explore" these "portals" deeply. This was among other things my way to success! Now to my preparations for the exam: 1. First of all, I looked at the Exam Topics to get a first impression of the scope of topics. https://docs.microsoft.com/en-us/learn/certifications/security-operations-analyst/ Please take a close look at the skills assessed: https://query.prod.cms.rt.microsoft.com/cms/api/am/binary/RE4Myp4 2. So that I can prepare for an exam I need an Azure test environment (this is indispensable for me). You can sign up for a free trial here. https://azure.microsoft.com/en-us/free/ Next, I set up a Microsoft 365 test environment. You can sign up for a free trial here. https://www.microsoft.com/en-us/microsoft-365/business/compare-all-microsoft-365-business-products I chose the "Microsoft 365 Business Premium" plan for my testing. 3. Now it goes to the Microsoft Learn content. These learn paths (as you can see below, all 😎 I have worked through completely and "mapped"/reconfigured as much as possible in my test environment. https://docs.microsoft.com/en-us/learn/paths/sc-200-mitigate-threats-using-microsoft-defender-for-endpoint/ https://docs.microsoft.com/en-us/learn/paths/sc-200-mitigate-threats-using-microsoft-365-defender/ https://docs.microsoft.com/en-us/learn/paths/sc-200-mitigate-threats-using-azure-defender/ https://docs.microsoft.com/en-us/learn/paths/sc-200-utilize-kql-for-azure-sentinel/ https://docs.microsoft.com/en-us/learn/paths/sc-200-configure-azure-sentinel-environment/ https://docs.microsoft.com/en-us/learn/paths/sc-200-connect-logs-to-azure-sentinel/ https://docs.microsoft.com/en-us/learn/paths/sc-200-create-detections-perform-investigations-azure-sentinel/ https://docs.microsoft.com/en-us/learn/paths/sc-200-perform-threat-hunting-azure-sentinel/ 4. Register for the exam early. This creates some pressure and you stay motivated. https://docs.microsoft.com/en-us/learn/certifications/security-operations-analyst/ 5. Please also have a look at Thomas Maurer's website! https://www.thomasmaurer.ch/2021/03/new-microsoft-security-certification-exams-in-beta/ 6. The Azure Sentinel book from the Microsoft Press Store has also been super helpful to me! https://www.microsoftpressstore.com/store/microsoft-azure-sentinel-planning-and-implementing-9780136485452 I know you've probably read and heard this many times: read the exam questions slowly and accurately. Well, that was the key to success for me. It's the details that make the difference between success and failure. One final tip: When you have learned something new, try to explain what you have learned to another person (whether or not they know your subject). If you can explain it in your own words, you understand the subject. That is exactly how I do it, except that I do not explain it to another person, but record a video for YouTube! I hope this information helps you and that you successfully pass the exam. I wish you success! Kind regards, Tom WechslerDevice is showing as Non-Compliant when login from Chrome
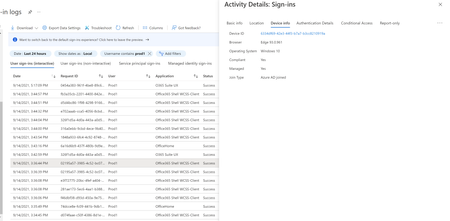
Hi All, I have created a Conditional access policy and session based access policy in MCAS to block download of sensitivity data from unmanaged device. everything is working fine when I login from Edge browser, but I concern is When I login from Chrome within Azure AD joined client that it's saying non-compliant. However When I login from Edge browser within same client, it will be showing as compliant in sign-in logs. appreciate the help! Thanks, DilanSolved7.9KViews0likes3Comments
A bug in the sign in with Security Key option for M365
1. Register a pair of keys in M365. 2. On a PC you are presented with an option to sign in with a security key! 3. On a MAC you are presented with an option to sign in with a security key! 4. On ChromeOS you are not presented with that option. ChromeOS supports FIDO2 and it works on many other sites. It is only M365 that has this issue. As a Partner I reached out to Microsoft support, who said Microsoft has dropped all support for ChromeOS. I do not expect to run Word on a Chromebook, but I can run the web version of any of Microsoft tools on a Chromebook. Why then, can I not have the same level of security on my account that I could if I was accessing the site on a PC or Mac? Microsoft should fix this bug if they really care about security of their customer's accounts, no matter how they access the site.My learning path to the Microsoft Certified: Identity and Access Administrator Associate (SC-300)!
Dear Microsoft 365 / Azure Security Friends, I thought that I have already done so much in Azure on the subject of identity and access, this test can not be so difficult! Wrong, absolutely wrong setting Tom! With exactly such a view it just does not work for me. So back to field 1! What was a big challenge for me, among other things, was to understand the different roles in Azure. For example; Application Administrator, Application Developer, Cloud Application Administrator are all familiar to me! BUT, what can one role do but not the other? That's where the challenge lies and that's one of the things I had to face. Now this is just an example, but it should show you that it's the details that matter! In this exam you will be quizzed on topics in Azure Apps, Azure Identity, Azure Identity Governance, etc. This spectrum is huge, please take enough time to "explore" all the topics described in the Skills measured! This was among other things my way to success! Now to my preparations for the exam: 1. First of all, I looked at the Exam Topics to get a first impression of the scope of topics. https://docs.microsoft.com/en-us/learn/certifications/identity-and-access-administrator/ Please take a close look at the skills assessed: https://query.prod.cms.rt.microsoft.com/cms/api/am/binary/RE4Mr7Z 2. So that I can prepare for an exam I need an Azure test environment (this is indispensable for me). You can sign up for a free trial here. https://azure.microsoft.com/en-us/free/ 3. Now it goes to the Microsoft Learn content. These learn paths (as you can see below, all 4) I have worked through completely and "mapped"/reconfigured as much as possible in my test environment. https://docs.microsoft.com/en-us/learn/paths/implement-identity-management-solution/ https://docs.microsoft.com/en-us/learn/paths/implement-authentication-access-management-solution/ https://docs.microsoft.com/en-us/learn/paths/implement-access-management-for-apps/ https://docs.microsoft.com/en-us/learn/paths/plan-implement-identity-governance-strategy/ 4. Register for the exam early. This creates some pressure and you stay motivated. https://docs.microsoft.com/en-us/learn/certifications/identity-and-access-administrator/ 5. Please also have a look at Thomas Maurer's website! https://www.thomasmaurer.ch/2021/03/new-microsoft-security-certification-exams-in-beta/ 6. I have compiled a list of links which were very helpful for me! https://github.com/tomwechsler/Microsoft_Cloud_Security/blob/main/Links.txt I know you've probably read and heard this many times: read the exam questions slowly and accurately. Well, that was the key to success for me. It's the details that make the difference between success and failure. One final tip: When you have learned something new, try to explain what you have learned to another person (whether or not they know your subject). If you can explain it in your own words, you understand the subject. That is exactly how I do it, except that I do not explain it to another person, but record a video for YouTube! I hope this information helps you and that you successfully pass the exam. I wish you success! Kind regards, Tom WechslerMy learning path to the Microsoft Certified Information Protection Administrator Associate (SC-400)!
Dear Microsoft 365 / Azure Security Friends, When I read the skills measured, I immediately thought this will not be easy. Of course, I have already configured several retention policies, labels, etc. But when I took a closer look at the skills measured, I immediately noticed that it would take more time to learn. Let me give you an example of this. Let's take a look at the different terms: 1. sensitive information types 2. trainable classifiers 3. sensitivity labels 4. implement encryption for email messages 5. data loss prevention policies 6. Microsoft Endpoint data loss prevention 7. retention policies and labels 8. data retention in Microsoft 365 9. records management in Microsoft 365 I don't know about you but there are so many similar words, label here and label there! Really a challenge. The skills measured do not seem so hugely extensive, but this is extremely deceptive from my point of view! Let's look at the item "encryption for email messages", which immediately means that Exchange Online is also in play. I don't know exactly how it is with you, but when was the last time you created a "mail flow rule"? Or how much have you spent in the Cloud App Security Portal lately? As I have often experienced (this is referring to me), success is in the details. Take enough time to work with the following portals and explore the details: 1. Microsoft 365 Compliance 2. Exchange Online (incl. PowerShell) 3. Cloud App Security (especially file policy) 4. Microsoft 365 Security (Endpoint section) 5. Azure Portal (Azure Information Protection) Now to my preparations for the exam: 1. First of all, I looked at the Exam Topics to get a first impression of the scope of topics. https://docs.microsoft.com/en-us/learn/certifications/information-protection-administrator/ Please take a close look at the skills assessed: https://query.prod.cms.rt.microsoft.com/cms/api/am/binary/RE4Myp6 2. So that I can prepare for an exam I need an Azure test environment (this is indispensable for me). You can sign up for a free trial here. https://azure.microsoft.com/en-us/free/ Next, I set up a Microsoft 365 test environment. You can sign up for a free trial here. https://www.microsoft.com/en-us/microsoft-365/business/compare-all-microsoft-365-business-products I chose the "Microsoft 365 Business Premium" plan and added the Microsoft 365 E5 Trial as well for my testing. 3. Now it goes to the Microsoft Learn content. These learn paths (as you can see below, all 3) I have worked through completely and "mapped"/reconfigured as much as possible in my test environment. https://docs.microsoft.com/en-us/learn/paths/implement-information-protection/ https://docs.microsoft.com/en-us/learn/paths/implement-data-loss-prevention/ https://docs.microsoft.com/en-us/learn/paths/implement-information-governance/ 4. Register for the exam early. This creates some pressure and you stay motivated. https://docs.microsoft.com/en-us/learn/certifications/information-protection-administrator/ 5. Please also have a look at Thomas Maurer's website! https://www.thomasmaurer.ch/2021/03/new-microsoft-security-certification-exams-in-beta/ 6. I have compiled a list of links which were very helpful for me! https://github.com/tomwechsler/Microsoft_Cloud_Security/blob/main/SC-400/Links.txt 7. A really great resource with video courses is Virtual Training Series from Microsoft! https://partner.microsoft.com/en-US/training/virtual-training-series I know you've probably read and heard this many times: read the exam questions slowly and accurately. Well, that was the key to success for me. It's the details that make the difference between success and failure. One final tip: When you have learned something new, try to explain what you have learned to another person (whether or not they know your subject). If you can explain it in your own words, you understand the subject. That is exactly how I do it, except that I do not explain it to another person, but record a video for YouTube! I hope this information helps you and that you successfully pass the exam. I wish you success! Kind regards, Tom WechslerNew Blog Post | Microsoft Defender Weekly Wrap - Issue #28
Microsoft Defender Weekly Wrap - Issue #28 | Revue (getrevue.co) Happy Friday everyone! This week marks the weekend just before the RSA conference kicks off. I’ll be there. I leave for an early flight on Sunday around 4am. I’m already kicking myself knowing how tired I’ll be when I arrive in San Francisco. But Sunday is big and a fully scheduled day for me. So, no rest for the weary - as they say. If any of you will be attending next week, feel free to hunt me down or look me up. I’ll be primarily in the Microsoft areas - the expo included. I won’t be hard to find. I’ll be the person sitting or standing next to a big stack of empty coffee cups. And, if you happen to bring along a copy of the Must Learn KQL book (paperback or hardcover), I’ll be happy to sign it and sit around to talk Microsoft security. … There’s a new book coming covering Defender for Cloud from Microsoft PMs, Yuri Diogenes and Tom Janetscheck, that you should keep tabs on. The listing is super new and not even available yet for pre-order, but here’s the link to bookmark for when it becomes available: https://cda.ms/4ps Amazon says it will release in November. … I’m really looking forward to the RSA conference next week. But even more than the conference itself, I’m really looking forward to connecting with this community there and I’d be sad and disappointed if you didn’t make the effort to at least say “Hi.” So, please, PLEASE look me up. I’ll be away from my family for the long week and your connection and conversation will help it go so much faster. Talk soon. -RodMCAS or 365 Security
Hey all, I'm relatively new into the industry and been tasked with championing some of our E5 platforms. We have both MCAS and MS 365 Security which I'm going to call MDE... My questions are: 1. Which one should I be using to manage alerts? a. Why can't I manage alert policies in MDE and I can in MCAS. 2. What are the differences between the two? 3. Should we even be using both of them?2.7KViews0likes3Comments
New|Microsoft Purview Data Loss Prevention: Announcing general availability of several capabilities
At Microsoft, we are committed to providing a unified and cloud-native solution that can help you prevent the loss of your sensitive data across your applications, services, and devices without the need to deploy and maintain costly infrastructure or agents. Microsoft Purview Data Loss Prevention (DLP) is an integrated, and extensible offering that allows organizations to manage their DLP policies from a single location and has a familiar user experience for both administrators and end-users. DLP is easy to turn on, doesn't require any agents and has protection built-in to Microsoft 365 cloud services, Office apps, Microsoft Edge (on Windows and Mac), and on endpoint devices. DLP controls can also be extended to the Chrome and Firefox browsers through the Microsoft Purview extension and to various non-Microsoft cloud apps such as Dropbox, Box, Google Drive, and others through the integration with Microsoft Defender for Cloud Apps. We are excited to announce the general availability of several capabilities in Microsoft Purview Data Loss Prevention that help organizations to increase their depth of protection, extend their protection capabilities to additional planes and platforms, as well as empower administrators to be efficient in their day-to-day tasks. Read the full blog here: Microsoft Purview Data Loss Prevention: Announcing general availability of several capabilities - Microsoft Community Hub