microsoft 365 apps for enterprise
290 Topics
Bookings Page - Some Error Occurred
Having an issue with a Microsoft Booking page where it keeps encountering the "Some error occurred." when loading. This Bookings page was confirmed working from creation date of May 14th, 2026 to recently, September 14th, 2026. As far as the user has told me, they had changed nothing between those dates. I had worked with the user and tried the following troubleshooting steps: 1.) I had the user switch the publishing from "Available to anyone" to "No self-service". Confirmed that the page then started showing a "Bad request" error and then changed the setting back to "Available to anyone." This did not fix the issue and the "Some error occurred" was still happening. 2.) Confirmed with the user if there was anything that changed that might be causing syncing issues between the staff calendars and the Bookings page. Found two instances (1 user who had they name changed and 1 user who went on leave of absence) and decided to see if these might be causing issues. The user who was on LOA was removed and this did not fix the issue. The user who had their name changed recently was appearing with the correct names in other Bookings pages but still had their old name in this one. Once removed and readded to this Bookings page their name was updated to be correct, but this did not solve the issue. 3.) I had the user check to see if the automated emails from the Bookings were still sending and they were confirmed to be sending. These automated emails do have specific Service links in them that are being received by customers and are working at this time. In regards to the above point, while I was working with the user who created the Bookings page, we found that the Calendar in the Bookings page was not working correctly. It does not show the Bookings that were created consistently and would usually appear blank. The Services that were created have all disappeared, but it looks like a filter is being forced. It shows "Services 52 of 0" and the user tried to remove the filter and nothing occurs. What are some next steps in troubleshooting the Bookings page?
Is there a way to create role-specific competency frameworks in Microsoft 365?
We already have a lot of employee information in Entra ID, like job title, department, manager, location, and other user attributes. What I’m trying to figure out is whether we can use those attributes to automatically assign different competency frameworks to different groups of employees. For example, engineers would have one set of competencies, sales another, and managers would have additional leadership competencies. Ideally this would update automatically when someone changes role or department in Entra rather than HR maintaining everything manually. Has anyone built something like this with Entra + SharePoint/Power Automate, or is there a better way to manage competency frameworks while still keeping Microsoft 365 as the source of employee data?271Views0likes2Comments
How much of your Microsoft 365 environment can you actually see at once?
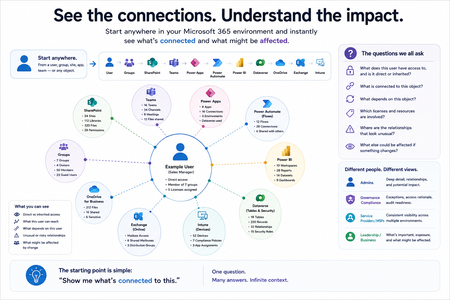
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?200Views0likes0Comments
Tracking whether managers actually complete their review cycles on time
Every quarter our HR team has to chase managers who havent finished their performance reviews. Right now they literally track it in an Excel spreadsheet and send reminder emails manually. Its embarrassing honestly. We're an M365 shop and I feel like there should be a way to automate this or at least get some visibility into completion rates without it being a manual process. Whats everyone else doing?316Views0likes3CommentsAutoSave disabled when opening SharePoint-synced files from Finder after macOS Tahoe 26.6 update
Files stored in SharePoint Online and synchronized locally through OneDrive are opened as local documents when launched from Finder. Office applications display "Saved to my Mac" and AutoSave is turned off by default. However, opening the exact same files through Word/Excel > Open > Sites, or via SharePoint "Open in Desktop App", correctly identifies them as cloud documents. In that scenario, AutoSave is enabled and collaboration/version history features work as expected. Troubleshooting already performed: OneDrive reset and re-linked SharePoint library re-synced Signed out and back into both Office and OneDrive Removed Microsoft credentials from macOS Keychain and re-authenticated Recreated local OneDrive sync relationships Verified OneDrive File Provider extensions are enabled Verified Office applications and OneDrive are fully up to date Tested with newly created files and existing files Tested "Always Keep on This Device" with no change in behavior The issue appears to be specific to the Finder-to-Office launch path after upgrading to macOS Tahoe 26.6. Before upgrading to macOS Tahoe 26.6, opening the same SharePoint-synchronized files directly from Finder correctly preserved cloud document identity and AutoSave was enabled as expected. I discussed this issue in detail with Apple Support, but they quickly dismissed it, saying that the problem is not on Apple's side and that I should contact Microsoft instead.3.6KViews13likes38CommentsNew Entra ID group device criteria scoping is missing from Cloud Update
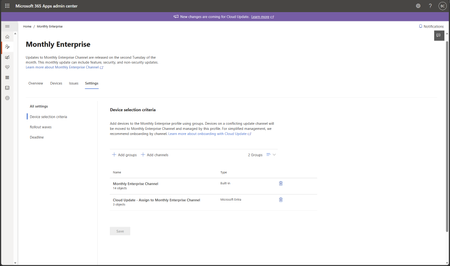
Hi, the New Entra ID group device criteria scoping is missing from Cloud Update. Message center says that it should be GA late July, but here we are and it's still not there. Is there a way to know when should we expect it to rollout for real? Thks in advance and don't hesitate if you have any questionsSolved247Views0likes3Comments
How can specific users be exempted from a tenant-scoped Microsoft 365 Apps Policy?
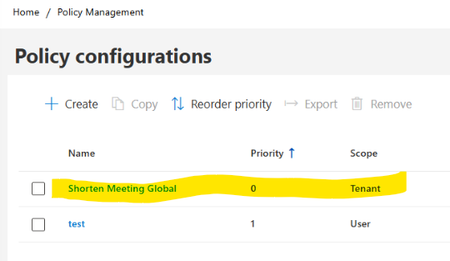
Hello, I am looking for guidance regarding Microsoft 365 Apps Cloud Policy Service behavior and policy precedence. Current configuration: In Microsoft 365 Apps Admin Center → Policy Management (config.office.com), we have the following policies: Policy 1 Name: Shorten Meeting Global Scope: Tenant Priority: 0 Configured settings: Shorten appointments and meetings = Enabled Reduce the end time of short appointments and meetings = 5 minutes Reduce the end time of long appointments and meetings = 10 minutes Policy 2 Name: Test Scope: User (Security Group) Priority: 1 Assigned only to a dedicated test group Relevant settings configured as Not Configured Observed client behavior: On corporate-managed devices, affected users receive the following registry values: HKCU\Software\Policies\Microsoft\Cloud\Office\16.0\Outlook\Options\Calendar shortenevents = End_Early endearlyshort = 5 endearlylong = 10 The Outlook option: File > Options > Calendar > Shorten appointments and meetings is greyed out. Additional validation: Using the same Microsoft 365 account on an external non-corporate device: The above registry path is not present. The Outlook option is editable. Testing performed: A user-scoped Cloud Policy was created and assigned to a dedicated security group. For the "Shorten appointments and meetings" setting, only the following options are available: Enabled Not Configured There is no Disabled option. but the Tenant policy continued to apply and the Outlook option remained locked. Questions Is there a supported way to exempt specific users from a tenant-scoped Microsoft 365 Apps Cloud Policy when the setting only supports "Enabled" and "Not Configured" and does not provide a "Disabled" option? Does Not Configured in a User-scoped policy allow evaluation to continue to the lower-priority Tenant policy? If policy precedence is changed so that: Test Policy = Priority 0 Tenant Policy = Priority 1 would the User policy potentially suppress the Tenant setting? Is there a supported way in Microsoft 365 Apps Cloud Policy Service to provide exceptions for specific users while keeping the Tenant policy as the organizational default? Has anyone successfully implemented an exclusion or override scenario for the "Shorten appointments and meetings" setting? Any guidance or documentation references would be greatly appreciated. Thank you.