mde
10 TopicsMulti-tenant endpoint security policies distribution is now in Public Preview
We’re excited to announce a key milestone in Defender’s multi-tenant management journey—Microsoft Defender for Endpoint security policies can now be distributed across multiple tenants from the Defender multi-tenant portal. This capability empowers security teams to manage policies at scale, ensuring consistency and saving valuable time. What is content distribution? Content distribution is a powerful Defender feature that enables scalable management of content across tenants. With this capability, you can create content distribution profiles in the multi-tenant portal that allow you to seamlessly replicate existing content—such as custom detection rules and now, endpoint security policies—from a source tenant to designated target tenants. Once distributed, the content runs on the target tenant, enabling centralized control with localized execution. How it works Security policies are now a selectable content type when creating a distribution profile. Simply choose existing policies from your home tenant and add them to the distribution profile. You can also decide which Microsoft Entra group(s) will be applied as scope. Policy targeting will be based on the Entra device groups that exist in every tenant, and you select the relevant groups for each tenant. Upon completion, policies are automatically distributed to the selected tenants and are applied on the targeted machines. Distributed policies also appear in a hierarchical view, with the original policy serving as the parent. You can find the policies that were distributed from the tenant under the original policy. This appears on the endpoint security policies page within multi-tenant management. The last distribution status for the original policy reflects the overall status of its distributed copies, and the tenants and tenant groups sections indicate the recipients of the policy. At any time, you can update the policies, tenants, scope or any other settings, and sync to apply these changes. This new capability enables consistency (maintaining uniform security posture across tenants), efficiency (eliminating manual duplication and reducing operational overhead), and scalability (easily expanding coverage as the tenant landscape grows). FAQ What pre-requisites are required? Access to more than one tenant with Microsoft Defender for Endpoint, with delegated access via Azure B2B or GDAP (CSP Partners only), using the multi-tenant management capability. A subscription to Microsoft 365 E5 or Office E5. What permissions are needed to distribute MDE security policies? To access endpoint security policies, users require the security administrator role in each relevant tenant. To distribute content using multi-tenant management content distribution, the Security settings (manage) or Security Data Basic (read) permission is required. Both roles are assigned to the Security Administrator and Security Reader Microsoft Entra built-in roles by default. Can I update or expand distribution profiles later? Yes. You can add more content, include additional tenants, or modify scopes as needed. Learn more For more information, see Content distribution in multitenant management. To get started, navigate to the Content distribution page. To learn more about Microsoft Defender's endpoint protection, check out our website and video. To learn more about Microsoft Security solutions, visit our website. Bookmark the Security blog to keep up with our expert coverage on security matters. Follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.
Can I check whether an IoC/hash is already monitored by MDE?
The list of IoC is limited to 15k. I imagine some IoCs entries from our "custom list" are already monitored by Microsoft/MDE. So, is there a way to check whether there is a detection rule for a specific IoC (hash)? This would save us some thousand entries and improve our monitoring coverage. *Better to join forces than reinvent the wheel.3.5KViews1like3Comments
Microsoft Defender for Endpoint Plan 1 Now Generally Available
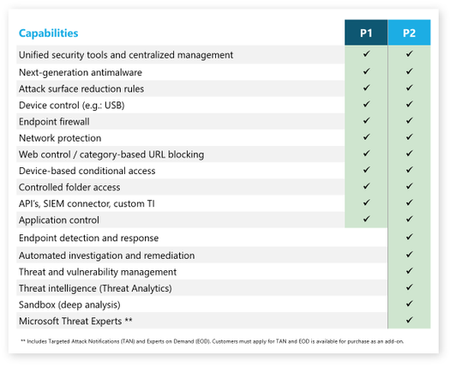
We are excited to announce the General Availability of Microsoft Defender for Endpoint Plan 1 (P1). Defender for Endpoint P1 demonstrates Microsoft’s commitment to delivering best of breed, multi-platform, and multi-cloud security for all organizations across the globe, providing a foundational set of our market leading endpoint security capabilities for Windows, macOS, Android, and iOS at a lower price point.
Boost protection of your Linux estate with behavior monitoring, extended distro coverage, and more
Microsoft protection for your Linux estate is getting an impressive boost across the full spectrum of the security suite. We are thrilled to share the latest news about Microsoft Defender for Endpoint on Linux next generation protection, endpoint detection and response (EDR), threat and vulnerability management (TVM).where can I see the "detection build id/number"?
Where can I see the "detection build id/number". For example, at https://msrc.microsoft.com/update-guide/vulnerability/CVE-2021-40444 it says; "Enterprise customers who manage updates should select the detection build 1.349.22.0 or newer and deploy it across their environments." I would like to know what version do my customer have deployed.Solved2.5KViews0likes1Comment
Permission required to import to Indicators page? Error "Failed to Import Indicators"
Hello, Do you need the permission "Manage security settings in Security Center" in order to import xslx to Indicators? User getting error "Failed to import indicators. User is not exposed to all Indicator's machine groups. Contact your administrator for further information." User is in role. Role is setup with a group that has all the permissions expect "Manage security settings in Security Center". Role also has access to device groups that are setup. https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/user-roles?view=o365-worldwide#permission-options -Link above doesn't list "Indicators" in permission options Can not find the answer based on Googling Thanks!2.2KViews0likes0CommentsDefender for Endpoint - Data Storage Location integrity question (GDPR/EU)
Hi, I have a question specific to Defender for Endpoint and its data storage within EU and the information provided on Microsoft Docs. The english text states customer data in psuedonymized form may also be stored and processed in US. Data storage location Defender for Endpoint operates in the Microsoft Azure datacenters in the European Union, the United Kingdom, or in the United States. Customer data collected by the service may be stored in: (a) the geo-location of the tenant as identified during provisioning or, (b) if Defender for Endpoint uses another Microsoft online service to process such data, the geolocation as defined by the data storage rules of that other online service. Customer data in pseudonymized form may also be stored in the central storage and processing systems in the United States. Once configured, you cannot change the location where your data is stored. This provides a convenient way to minimize compliance risk by actively selecting the geographic locations where your data will reside. <https://eur02.safelinks.protection.outlook.com/?url=https%3A%2F%2Fdocs.microsoft.com%2Fen-us%2Fmicrosoft-365%2Fsecurity%2Fdefender-endpoint%2Fdata-storage-privacy%3Fview%3Do365-worldwide&data=04%7C01%7C%7C1404cf212ff34bf4979e08d9333620bc%7C15d06cbf5ba64055954d531141e50e6c%7C0%7C0%7C637597130888246031%7CUnknown%7CTWFpbGZsb3d8eyJWIjoiMC4wLjAwMDAiLCJQIjoiV2luMzIiLCJBTiI6Ik1haWwiLCJXVCI6Mn0%3D%7C1000&sdata=29la4wV9ktedgf0s7ssq58fQ702nsI2oQRTUGc41lFw%3D&reserved=0> OK, I get that. What I don't get is that on the corresponding Docs site in Swedish, the machine-translation instead presents the word "anonymiserad" which in English is "anonymized" which is a completely different thing. Is this a bug? What is actually correct here and where can I find information about this? The following is in swedish, link/Source at the bottom: Datalagringsplats Defender för Endpoint fungerar Microsoft Azure datacenter i EU, Storbritannien eller USA. Kunddata som samlas in av tjänsten kan lagras i: (a) klientorganisationens geoplats som identifieras under etableringen eller(b) om Defender för Endpoint använder en annan Microsoft-onlinetjänst för att bearbeta sådana data, den geolokalisering som definieras av datalagringsreglerna för den andra onlinetjänsten. Kunddata i anonymiserad form kan också lagras i de centrala lagrings- och bearbetningssystemen i USA. När den har konfigurerats kan du inte ändra platsen där dina data lagras. Det här är ett bekvämt sätt att minimera efterlevnadsrisken genom att aktivt välja de geografiska platser där dina data ska lagras. <https://eur02.safelinks.protection.outlook.com/?url=https%3A%2F%2Fdocs.microsoft.com%2Fsv-se%2Fmicrosoft-365%2Fsecurity%2Fdefender-endpoint%2Fdata-storage-privacy%3Fview%3Do365-worldwide&data=04%7C01%7C%7C1404cf212ff34bf4979e08d9333620bc%7C15d06cbf5ba64055954d531141e50e6c%7C0%7C0%7C637597130888246031%7CUnknown%7CTWFpbGZsb3d8eyJWIjoiMC4wLjAwMDAiLCJQIjoiV2luMzIiLCJBTiI6Ik1haWwiLCJXVCI6Mn0%3D%7C1000&sdata=M5N09JM9glwHRV8ztMUZhZyVGBxhQsjaAq8w70%2FqEbk%3D&reserved=0>4.6KViews0likes1Comment
Defender for Endpoint - EDR Block Mode
Hi All, Is there anyway to verify that MDE is in block on mode on any given endpoint? Is there a powershell command or similar we can use to verfy that EDR Block Mode is actually enabled? Other than having it turned on in the Security Center's Advance Features section? I have it turned on yet I see some Endpoints still showing security recommendations to turn it on. Freshly onboarded and latest version of windows 10. Defender is in active mode. Any ideas? Thanks in advance.1.2KViews1like0Comments