configuration
59 Topics
Azure AD Premium P1 features without AADP1 license assigned
Dear community, I have noticed that our Azure AD tenant overview shows that we are using Azure AD Premium P1. However, we have never purchased Azure AD Premium P1 add-on licenses. We use Office 365 E3 and E1 plans, which do not include AADP1. The premium features work, though. We can use conditional access, which is actually intended only for premium tenants, and we can also add a custom login screen with our company logo for Office sign-ins. We are a bit puzzled about how this could be. We have checked our tenant again, but we have never activated Azure AD Premium P1 for the entire tenant or assigned any licenses that include AADP1. Is there an explanation for this? Has anyone else been affected by this? Of course, we want to ensure that our tenant is correctly licensed and used, and we wonder if we are obliged to purchase AADP1 licenses, even though we have never made any configuration changes to our tenant that would introduce AADP1. Thank you very much and best regards.7.4KViews0likes11Comments
Enable Guests to be able to send email to Group
The goal of this post is to find a way to allow specific external users to send an email message to a Group. I wish to do this via whitelist: I do not want to allow all external users to message the group. I also do not want to require the external user to be a member of the Group they wish to message (e.g. via a Guest User account). With this framework in mind, let me lay out how I think the permissions operate natively on the system... By design, both internal User Accounts and external parties can send email to other User Accounts on an MS 365 tenant. However, also by design, while internal User Accounts can send a message to a Group, external parties cannot send an email to a Group: Can send email to User Can send email to Group that sender is not a Member of User Accounts on the tenant Yes Yes External users not registered on the tenant Yes No [If I have any of the above wrong, I would welcome your corrections!] The red "No" permission above can be altered by enabling the "Let people outside the organization email this team" setting for the Group. Flipping this bit to enabled, however, is a global setting which allows all external parties to send emails to the Group's email address; that creates a spam risk. I am looking for a way to create a whitelist of allowed email address(es) and/or domain(s) that are able to message a specific Group and/or all Groups. I had presumed that creating a Guest User would address the issue. But to my understanding Guest Users cannot send an email to a Group unless they are Member of that Group. Effectively Guest Users are treated like external senders in this respect: Can send email to User Can send email to Group that sender is not a Member of User Accounts on the tenant Yes Yes Guest Accounts on the tenant Yes No External users not registered on the tenant Yes No I have crawled all over the Admin Centers for MS 365, Exchange, Entra, and Teams and I am just not finding a setting that allows me to create a whitelist of authorized external users (or domains) that can message a specific Group (or all Groups). I have also searched the Internet widely to no avail. Does anyone know how to do this? I suspect that PowerShell is the way to go, a tool I am barely competent in. But I am willing to try! If PowerShell can be used to grant the proper permissions I would appreciate it if you could recommend the specific version of PowerShell I should use on Windows (e.g. Windows PowerShell) and the specific Micrisoft Graph cmdlet(s) I should access. Thank you for your time and wisdom!6.3KViews0likes4CommentsHow to correctly implement Entra ID Connect sync when users exists in Entra ID as cloud users?
Hi Everyone, I have a small on-premises exchange server 2016 setup which we're planning to make Hybrid. We do have a O365 environment (Business Standard Licensed) which is independent as users signed in for Teams and SharePoint Online usage. We now have to implement Entra ID Connect (Azure AD Connect) to facilitate Exchange Hybrid deployment. My questions are: 1. These users currently exists in Entra ID as cloud accounts (as they've been using Cloud Apps such as Teams, SPO with their Windows 10 joined to Entra ID) will there be any issues when sync is configured ? (i.e. duplicate of identity errors etc..) 2. What's the best approach to implement Entra ID Connect and sync these user from AD to Engtra ID without having to remove these accounts from Entra ID? Any inputs are highly appreciated ! Thank you!6.2KViews0likes2CommentsCross-tenant synchronization (Private mode)
Cross-tenant synchronization enables you to automate provisioning identities across tenants in your organization and simplify collaboration within your organization. In addition, automate removing accounts when users don't need access and keep accounts synchronized across tenants. This feature will not appear on all tenants until Microsoft releases it as preview.6KViews2likes4Comments
Problems configuring federation to SAML IdP
Hi. I'm trying to configure our Entra domain to federate to our existing IdP, following the guidance found https://learn.microsoft.com/en-us/entra/identity/hybrid/connect/how-to-connect-fed-saml-idp#supported-bindings and am having real problems when it comes to using the Microsoft Graph API in PowerShell. After eventually working out what permissions I needed to request (more than what is stated in the doc), I ran the New-MgDomainFederationConfiguration cmdlet, and received the following error: "FederatedIdpMfaBehavior cannot be empty" This parameter is not mentioned in the doc either. So, then I added that parameter, and got the following: "Domain already has Federation Configuration set." But when I run Get-MgDomainFederationConfiguration, I get: "Resource 'federationConfiguration' does not exist or one of its queried reference-property objects are not present." When I run Get-MgDomain, AuthenticationType shows as "Federated", but I still see a managed login when I check. So I seem to be stuck with it seemingly half-configured, with no way to view or remove the configuration. Any ideas? Thanks, Nick5.8KViews0likes7Comments
Disabling PIN-based login on Entra-joined PCs
Hi guys. Yesterday I took two machines off the domain and Entra joined them. The goal was 1) remove their access to domain resources 2) have tenant users login to the machine and get enriched tokens every time. this works as desired. The problem is every user gets prompted to set a pin. these are both shared secondary/tertiary PC's - there is no point to having a 6 digit PIN on them. I thought the new Authentication Methods tools had controls for this, but apparently not. A script was run to change certain related Reg Keys (by my onsite tech) but this had no change on reboot. textreg add "HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\PassportForWork" /v Enabled /t REG_DWORD /d 0 /freg add "HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\PassportForWork" /v DisablePostLogonProvisioning /t REG_DWORD /d 1 /f HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\PassportForWork Enabled key was set to 0, and DisablePostLogonProvisioning was set to 1. These are from various help threads I found here and other resources. Unfortunately, they do not work. Not sure what to do here. I've read there are InTune controls for this - but I don't really have the time to work out WindowsPC ennrollment profiles for 2 machines. The site has InTune, but only for iOS mobile management. Thoughts?5.6KViews0likes7CommentsIssue after sync with Azure AD Connet
Hello, I'm trying to do some experiments with Azure AD Connet and found some issue and I like to find some suggestion from other experienced people on how to manage them. First thing I noticed is with the registered devices: I simulated my organization, so I created some virtual machine where I installed Office desktop apps and Teams; the devices are seen in AAD as Azure AD Registered; then I've done the sync of the devices from AD; I have an OU with inside our org accounts, so I have, for example, an inner Management OU with management user accounts; inside Management OU I have an OU called Management Computers where there are the management's devices; I have synced them and then enabled the Hybrid Join in Azure AD Connect. I've seen that the devices have been registered as Hybrid Join, but I have the situation where there are the duplicated devices; on every system, there is a Windows 10 version greated than 1803; I waited 2 days but never happened: I red some people that deleted the Azure registered one, but have red also that people have experiecenced issue to do so. Other question: I synced my users and it seems was all ok, so I saw in AAD Users->All Users the parameter "Directory synced" on Yes; after some delta sync I saw that a user that was synced that have no more Yes on that parameter and a new user, with that parameter was created; I deleted it and done a sync but on the old user I can't see that directory sync is again true: how to resolve this issue? Apart from these problems, I'd like to have a suggestion on how proceed when I have to sync real data; as I said previuosly, I have nested OU with users and their computers, but I don't want to sync all the users together; for example, I thought to sync first OU Managers (and their devices), than Marketing (and their computers) and so on: do you think this is an acceptable approach or I have to change it? Any help is very appreciated.5.6KViews0likes9CommentsTenant restrictions (Preview) - Tenant restriction settings
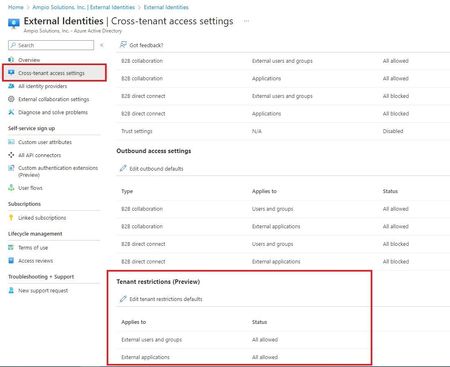
Tenant restrictions lets you control whether your users can access external applications from your network or devices using external accounts, including accounts issued to them by external organizations and accounts they've created in unknown tenants.4.7KViews0likes4Comments