azure
25 Topics
401 Error using PnP PowerShell in Azure Runbooks
Trying to get PnP PowerShell cmdlets to work within an Azure Runbook with modern authentication (no username/password). I tried registering an Azure AD app and a Service Principal (Run as account) from the automation account that hosts the Runbook. Both use a certificate thumbprint and authorization itself doesn't throw an error. Here's the code I'm using: $connection = Get-AutomationConnection –Name "AzureRunAsConnection" $tenant = '[tenant].onmicrosoft.com' $url = 'https://[tenant].sharepoint.com/sites/test' Connect-PnPOnline -Url $url –Thumbprint $connection.CertificateThumbprint –ClientId $connection.ApplicationID -Tenant $tenant For every PnP cmdlet this throws the following error. Get-PnPTenantSite : The remote server returned an error: (401) Unauthorized. At line:7 char:1 + Get-PnPTenantSite + ~~~~~~~~~~~~~~~~~ + CategoryInfo : NotSpecified: (:) [Get-PnPTenantSite], WebException + FullyQualifiedErrorId : System.Net.WebException,PnP.PowerShell.Commands.GetTenantSite I have also updated the cmdlets from SharePointPnPPowerShellOnline to the newest PnP.PowerShell. Furthermore, the Azure app and service principal are members of the SharePoint administrators group. When I attempt to reproduce the issue on a local machine I get the same 401 error. Any ideas? Thanks!Solved7.7KViews0likes3Comments
How to get an accessToken using MSAL library inside a Sharepoint Web Part?
I have developed a Sharepoint Web Part where I need to obtain the accessToken. To obtain the token I have used a MSAL library. My problem is the next one: I'm logged in my Sharepoint but when the Web Part try to retrieve the accessToken something fails in the authentication and appears this error: xxxx-web-part.js:1838 ClientAuthError: User login is required. at ClientAuthError.AuthError [as constructor] (https://localhost:4321/dist/xxx-web-part.js:2057:28) at new ClientAuthError (https://localhost:4321/dist/xxxx-web-part.js:630:28) at Function.7ZR7.ClientAuthError.createUserLoginRequiredError (https://localhost:4321/dist/xxxx-web-part.js:682:16) at https://localhost:4321/dist/xxx-web-part.js:2916:103 at new Promise () at UserAgentApplication.ZES5.UserAgentApplication.acquireTokenSilent (https://localhost:4321/dist/xxxx-web-part.js:2905:16) at UserAgentApplication.descriptor.value [as acquireTokenSilent] (https://localhost:4321/dist/xxxx-web-part.js:2543:38) at xxxWebPart.PlTk.xxxxWebPart.render (https://localhost:4321/dist/xxxx-web-part.js:1828:19) at xxxxWebPart.t._renderWithAccessibleTitle (https://spoprod-a.akamaihd.net/files/sp-client/sp-webpart-workbench-assembly_en-us_27e01b6941bf5cdddecc695bd3bdbb95.js:21:585834) at https://spoprod-a.akamaihd.net/files/sp-client/sp-webpart-workbench-assembly_en-us_27e01b6941bf5cdddecc695bd3bdbb95.js:21:585352 How can fix this problem?. I would like that if I'm logged in Sharepoint obtain the accessToken without relogin into the system. This is my code: export default class MyWebPart extends BaseClientSideWebPart <IWebpartProps> { public render(): void { const config = { auth: { clientId: "xxxxxxxxxxxxxxx", authority: "https://login.microsoftonline.com/yyyyyyyyyyyyyyyyyyy" } }; const myMSALObj = new UserAgentApplication(config); let accessTokenRequest = { scopes: ["user.read"] } myMSALObj.acquireTokenSilent(accessTokenRequest).then(function(accessTokenResponse) { // Acquire token silent success // call API with token let accessToken = accessTokenResponse.accessToken; let scopes = accessTokenResponse.scopes; }).catch(function (error) { //Acquire token silent failure, and send an interactive request console.log(error); if (error.errorMessage.indexOf("interaction_required") !== -1) { myMSALObj.acquireTokenRedirect(accessTokenRequest); } });7.5KViews0likes1Comment
Azure SharePoint Logic App Connector Security
Using the SharePoint Logic App connector, how can the Azure Key Vault be leveraged in place of a hard-coding AD account? Currently, we are using a dedicated AD account to authenticate with SharePoint, and our password policy requires we update the password every X months. As the usage of Azure and SPO grows, this model is quickly becoming unmanageable.5.2KViews0likes1CommentAdding a comment to a DevOps Work Item using a given user
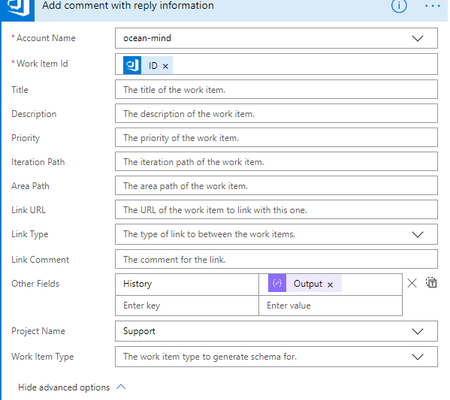
Second time writing this, as when trying to post the first time it gave me an error "invalid html" and discarded all my content -.- In Flow, I am using a DevOps - Update Work Item action, that updates a work item and adds a comment to it, using the Other Field "history" as the content of the comment. The problem is that the author is set to be the owner of the connection that the action is using, yet since the flow is triggering using an email, the author needs to be set dynamically using the email's author (provided he has an account in DevOps). How can I do this? Is there another name in "other fields" section, perhaps something like "Author" that I can use to set the author of the comment given the name, email or id from the email that started the flow? Screenshot:How can I auto-logged an user inside a Sharepoint Web Part?
I have a website "Play web". When I want to access into this site I have to login previously with user/pass. An authtentication module, handle this info and starts a communication with an Azure AD. If the user is validated properly using a callback the control is returned to the Play Web with the user logged. All these steps works fine. Where is the problem?. One of our clients wants to embed this "Play web" inside his Sharepoint but he doesn't want relogin. He needs to use the Sharepoint context to autologged the user into the website. Is there any way to do this?, Should have I setup something in Azure AD: Proxy, Function? I'm stuck with this. RegardsSolved4.1KViews0likes3Comments