azure
81 Topics
Enhanced data protection for Azure Files
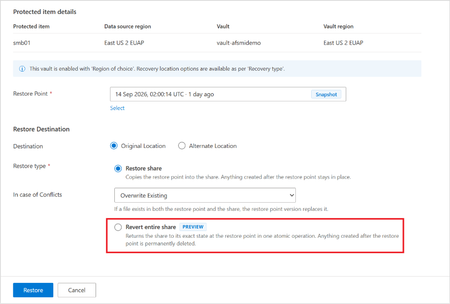
Organizations rely on Azure Files for business-critical workloads such as VDI, SAP, and general-purpose file shares that hold their enterprise data. For these workloads, backup and disaster recovery are day-one requirements. Customers need a simple, scalable way to recover from an accidental change to production data, a regional disruption or a ransomware attack, both within a region and across regions. Today, we’re announcing new capabilities, in Public Preview, that expand business continuity and disaster recovery (BCDR) capabilities for Azure Files. They help customers recover from operational issues, strengthen regional resilience and protect critical file data from cyber threats: Vaulted backup for NFS shares: Protect NFS file shares with isolated recovery points through Azure Backup for protected, trusted recovery from cyber incidents. Revert snapshot: Roll an existing file share back to a known-good point in time, in place, without changing the endpoint or mount path for fast. This gives you fast recovery from operational issues. Azure Files-to-Azure Files copy and sync with Storage Mover: Use Azure Storage Mover to maintain a secondary copy of your SMB file share data in the Azure region of your choice, with scheduled incremental transfers to keep it current for disaster recovery. Together, these capabilities let customers build Azure Files resiliency in layers: roll back quickly, maintain secondary copies and recover from protected backups. Vaulted backup for Azure Files NFS shares Cyber recovery introduces another dimension to resiliency: When ransomware or another security incident compromises the production environment, organizations need protected recovery points and may need to validate recovered data before reconnecting it to production. Azure Files already supports vaulted backup for SMB shares. With this preview, that protection extends to NFS shares. Vaulted backup for Azure Files NFS shares adds an additional protection layer through Azure Backup. Recovery points are maintained separately from the production file share and managed through backup policies designed to support long-term retention, immutability, and cyber recovery objectives. Vaulted backup helps customers protect critical file data when: Recovery points need protection separate from production: Maintain protected recovery points separately from the production file share, adding another layer of protection for critical file data. Backup strategies require immutability: Support immutable backup strategies as part of the broader approach to protecting recovery points and meeting cyber recovery objectives. Data must be retained long term: Manage recovery points through backup policies designed to support long-term retention and meet the organization’s retention requirements. Ransomware resilience is a priority: Strengthen resilience with protected recovery points for recovery when ransomware or another security incident compromises the production environment. To participate in the Vaulted backup for NFS shares preview, sign up here. Roll back quickly with Revert snapshot Operational mistakes are among the most common reasons applications need data recovery. A deployment can modify the wrong files, a configuration rollout can affect an entire namespace, or an administrator can accidentally overwrite critical content. Azure Files Revert Snapshot initially provides in-place recovery for data and applications hosted on SMB file shares, with NFS support coming next. Customers can select a point-in-time snapshot and restore the existing file share to that state while applications continue using the same file share, endpoint, and mount path. Common scenarios include: Failed application deployments: Roll back after a deployment modifies the wrong files. Incorrect configuration changes: Restore the share after a configuration rollout affects the namespace. Accidental mass modifications: Return to a point-in-time snapshot after unintended changes or overwrites. Development and test environment resets: Reset the file share to a selected snapshot. Azure Backup offers an integrated experience in the Azure portal restore blade to revert snapshots it manages. To participate in the Revert Snapshot preview, sign up here. Azure Files-to-Azure Files copy and sync with Storage Mover From disaster readiness and regional expansion to workload relocation and storage consolidation, customers need a simple, scalable way to copy and sync file data across storage accounts and Azure regions. Common use cases include Virtual Desktop Infrastructure (VDI) users maintaining secondary copies of FSLogix profiles and user data to support regional continuity, SAP and enterprise applications moving application data during regional expansion, organizations consolidating distributed content to simplify administration, and AI workflows placing datasets closer to AI and analytics compute to support distributed development and processing. Azure Files-to-Azure Files copy and synchronization with Azure Storage Mover gives customers a fully managed Azure service to copy data between SMB file shares across storage accounts, regions, and subscriptions (within the same tenant). They can also schedule incremental transfers to keep destination shares up to date. Customers can: Maintain secondary copies for business-critical workloads to an Azure region of choice. Schedule incremental synchronization of application data, user profiles, and shared content to another Azure region, helping organizations strengthen business-continuity and recovery planning. Copy or migrate file share data between regions: Copy data for regional expansion, datacenter transitions, or workload relocation. Consolidate file shares: Bring data together across storage accounts and regions to simplify management. Operate at scale with less overhead: Centrally schedule, monitor, and audit transfers instead of maintaining scripts or copy infrastructure. Azure Storage Mover reduces operational overhead with centralized scheduling, monitoring, auditing, metadata preservation, and orchestration for recurring file transfers. Figure: Storage Mover (West Central US) copies File share 1 in East US to File share 2 in West Central US. Preview support for Azure Files to Azure Files data copy is now available for SMB shares, with NFS support coming soon. To participate in the preview program, sign up here. Together, these capabilities help customers protect critical file data, recover quickly from operational issues and strengthen continuity across regions. Vaulted backup for NFS shares, Revert Snapshot and Azure Files copy and synchronization with Storage Mover provide complementary layers for a more resilient BCDR strategy. Learn more About Azure Files backup - Azure Backup | Microsoft Learn Use Azure Files Share Snapshots | Microsoft Learn Get started with Azure Files-to-Azure Files data copy in Azure Storage Mover (preview) | Microsoft Learn For questions or feedback, please reach out to the team at azurefiles@microsoft.com.219Views0likes0Comments
Discover and assess on-premises Network Attached Storage (NAS) shares using Azure Migrate
Network-attached storage (NAS) holds much of an enterprise’s data; home directories, project shares, media libraries, application data, and analytics datasets, often spanning tens or hundreds of terabytes across protocols and administrative boundaries. Moving this estate to Azure starts not with copying data, but with understanding what you have, where each share should go, and what it will cost. Building on the file share assessment capability we announced in May, today we’re announcing the public preview of NAS share discovery and assessment in Azure Migrate. It connects directly to Dell PowerScale/Isilon and NetApp ONTAP clusters, inventories every SMB, NFS, and S3 share, and assesses each against Azure Files, Azure Blob Storage, and Azure NetApp Files—providing readiness, right-sized configurations, cost estimates, and migration tooling guidance. Your NAS assets now join servers, applications, and databases in the same Azure Migrate project, inventory, and business case. Why does this matter NAS planning has historically been done with spreadsheets, vendor-specific tools, and a lot of manual reconciliation. Storage ends up being assessed separately from the servers and applications that depend on it, which makes it hard to sequence a migration or defend a budget. This capability is designed to help you: Replace manual inventory with automated discoveries across Dell and NetApp platforms, so you can go from "we think we have a few thousand shares" to a verified, per-share inventory. Effectively plan your NAS shares alongside everything else. NAS clusters and their shares appear in the same Azure Migrate inventory as your VMware, Hyper-V, and physical servers, databases, and web apps. Make your informed decision before you migrate. Each share gets a readiness verdict, a recommended Azure service and SKU, and a monthly cost estimate. What's available in public preview Add Dell or NetApp NAS clusters: Discover Dell PowerScale / Isilon (OneFS) and NetApp ONTAP AFF / FAS clusters, and inventory every SMB, NFS, and S3 shares they host — including shares exposed through more than one protocol. Explore and review on-prem shares and workloads: Review cluster and share details in the portal: model, nodes, total and used capacity, protocol versions, volume, and estimated size. Group and filter shares by tag — by business unit, cost center, or application — so related workloads can be planned together. Suitable Azure storage targets: Assess each share against Azure Files, Azure Blob Storage, and Azure NetApp Files, with control over target region, sizing criteria, comfort factor, redundancy, media type, access frequency, and workload type. Alternative migration paths: Compare various migration paths side by side — a recommended mixed path that sends each share to its best-fit service, alongside single-service alternatives — with readiness, monthly cost, and estimated emissions for each. Business case: Build a business case for a NAS-only estate or for a mixed estate of VMs and NAS, comparing a modernization approach against lift-and-shift. End-to-end experience The experience follows the same guided workflow you already know from Azure Migrate. 1. Enable the feature Install the latest Azure Migrate appliance or turn on auto-update, so your existing appliance picks up the new capability. Unlike file shares hosted on Windows and Linux servers, NAS clusters need to be added explicitly: in the appliance configuration manager, add a credential of source type NAS Server, then add a discovery source of type NAS Server with your cluster's FQDN and port. The account needs read-only permission at cluster level — Azure Migrate only reads metadata and never writes to your storage. 2. Discover your NAS estate Create an Azure Migrate project, deploy the appliance on VMware, Hyper-V, or a physical server, and point it at your clusters. The appliance connects to each cluster's management endpoint and collects system and share metadata, vendor, product and model, operating system version, cluster nodes, total and used capacity, share and bucket paths, protocols and protocol versions; followed by performance signals such as IOPS and throughput. Discovered clusters and their shares appear as first-class inventory objects, listed alongside the Windows and Linux file servers the appliance already finds. Filter by type, search, tag, and export the inventory at whatever scale your estate demands. Discovery runs a daily cycle and updates existing items as new metadata arrives, so the picture improves over time rather than being a one-shot snapshot. 3. Create an assessment Select the shares you care about — individually, by tag, or a whole cluster at a time — and create an assessment. The share is the unit of assessment, so every SMB, NFS, or S3 share receives its own verdict rather than inheriting one from its host. Assessment settings let you shape the recommendation to your environment: choose the target Azure region, pick as-is or performance-based sizing, set a comfort factor for headroom, and configure redundancy, Azure Files media preferences, and Azure Blob access frequency. A workload type setting from general purpose file shares through to AI/ML and mission-critical, helps Azure Migrate recommend an appropriate performance level. Azure NetApp Files is added to the evaluation automatically when the source share is detected on NetApp NAS. Settings can be changed, and the assessment recalculated at any time. 4. Review results and build the business case Results are organized as migration paths. The recommended path routes each share to its best-fit Azure service and is shown next to single-service alternatives, so you can compare readiness and cost on the same basis. Key insights include: Readiness for every share — Ready, Ready with conditions, or Not ready — with the warnings that need attention before you move. A recommended Azure configuration per share. For example, a multi-protocol NetApp volume is recommended for Azure NetApp Files, while a general-purpose SMB share is recommended for Azure Files with a specific media type and redundancy. Provisioned size, IOPS, and throughput behind the recommendation, plus the reasoning Azure Migrate used to select the SKU and access tier. Monthly cost estimates per share and per path, an on-premises versus Azure TCO comparison, and estimated carbon savings. Next, you can generate a wave plan to sequence the migration or build a business case that helps you with cost modernizing Azure storage services. Assessment results showing the recommended path, source-to-target mappings, estimated Azure TCO, and carbon savings. Note: All screenshots in this post are from a sample environment. Cluster and share names, capacity values, readiness distributions, cost and TCO estimates, and emissions figures are illustrative and shown for reference and indicative purposes only. They are not a price quote. Your own results depend on your discovered environment, the assessment settings you choose, your target Azure region, and the pricing and offers that apply to your subscription. Prepare for migration with the right tool Assessment tells you where each share should go; Azure Migrate then points you at the tool to get it there. Azure Storage Mover is the recommended path for moving shares to Azure Files and Azure Blob Storage. For ONTAP volumes heading to Azure NetApp Files, the Azure NetApp Files migration assistant is recommended, and Azure File Sync remains the option for active sync and hybrid scenarios with Windows file servers. To learn more about our recommendations for unstructured data migration, visit https://aka.ms/migratemydata. Get started Update your Azure Migrate appliance, add your first NAS cluster, and let a discovery cycle run. Within a few hours you'll start to see a per-share picture of your NAS estate; you can then create an assessment to view the right target service to migrate to Azure. Learn more in our documentation. Connect and discover your NAS appliance Review discovered NAS resources Create a fileshare assessment of NAS shares Review NAS File share assessment recommendations Write to us at azurestoragemigrations@microsoft.com with questions or feedback, or to suggest additional NAS systems you’d like this capability to support. We look forward to hearing from you!200Views0likes1CommentAzure Storage Discovery now offers advanced capacity insights
Azure Storage Discovery is introducing advanced capacity insights to help customers gain deeper visibility into their data estate, identify inactive or inefficiently stored data, understand storage composition and retention considerations, and pinpoint resources for further investigation and optimization.691Views0likes1CommentMore EDA Job Sets per Volume: Azure NetApp Files Raises the Performance Bar
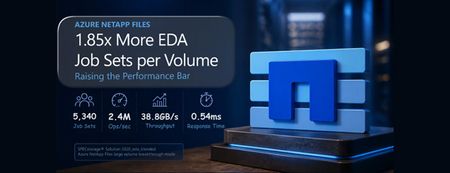
Azure NetApp Files raises the performance ceiling for cloud-based electronic design automation (EDA) with a new independently published SPECstorage® Solution 2020 EDA_BLENDED result for a single large volume in breakthrough mode: 5,340 job sets, 2.4 million operations per second, 38,776 MB/s peak throughput, and 0.54 ms overall response time. Delivering 1.85 times the job sets, operations, and throughput of the previous single-volume result while preserving sub-millisecond latency through most load points, the result enables more concurrent simulations, shorter regression cycles, and better utilization of compute and tool licenses without dataset sharding. Combined with proven linear scale-out and generally available Azure NetApp Files cache volumes that provide on-demand access to on-premises data, it gives EDA teams a practical foundation for high-performance cloud deployment and bursting.333Views0likes0CommentsBoost performance with NFS nconnect on Azure NetApp Files datastores for Azure VMware Solution
Azure VMware Solution now supports nconnect=4 with Azure NetApp Files datastores each ESXi host opens up to four parallel TCP connections to a single NFS datastore, raising throughput and lowering latency under load. Supported on both Gen 1 and Gen 2 private clouds, it makes Azure VMware Solution with Azure NetApp Files an even stronger home for databases and other storage‑intensive workloads.555Views0likes0CommentsBringing Enterprise File Data to Users with Azure NetApp Files, Microsoft Foundry, and M365 Copilot
This is Part 3 of a 3-part series on extending AI to enterprise file data, showing how the knowledge pipeline is surfaced through enterprise AI agents and user experiences including Microsoft 365 Copilot.687Views0likes0CommentsFrom Enterprise File Storage to an AI-Ready Data Foundation using Azure NetApp Files and OneLake
This 3-part series shows how to extend AI to enterprise file data – without migration – by combining Azure NetApp Files, OneLake, and a RAG-based architecture that surfaces grounded insights through enterprise AI agents. This is Part 1 of a 3-part series covering the data foundation, knowledge pipeline, and user experience layers.687Views0likes0CommentsFrom File Data to AI‑Powered Knowledge Pipelines using Azure NetApp Files object REST API
This is Part 2 of a 3-part series on extending AI to enterprise file data hosted on Azure NetApp Files, building on the data foundation to create a knowledge pipeline that makes enterprise file data usable by AI systems.574Views0likes0CommentsSimpler, scalable file share management in Azure - now generally available
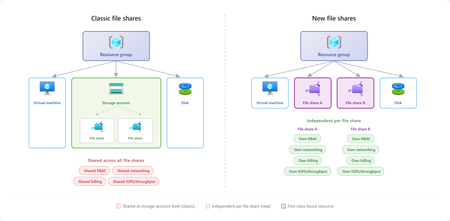
Linux workloads in Azure are scaling faster than ever, powering everything from container platforms, analytics pipelines, SAP environments to line-of-business applications. As these workloads grow, infrastructure teams commonly run into challenges with scale, cost management, complexity and compliance. IT organizations need more granular control over management and isolation boundaries for file shares independent of storage accounts, to prevent multiple application teams sharing the same capacity pools, limits, and configuration surface across different storage services. Infrastructure administrators seek operational simplicity with managing access control, policy and networking isolation for file shares, so application teams can focus on business logic and development agility. We are announcing the general availability of a new service management experience for premium SSD file shares (NFS) which allows each file share to be created, secured, scaled, and billed independently, without being tied to a storage account. Key benefits include: Familiar and intuitive file share management: Aligns user experience with on-premises NAS and file server paradigms, improving usability compared to the classic model. Infrastructure-as-Code: Define naming, capacity, IOPS, networking, tags, and security in Bicep or ARM templates for simplified automation with your favorite DevOps tools. Scale to match the workload: Support for up to 10,000 file shares per subscription per region, with 2.5x faster file share provisioning experience. Share-level security and networking: Network restrictions, snapshots, and encryption scoped to the individual share, making isolation boundaries match workload boundaries. Per-share cost visibility: Billing meters emit under the file share resource, teams can crossbill accurately, track per-workload costs, and improve chargeback without workarounds. Independent performance, security, and billing per share Combined with the provisioned v2 model, each file share is independently provisioned with its own storage, IOPS, and throughput. This allows organizations to align file shares directly to application or tenant boundaries, rather than grouping them under shared infrastructure constructs. For multi-tenant SaaS platforms, this enables a natural one-to-one mapping between tenants and file shares. Each tenant operates within its own performance envelope, allowing steady workloads and bursty workloads to scale independently without contention. This reduces the need for capacity planning tradeoffs or overprovisioning to accommodate peak usage across tenants. This isolation extends beyond performance; each file share carries its own encryption in transit settings, RBAC, policy, and network boundaries. For example, production tenants can be isolated with dedicated private endpoints, while development environments can operate under more flexible configurations. These boundaries align directly with application design, making systems easier to reason about and manage at scale. Finally, treating each file share as its own resource simplifies cost management. Teams can tag and track usage at the workload or tenant level, enabling more accurate chargeback and better visibility into resource consumption. This makes it easier to understand how individual workloads contribute to overall spending without introducing additional tracking mechanisms. Start easy, scale big Cloud-native Linux applications often scale dynamically, so the underlying storage platform must provide resources quickly and support higher scale limits to keep pace with workload demand and enable teams to quickly provision infrastructure and keep pace of development. The new file share experience supports up to 10,000 file shares per subscription per region, making it practical to use a dedicated share for each application, environment, or tenant without running into platform limits. It also provides faster provisioning, with time to first share 2.5x times faster than classic file shares, so teams can spend less time waiting on infrastructure and more time building, testing, and shipping. “Provisioning is fast and integrates seamlessly with Linux environments through NFS.” - Siam Commercial Bank Data protection with snapshots Linux workloads using shared file storage require robust data protection. With the new service management experience, customers can continue to leverage point-in-time incremental snapshots with up to 200 snapshots per share. You can also now edit metadata on individual snapshots, making it easier to organize and identify recovery points. Whether you need short term restore points or need to retain data for compliance requirements, snapshots provide an easy and cost-effective recovery mechanism. Get started today The new file share experience is available for NFS 4.1 file shares on SSD storage, using the provisioned v2 billing model with LRS and ZRS options. Whether the deployment model is ARM templates, Bicep, MCP server, or custom CI/CD pipelines, file shares are scriptable, repeatable, and automatable through the same tooling used for the rest of Azure infrastructure. Explore our documentation for step-by-step guidance. We're continuously enhancing the new file share experience with the goal of achieving full feature parity while delivering improved scale and performance limits. We would love to hear your feedback, please fill out the survey to share your thoughts. Learn more Planning for an Azure Files deployment How to create a file share Scalability & performance targets For questions or feedback, contact us at azurefiles@microsoft.com.1.8KViews3likes0CommentsSecure, Modern Access to Azure Files on macOS with MS Entra ID
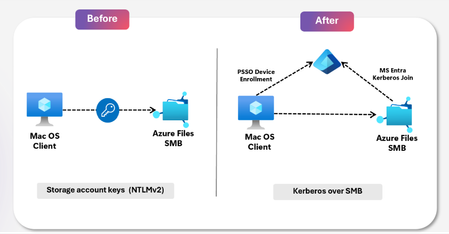
Enterprises, large and small, rely on Azure Files for secure, scalable, and cost-efficient file storage. Modern workflows today span devices, platforms, and geographies; seamless, and secure access to shared data across every endpoint is critical to keeping teams productive and collaborative. With the growing demand for access across every device, Azure Files now extends secure access to macOS with Entra ID authentication, supporting design, creative, and AI teams where they work. Today, we are announcing the Public Preview of MS Entra ID based authentication for Azure Files on macOS. Whether you are running creative production pipelines, design workflows, or AI workloads, macOS users can now access Azure file shares securely, meeting Microsoft Entra ID enterprise governance standards automatically and seamlessly, with no credential prompts, no storage account keys, and no complexity. Key benefits Enhanced Security posture: MacOS users can now sign in to their device and open shared files in Finder with no credential prompts and no storage account keys. Microsoft Entra ID governs access, conditional access policies, MFA requirements, and MS Entra ID governance applies automatically with AES-256 encryption. Reduced operational overhead: IT admins no longer need to manage storage account key distribution/rotation. Provisioning and deprovisioning access is handled through standard Entra ID group membership. No dependency on Active Directory: Organizations moving away from on-premises infrastructure, including Active Directory, can now give MacOS users full access to Azure file shares using cloud-based identities in MS Entra ID, with no domain controller required. MacOS users get full parity with the traditional Windows SMB share experience. Identity Based Access model: User authentication is enforced with Kerberos and share-level access is enforced through Azure RBAC. File and folder permissions are controlled through NTFS ACLs, giving organizations precise, layered control. Enabling AI-Driven Workloads: SMB shares on macOS enables AI teams to seamlessly access and share large datasets, fueling faster experimentation and streamlining developer and AI-generated workflows. Partnership with Apple Azure Files support for macOS is built in close collaboration with Apple macOS SMB engineering team. The integration works with Apple’s Platform SSO and the Microsoft Enterprise SSO plug-in, via MDM platforms such as Microsoft Intune. This allows macOS devices to authenticate through Microsoft Entra ID with single sign-in. We are committed to continuing this partnership to ensure Mac users in enterprise environments have a first-class experience accessing cloud services. Powering Diverse Workloads across Design, Developer and Education Enterprises Secure SMB access for creative workloads Creative workflows on macOS have historically required workarounds to reach centralized cloud storage, often meaning local copies, consumer file sharing tools, or storage account keys distributed to individuals. Azure Files gives creative teams direct access to shared project libraries and production files from Finder, with no syncing or local copies needed. For IT, setup is simple: assign the right RBAC role on the share, add users to an Entra group, and access is ready. No keys to distribute and no deep storage expertise required. "Secure access for our macOS users is a gamechanger for our creative teams. The ability to mount directly and access shared files securely — without keys, without workarounds — changes how we work. It’s how modern enterprise file access should feel." -Peter Day, Senior Engineer, The Marketing Store SMB shares streamline developer and AI-generated build workflows MacOS developers rely on local tools like Visual Studio Code, GitHub copilot, or fast iteration, but build artifacts, logs, and AI-generated outputs often end up fragmented across machines and pipelines. With Azure Files, teams can use SMB shares as a centralized workspace for build outputs and shared assets. Mac build systems can write directly to a mounted share, making artifacts immediately accessible across developers, pipelines, and AI agents. DevOps teams gain a secure, identity-based storage layer using RBAC and Microsoft Entra, without managing keys or custom storage solutions. Enable collaboration across mixed platform environments Mac users should not be a special case. Azure Files gives MacOS users the same governed, identity-based access to shared storage that Windows users have always had. Access is provisioned through Entra ID, enforced through RBAC, and managed without a separate workflow, separate keys, or separate infrastructure. For large organizations running mixed-OS environments, this means a single, consistent access model tied to the user and not a device – the user can seamlessly access the SMB share across their Windows and Mac devices. “By supporting Kerberos authentication for Azure Files on Mac devices, Microsoft delivers secure, consistent access for organizations operating mixed-OS environments. It addresses a long-standing enterprise gap by extending centrally governed identity controls to all users, regardless of device—helping organizations simplify access management and maintain trust at scale.” -Preetham G.K., CDL, Accenture Modernize Infrastructure and secure access for Educational Institutions Institutions standardizing on macOS have faced a hard tradeoff: maintain costly on-premises infrastructure at every site or accept that MacOS users fall back on personal drives and consumer file sharing. Neither is acceptable at scale. Azure Files removes the tradeoff. Students, faculty, and staff access shared repositories and course materials directly from an SMB share over Finder using their Entra ID credentials. Access management can be controlled through group membership, with no per-site infrastructure and no manual credential management. Get started with Azure Files Entra Kerberos authentication for macOS Start leveraging secure, identity-based file access on macOS today at no added cost. Explore our documentation for step-by-step guidance. Whether you are onboarding new Mac users or modernizing an existing deployment, this feature gives your organization a simple path to identity management for Azure Files on macOS. Make your Mac workloads ready for the future! For any questions, please reach out to the team at azurefiles@microsoft.com.1.2KViews0likes0Comments