azure ad
33 TopicsAzure AD group-based license management for Office 365 and more
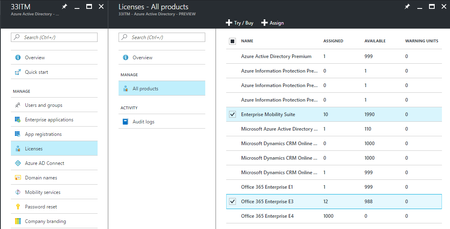
This looks awesome - simplify licence management for Office 365, EMS, Dynamics 365 and more with the https://blogs.technet.microsoft.com/enterprisemobility/2017/02/22/announcing-the-public-preview-of-azure-ad-group-based-license-management-for-office-365-and-more/: Microsoft cloud services such as Office 365, Enterprise Mobility + Security, Dynamics CRM, and other similar products require licenses to be assigned to each user who needs access to these services. Until now, licenses could only be assigned at individual user level, which can male large-scale management difficult for our customers. We have introduced a new capability of the Azure AD license management system: group-based licensing. It is now possible to assign one or more product licenses to a group. Azure AD will make sure that the licenses are assigned to all members of the group. Any new members joining the group will be assigned the appropriate licenses and when they leave the group those licenses will be removed. This eliminates the need for automating license management via PowerShell to reflect changes in the organization and departmental structure on a per-user basis. Here is the documentation with the steps to get started - https://docs.microsoft.com/en-us/azure/active-directory/active-directory-licensing-whatis-azure-portalSolved25KViews12likes38CommentsAzure AD Pass through authentication roadmap/GA?
We have a customer really interested in this new AADConnect feature. They have a complicated ADFS setup and we are thinking about "migrating" to this new feature "Azure AD Passthrough Authentication". We are fine with an evaluation during preview phase, but at the moment don't have any information about a GA date. We need a rough estimate. H2 2017? Q3 2017? 2018? On what offical roadmap would I find this feature? Checked O365 and Cloud plattform without success. That is what we are looking for: https://docs.microsoft.com/en-us/azure/active-directory/connect/active-directory-aadconnect-pass-through-authenticationSolved8.1KViews2likes10CommentsThe final push to GA "Azure AD in new Azure Portal": We need your help!
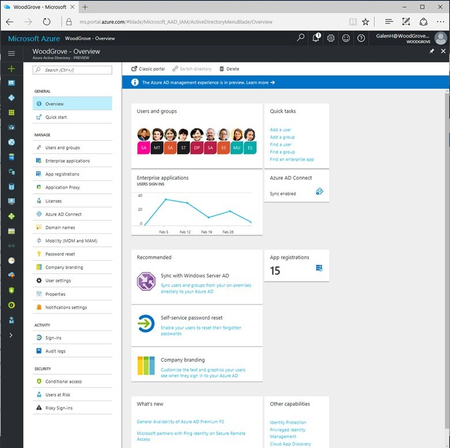
Hello folks, We`re making our final push to the General Availability of "Azure Active Directory in the new Azure Portal", and we need your help to make sure it is great for you. As Alex Simons shared: "Last September we shared the first preview of the new administration experience for Azure Active Directory in the new Azure portal. Since then, we’ve added lots of new functionality, including reporting, app management, conditional access, B2B, and licensing. Many of you are using the new experience regularly – in fact, over half a million of you are using it, from almost every country in the world, with usage increasing by about 25% each month. We appreciate all your positive feedback, and love the constructive feedback that’s helped us make an even stronger product. But there are still a LOT of you using the old portal. Late last week we turned on the another set of feature updates, and the new experience now has all of the features identity admins frequently use. With that update, we’ve entered our final push to GA the UX in the next ~60 days. And that’s where we need your help: We need everyone to move over to using the new portal for production tasks so we can uncover any last minute lingering issues." Please, do read Alex` blog post for more details and send us your feedback in the ‘Admin Portal’ section of our feedback forum. Let us know what you think!6.9KViews11likes14CommentsAzure Enterprise Apps - permissions
Trying to set up SSO with Box.com via application listed in Azure AD Application Gallery. Followed online instructions https://docs.microsoft.com/en-us/azure/active-directory/active-directory-saas-box-tutorial on both the old AAD portal and within new portal (which is very different). However when testing get an error message. AADSTS65005 - The client application has requested access to resource '00000002-0000-0000-c000-000000000000'. This request has failed because the client has not specified this resource in its required Resource Access list. From what I can determine the 'resource' is AAD and I think it is looking for the Box app to have authority to AAD. Is it an undocumented step to grant permissions via the new azure AD portal, has something failed during setup or am I missing something more fundamental ? Has anyone encountered similar issues with the application gallery apps ?Solved6.2KViews0likes3CommentsPower BI Content Pack for Azure Active Directory
Seems like PowerBI is finally getting some attention from the rest of Microsoft's services teams. First we got the Office 365 Content pack (preview), and now we also have a content pack for Azure AD. The official announcement is here: https://blogs.technet.microsoft.com/enterprisemobility/2017/01/20/admins-rejoice-azure-active-directory-meets-power-bi/ The setup instructions can be found here: https://powerbi.microsoft.com/en-us/blog/azure-active-directory-meets-power-bi/preview/. In my case the login only worked with OAuth, not sure why.5.4KViews3likes2CommentsAzure AD by the numbers?
Good morning everyone, I'm looking for a source of numbers about Azure AD. What do I mean by numbers? Well I've seen talks about how Azure AD is doing 1.3 Billion Enterprise Authentications per day, there are 600 Million Enterprise Accounts and X Millions of synchronized directories... it would be great if someone could point me to a recent slide deck or maybe a website that hosts such information. Thanks and have a nice weekend! Tom5.3KViews1like4CommentsAgent for Identity Manager to sync to Azure AD
I colleague asks if there is a way to use MIM/FIM to sync to Azure AD? I recall that there used to be a FIM agent that you used in multi-forest scenarios. Today AAD Connect handles multi-forest. This company already has Identify Manager deployed and uses it heavily, so they want use it instead of deploying Azure AD connect if possible.4.6KViews0likes4Comments