azure ad
14 TopicsBest practice for Win10 local admin user when computer offline
I have question about your best practices for organizations. Scenario: You have only Azure AD joined - Windows 10 computers, with Intune MDM management. Only one user is using Windows 10 PC device, and has local admin rights. Additional Azure AD users are deployed as local administrators to the device. There is also Bitlocker encryption and secure boot implemented. Challenge: What if user forgets the password (or user is no longer active in organization), and device goes offline (example network card driver issue), how can other users / Azure AD users, login to the device, to fix the issue on local windows? Possible solution would be to deploy always additional local windows account, with admin rights, but this always has sign-in disabled (since Intune enforces this). What do you recommend?8.2KViews1like9Comments
Decrease Maximum Number of Devices Per User
Hi All, Currently in our Azure AD tenant the "Maximum number of devices per user" is set to unlimited. I want to decrease this number to 20 a per MS recommendation. The problem I have, that I could not find any information on, is this. There is one account that have Enrolled and is the Primary User on about 180 devices. My question is, without removing the Primary user or changing this account from being the primary user, what will happen to these devices when I decrease the Maximum number of devices per user to 20? Will any of those devices become stale, require a new sign in or an update on the user side? Thank you.4.8KViews0likes3Comments
Require MFA OR Intune Enrollment/compliance when Outside the Trusted IP Range
My company is currently piloting MFA and we have recently deployed Intune for corporate Mobile devices. We have our MFA setup so it only requires 2 step verification when a device is outside the corporate network. We would like to require either MFA OR Intune enrollment on mobile devices when they are outside teh corp. network. I am testing a conditonal access policy to accomplish this but it is still asking for 2 step verification even though my test mobile device is enrolled and compliant with intune. Under Access controls, i've selected grant access, require mfa, require device to be marked as complaint, and require ONE of the selected controls (preview) Has anyone seen this issue before?3.6KViews0likes5CommentsisManaged but mdmdDisplyaName (blank)
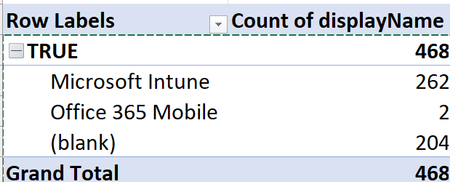
Hola! Would like to understand difference between "isManaged" and really getting managed by an MDM, in this case MEM. isManaged = True I'm onboarding devices to MEM Intune, currently only worried about Hybrid devices. Hybrid environment (AD Connect configured), MDM Enrollment GPO deployed. After 3 weeks only 262 out of 462 units have enrolled to MDM, needle is not moving at all. Might be a lot of options. For now I would only like to understand what does it mean that an Azure AD "Device" object has the "isManaged" attribute set to True when not already enrolled to intune, is this a clue that it has started the procees? is it just nothing? Thanks in advance for feedback and/or comments. Best regards, Manuel2.6KViews0likes3Comments
Move Hybrid Azure AD Devices to Intune
Hello, we have already a lot of devices on our azure active directory (AD) registered. We want move them to Intune / Autopilot without generating hardware hashes. Is it possible? To move existing Azure AD Devices to the Microsoft Intune Center? And how we can solve this problem? Thanks a lot Best Regards NY1.8KViews0likes2CommentsAzure AD conditional Access.
Hi All, I was looking for some insights on how large enterprises handle this situation. Assuming you have IP based restrictions for SharePoint Online OR Conditional access where you created a named location with a set of IPS. In a scenarios where on the network infrastructure is changed or updated/ new sites added/ circuits changed, how do large enterprises deal with handling this change? For a large enterprise you could have multiple locations and a complex network, is there a best approach to handle change in the IPs so that users don't get locked out of Office 365? Thanks, PriyankSolved1.8KViews0likes1Comment
GIA - 2.0 - Get Intune Assignments
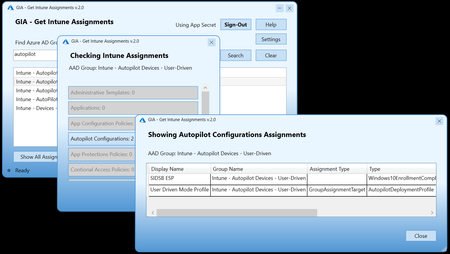
GIA - Get Intune Assignments Hello everyone I just released a new version from my App. https://github.com/sibranda/GetIntuneAssignments/releases/tag/v2.0 It's a C#.NET application developed for Intune to query MS Graph Information from Intune Assignments who target the Azure Ad Groups. You can export the data to CSV file if you wish. In this new version you can get information from the following types of assignments: Adm Templates; Applications; App Config Policies; Autopilot Configurations (new on 2.0); App Protection; Conditional Access; Compliance Policies; Configuration Profiles; Settings Catalog; Endpoint Security Policies; Enrollment Restrictions (new on 2.0); iOS App Provisioning (new on 2.0); Policy Sets; PowerShell Scripts; Proactive Remediations (new on 2.0). All this from a Graphic Interface with just a few clicks. https://github.com/sibranda/GetIntuneAssignments/releases/tag/v2.0 Please send me any feedback you want. This can help me to fix bugs and make better solutions to help everyone.1.7KViews0likes0Comments