app connectors
55 Topics
Why is this a High severity Alert with Suspicious Activity as classification?
System alert: Network Requirements Update for API Connectors There must be better ways of allowing customers to deal with Connector-updates? I also couldn't find a Policy or Template in which I could tune/manipulate severity, threshold or turning it off?
Autht cloud app security
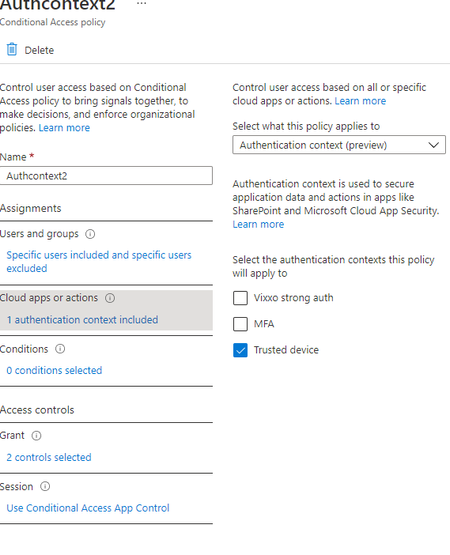
Hello I have setup an authentication context and published it to CA polices. The Authentication Context name is "trusted device". I created the CA policy per below . When i log into the application from a non trusted device, and do a copy and or paste, i should be getting prompted from cloud app security to step up authentication, but i dont. Any help is greatly appreciated In cloud app security i created session policy , category = "Compliance". Below are the settingsSolvedadding azure enterprise apps to cloud app security
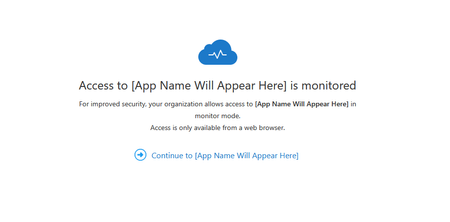
Hello We have many saml enterprise apps that have been added to Azure enterprise apps. Some of the apps are accessed using a client app that's on the users mobile device. When looking at the default message in cloud app security, below its suggesting that the application can only be accessed from a browser. When people see this message , they associate "web browser" with desktop or laptop, not a mobile client app thats on a mobile device. I have tested this and against one of our saml apps "Zendesk" using the mobile client, and everything works, but considering every modern saml app has a mobile app, why would this be the default message ?Cloud app security non-interactive
Does cloud app security detect and log non-interactive sign-on's ? When i look at the azure sign-in logs for a particular user, i can see the non interactive sign-on's, however trying to match this up or corelate this in cloud app security is proving to be difficultHow to get Sharepoint online into Conditional Access app Control
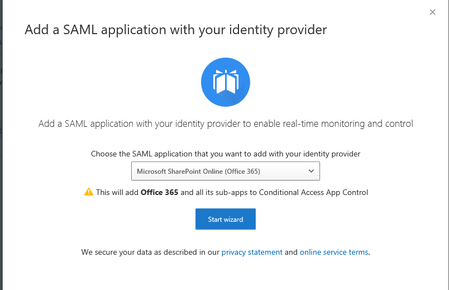
Hello What are the steps to add sharepoint online into Conditional Access app Control ? When i add a new app then search for Sharepoint i get the message below. When i click on the "start wizard" its asking me for saml xml data. Is this the proper way to add SharePoint online to Conditional Access app Control ?Conditional Access app control
I have configured a CA policy to use a custom policy for CA app control. When i navigate to cloud app security and "Conditional Access App Control apps" and add an app, i search for Sharepoint. I then receive the message below. When i click "start wizard" its asking for a metadata file. Does this feature not work with O365 applications like SharePoint and Exchange online ? Also if i navigate to polices in MCAS, click on "Conditional access" and create a new session policy i receive the below message. Its asking me to first create CA app control , but as i previously mentioned its asking me for metadata file, but im trying to protect sharepoint online. Very confused here. https://docs.microsoft.com/en-us/cloud-app-security/proxy-deployment-aadLag in Cloud App Security
Does anyone else notice/experience a lag in the logging within Microsoft Cloud App Security? It's more noticeable with connections to other cloud services but even processing rules around revoking rights to for example files flagged as sensitive seems to take longer than what I would describe as acceptable to process (so more than 30 minutes). As a small team, ideally we would like to trust the reporting and actions that this product generates and takes but it just doesn't seem to be consistent.1.8KViews1like2CommentsMCAS and Salesforce - Do we need SF shield ?
Hi, We asked Microsoft and Salesforce if the SF shield licenses were a requirement to improve monitoring, neither were able to respond so I'm reaching out to the community. We have connected our SF instance to MCAS following the available documentation. We had to do some tinkering to bypass having to use a Sysadmin profile. SF shows up as connected and we get the users correlation between Azure/O365/MCAS and SF plus some login/logout events. Now we don't get a lot of data/alerts from Salesforce, will this be improved by adding the extended event monitoring provided by SF shield ? Thanks for any experiences and feedback, RobertSolvedUsing end-points from mcas-siemagent-0.111.126-signed.jar
I’ve been using mcas-siemagent-0.111.126-signed.jar file to retrieve logs from my cloud services. I’ve been saving the logs to a local directory and while looking at them I’ve noticed two interesting endpoints: Executing request GET /api/v1/agents/siem/consume/ Executing request GET /api/v1/agents/siem/get_data/?{some cursor related data} Is there any way of getting the logs information using those end points, without using the .jar?
Uploading Palo Alto firewall logs to MCAS and Sentinel
Hi, I'm investigating the best way to get our Palo Alto firewall logs into MCAS and Sentinel. My present understanding is two different log collector methods would be required in parallel. - MCAS - Log collector running in Docker - Sentinel - Syslog server with the OMA agent installed As the documentation is indicates MCAS processing is every 24 hours, I'm assuming the PA firewall logs cannot be passed over to Sentinel on the MCAS connector. Is it possible to run the docker log collector and the syslog via OMA on the same host if it has a high enough specification to take the load?