app connectors
55 Topics
MCAS API Connector - Connect GCP - Error: Failed to create sink via Stackdriver Logging API
Hi Everyone, I follow the Microsoft official procedure (Link: https://docs.microsoft.com/en-us/cloud-app-security/connect-google-gcp-to-microsoft-cloud-app-security) to connect GCP to MCAS through API Connector. Unfortunately when I'm going to connect GCP the MCAS report the following error: Error: Failed to create sink via Stackdriver Logging API. Any suggestion? Is there a way to solve this issue? Thanks in advance. Regards, Vittorio (Security Team Lead)
Application Script That Filters Risky Unused Apps on Your Environment.
Hey there everyone. Recently made a script that filters out high risk applications (Risk score <4) that haven't been used in awhile on your environment. An easy win is to block applications that haven't been used in a bit. We have specific application categories we are more interested in than others. Feel free to copy this template, or use others. Oh- you need the MCAS Powershell package installed too. Here is the download link: https://github.com/microsoft/MCAS/ #defining variables $count = 0 #Count variable used for determining the number of apps left $obj = @() #Array where the apps will be added to do { $applist = Get-MCASDiscoveredApp -Skip $count $count += $applist.count ## applies the list count to the specific count itself. foreach($app in $applist){ ##for each application inside the list of 100 if(($app.category -eq "SAASDB_CATEGORY_SOCIALNETWORK") -or ($app.category -eq "SAASDB_CATEGORY_NEWS_AND_ENTERTAINMENT") -or ($app.category -eq "SAASDB_CATEGORY_CLOUD_COMPUTING_PLATFORM") -or ($app.category -eq "SAASDB_CATEGORY_CONTENT_MANAGEMENT") -or ($app.category -eq "SAASDB_CATEGORY_COLLABORATION") -or ($app.category -eq "SAASDB_CATEGORY_HOSTING_SERVICES") -or ($app.category -eq "SAASDB_CATEGORY_IT_SERVICES") -or ($app.category -eq "SAASDB_CATEGORY_MARKETING") -or ($app.category -eq "SAASDB_CATEGORY_IT_SERVICES") -or ($app.category -eq "SAASDB_CATEGORY_WEBMAIL") -or ($app.category -eq "SAASDB_CATEGORY_SECURITY") -or ($app.category -eq "SAASDB_CATEGORY_FORUMS") -or ($app.category -eq "SAASDB_CATEGORY_ONLINE_MEETINGS") -or ($app.category -eq "SAASDB_CATEGORY_COMMUNICATIONS") -or ($app.category -eq "SAASDB_CATEGORY_WEB_ANALYTICS") -or ($app.category -eq "SAASDB_CATEGORY_ADVERTISING") -or ($app.category -eq "SAASDB_CATEGORY_WEBSITE_MONITORING") -or ($app.category -eq "SAASDB_CATEGORY_CONTENT_SHARING") -or ($app.category -eq "SAASDB_CATEGORY_ADVERTISING") -or ($app.category -eq "SAASDB_CATEGORY_BUSINESS_INTELLIGENCE")){ ##filters on application category - we look for specific types here for our enviornment. Change to your liking. if($app.lastUsed -lt (get-date).AddDays(-14).ToString("yyyy-MM-dd") -and ($app.revised_score_total -lt 5)){ ##checks and sees if the application has been used by anyone in the organization in the last 14 days. $obj += $app ##Adds the application and the data from MCAS to the array. } } } Start-Sleep -Seconds 6 ##API Connection times out after awhile. This start sleep prevents these issues. } while($applist.count -ge 100) ##Do While loop while there still apps to be pulled $obj | Export-CSV -Path "C:\Script\apps.csv" -Force ##Exports the list to an apps csv Pretty much, the script runs and looks for applications that haven't been used in the last two weeks. If your parser and ADATP logs are constantly up to date, you should definitely have a good list of risky applications to block on your environment. If you have any questions, feel free to post below.Recording of Cloud App Security Intro Webinar
Thanks to those of you who joined our introductory webinar for Microsoft Cloud App Security. For those who couldn't make it, you can find the recording at https://youtu.be/dUoicG0Hc-o. Also, thanks to Sebastien Molendijk for an informative presentation. If you'd like to ensure you're notified of future calls, please join our community using the instructions at https://aka.ms/SecurityCommunity.
MCAS Regex Engine
Maybe you have a Quick answer. We are currently evaluating DLP Capabilities with MCAS. As we are now implementing Use Cases, we discovered that the Regex Engine from Microsoft is somewhat special. Me and my colleagues understand that this is a mass amount engine and therefore has its limitations regarding the Quantifiers. Now, the Docs are kind of clear but only very less. How does the Regex Engine actually works, what are the limitations? We can investigate every single regex match but how do we validate false positives for a amount of matches? (Probability Score or Reducing the max. Matches per day) Some example use cases from the customer: - Leveraging regex to look for http headers - Look for Cookies (e.g. Look for "Set-Cookie") - Regex hunting base64 encoded jwt id or access tokens or other custom tokens with various file types - pci data (can be covered by MCAS) - aws session token (SessionToken AND base64 encoded data in the vicinity) - MIP labeled documents ( can be covered by MCAS) Hope someone can helpMCAS doesn't receive anymore any files from connected app Office 365
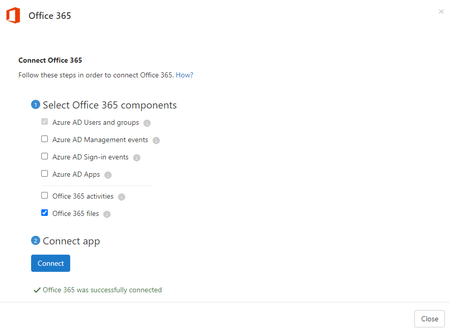
Hello, MCAS doesn't receive anymore any files (In "Investigate > Files") from connected app Office 365 from July, 1 2020. Below, in the two screenshot, you can find my currently MCAS Connected Apps configuration with Office 365 and all seems ok. What could be the problem? I already tried to disable and re-enable the MCAS Office 365 app connector, connect and test it again, but nothing, the problem persists 😞 I continue to not receive any file in MCAS Investigate > File section of the portal. It's a very strange problem. Someone else had this same problem and can help me to resolve it, please? Thanks in advance, Max2.9KViews2likes8CommentsPlans for multi instance app connectors to Office 365 and/or Azure?
Hi! Anyone know if there are any plans for multi-instance support for Office 365 and Azure app connectors? I have a customer which have lots of tenants and they would like to aggregate all the security logging into the same centralized MCAS solution. But since it doesn't seem to be possible today they are pulling all the logs down on-premises for further analysis in their own SIEM. I can really see the need for this functionality since many organisations buy other companies and end up with more tenants. If they are going to be able to keep control over the ever increasing security boundary they are forced to download all the logs to their local SIEM. Thanks in advance!Autht cloud app security
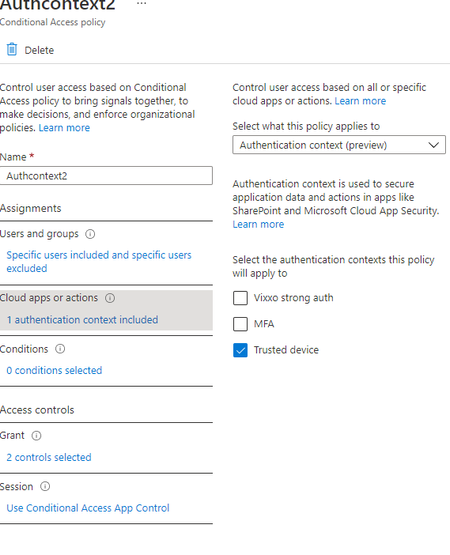
Hello I have setup an authentication context and published it to CA polices. The Authentication Context name is "trusted device". I created the CA policy per below . When i log into the application from a non trusted device, and do a copy and or paste, i should be getting prompted from cloud app security to step up authentication, but i dont. Any help is greatly appreciated In cloud app security i created session policy , category = "Compliance". Below are the settingsSolvedLag in Cloud App Security
Does anyone else notice/experience a lag in the logging within Microsoft Cloud App Security? It's more noticeable with connections to other cloud services but even processing rules around revoking rights to for example files flagged as sensitive seems to take longer than what I would describe as acceptable to process (so more than 30 minutes). As a small team, ideally we would like to trust the reporting and actions that this product generates and takes but it just doesn't seem to be consistent.1.8KViews1like2CommentsMCAS and Salesforce - Do we need SF shield ?
Hi, We asked Microsoft and Salesforce if the SF shield licenses were a requirement to improve monitoring, neither were able to respond so I'm reaching out to the community. We have connected our SF instance to MCAS following the available documentation. We had to do some tinkering to bypass having to use a Sysadmin profile. SF shows up as connected and we get the users correlation between Azure/O365/MCAS and SF plus some login/logout events. Now we don't get a lot of data/alerts from Salesforce, will this be improved by adding the extended event monitoring provided by SF shield ? Thanks for any experiences and feedback, RobertSolved