Recent Discussions

2026-04 Update Breaks Domain Logins
I have an Active Directory domain that is old (from 2000!) that has been upgraded and moved to newer versions of Windows Server and Active Directory. I have domain controller VMs running Windows Server 2025 Standard Edition. Unfortunately they installed the latest 2026-04 patches which my have changed the Kerberos encryption from RC4 to AES. This has resulted in my not being able to log into any Active Directory domain accounts and the domain controllers themselves. I can only log into workstations using the local account. Suffice to say this a nightmare. Any ideas how to fix it since I can't access the usual tools like Active Directory Users and Computers, Hyper-V won't connect to the VMs, etc. Thanks. SSolved5.7KViews2likes9Comments
Update Daylight saving time on Windows server client from domain controller
Hello, The September 2026 cumulative update includes the Morocco Daylight Saving Time update. We are planning to update our domain controllers to apply the new DST schedule. Is there any option for domain-joined Windows Servers to update their Daylight Saving Time configuration from the domain controller without installing the September 2026 cumulative update on each server ? Or does the update need to be installed on every Windows Server individually ?Solved101Views0likes2Comments
Assigning IP address for Hyper-V VM Windows Server 2025
I am building my first Windows Server 2025 VM on HyperV and trying to assign an IP address to the VM. I want the VM's to be like an actual server so I created an external vswitch. The original IP address for the server was 172.16.1.41 with a gateway of 172.16.1.5. When I activated the Hyper-V role, that IP was associated with the switch as described in the setup. I created my VM and successfully installed Windows Server 2025. However, when I try to assign the IP for the new VM, 172.16.1.42/255.255.255.0 and the Gateway is 172.16.1.5, I am not able to ping from the new VM. The IPCONFIG /ALL is below for both the Hyper-V and the new VM. There are 4 ethernet adapters on the physical server. The Virtual Switch created in the configuration is using Adapter 1. Should it be using Adapter 2 as shown on the Ethernet Adapter Slot4? Hyper-V Server Ethernet adapter vEthernet (Virtual Switch): Connection-specific DNS Suffix . : Description . . . . . . . . . . . : Hyper-V Virtual Ethernet Adapter Physical Address. . . . . . . . . : D4-04-E6-0E-A2-87 DHCP Enabled. . . . . . . . . . . : Yes Autoconfiguration Enabled . . . . : Yes Link-local IPv6 Address . . . . . : fe80::a334:5bd:24d:d2b3%19(Preferred) Autoconfiguration IPv4 Address. . : 169.254.142.53(Preferred) Subnet Mask . . . . . . . . . . . : 255.255.0.0 Default Gateway . . . . . . . . . : DHCPv6 IAID . . . . . . . . . . . : 416548070 DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-2D-D9-50-A2-D4-04-E6-0E-A2-87 NetBIOS over Tcpip. . . . . . . . : Enabled Ethernet adapter Slot4 Port 1: Connection-specific DNS Suffix . : Description . . . . . . . . . . . : Broadcom 5719 1GbE RJ45 4-port OCP Ethernet Adapter #2 Physical Address. . . . . . . . . : D4-04-E6-0E-A2-86 DHCP Enabled. . . . . . . . . . . : No Autoconfiguration Enabled . . . . : Yes Link-local IPv6 Address . . . . . : fe80::b50d:7748:f233:237c%3(Preferred) IPv4 Address. . . . . . . . . . . : 172.16.1.41(Preferred) Subnet Mask . . . . . . . . . . . : 255.255.255.0 Default Gateway . . . . . . . . . : 172.16.1.5 DHCPv6 IAID . . . . . . . . . . . : 181667046 DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-2D-D9-50-A2-D4-04-E6-0E-A2-87 DNS Servers . . . . . . . . . . . : ::1 172.16.1.41 66.187.177.13 66.187.178.13 NetBIOS over Tcpip. . . . . . . . : Enabled Ethernet adapter Ethernet: Connection-specific DNS Suffix . : Description . . . . . . . . . . . : IBM USB Remote NDIS Network Device Physical Address. . . . . . . . . : 3A-68-DD-C6-88-1F DHCP Enabled. . . . . . . . . . . : No Autoconfiguration Enabled . . . . : Yes Link-local IPv6 Address . . . . . : fe80::6d32:f1e6:7c0f:dd5d%9(Preferred) IPv4 Address. . . . . . . . . . . : 169.254.95.120(Preferred) Subnet Mask . . . . . . . . . . . : 255.255.255.0 Default Gateway . . . . . . . . . : DHCPv6 IAID . . . . . . . . . . . : 473589981 DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-2D-D9-50-A2-D4-04-E6-0E-A2-87 NetBIOS over Tcpip. . . . . . . . : Enabled New VM Ethernet adapter vEthernet (Virtual Switch): Connection-specific DNS Suffix . : Description . . . . . . . . . . . : Hyper-V Virtual Ethernet Adapter Physical Address. . . . . . . . . : D4-04-E6-0E-A2-87 DHCP Enabled. . . . . . . . . . . : Yes Autoconfiguration Enabled . . . . : Yes Link-local IPv6 Address . . . . . : fe80::a334:5bd:24d:d2b3%19(Preferred) Autoconfiguration IPv4 Address. . : 169.254.142.53(Preferred) Subnet Mask . . . . . . . . . . . : 255.255.0.0 Default Gateway . . . . . . . . . : DHCPv6 IAID . . . . . . . . . . . : 416548070 DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-2D-D9-50-A2-D4-04-E6-0E-A2-87 NetBIOS over Tcpip. . . . . . . . : Enabled Ethernet adapter Slot4 Port 1: Connection-specific DNS Suffix . : Description . . . . . . . . . . . : Broadcom 5719 1GbE RJ45 4-port OCP Ethernet Adapter #2 Physical Address. . . . . . . . . : D4-04-E6-0E-A2-86 DHCP Enabled. . . . . . . . . . . : No Autoconfiguration Enabled . . . . : Yes Link-local IPv6 Address . . . . . : fe80::b50d:7748:f233:237c%3(Preferred) IPv4 Address. . . . . . . . . . . : 172.16.1.41(Preferred) Subnet Mask . . . . . . . . . . . : 255.255.255.0 Default Gateway . . . . . . . . . : 172.16.1.5 DHCPv6 IAID . . . . . . . . . . . : 181667046 DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-2D-D9-50-A2-D4-04-E6-0E-A2-87 DNS Servers . . . . . . . . . . . : ::1 172.16.1.41 66.187.177.13 66.187.178.13 NetBIOS over Tcpip. . . . . . . . : Enabled Ethernet adapter Ethernet: Connection-specific DNS Suffix . : Description . . . . . . . . . . . : IBM USB Remote NDIS Network Device Physical Address. . . . . . . . . : 3A-68-DD-C6-88-1F DHCP Enabled. . . . . . . . . . . : No Autoconfiguration Enabled . . . . : Yes Link-local IPv6 Address . . . . . : fe80::6d32:f1e6:7c0f:dd5d%9(Preferred) IPv4 Address. . . . . . . . . . . : 169.254.95.120(Preferred) Subnet Mask . . . . . . . . . . . : 255.255.255.0 Default Gateway . . . . . . . . . : DHCPv6 IAID . . . . . . . . . . . : 473589981 DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-2D-D9-50-A2-D4-04-E6-0E-A2-87 NetBIOS over Tcpip. . . . . . . . : Enabled65Views0likes1Comment
Windows Server Datacenter: Azure Edition preview build 29659 now available in Azure
Hello Windows Server Insiders! We welcome you to try Windows Server vNext Datacenter: Azure Edition preview build 29659 in both Desktop experience and Core version on the Microsoft Server Operating Systems Preview offer in Azure. Azure Edition is optimized for operation in the Azure environment. For additional information, see Preview: Windows Server VNext Datacenter (Azure Edition) for Azure Automanage on Microsoft Docs. For more information about this build, see https://techcommunity.microsoft.com/discussions/windowsserverinsiders/announcing-windows-server-vnext-preview-build-29659/4554949.88Views0likes0CommentsHyper-V replication
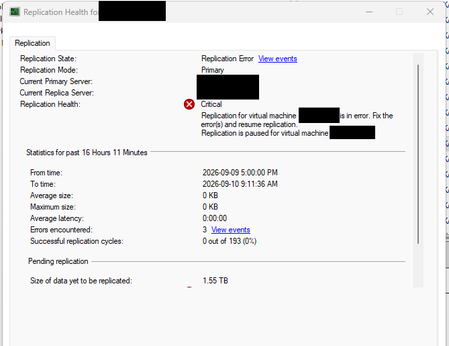
I have two Hyper-V failover clusters (primary and secondary) with replication enabled. I got a server replication error: But recently, the only way to fix it has been to remove the replication and enable it again. Is there another way to fix the Hyper-V replication?Solved72Views0likes2Comments
Strict users to use specific software windows server 2022
I have MT5 installed on (C:\Program Files\MetaTrader 5) there are the meta trader 5 terminal64.exe and MetaEditor64.exe applications, mt5 data folder as follow C:\Users\Administrator\AppData\Roaming\MetaQuotes\Terminal\ MT4 on (C:\Program Files (x86)\MetaTrader 4) there are applications terminal.exe and metaeditor.exe and data folder as follow C:\Users\Administrator\AppData\Roaming\MetaQuotes\Terminal\ I use windows server 2022 and I want to create user accounts each account have access only to MT4 or MT5 and the meta editor and data folder only and each user can use the software MT4 or MT5 based on assigned group, users can use the same software at the same time in their own accounts I need 2 windows powershell scripts 1-create 2 user groups for MT4 and MT5 with the access restrcicted to all windows software and features execpt the MT4 or MT5 and the meta editor, and the data folder and desktop showing these icons/shortcuts and webview2 runtime to installed be allowed because it is needed by meta trader ( user cannot see windows bar cannot use any windows software, and the most important that the MT4 or MT5 software to be always running and start always after windows reboot/restart not when user log on, these software run trading algoeithms and must be working around the clock even if the user is not logged in 2- interactive script that use to create the users37Views0likes0CommentsAnnouncing Windows Server vNext Preview Build 29659
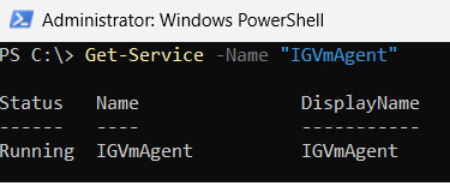
Hello Windows Server Insiders! Today we are pleased to release a new build of the next Windows Server Long-Term Servicing Channel (LTSC) Preview that contains both the Desktop Experience and Server Core installation options for Datacenter and Standard editions and Azure Edition (for VM evaluation only). Branding remains Windows Server 2025 in this preview - when reporting issues please refer to Windows Server vNext preview. Build 29531 established a new Server preview baseline build. Please perform a clean install of Build 29531 (or later) using the installation media linked below. Please note: Upgrades from Windows Server vNext preview builds older than 29531 are not supported. We encourage all Windows Server vNext preview users to perform a clean install using 29531 or later to successfully upgrade to future Windows Server vNext preview builds. While upgrades from earlier Windows Server previews (Build 26525 and older) are not technically blocked by setup.exe, a number of known issues have been identified related to upgrades necessitating the establishment of a new baseline build for our Server vNext Preview Program. The new baseline build (29531) will not be Flighted due to upgrade issues. Flighting support resumed with preview build 29550 or later. What's New Trusted Launch for virtual machines (TVMs) on Windows Server—a security feature you can enable when creating Generation 2 VMs. This initial preview supports TVMs with Secure Boot, vTPM, and vTPM state protection (at rest), managed via PowerShell. ⚠ Not supported in this release: Moving TVMs to another server TVMs in failover clusters or Hyper-V Replica Boot integrity verification TVMs in Windows Admin Center (WAC) Instructions 1. Install the latest ServerInsider preview build. 2. Enable Hyper-V (restarts the server): Install-WindowsFeature -Name Hyper-V -IncludeManagementTools -Restart 3. Set the registry keys: New-Item -Path "HKLM:\SOFTWARE\Microsoft\AszIgvmAgent" -Force New-ItemProperty -Path "HKLM:\SOFTWARE\Microsoft\AszIgvmAgent" -Name "TvmWinServer" -Value 1 -PropertyType DWord -Force 4. Enable Trusted Launch: Enable-WindowsOptionalFeature -Online -FeatureName "IsolatedGuestVm" -NoRestart 5. Verify IGVmAgent is running (should show Running): Get-Service -Name "IGVmAgent" If it isn't running, report the issue with the IGVmAgent and IGVmSystem Operational logs (Event Viewer → Applications and Services Logs → Microsoft → Windows). 6. Create an external virtual switch (if needed): (Get-VMSwitch | Where-Object { $_.SwitchType -eq "External" }).Name 7. Create the TVM. With an existing Gen 2 VHDX: New-VM -Name <VMName> -Generation 2 -GuestStateIsolationType TrustedLaunch -SwitchName <switch> -VHDPath <path to vhdx> -Path <config path> Or with a new VHD, then attach a Gen 2–compatible guest OS ISO: New-VM -Name <VMName> -SwitchName <switch> -NewVHDPath <new VHD path> -NewVHDSizeBytes 40GB -Generation 2 -GuestStateIsolationType TrustedLaunch -Path <config path> Add-VMDvdDrive -VMName <VMName> -Path <Guest OS ISO path> Ensure the DVD drive is first in the firmware boot order so the VM boots from it. 8. Verify isolation type (should return TrustedLaunch): (Get-VM -Name <VMName>).GuestStateIsolationType 9. Verify guest state protection: Stop the IGVmAgent service and restart the VM—without IGVmAgent running, a Trusted launch VM with guest state protection won't start. For more information, please review our blog post: Announcing Trusted Launch for Virtual Machines for Windows Server Insiders | Microsoft Community Hub Quick Machine Recovery available in Windows Server vNext Insider Previews. Quick machine recovery (QMR) is now available for Server vNext Insiders to test. This feature enables the recovery of Windows Server devices when they encounter boot critical errors that prevent them from booting. QMR can automatically search for cloud‑based remediations to recover from widespread boot failures significantly reducing the burden on IT administrators when multiple devices are impacted. This supports the goals of the Windows Resiliency Initiative by enabling applicable fixes to be delivered through trusted Windows Update to restore affected devices, helping reduce downtime and minimize manual recovery efforts across enterprise environments. This feature is currently enabled in the latest Server vNext Insider builds for customers to experience test mode. A Group Policy option to enable or disable the feature will be introduced in upcoming builds to provide additional administrative control. To simulate the quick machine recovery experience, use the following commands from an elevated command prompt: Enable test mode: reagentc.exe /SetRecoveryTestmode Configure Windows to boot to Windows Recovery Environment on the next boot: reagentc.exe /BootToRe Reboot your device.The system goes through autoremediation of a simulated crash safely and reboots back to Windows Server. For more information, please review Quick machine recovery (QMR) and Windows Resiliency Initiative. When providing feedback using Feedback hub, please select QMR from the Recovery and Uninstall category in the app. NVMe-over-Fabrics (NVMe-oF) extends the NVMe protocol—originally designed for local PCIe-attached SSDs—across a network fabric. Instead of using legacy SCSI-based protocols such as iSCSI or Fibre Channel, NVMe-oF allows a host to communicate directly with remote NVMe controllers using the same NVMe command set used for local devices. In this Insider build, Windows Server supports: NVMe-oF over TCP (NVMe/TCP), allowing NVMe-oF to run over standard Ethernet networks without specialized hardware. NVMe-oF over RDMA (NVMe/RDMA), enabling low-latency, high-throughput NVMe access over RDMA-capable networks (for example, RoCE or iWARP) using supported RDMA NICs. For more information, please visit: Introducing the Windows NVMe-oF Initiator Preview in Windows Server Insiders Builds | Microsoft Community Hub ReFS Boot is enabled for Windows Server vNext preview builds. Known Limitations ReFS Boot systems create a minimum 2GB WinRE partition. When WinRE cannot be updated due to space constraints, the system may disable WinRE. Disabling WinRE does not remove the partition. If the WinRE partition is deleted and the boot volume is extended over it, this operation is unrecoverable without a clean install. For more information, please visit: Resilient File System (ReFS) overview | Microsoft Learn Feedback Hub app is available for Server Desktop users! The app should automatically update with the latest version, but if it does not, simply Check for updates in the app’s settings tab. Known Issues A race condition in the TLS hybrid key exchange implementation may cause the LSASS service to crash when hybrid groups are negotiated by a TLS server. To avoid this issue until the fix is released, please disable hybrid groups (X25519_MLKEM768, SecP256r1_MLKEM768, SecP384r1_MLKEM1024) using TLS cmdlets or Group Policy, as outlined here. Server Core Upgrades and AppCompat FOD: Enabling AppCompat FOD after reinstall may fail due to legacy 3rd-party license compatibility issues on Server Core devices. Server Core users may be unable to install the latest AppCompat FOD after upgrading to build 29574. This appears to be limited to Server Core installations with 3rd-party application licenses that fail compatibility checks after upgrade. This will be addressed in a future build. Upgrading from older builds of Windows Server vNext previews (26525 or older) are not supported. Please perform a clean install of build 29531 or later. Users may experience failures when attempting to upgrade from earlier previews (build 26525 and older). VMs may fail to upgrade or start after upgrade from older preview builds impacting live migration and failover cluster scenarios. Download Windows Server Insider Preview (microsoft.com) Flighting: The label for this flight may incorrectly reference Windows 11. However, when selected, the package installed is the Windows Server vNext update. Please ignore the label and proceed with installing your flight. This issue will be addressed in a future release. Available Downloads Downloads to certain countries may not be available. See Microsoft suspends new sales in Russia - Microsoft On the Issues. Windows Server Long-Term Servicing Channel Preview in ISO format in 18 languages, and in VHDX format in English only. Windows Server Datacenter Azure Edition Preview in ISO and VHDX format, English only. Microsoft Server Languages and Optional Features Preview Keys: Keys are valid for preview builds only Server Standard: MFY9F-XBN2F-TYFMP-CCV49-RMYVH Datacenter: 2KNJJ-33Y9H-2GXGX-KMQWH-G6H67 Azure Edition does not accept a key. Symbols: Available on the public symbol server – see Using the Microsoft Symbol Server. Expiration: This Windows Server Preview will expire October 15, 2027. How to Download Registered Insiders may navigate directly to the Windows Server Insider Preview download page. If you have not yet registered as an Insider, see GETTING STARTED WITH SERVER on the Windows Insiders for Business portal. We value your feedback! The most important part of the release cycle is to hear what's working and what needs to be improved, so your feedback is extremely valued. Please use the new Feedback Hub app for Windows Server if you are running a Desktop version of Server. If you are using a Core edition, or if you are unable to use the Feedback Hub app, you can use your registered Windows 10 or Windows 11 Insider device and use the Feedback Hub application. In the app, choose the Windows Server category and then the appropriate subcategory for your feedback. In the title of the Feedback, please indicate the build number you are providing feedback on as shown below to ensure that your issue is attributed to the right version: [Server #####] Title of my feedback See Give Feedback on Windows Server via Feedback Hub for specifics. The Windows Server Insiders space on the Microsoft Tech Communities supports preview builds of the next version of Windows Server. Use the forum to collaborate, share and learn from experts. For versions that have been released to general availability in market, try the Windows Server for IT Pro forum or contact Support for Business. Diagnostic and Usage Information Microsoft collects this information over the internet to help keep Windows secure and up to date, troubleshoot problems, and make product improvements. Microsoft server operating systems can be configured to turn diagnostic data off, send Required diagnostic data, or send Optional diagnostic data. During previews, Microsoft asks that you change the default setting to Optional to provide the best automatic feedback and help us improve the final product. Administrators can change the level of information collection through Settings. For details, see http://aka.ms/winserverdata. Also see the Microsoft Privacy Statement. Terms of Use This is pre-release software - it is provided for use "as-is" and is not supported in production environments. Users are responsible for installing any updates that may be made available from Windows Update. All pre-release software made available to you via the Windows Server Insider program is governed by the Insider Terms of Use.Assign IP Address for Windows Server 2025 VM on Hyper-V
I have built my first Windows Server 2025 VM on HyperV and trying to assign an IP address. I want the VM's to be like an actual server so I Created an external vswitch. The HyperV server IP is 172.16.1.41 with a physical gateway of 172.16.1.5. I have tried to assign the new VM with 172.16.1.42/255.255.255.0 and the Gateway is 172.16.1.5 also. However, I cannot get a positive ping. Do I need another VSWITCH configured or what am I missing?232Views0likes5Comments
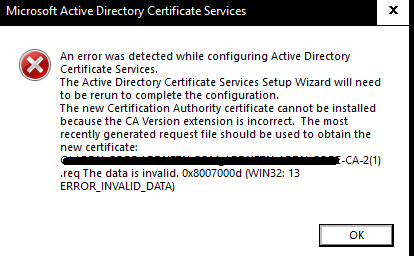
Two-tier AD Certificate Services error importing cert into SubCA
Hello, I'm new here, but excited about being able to hob nob with all you in furthering our IT goals. I'm setting up my root and Subordinate CA and I'm importing my rootCA issued, subCA certificate into the subCA. I get I get the same error when the subCA automatically exports its cert req to the root Ca and when I do it manually. I also get this error whether i'm using X.509 or p7b files. what's unusual about this error is that it seems to be referencing a .req file with a '(1)' added to the end of the title. Original .req did not have the '(1)'. any assistance I can get from the community would be appreciated.234Views0likes2Comments 190Views0likes2Comments
How are you managing Group Policy changes after AGPM end of support?
Hi, I’m interested in how organizations are handling Group Policy change management now that AGPM is no longer supported. In environments where GPOs are still heavily used, what are you relying on today for version history, change tracking, rollback and approvals? Are you continuing with AGPM, moving to products such as GPOADmin or Cayosoft, or mainly using native GPMC backups and PowerShell? I’m also interested in whether there is still a gap around having a clear web-based view of GPO history and changes, especially being able to understand exactly what changed and which users or computers may be affected before a change is applied. I’d be interested to hear how this is handled in real production environments and what parts of the process are still manual or difficult.137Views0likes1Comment
SNMP Query fails with Error: Error in packet. Reason: (genError) A general failure occured
I have enabled a win Server 2022 and a Win11 machine to answer SNMP requests. However both machines run into error while doing a snmpwalk. I have started with OID just before errornous OID. Both machines show same behaviour. Does someone experience same problem? Can someone recreate this problem? Does someone know a cure fort this problem? Does someone have any ideas how to proceed? root# snmpwalk -Os -v 1 -c public <hostname> .1.3.6.1.4.1.77 comVersionMaj.0 = STRING: "10" comVersionMin.0 = STRING: "0" comType.0 = Hex-STRING: 03 00 00 00 Error in packet. Reason: (genError) A general failure occured Failed object: comType.0 root@monitor:/etc/munin/plugins# snmpwalk -On -v 1 -c public <hostname> .1.3.6.1.4.1.77 .1.3.6.1.4.1.77.1.1.1.0 = STRING: "10" .1.3.6.1.4.1.77.1.1.2.0 = STRING: "0" .1.3.6.1.4.1.77.1.1.3.0 = Hex-STRING: 03 00 00 00 Error in packet. Reason: (genError) A general failure occured Failed object: .1.3.6.1.4.1.77.1.1.3.0175Views0likes2CommentsWindows Server 2022 Hyper-V : vmconnect introuvable pour accéder à la console VM (Server Core)
Contexte Windows Server 2022 [Standard/Datacenter — à préciser], rôle Hyper-V installé. J'ai créé une VM invitée Linux nommée « Wazuh » (installation d'une plateforme SIEM), elle démarre correctement. ce serveur est une VM imbriquée dans un autre hyperviseur type VMware Workstation. je suis en simple groupe de travail (workgroup). Ce que je constate PS C:\Users\Administrator> Start-VM -Name 'Wazuh' PS C:\Users\Administrator> vmconnect localhost Wazuh vmconnect : The term 'vmconnect' is not recognized as the name of a cmdlet, function, script file, or operable program. Check the spelling of the name, or if a path was included, verify that the path is correct and try again. At line:1 char:1 + vmconnect localhost Wazuh + ~~~~~~~~~ + CategoryInfo : ObjectNotFound: (vmconnect:String) [], CommandNotFoundException + FullyQualifiedErrorId : CommandNotFoundException PS C:\Users\Administrator> Get-VM -Name 'Wazuh' | Select-Object State, Status State Status ----- ------ Running Operating normally PS C:\Users\Administrator> vmconnect localhost Wazuh vmconnect : The term 'vmconnect' is not recognized as the name of a cmdlet, function, script file, or operable program... La VM est bien « Running / Operating normally » selon Get-VM, donc le souci n'est pas la VM elle-même mais l'accès à sa console. Ce que j'ai déjà essayé Get-WindowsFeature *Hyper-V* → [colle ici la sortie exacte que tu as obtenue] Install-WindowsFeature -Name RSAT-Hyper-V-Tools -IncludeAllSubFeature → toujours pas de vmconnect.exe fonctionnel après coup Je soupçonne que ce serveur est installé en mode Server Core (pas d'interface graphique locale), et j'ai lu que la conversion Core → Desktop Experience n'est plus possible après coup depuis Server 2016. Ma question pour la communauté Est-il vraiment impossible d'obtenir une console graphique locale (vmconnect / Hyper-V Manager) sur un Server Core, même une fois les outils de gestion Hyper-V installés ? Quelle est la méthode la plus fiable pour accéder à la console d'une VM Hyper-V hébergée sur un Server Core, en environnement non-domaine (workgroup) : Windows Admin Center, Hyper-V Manager distant (config WinRM/TrustedHosts), ou faut-il simplement réinstaller en Desktop Experience ? Si quelqu'un a déjà mis en place Windows Admin Center ou du Hyper-V Manager distant sur un lab en groupe de travail (sans AD), un retour d'expérience serait très utile. Merci d'avance !215Views0likes1CommentIssue with Temporary Profile on Windows Server 2025 after renaming built-in Administrator account
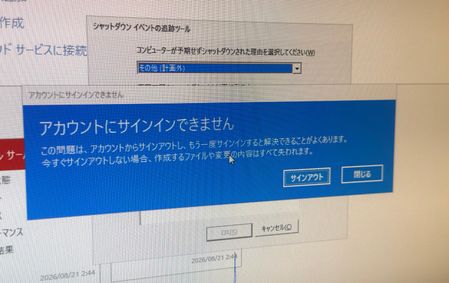
Hi everyone, I am facing an issue with a temporary profile on Windows Server. Environment details: ・OS: Windows Server 2025 Datacenter ・Setup: On-premises environment with 2 servers (AD DS Domain Controller and Web Server) ・Affected Server: Web Server (Domain joined) Recently, I renamed the built-in Administrator account on the Web Server. After that, the system became completely unresponsive, so I had to force a power off. Upon signing in after the reboot, I received the error message: "We can't sign in to your account" (or "You've been signed in with a temporary profile"). It seems the profile folder or registry mapping for the renamed Administrator account was corrupted due to the force shutdown. I tried restarting the server, but the issue persists. Could anyone please advise on the proper way to resolve this registry/profile conflict and safely restore the renamed Administrator profile? Please note that I am a native Japanese speaker and a beginner in IT, so I may not fully understand complex technical English. Simple, step-by-step instructions would be greatly appreciated! Thank you in advance for your help! Translated by Gemini, grammar checked by DeepL500Views2likes7Comments






Events
Recent Blogs
- Windows Server continues to be the foundation for many of the world's most critical business applications. As organizations modernize their infrastructure, extend management beyond the datacenter, an...Aug 12, 2026337Views1like0Comments
- Trusted Launch for virtual machines We are excited to announce Trusted Launch for virtual machines (TVMs) in Windows Server Insider Preview. Trusted Launch is a security feature you can enable whe...Jul 14, 20261KViews4likes5Comments